

We’re determined to make organizations secure against cyber threats and confident in their readiness.
Joined April 2009
- Tweets9.6K
- Following4.1K
- Followers13K
- Likes2.5K




Mandiant (part of Google Cloud) retweeted
A brief update on the critical vulnerabilities in PHP:
We have not yet validated exploitation in the wild and we have no evidence of successful wide scale exploitation. There are currently several exploit PoCs publicly circulating, many of which appear to be "vibe-coded" and are incapable of remote code execution. We have validated some PoCs, however, that are capable of RCE against default deployments of mod_php but not PHP-FPM.
Nonetheless, exploitation may have already begun in a limited fashion and the threat is viable and very serious. Defenders should:
1) Patch & Restart by upgrading to PHP 8.5.12, 8.4.27, 8.3.36, or 8.2.35 and restarting web services
2) Layer Temporary Safeguards at the network edge (WAF/proxy rules) and server configuration level if immediate patching requires a maintenance window
3) Protect Credentials by monitoring for abnormal session traffic and rotating keys and passwords on compromised internet-facing PHP systems exposed prior to patching
🔗 We are continually updating our Cloud Security blog post on this topic with real-world guidance and actionable defense strategies as we learn more. Please keep monitoring these posts for updates as you prioritize your patching efforts: cloud.google.com/blog/produc…
🔗 Technical details from Wiz: wiz.io/blog/php2shell-php-rc…
🔗 Details of the exposure from VirusTotal: blog.virustotal.com/2026/10/…

Friday focus: CTI. 🧑💻
Explore Mandiant Academy courses on OSINT, network enrichment, & attribution.
Swipe for the details and find links in the thread below. 👇

ALT Explore Mandiant Academy

ALT Explore Mandiant Academy

ALT Explore Mandiant Academy

ALT Explore Mandiant Academy
🔍 Sharpen your OSINT investigations: goo.gle/4zRkUpr
🛡️ Enrich your network defenses: goo.gle/47x3Ysh
🌍 Map threat actor attribution: goo.gle/4BmgEQf
🏗️ Build a world-class CTI program: goo.gle/4AbklXR

ALT Explore Mandiant Academy

ALT Explore Mandiant Academy
Mandiant (part of Google Cloud) retweeted

Our @Mandiant red team tricked a developer assistant into uploading an entire codebase—no exploit needed. ⚠️
Static rules won't protect autonomous workflows. You need real-time monitoring, scoped permissions, and active guardrails.
Join us Nov 4: goo.gle/3UGpFmI

🚨 Two critical PHP core vulnerabilities (CVSS 9.2) expose web apps to RCE and memory disclosure across PHP 5.4–8.5.11. Use our guide to patch and hunt for compromise.
@googlecloud advisory: goo.gle/4idT13I
@wiz_io research: goo.gle/4BiQgGX

🚨 Suspected PRC-nexus actor ARMORY CASTLE is exploiting a BeyondTrust zero-day (CVE-2026-102764) to gain root persistence, dump vault secrets, and wipe logs.
📋 Full analysis & IOCs: goo.gle/4dKpqxv

RT @GoogleCloudSec: Attackers aren't just trying to trick models—they’re going after the plumbing. ⚠️
From poisoned packages to hijacked c…
School is back in session 📚
Level up your security game with refreshed Mandiant Academy courses. Explore the catalog and sign up today ⬇️


🗳️ Election Security: goo.gle/4hFR3ZE
🌍 Inside the Mind of an APT: goo.gle/4rNC7xd
🔧 Intelligence Research I—Scoping: goo.gle/3VlO8xO
📋 Cyber Intelligence Production: goo.gle/4xYNmV6


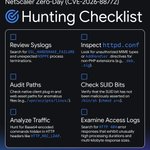
🚨 Mandiant & GTIG have identified active zero-day exploitation of Citrix NetScaler appliances (CVE-2026-88772).
Attackers are deploying custom tools like WHIPSHOT. Since edge devices lack EDR, use this hunting checklist to detect compromise.
📋 goo.gle/4dfZzxb

ALT CVE-2026-88772 hunting checklist
Adversaries are targeting AI pipelines. Are you equipped to hunt them? 🔍
🧑💻 Join Mandiant Academy’s ThreatSpace (Oct 13–14) to hunt AI-specific TTPs and disrupt the AI Application Kill Chain in a hands-on cyber range.
Upgrade your playbook today.
✍️ goo.gle/4hNxQGy
🛡️ CDS '26 is a wrap!
Thanks to the experts and partners who joined us in DC. We covered it all this week: AI advantages, growing vulnerabilities, next-gen adversaries, Gretzky metaphors. 🏒
See you in 2027! 👋


What happens when an AI coding assistant is exploited as a Trojan horse? ⚠️
Our AI Risk & Resilience 2026 report details how a hijacked session deployed the 'Shai-Hulud' worm to exfiltrate code.
Look at the attack flow. What's your move? ♟️
📄 goo.gle/4rewCHD

ALT AI Risk and Resilience

ALT AI Risk and Resilience

ALT AI Risk and Resilience

ALT AI Risk and Resilience
Cyber Defense Summit 26 kicks off tomorrow! 📣
AI. Cybercrime. Resilience. Nation-state threats. Real-world cases. @briankrebs going unscripted with @JohnHultquist. 🍿
Check the agenda, pick your sessions, and get ready.
✍️ Still time to register: goo.gle/4yA5rcH
AI is reshaping cyber defense. Next week at #CDS2026, we’re moving past the hype.
Join Mandiant consultants, the FBI, and industry leaders for 5 critical sessions covering AI governance, zero-days, and securing LLMs. 👇

ALT AI Sessions at CDS 2026

ALT AI Sessions at CDS 2026

ALT AI Sessions at CDS 2026

ALT AI Sessions at CDS 2026
Hear from the experts. Register today: goo.gle/4dsBjYs

ALT AI Sessions at CDS 2026

ALT AI Sessions at CDS 2026

ALT AI Sessions at CDS 2026
Mandiant (part of Google Cloud) retweeted
⏱️ 6 hours. That’s all it took for an adversary to compromise a cloud environment and harvest thousands of credentials—all driven by AI.
Our new GTIG AI Threat Tracker details the shift to autonomous operations and how Google disrupts these campaigns.
📄 goo.gle/4xa7Zgr


