



Pinned Tweet
𝗪𝗲 𝗵𝗲𝗮𝗿𝗱 𝘆𝗼𝘂. 𝗬𝗼𝘂 𝗮𝘀𝗸𝗲𝗱. 𝗪𝗲 𝘀𝗮𝗶𝗱 𝗻𝗼𝘁𝗵𝗶𝗻𝗴.
𝗕𝗲𝗰𝗮𝘂𝘀𝗲 𝘄𝗲 𝘄𝗲𝗿𝗲 𝗯𝘂𝗶𝗹𝗱𝗶𝗻𝗴.🔐
Meet 𝟮𝗙𝗔𝗦 𝗣𝗮𝘀𝘀 – our new Local-first Password Manager.
• No cloud dependency
• No accounts
• Privacy by design
It’s here. It’s secure. It remembers what you forget.
Learn more: 2fas.com
Watch the video: youtu.be/UDIWzk7D--s
Oh, and 2FAS Auth is still going strong!✌️


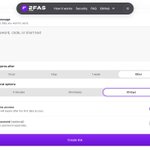
Introducing 2FAS Share!
Need to send someone a password or other sensitive information? Don't send it over chat or email, where it can stay forever. Use a secure link that expires automatically.
With 2FAS Share your messages are end-to-end encrypted. You can set an expiration time, choose between one-time and repeated access, and add a password for extra protection.
It's free for everyone. No accounts or downloads needed for you or the recipient.
Check it out: share.2fas.com/

Top 150 worst passwords. If you recognize yours, change it.
1. 123456
2. Password
3. 123456789
4. qwerty
5. 12345678
6. admin
7. 12345
8. 111111
9. 1234567
10. 1234567890
11. abc123
12. password1
13. password123
14. qwerty123
15. 123123
16. 000000
17. iloveyou
18. letmein
19. welcome
20. 1234
21. admin123
22. Admin@123
23. 121212
24. 222222
25. 12341234
26. monkey
27. football
28. dragon
29. michael
30. sunshine
31. master
32. 654321
33. princess
34. baseball
35. secret
36. charlie
37. mustang
38. login
39. chocolate
40. batman
41. jennifer
42. 112233
43. shadow
44. liverpool
45. computer
46. cookie
47. princess1
48. summer
49. Ferrari
50. ashley
51. pokemon
52. guest
53. tiger
54. freedom
55. Hello
56. daniel
57. coffee
58. 666666
59. passw0rd
60. maverick
61. banana
62. superman
63. amanda
64. hockey
65. changeme
66. mercedes
67. rainbow
68. hunter
69. minecraft
70. P@ssw0rd
71. london
72. pepper
73. Jessica
74. Blahblah
75. whatever
76. dolphin
77. matrix
78. Andrew
79. welcome1
80. chelsea
81. 55555
82. diamond
83. Corvette
84. test
85. naruto
86. flower
87. william
88. soccer
89. zxcvbnm
90. harley
91. kitten
92. nothing
93. starwars
94. Robert
95. pizza
96. Aa123456
97. winter
98. administrator
99. panther
100. toyota
101. emily
102. tennis
103. trustno1
104. pikachu
105. ginger
106. ranger
107. barcelona
108. internet
109. sarah
110. penguin
111. admintelecom
112. zaq1zaq1
113. fortnite
114. butter
115. 1qaz2wsx
116. dallas
117. Nicole
118. abcdef
119. puppy
120. default
121. spiderman
122. spring
123. abcd1234
124. matthew
125. samsung
126. lucky
127. rabbit
128. merlin
129. access
130. george
131. honda
132. querty
133. bandit
134. bailey
135. cowboys
136. elephant
137. thomas
138. arsenal
139. loveme
140. harrypotter
141. jaguar
142. david
143. lakers
144. qwertyuiop
145. music
146. Cheese
147. James
148. john
149. gandalf
150. aaaaaa
1
12
833
For those of you asking why:
1. If someone gets into your email, they can often reset passwords for your other accounts. If your 2FA codes go to that same inbox, they get those too. One hacked inbox can open the door to several accounts.
2. Attackers don't always need your email password. Malware can steal an existing login session letting someone access your inbox as if they were already logged in, without entering your password or a new 2FA code.
3. With a separate authenticator app, getting into your email doesn't give the attacker your codes. Even if they reset your password, 2FA can still stop them.
7
290
❗️Two carmakers left admin consoles on their login servers with both the username and password set to "admin."
Researchers used that unchanged default login as part of an attack that let them unlock cars and start their engines remotely.
Sam Curry and Shubham Shah bypassed security filters on the servers behind the carmakers' apps. From there they could change a customer's email and password, sign in as them and use the car's available remote features.
The owner stayed logged into the app and the researchers could redirect notifications so those alerts wouldn't reach the owner's phone.
Both carmakers, unnamed in the report, fixed the issue about two hours after researchers contacted them.

1
12
621
Source: samcurry.net/forgerock

163
A screenshot of a password is still a copy of that password.
Saving it to your photo gallery means it could end up in photo backups, accidentally get added to a shared album, or sync to your tablet and sit there forgotten for years. "Just saving it for a second" can create a very long lived copy.
What does that look like in practice?
Someone who gains access to your photo backups could find the password there, even if you've deleted the screenshot from your phone.
A family member using your tablet could come across it while browsing your photos.
You could accidentally show it while sharing your screen or selecting photos to send.
Every extra copy is another place you need to protect.
Save passwords where they belong: in a password manager, designed to keep them encrypted and protected.

2FAS vs. Big Tech: 2FA Privacy Edition
Your authenticator is part of your security setup. But what does it know about you?
What data does it collect? Is it linked to you? Does your 2FA app really need it?
Choose an authenticator app that protects both your accounts and your privacy.
#2FAS #CybersecurityAwarenessMonth #opensource

A recently disclosed security flaw called PHP2Shell could let attackers run code on vulnerable web servers without logging in. Depending on what those servers can access, attackers could steal customer data, change it or tamper with the service itself.
It's a reminder that where your data lives and who can access it matters.
That's the idea behind 2FAS Pass password manager:
your passwords are encrypted on your phone. We don't hold your vault. There's no account to create and no central collection of our users' vaults to steal from us.
Want a backup? It's encrypted on your device with your keys. You choose where to keep it. Someone who steals that copy can't read anything.
That's what local-first means to us:
your vault stays in your hands.
Hackers can't steal from us what we don't have.
Your passwords. Your device. Your control.
14
633
Switching to 2FAS Pass is easier than you think.
Import your saved passwords from your browser or existing password manager without copying them one by one.
Go to Settings → Transfer from other Apps → Choose your source and move your passwords into the local-first, end-to-end encrypted password manager designed with privacy and security as its core.


STOP PUTTING PASSWORDS IN YOUR NOTES APP
STOP PUTTING PASSWORDS IN YOUR NOTES APP
STOP PUTTING PASSWORDS IN YOUR NOTES APP
STOP PUTTING PASSWORDS IN YOUR NOTES APP
STOP PUTTING PASSWORDS IN YOUR NOTES APP
STOP PUTTING PASSWORDS IN YOUR NOTES APP
STOP PUTTING PASSWORDS IN YOUR NOTES APP


Can you spot the difference?
аmazon.com
amazon.com
These two look almost identical.
Homograph attacks use lookalike characters to make malicious links appear legitimate.
Don't trust your eyes.
Here's how to outsmart scammers:

3/
Bookmark important websites.
Save your bank and other important accounts as bookmarks. When you need to log in, use the bookmark instead of searching for the site or clicking a link in a message.
1
3
266