

For those interested in the research and development of the Bitcoin protocol. npub1nydevscv0slx9eyr0chkkdgzqfhtp4guk039akhq6g9fnsrf6lcsup3hqs
New York, NY, USA
Joined November 2023
- Tweets368
- Following289
- Followers495
- Likes203






Pinned Tweet
Our next BitDevs Meetup is Thursday October 22.
Sponsored by @cakewallet and @ChaincodeLabs
RSVP on Meetup or Luma:
meetup.com/bitdevsnyc/events…
luma.com/0v4gd0aq

Tons of topics ready for TOMORROW!
bitdevs.org/2026-10-22-socra…
Come enjoy some beer, pizza, and BITCOIN with us.

Our next BitDevs Meetup is Thursday October 22.
Sponsored by @cakewallet and @ChaincodeLabs
RSVP on Meetup or Luma:
meetup.com/bitdevsnyc/events…
luma.com/0v4gd0aq
BitDevsNYC retweeted
Big update alert! There’s a LOT packed into Cake Wallet v6.5.0 🔥
🗂️ Bitcoin Accounts + faster syncing
📈 Price charts
💸 Cash App Pay via MoonPay
🧅 Expanded Tor node support
🔒 Monero update + safer sends
🏹 Robinhood Chain
Plus plenty of fixes and improvements!
Update now to check it all out, and keep an eye out for upcoming video demos and tutorials!

We're collecting topics for this Thursday's BitDevs meetup. Leave a comment if there's something important to you for us to discuss!
Sponsored by @cakewallet and @ChaincodeLabs
github.com/BitDevsNYC/BitDev…

Register on Meetup or Luma:
meetup.com/bitdevsnyc/events…
luma.com/0v4gd0aq

BitDevsNYC retweeted

Everything you always wanted to know about Secp256k1's ½G*
(*but were afraid to ask)

Next mystery: the unexplained origin of secp256k1’s 1/2G.
@AnthropicAI please ask Claude to also find those seeds, underlying Bitcoin and most other cryptocurrencies.

See you next week! Sign up on Meetup or Luma
Our next BitDevs Meetup is Thursday October 22.
Sponsored by @cakewallet and @ChaincodeLabs
RSVP on Meetup or Luma:
meetup.com/bitdevsnyc/events…
luma.com/0v4gd0aq
BitDevsNYC retweeted

Post-quantum transactions that require only 96 bytes on-chain:
@will_wjk (Imperial College) et al. published a very interesting variant of Shielded CSV, called Compact Shielded CSV.
I've always thought the CSV model is attractive in a PQ setting: the blockchain only stores the nullifier, so miners don't have to verify a signature before it gets into a block. Compact Shielded CSV goes a step further: the on-chain nullifier carries no signature at all, only what they call a "degriefer". Pre-quantum that's more than Shielded CSV's 64 bytes, but post-quantum it's much less.
Unlike Shielded CSV, which operates on top of Bitcoin, Compact is its own blockchain. That matters for the degriefer: a Compact miner who includes a nullifier with an invalid degriefer can't claim the block reward. Shielded CSV could adopt the degriefer, but on Bitcoin there is no such penalty. Anyone who sees your nullifier before it's confirmed can front-run it with bogus copies for ~100 bytes of fees each, and your spending proof then has to show for every one of them that it's invalid. This is something we deliberately avoided in the design of Shielded CSV. With PQ signatures as large as they are, it probably is a reasonable trade-off.
Compact also never discusses reorgs, which are a significant part of the Shielded CSV design. Integrating the degriefer into Shielded CSV would require combining it with the existing reorg handling.
arxiv.org/pdf/2609.32015

BitDevsNYC retweeted

Fresh research article on Tibane.net just dropped about the spy chipped Ledger happening! 😸
Read it here: tibane.net/research/ledger-n…


I've put together a research page on the Ledger implants I've found in order to organize my findings and future research. The next steps will be to analyze each SIM card as well as each MCU (firmware extraction, etc).
tibane.net/research/ledger-n…

BitDevsNYC retweeted

Ledger is investigating reports of loss of funds from users in South East Asia who purchased products from a reseller named CryptoBillis. As a precaution, and pending the results of our investigation, we have asked CryptoBilis to pause all sales and shipments of Ledger devices. We recommend Ledger users who purchased from this reseller in the last 90 days to not initiate set up if you have not done so yet. If you have set up your Ledger device, consider moving assets to a new Ledger signer (with new seed). We will continue to inform customers of updates as the investigation progresses.
Reach out to Ledger customer support through official channels with any questions: support.ledger.com/
BitDevsNYC retweeted

Two Bitcoin security researchers on Justin Drake's "bunker mode" call, asked separately:
⛓️ Chaincode Labs' Antoine Poinsot:
"I think that there is no evidence for the claim."
"When there is real basis for the fear, they may just not trust the security researchers anymore."
⚡️ Mara Foundation's Isabel Foxen Duke:
"There was a bit of a leap to this conclusion that because we're solving other math problems with AI, therefore cryptography is at risk."

Today I call upon the blockchain industry to calmly begin planning for "bunker mode". My personal recommendation is to set in motion a controlled mass migration of assets to fresh addresses, i.e. addresses whose pubkeys remain hidden behind a hash.
Holders, starting with large and sophisticated ones, should consider moving the bulk of their funds to addresses that have never signed a transaction. And when they do sign one, they should also move remaining funds to a new address (possibly generated from the same seed phrase).
Don't rush. While I believe there is cause for action a rushed migration would do more harm than good. Don't panic either. Moving assets to protected addresses is a simple, preventative step which does not require new cryptography or new wallets.
IMO it is now reasonable to brace for the possibility that ECDSA breaks before qday, in the worst case in months not years. By "break" I mean fast private key recovery (e.g. in one week) on available hardware (e.g. a large GPU cluster).
Recent days have been humbling for human mathematical intuition. Long-held, unquestioned hypotheses have fallen. This includes the n log(n) bound for integer multiplication and the 3SUM conjecture. In hindsight, May's unexpected disproof of the Erdős unit distance conjecture was our warning shot.
Yesterday's OpenAI drop made it clear that mathematical superintelligence is upon us. They say there are weeks where decades happen. We are about to live through weeks where centuries of mathematical progress happen. Could our magic 64-byte ECDSA signatures be too good to be true? Was it just security through obscurity all this time?
Elliptic curves feel especially vulnerable to superintelligence. Curves carry rich structure, with room for fancy tricks like Schoof, Frobenius, pairings. (By contrast, hashes are designed to minimise algebraic structure.)
Separately, as Ewin Tang can attest, an efficient quantum algorithm sometimes foreshadows an efficient classical one. We should be open to the possibility of a classical counterpart to Shor that breaks elliptic curves and RSA at once.
Also noteworthy is the striking under-representation of cryptographic breakthroughs among the 722 mathematical results OpenAI published. I've witnessed first-hand the US government censoring academic quantum cryptanalysis results. Backroom interventionism is my base case.
I urge large, sophisticated actors to lead by example. Project11's "risq list" (bitcoin-risq-list.projecteleven[.]com) is a great tracker of exposed BTC pubkeys. Binance, Bitbank, Robinhood, Bitfinex, and Tether have an opportunity to harden their cold storage. Next month I'll address institutions in London in a live Q&A (forum.ethereuminstitutional[.]org/london-2026).
Again, please do not rush. Wallets holding under 50 BTC enjoy partial cover from "Satoshi's shield", i.e. his 20K exposed addresses that hold 50 BTC each. Load-bearing signers like oracles and L2 security councils should consider rotating ECDSA pubkeys with every signed message and/or multi-signing with a hash-based schemes like SPHINCS.
Exiting bunker mode safely will require post-AI cryptography. My inclination is to go all-in on hash-based cryptography and avoid structured mathematical assumptions entirely, whether from curves, lattices, or isogenies. A single battle-tested hash (e.g. from the SHA or BLAKE families) yields plausible post-AI security.
The Ethereum roadmap on strawmap[.]org fully embraces hash-based cryptography with end-to-end formal verification as a response to the quantum threat. Those timelines must now be revisited and accelerated in light of mathematical superintelligence. I'll be pushing for maximum defensive acceleration.
BitDevsNYC retweeted
It felt great to be back at @bitcoinmagazine HQ as a guest on @watchbmtv.
I appreciated @realseanhagan and @GraceRemiTV giving me some space to talk to talk about a number of incredible people, projects, and communities from around the world, including:
@AfribitKibera
@EcoBitz_21m
@kevmakini
@MukunguFelix
@thecore21m
@bitcoinindo21
@Silatoshi_id
@bitcoinbharat_
@JimmyKostro
@btc_dada
@thebitmela
@DecentraSuze
@elsultanbitcoin
@JraissatiJorge
Enjoy!
BitDevsNYC retweeted
A new release candidate of Bitcoin Core, v32.0rc2, is available for testing.
This is a new major release, and follows v31.1.
Work-in-progress release notes are here: github.com/bitcoin-core/bitc…
Binaries are available here: bitcoincore.org/bin/bitcoin-…

BitDevsNYC retweeted
I filmed a whiteboard session...
GLASS COINS vs SHIELDED BITCOIN
∙ Key architecture and metaprotocol tradeoffs
∙ BitVM vs PIPEs (full comp of bridges)
∙ Cutting through delusion: the case for Bitcoin upgrades


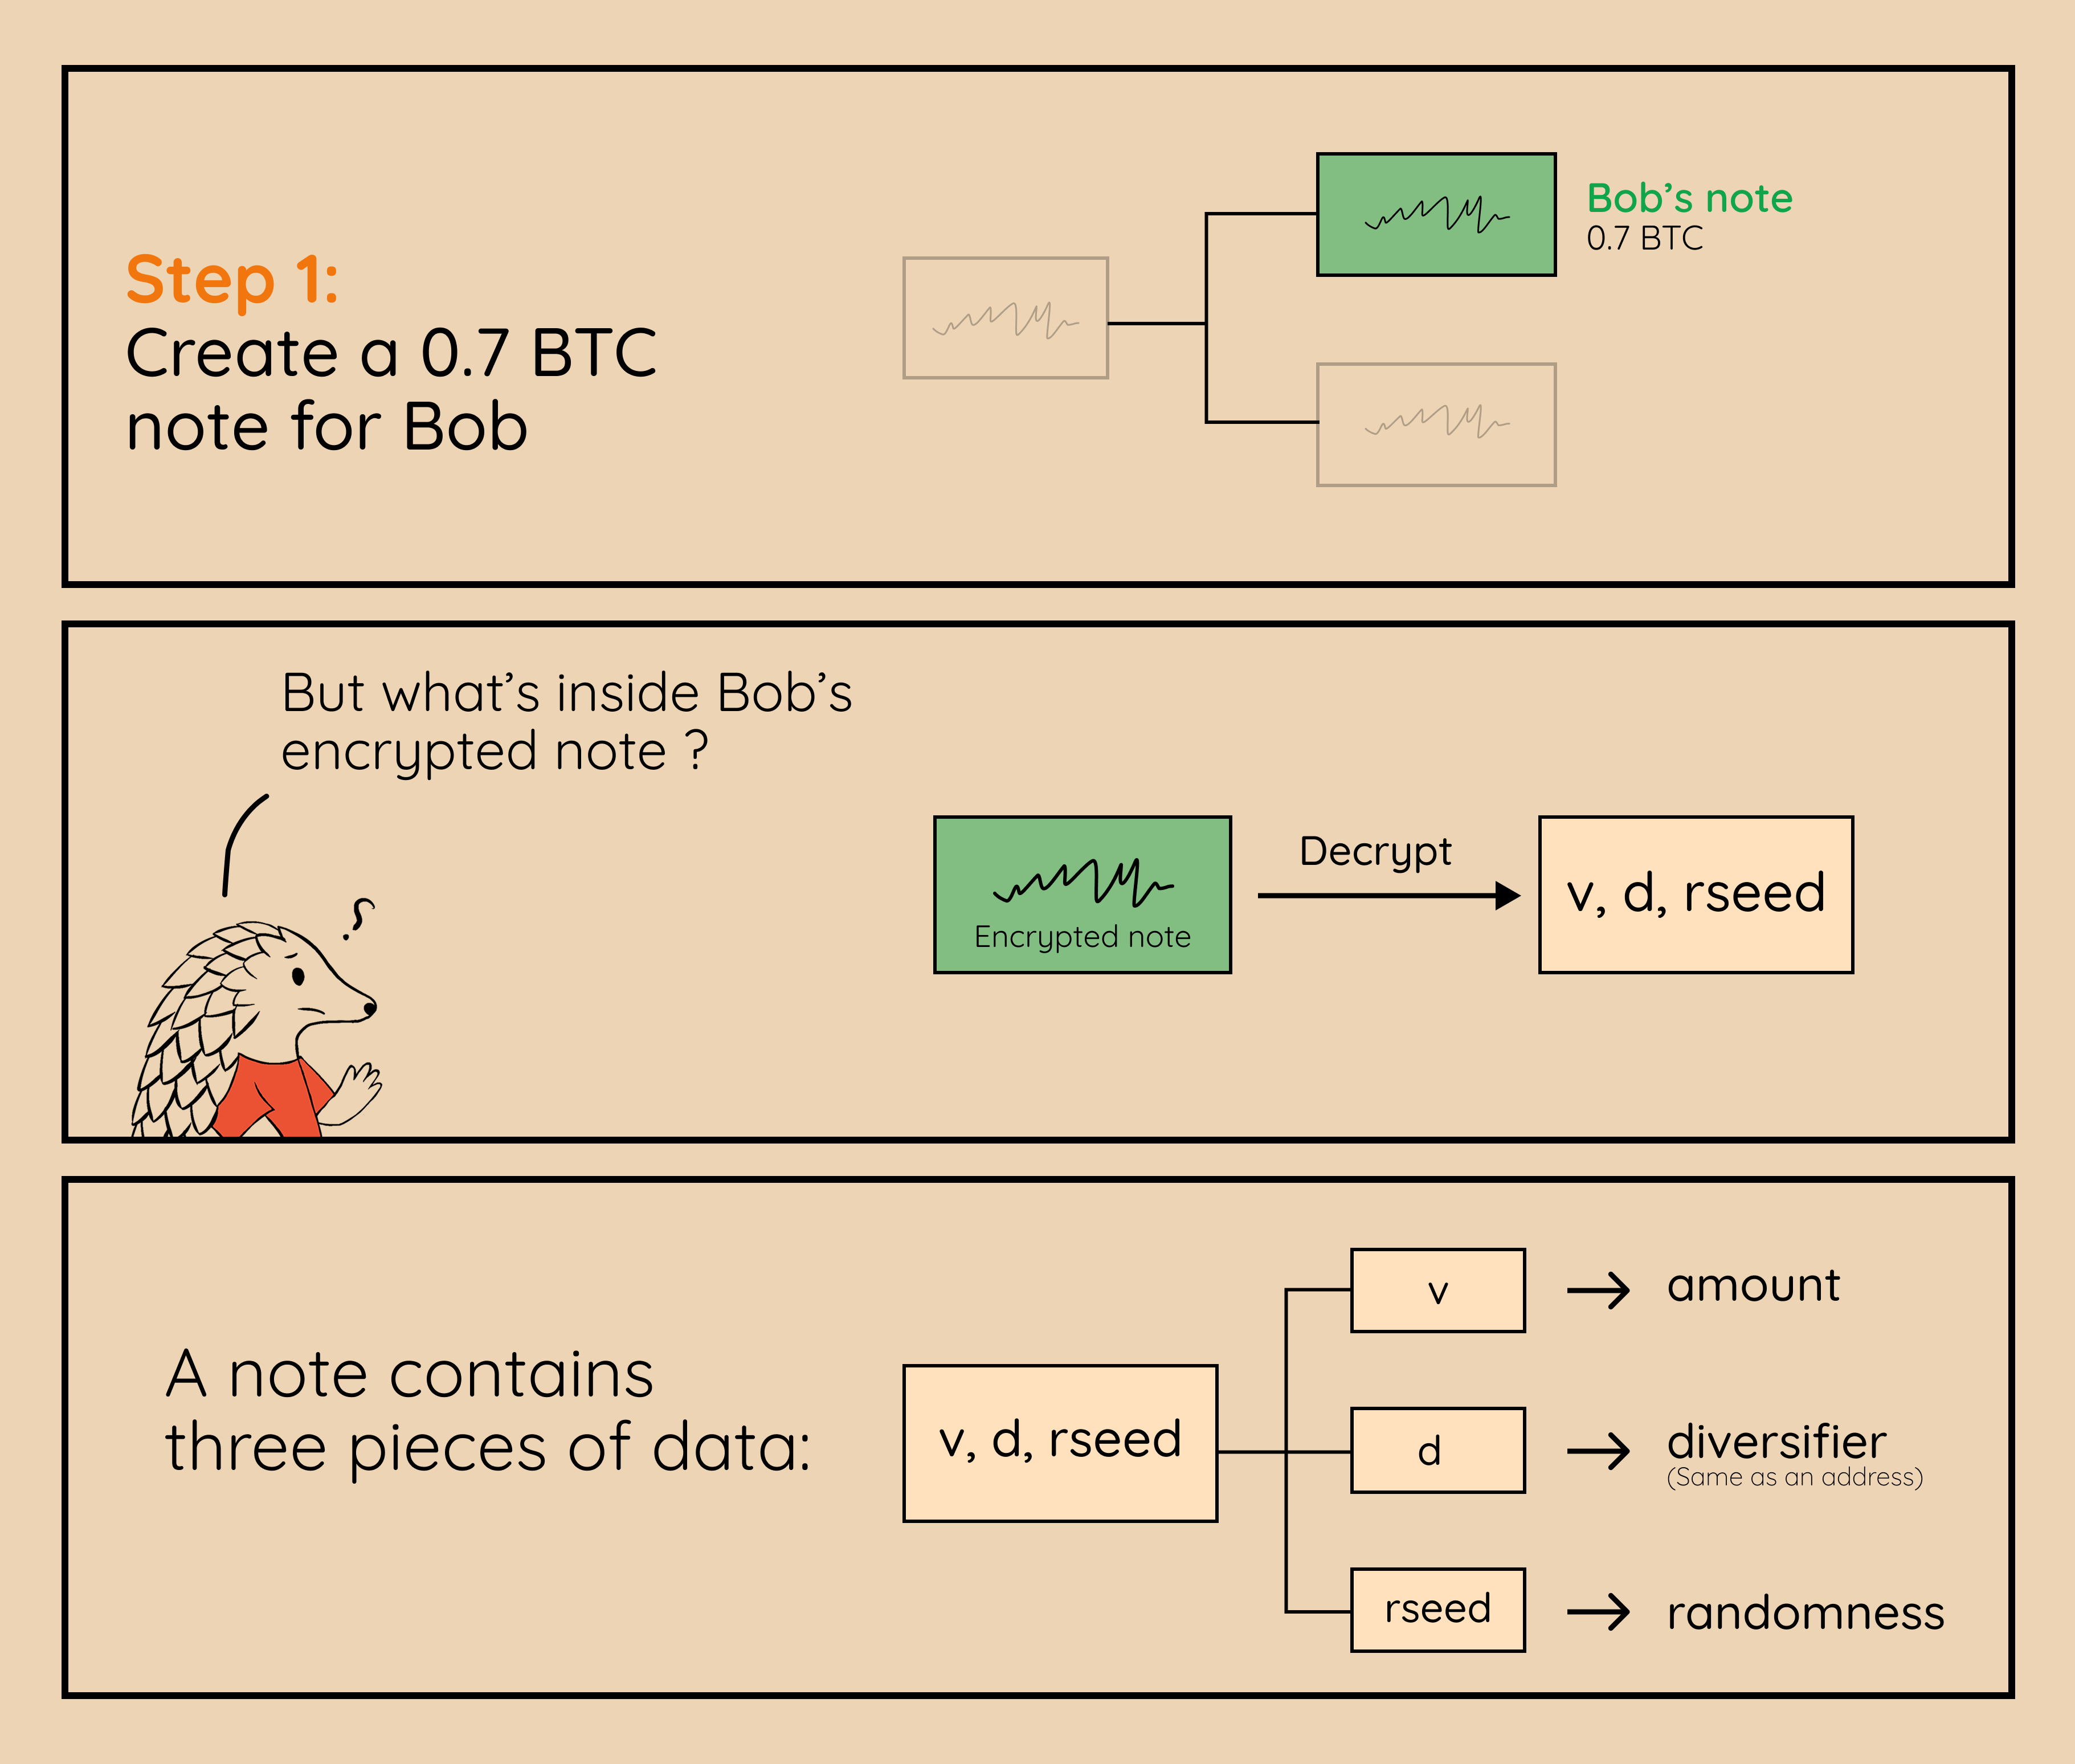
Hot! 🔥 Tonight at BitDevs, @ClaraShik will present the amazing work AllocInit has just published (today!) about private bitcoin transfers without consensus changes.
RSVP on meetup or luma:
meetup.com/bitdevsnyc/events…
luma.com/4l4jywq0


Beer, Brains and Bitcoin TONIGHT!
bitdevs.org/2026-09-24-socra…
- Liquid Hack
- Core Lightning bugs
- Consensus changes
- Bitcoin Core v32 !
- Quantum threats
- LLM threats!
- Minor miner mistakes!
See you tomorrow! 6pm at @ChaincodeLabs
sponsored by @cakewallet
RSVP on Meetup or Luma:
luma.com/4l4jywq0
meetup.com/bitdevsnyc/events…

See you tomorrow! 6pm at @ChaincodeLabs
sponsored by @cakewallet
RSVP on Meetup or Luma:
luma.com/4l4jywq0
meetup.com/bitdevsnyc/events…
🤖 Made with AI
BitDevsNYC retweeted

A Bitcoin block can carry full proof of work and still be invalid.
I've catalogued 143 established cases from 2010 to 2026, including two previously unreported F2Pool timestamp failures this year.
deadmanoz.xyz/posts/2026/inv…
1/4
