

Breach Exposure Monitoring | Smarter Privacy Starts with Awareness
Joined November 2016
- Tweets7K
- Following2K
- Followers1.7K
- Likes9.6K





BreachAware ® retweeted

🚨 DreamHost forces email and FTP/SFTP password resets during ongoing incident
DreamHost has expired passwords for some email and FTP/SFTP users following an incident affecting its webmail and File Manager services.
⠀
The company says all impacted account owners have now been emailed instructions. Affected users will remain unable to access their email or files until the account owner creates new passwords and shares the credentials with them.
⠀
DreamHost has not disclosed the cause of the incident, whether any data was accessed or how many customers were affected.
Its browser-based File Manager also remains unavailable as restoration work continues.
⠀
Account owners should go directly to panel.dreamhost.com and reset credentials under:
• Mail > Manage Email
• Websites > SFTP Users & Files
DreamHost warns that it will never request passwords by email or direct customers to sign in through an emailed link.


BreachAware ® retweeted

The critical PHP security issue highlights the importance of understanding your organisation’s attack surface.
The NCSC’s guidance can support your organisation to navigate a vulnerability patch wave and respond with greater confidence.
Learn more:
ncsc.gov.uk/blogs/prepare-fo…

ALT Is your organisation ready for a vulnerability patch wave? Organisations must act now to prepare for a wave of patches that will address decades of technical debt.


BreachAware ® retweeted

OpenAI’s dirty deeds Down Under included security bypass attempts, using exposed keys, source code siphon theregister.com/ai-and-ml/20…

BreachAware ® retweeted

Today, our partners at the Dutch National Police announced the arrest of one of the alleged leaders of ShinyHunters, a group linked to cyberattacks in the United States, the Netherlands, and around the world.
The Dutch High-Tech Crime Unit arrested the suspect under Dutch law. That's exactly how the "best athlete" model in the new FBI Cyber Strategy is meant to work: the partner with the strongest authority and access leads.
The @FBI is grateful to everyone who has assisted us in the ShinyHunters investigation, especially the Dutch National Police and the industry partners who shared information with us.
BreachAware ® retweeted
ShinyHunters has told 404 Media that they don't intend on publishing the FBI data...
404media.co/fbi-hackers-say-…


Don’t let the headline wag the dog!
The headline figure was more than 21 times higher than the apparent number of individuals involved.
lnkd.in/p/es2x_-5u

"Trust may depend less on whether you were attacked and more on what you do, and what you tell people and when you discover it. Stay tuned. Our clients know now."
lnkd.in/p/e26FtT7M

BreachAware ® retweeted

Chinese-speaking hacker used AI agents to steal 600,000 credit cards qz.com/chinese-hacker-ai-age…

Why look at a BreachAware scan? Not because it makes you NIS2 compliant.
It doesn’t.
NIS2, the UK Cyber Security and Resilience Bill, DORA and NIST are all pushing in the same direction:
Exposure tells you what has escaped.
That is not compliance. breachaware.com/scan

BreachAware ® retweeted

Ransomware Operator Claims - Week 37 2026
167 Ransomware Victims tracked
dbdigest.com/2026/09/ransomw…
#databreach #databreaches #databreachesdigest #dataprivacy #GDPR #cybersec #cybersecurity #infosec #informationsecurity #cyberattack #hacked #malware #phishing #ransomware #ROCreport

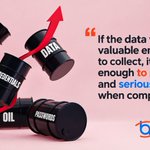
Data is oil when we own it, but sand when we lose it. Strange how quickly value disappears when accountability arrives.
lnkd.in/p/eE-b9H3s


BreachAware ® retweeted
Actively exploited vulnerabilities CVE-2026-72529 and CVE-2026-72530 pose severe risks to federal systems. More details: cnews.link/trueconf-vulnerab…

BreachAware ® retweeted

🚨 Microsoft Entra ID CVSS 10.0 Vulnerability Reported as Actively Exploited
A maximum-severity vulnerability affecting Microsoft Entra ID has been disclosed, with Microsoft reportedly indicating that the vulnerability is being actively exploited.
Tracked as CVE-2026-69836, the vulnerability involves deserialization of untrusted data and can allow an unauthorized attacker to execute code over a network.
* CVE: CVE-2026-69836
* Product: Microsoft Entra ID
* Severity: CRITICAL
* CVSS: 10.0 — assigned by Microsoft
* Weakness: CWE-502 — Deserialization of Untrusted Data
* Attack Vector: Network
* Authentication Required: None
* User Interaction Required: None
* Potential Impact: Remote code execution
* NVD lists Microsoft Entra as affected and classifies the product as an "Exclusively Hosted Service"
* CERT-FR issued advisory CERTFR-2026-AVI-1074 on August 21
* CERT-FR explicitly states that Microsoft reports CVE-2026-69836 as actively exploited
⚠️ Important Clarification:
NVD is still enriching the vulnerability record.
The current CISA SSVC information displayed through NVD lists exploitation as "none," so it would be premature to claim that CISA independently confirms active exploitation or that the vulnerability has been added to CISA's Known Exploited Vulnerabilities catalog without additional confirmation.
⚠️ Analyst Note:
The combination of CVSS 10.0, network accessibility, no authentication requirement and no required user interaction makes this an exceptionally important identity-security vulnerability.
Because Entra ID sits at the center of authentication and identity infrastructure for many organizations, defenders should review Microsoft's guidance immediately and assess any recommended remediation or mitigation.
Official Sources:
NIST NVD:
nvd.nist.gov/vuln/detail/cve…
Microsoft MSRC:
msrc.microsoft.com/update-gu…
CERT-FR:
cert.ssi.gouv.fr/avis/CERTFR…
#DDW #Microsoft #EntraID #CVE #CyberSecurity #Vulnerability #ThreatIntelligence


BreachAware ® retweeted
A hacker pretending to work for a leading cryptocurrency news website targeted several cybersecurity professionals using Google Docs as a way to deliver malware.
spr.ly/6017B1ckGv

