
My brain could not registered what happened when I read this rule. If you know 😅
🚨 𝗡𝗲𝘄 𝗪𝗣𝟮𝗦𝗵𝗲𝗹𝗹 𝗪𝗼𝗿𝗱𝗣𝗿𝗲𝘀𝘀 𝗖𝗼𝗿𝗲 𝗙𝗹𝗮𝘄
Unauthenticated attackers can remotely execute code on WordPress sites via a simple anonymous HTTP request. Critically, this vulnerability exists in 𝗪𝗼𝗿𝗱𝗣𝗿𝗲𝘀𝘀 𝗰𝗼𝗿𝗲 𝗶𝘁𝘀𝗲𝗹𝗳 — meaning even a bare installation with zero plugins is exploitable.
A public 𝗪𝗣𝟮𝗦𝗵𝗲𝗹𝗹 𝗽𝗿𝗼𝗼𝗳-𝗼𝗳-𝗰𝗼𝗻𝗰𝗲𝗽𝘁 (𝗣𝗢𝗖) has already been released, escalating the risk. Defenders are now racing against time to identify vulnerable WordPress deployments, especially 𝗶𝗻𝘁𝗲𝗿𝗻𝗲𝘁-𝗳𝗮𝗰𝗶𝗻𝗴 𝗶𝗻𝘀𝘁𝗮𝗻𝗰𝗲𝘀 susceptible to exploitation.
To help close this gap, I’ve built a straightforward 𝗪𝗣𝟮𝗦𝗵𝗲𝗹𝗹 𝗘𝘅𝗽𝗼𝘀𝘂𝗿𝗲 𝗗𝗲𝘁𝗲𝗰𝘁𝗶𝗼𝗻 𝗞𝗤𝗟 query that enables defenders to quickly assess their environment and pinpoint at-risk installations.🫡
detections.ai/share/rule/4l6…
#Cybersecurity #WP2SHELL #AttackSufaceReduction
40
New drop in the RMM forensics series: Action1. 🐔
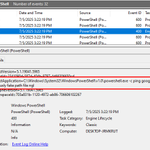
I dug into what it drops, what it spawns, and what survives a remote uninstall (spoiler: the logs snitch, and there's a firewall rule that outlives the agent).
chicken0248.fyi/research/act…
Chicken retweeted
For the IT admins & security folks who are unaware...
In Windows Server 2025, RPC over named pipes (via SMB) for the Print Spooler is disabled by default. I believe this started with Windows Server 2022 23H2 and up.
Also EFS is now similar to WebClient where it can be targeted but has to be activated first. There's a netexec module to perform this one for inquiring minds...
It's also common to see DFS on Domain Controllers but of course it's not enabled by default.
So tools like Coercer seem to not be too successful against Server 2025 in basic out of the box configurations.
Chicken retweeted
WHQL-signed kernel driver with a full network-accessible backdoor
wskmon.sys registers a WFP stream callout, intercepts inbound TCP traffic, searches for a custom NTF packet, verifies HMAC-SHA256, decrypts the payload, and executes commands from kernel context.
- No IOCTL.
- No user-mode agent.
- No injected DLL.
Any inbound TCP service can act as transport. In our demo, a simple Python HTTP server receives a POST request while the driver already processed the payload below it.
Nice reminder that “WHQL-signed driver” does not mean “safe driver”
Full analysis
nextron-systems.com/2026/06/…
Chicken retweeted
Time for another giveaway!
We will pick 6 winners to win one of the following:
1x Annual VIP @hackthebox_eu Licence
5x @PentesterLab 3 Month Licences
To enter:
1️⃣ Follow us @BugBountyDefcon
2️⃣ Like this post ❤️
3️⃣ Re-tweet this post 🔁
Giveaway open until Monday June 15th! GOOD LUCK!
Replying to @OX__Security
@OX__Security has done some vibe research and apparently I am a criminal now for using hacker cat emoji. Thanks, I guess?
Chicken retweeted
我终于明白为啥最近很多人都在说,GPT和Claude突然变笨了,
昨天OpenAI和Anthropic同时发布了官方提示工程指南,
看完我才发现,并不是模型变笨了,
是它们终于聪明到,不再容忍人类懒得想清楚了🤣🤣🤣
而且最有意思的是,
两个模型的进化方向,居然是完全相反的,
Claude Opus 4.7变得越来越字面,
以前它会主动帮你补全模糊的指令,
现在你说什么它就做什么,多一个字都不会猜🤣🤣
GPT-5.5变得越来越自主,
以前你要手把手教它每一步怎么做,
现在你只要告诉它你想要什么结果,它自己会选最优路径,
所以老提示失效的原因也完全相反,
用在Claude上的模糊提示,会得到越来越窄的输出,
用在GPT上的详细流程,会变成多余的噪声,
过去三年我们一直在学怎么教模型做事,
现在反过来了,
模型开始要求我们,先把自己的思考结构化,
其实就是提示工程的本质,
已经从教模型怎么做,变成了先把自己想明白,
所以真正的瓶颈可能不是模型的能力,而是写提示的那个人的思考清晰度,
我感觉以后赢的人,不会是提示写得最长最复杂的人,而是那个最知道自己真正想要什么的人🤔
Chicken retweeted
All EZ Tools have been updated! New version is 2026.5.0 across the board.
Nuget updates, control updates, bug fixes and general refreshing of everything.
Enjoy!!
#dfir
Chicken retweeted
🔵 BlueSky Ransomware — 50% Off This Weekend
To celebrate the upcoming release of our new DFIR Labs case, RomCom RAT Results in Domain Compromise, we're putting our most popular lab on sale.
Based on our public case SQL Brute Force Leads to BlueSky Ransomware — MSSQL brute force, Cobalt Strike, Tor2Mine, and network-wide ransomware in under 32 minutes. ⏱️
💸 50% off through the weekend. Price reflected in cart.
🗓️ Pay now, activate anytime within the next 3 months.
🔗 store.thedfirreport.com/prod…
Chicken retweeted
Kedar Shashikant Pandit & Prathamesh Shingare at Point Wild uncover a fileless Remcos RAT chain that starts with a phishing email and a ZIP disguised as a business document. pointwild.com/threat-intelli…
Chicken retweeted
Concrete jungle where hackers are made of 🎤
Here are the pieces of content coming to the #HackTheBox platforms this week!
🔵 Liberty, a Sherlock created by chicken0248
🔴 VariaType, an HTB Season 10 Machine, created by WackyH4cker
🔴 GameLoader, a Challenge created by pakcyberbot
Find them on #HTB Labs and Enterprise Platform: okt.to/HhOLJD
#Cybersecurity #InformationSecurity #NewRelease #Hacking #CyberSkills
One of the best deal I could ask for
🤝 We’ve partnered with @13CubedDFIR to level up your #DFIR training.
🔹 DFIR Labs users: Finish a quiz & get $100 OFF 13Cubed courses.
🔹 13Cubed users: Buy "Investigating Windows Endpoints" & get 20% OFF DFIR Labs!
👉 training.13cubed.com/
👉 dfirlabs.thedfirreport.com
47
📣 I partnered with @13CubedDFIR for a Valentine's Day Giveaway! 🎁
🏆 1 Grand Prize winner will receive one course of their choice from the list below + a 13Cubed Investigator T-Shirt.
Courses:
- Investigating Windows Endpoints
- Investigating Windows Memory
- Investigating macOS Endpoints
- Investigating Linux Devices
Each course comes with a Certificate of Completion as well as Certification attempts.
👕 5 winners will receive 13Cubed Investigator T-Shirts.
To Enter:
✅ Like
✅ Comment with the name of the course you want to win
✅ Repost
On Valentine's Day (February 14th, 2026) entries from across three social media platforms will be combined and winners will be selected.
For more info check out:
13Cubed Courses: training.13cubed.com/
Certification Information: training.13cubed.com/certifi…
T-Shirts: shop.13cubed.com/
#DFIR #DigitalForensics #IncidentResponse
Chicken retweeted
Big giveaway.
- (x3) Certified Red Team Expert (CRTE)
- (x3) Certified by Altered Security Red Team Professional for Azure (CARTP)
- (x10) Malware Analysis for Hedgehogs Bundle
CTRE and CARTP sponsored by @nikhil_mitt
Malware Analysis sponsored by @struppigel
Leave a comment below on what you'd like. Winners chosen in 24 hours.
Chicken retweeted
Researchers from Bitdefender revealed that a fake Leonardo DiCaprio movie torrent for "One Battle After Another" is spreading the Agent Tesla malware through a complex PowerShell chain, exploiting the film's popularity as a cybercriminal lure. bitdefender.com/en-us/blog/l…
Chicken retweeted
Giveaway.
@nikhil_mitt has sponsored THREE (x3) CRTP (Certified Red Team Professional) vouchers.
- 30 day on-demand course
- Attack & Defend labs
- Lab access
Comment below for a chance to win. Winners selected in 24 hours.
Pic unrelated
Chicken retweeted
Giveaway.
@Cyb3rMonk has sponsored FIVE "Hands-On KQL for Security Analysts" courses. The course graphic also has a very silly cat wearing KQL swag. Very cool.
Leave a comment below for a chance to win. Winners select in 24 hours.
More information: academy.bluraven.io/course/h…
Chicken retweeted
Giveaway.
Thank you @mrd0x for sponsoring this.
We've got FIVE @MalDevAcademy vouchers. These vouchers are bundles. This vouchers give you:
- Full access to malware source code database
- Full access to malware development course
Comment below for a chance to win.
Chicken retweeted
❄️ FrostByte goes LIVE tomorrow!
From 5th December to 9th January, you can jump into five brand-new winter-themed labs and completing them could win you a BTLO subscription.
Swipe to see how the competition works and what you can win 👇
🏆 Register on the FrostByte event page
🧪 Finish at least 2 labs to enter
🔁 Want more chances? Every extra lab = extra entries
Top prizes: 12-month, 6-month, and 3-month BTLO subscriptions.
Ready to sharpen your skills this winter: blueteamlabs.online/frostbyt…
#BTLO #FrostByte #Cybersecurity

ALT Promotional image for Blue Team Labs Online event from December 5th to January 9th, featuring prizes for 1st, 2nd, and 3rd places. First place receives a 12-month subscription, second place a 6-month subscription, and third place a 3-month subscription, each represented by stylized icons of flames in varying sizes and colors.
Chicken retweeted
Giveaway.
@Level_Effect has gifted us 5 x SOC Analyst Tier 3 Bundles
> Takes you literally from how Windows boots up, to Tier 2-3+ levels of triage, remediation, and prevention.
> Includes Virtual SOC training handling tickets in a case management platform.
> Courses have vouchers to their exams including CDCP cert which is a 1 week practical, no multiple choice, report-deliverable certification exam that is manually graded
Leave a comment below for a chance to win. Winner will be selected in 24 hours.
Course information: training.leveleffect.com/bun…


