

Information security | VAPT | OWASP Kathmandu Chapter Leader
Kathmandu, Nepal
Joined December 2012
- Tweets1.6K
- Following507
- Followers1.2K
- Likes2.8K





Oops! retweeted
Introducing Burp AT.
Agentic AI for human-led pentesting, with Burp Suite’s proven tools, your project context, and purpose-built skills.
Now live in public beta for Burp Suite Professional users.
portswigger.net/blog/introdu…

Oops! retweeted

Huge thanks to the @owasp_kathmandu (@Corrupted_brain and the team) for providing me the oppurtunity to share my findings and thoughts with the community. It was a pleasure connecting with everyone there. Looking forward to more such events in the future!
Oops! retweeted

Thank you Ullens College @Bugcrowd @AlteredSecurity @Hacker0x01 @apisecu NCA Nepal Rovix Cloud stickermandu🙏🇳🇵
A huge appreciation to all the amazing speakers, volunteers, & participants who made this event possible! 🎉
We look forward to organizing another event together soon!

Oops! retweeted

Had a really great time talking at @Steel_Con
Giving talks, meeting people, playing games and stuffs. Fun times!


Oops! retweeted
Slides from our (w/@bishal0x01 ) talk at @owasp_kathmandu "Breaching The Perimeter - Our Most Impactful Bug Bounty Findings" is now up. Shout out to the OWASP KTM organizers @smaranchand @Corrupted_brain for another grand event!! 🔥🔥
#BugBounty #owasp
docs.google.com/presentation…

Oops! retweeted
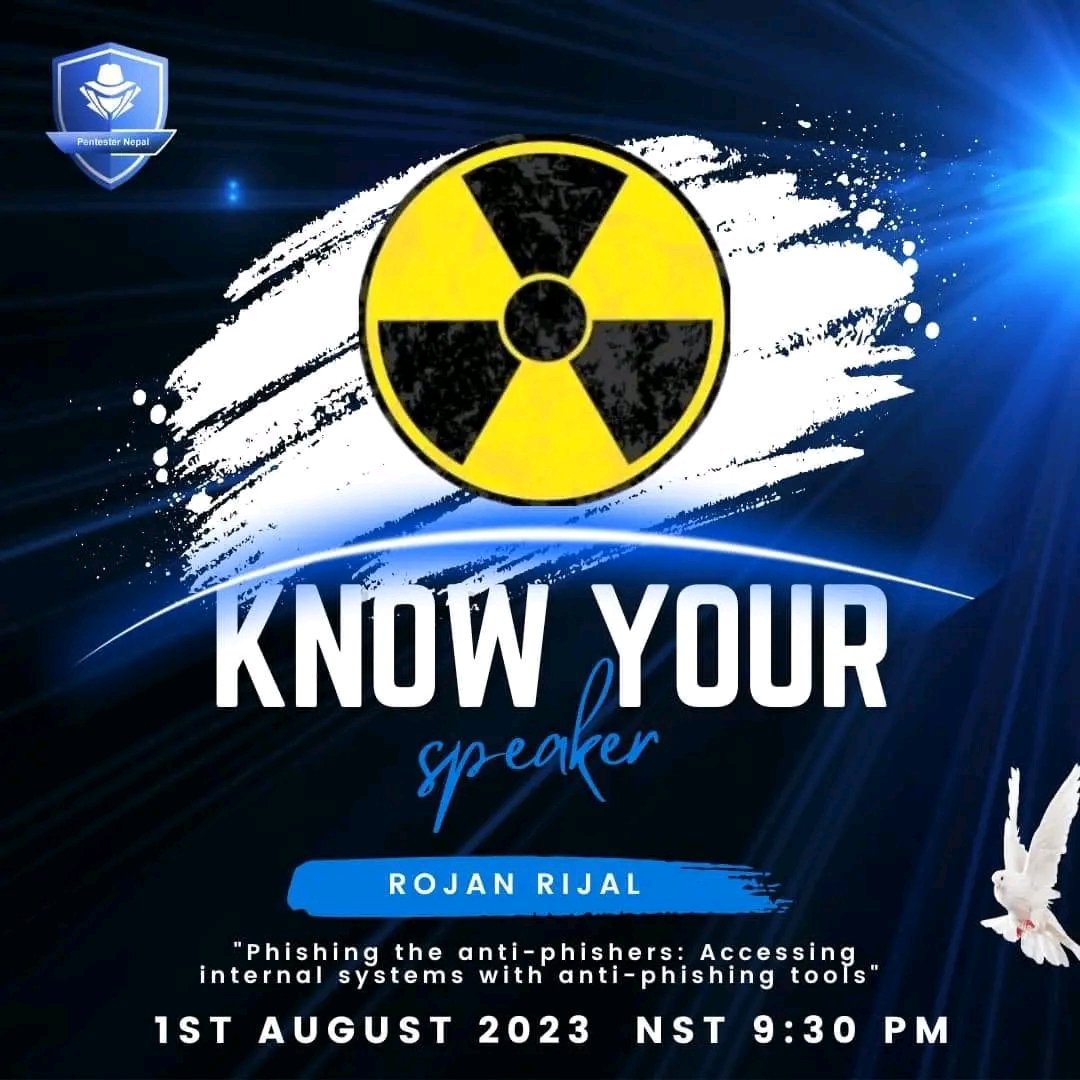
Mr. Rojan Rijal also known as @uraniumhacker, will be giving his talk on "Phishing the anti-phishers: Accessing internal systems with anti-phishing tools". He is Security Researcher at Ophion Security.
This virtual talk will be streamed live on our official Facebook page.
Oops! retweeted
We hosted two in-person hacking events on July 9th and July 15th for the quarter-finals. This round was extremely fun!
Thanks to @Hacker0x01 and @vairavtech for sponsoring the events.
#AmbassadorWorldCup #togetherwehitharder #bugbounty


Oops! retweeted

I've tried to cover my knowledge on insecure Deserialization on php, you can find it here:
medium.com/pentesternepal/de…
#bugbountytips #bugbounty

Oops! retweeted
Here’s How We Exploited the GitHub Workflow: A Walkthrough of @owasp_kathmandu CTF
veshraj.medium.com/heres-how…
#ctf #cybersecurity #owasp

Oops! retweeted

Our team veryverynoob won @THREAT_CON CTF by securing 5654 points. Great teamwork and coordination made this possible. #threatcon2022


Oops! retweeted
Hi @Hacker0x01 My dear friend @Corrupted_brain desperately needs a hackerone hoodie. We rode around 1.5 hr to get this picture. Would be glad enough if there is any provision to have one. 😀

Oops! retweeted

Come be a part of #THREATCON2022 and not only get involved with #infosec beneath the Himalaya 🏔️ but experience beauty and adventure like never before🤩
This is what waits for you in #Nepal.
youtu.be/nYfUfrmWb94
Oops! retweeted

How I chained two client side vulnerabilities to steal credit card details? Here is the write up of a security assessment I have done recently. I have put the entire report as a blog post as it is. I hope it is helpful.
codedbrain.com/how-i-chained…
Oops! retweeted
📢📢Calling for papers/workshops/tools for THREAT CON 2022!!
Submit your proposals by June 20 to be a part of #THREATCON2022 and present your research to the world.
threatcon.io/cfp
threatcon.io/cft
threatcon.io/cfw
#CFP #cybersecurity #infosec

Oops! retweeted

CVE-2021-46065 A Cross-site scripting (XSS) vulnerability in Secondary Email Field in Zoho ManageEngine ServiceDesk Plus 11.3 Build 11306 allows an attackers to inject arbitrary JavaScript code. cve.mitre.org/cgi-bin/cvenam…
Oops! retweeted
Sharing my thoughts about the Application Security & VAPT project I recently accomplished. An exciting discovery by correlating the vendor's malpractice.
smaranchand.com.np/2022/01/o…
#applicationsecurity #pentesting #cybersecurity

Oops! retweeted
Pretty useful for the daily pentest Job,
Java Melody XSS nuclei template by @Corrupted_brain
github.com/projectdiscovery/…


Oops! retweeted

.@ryotkak found a remote code execution vulnerability in cdnjs (Cloudflare), which could've affected 1/8th of the internet: blog.ryotak.me/post/cdnjs-re…. Such a great writeup and vulnerability! #TogetherWeHitHarder
