


Douglas C retweeted

With all the outages happening, it's hard to not lean towards something larger happening. We still have no evidence of mass outages caused due to cyber.
The FBI warning around ARTEX was more of an advisory around it being used by threat actors doing active campaigns, not disruption efforts.
Most folks don't realize that our interconnected systems, predominantly because we put all of our eggs in large baskets causes much of this. Instability in large cloud providers cause not one outage, but thousands if not hundreds/millions of outages as we saw last week with Microsoft.
I know folks in almost every organization that has been impacted here, folks I've known for years - all confirming it was not cyber-related.
In stating that - is it possible? Absolutely. However, a lot of what we are seeing is hyper sensitivity - any blip is going to cause a reaction right now.
Again, can't rule out cyber attacks in any stretch, and I'm deeply concerned on what we are seeing across the spectrum from a security operations perspective and incident respond side. It is definitely elevating upward for data breaches especially with autonomous attacks.
The next 6 months are going to be rough, at the same time - we will always find a way to get better, improve, make these less impactful.
I want to emphasize again, none of these outages have been confirmed a cyber attack and have clear explanations on what has happened. Which honestly, should concern us more. It's showing how weak our infrastructure in supporting our daily lives really is, and how that can change very quickly.
We must do better.
Douglas C retweeted

Rewriting lines in Lazarus Pt 2 just to make sure this king gets well deserved creds and a drop in




Douglas C retweeted

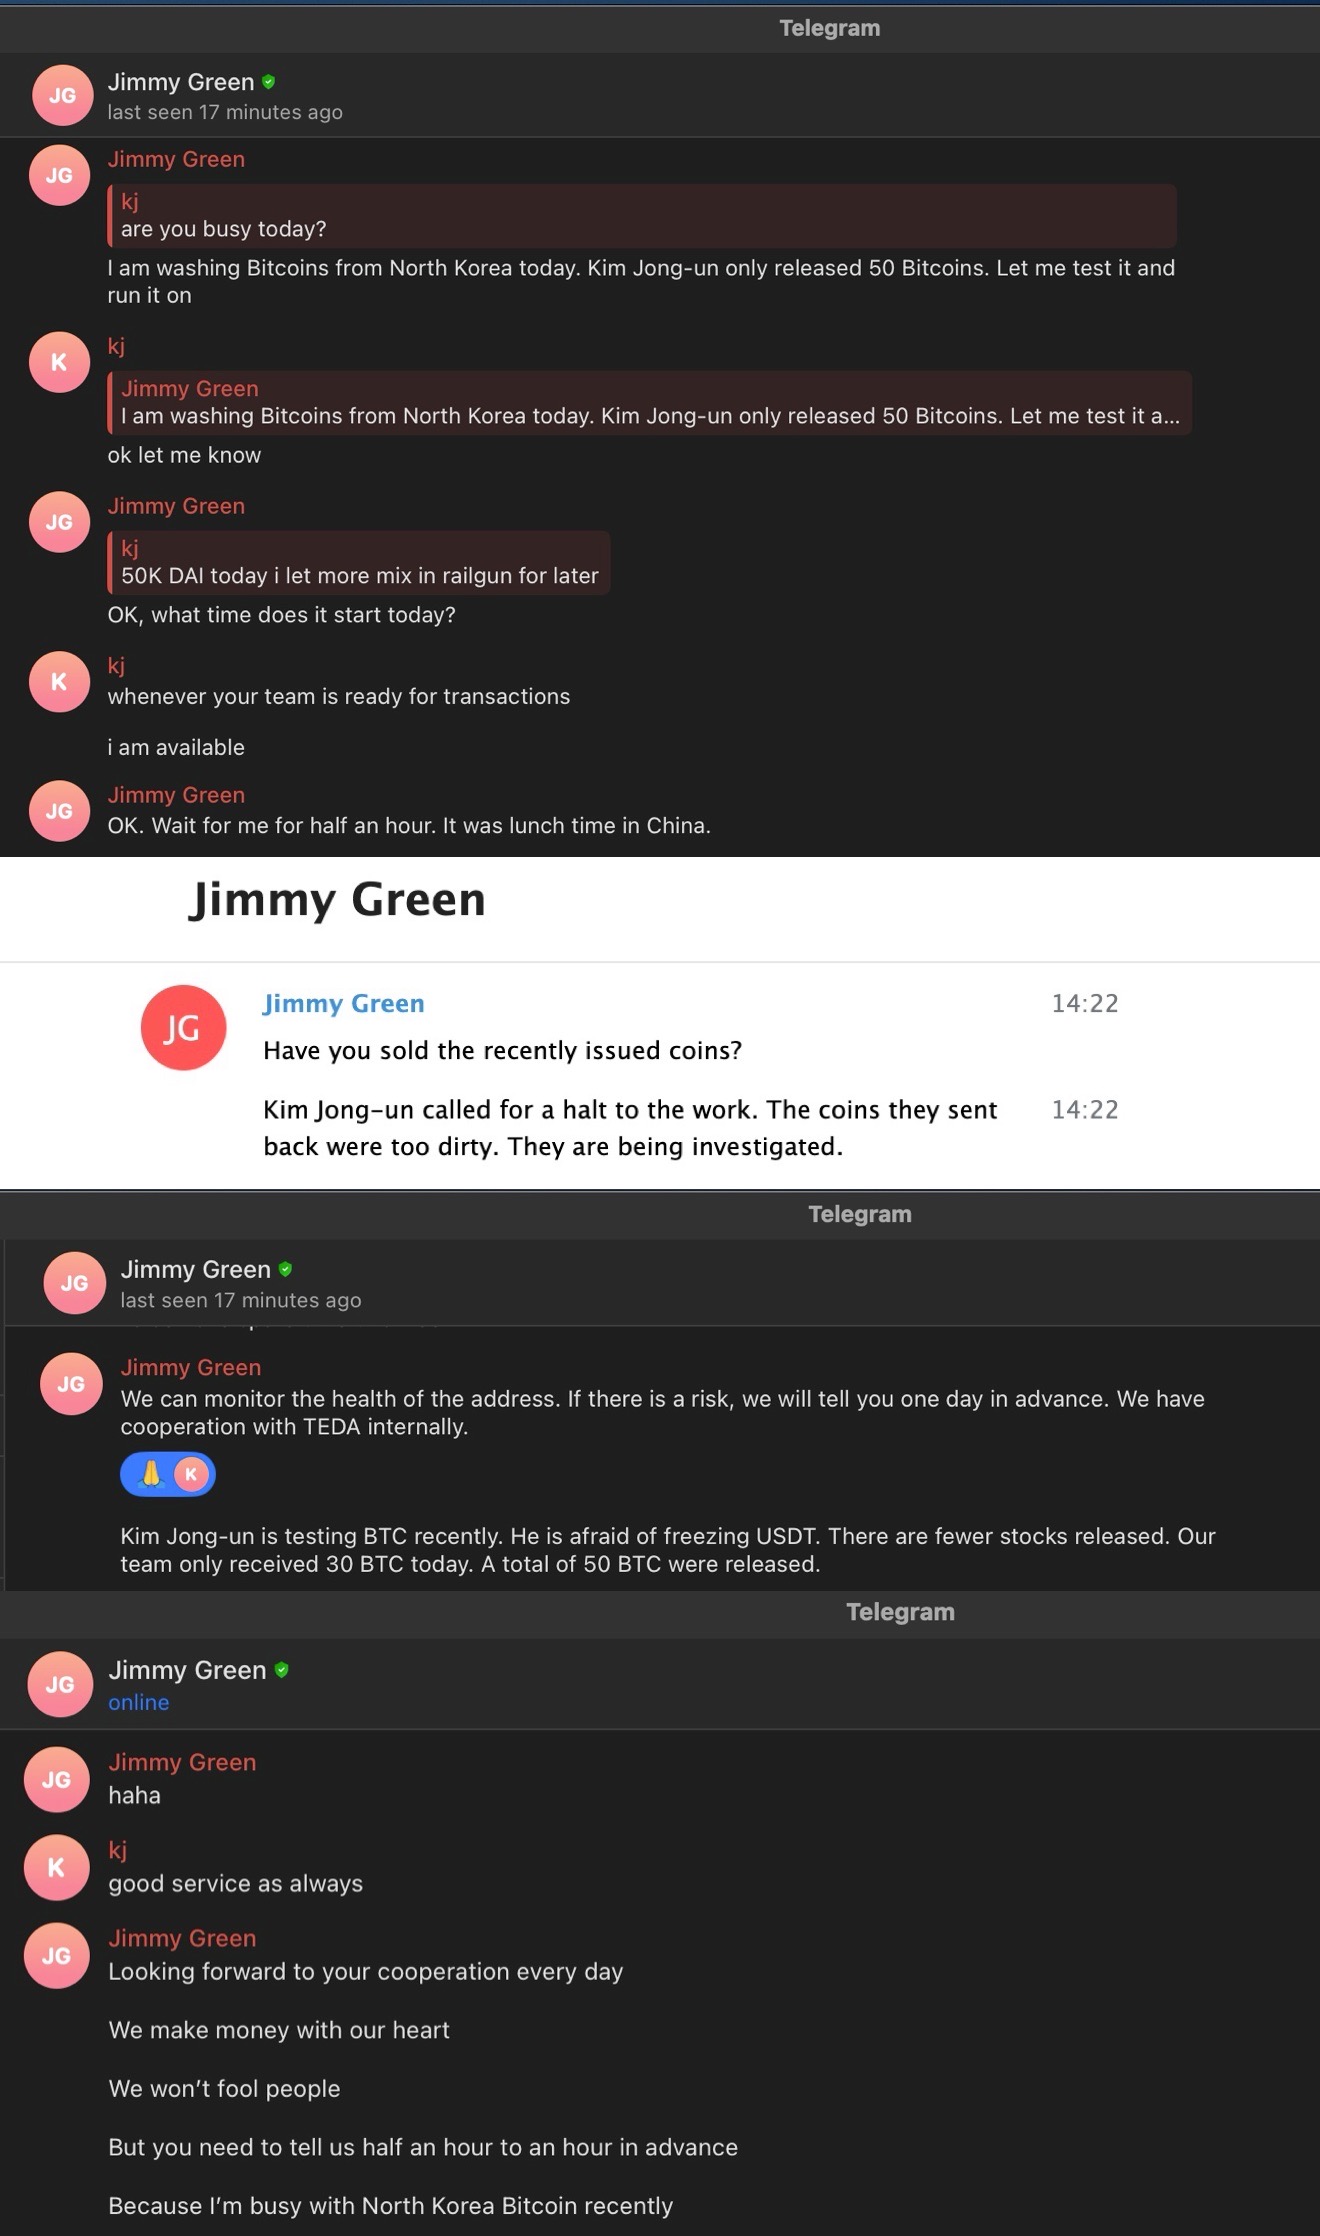
Someone shared with me a clever and crafty ClickFix lure, that smuggled in and extracted its next stage payload from the victim's web browser cache 👀
I dug into it in a video: youtu.be/oJHOlNTH7lY
🤖 Made with AI

Douglas C retweeted
NOW PLAYING
UwU Underground
"$ELL THE CAGE"
▶ ━━━━━●──────── 04:06
⇆ㅤ ◁ㅤ ❚❚ㅤ ▷ㅤ ↻
♫ BABY, BUILD THE MONSTER, SELL THE CAGE ♫
Douglas C retweeted
We're investigating an issue with users experiencing delays sending to and receiving email from external domains. We've identified the cause of the issue and are applying a mitigation which should complete shortly. Further details are provided under EX1467029 in the admin center.


Douglas C retweeted
It’s true. It works. It completely changes everything as we know it in cybersecurity.

NightBeacon CMD replaces the queue with a live entity map across endpoint, identity, data, and cloud. A saturation meter tells you, at a glance, whether you're winning. And a Peace-of-Mind panel shows you the state most teams never get to see.
On a good day, there's nothing in the queue. Alarms correlate into Situations. Analysts resolve them. What's left is quiet, plus the numbers that prove it's earned.
Quiet isn't the absence of evidence. It's the result of it.
Read the full datasheet here: hubs.li/Q04sZ95R0

Douglas C retweeted

The floor's loud. The pitches are louder. Somewhere in all of it: one idea worth actually stopping for.
Multiple alarms don't need a faster engine. They need to become one Situation.
Find us on the floor in booth 6017, or skip the noise entirely: hubs.li/Q04s7y-g0
#BlackHat

Douglas C retweeted

Howdy all,
Just my daily plug if you want one of these in time for Defcon. I'll pause ordering on Wednesday until after Defcon but if you want one for pickup at Defcon, please order before then and send me a message on Etsy for the Defcon pickup

Looking for a fun badge this conference season? Consider picking up a UwU Underground custom acrylic RGB badge today! I have 7 different hand-drawn designs for a limited run which includes a custom UwU Underground Lanyard + NFC chip for linked hidden UwU Underground goodies. Profits will go back to help UwU Underground and the community.
I can ship or give it to you at Defcon. Check out my Etsy store for details. I will only be making 20 of each badge type for a limited run.
etsy.com/shop/NodeTech?ref=d…

Douglas C retweeted
I'll be at Blackhat this week & would love to catch up! 😊 I'm open to work opportunities so please reach out if you have anything that might be a good fit. Either W2 or contract work, but must be remote from outside the US (UTC-6 timezone) where I do have legal rights to work 🤗
Douglas C retweeted
Want to drive NightBeacon CMD and see the power we've been building for over a year?
Gamified - run through an entire situation from start to finish, conduct threat hunts to identify compromised identities, see the power of what CMD really is.
Simply fill out information, get approved in minutes, and drive NightBeacon CMD.
live-demo.nightbeacon.binary…
#BinaryDefense


Douglas C retweeted
New diss track tomorrow.
While you wait, drop the worst cyber bootcamp red flags you’ve seen.
Bring receipts. Watch '90 days to six figures' enter its flop era.

Douglas C retweeted
🎀 . ݁⋈ . ݁. ݁₊🎀 . ݁ ݁Now Playing 🎀 . ݁⋈ . ݁. ݁₊ 🎀 . ݁ ݁
UwU Underground
Scams Gotta Shout To Persist
0:28 ━●────────── 04:11
◁ㅤ ❚❚ ㅤ▷
🎀 . ݁⋈ . ݁. ݁₊ 🎀BOOTCAMP SCAMS🎀 . ݁⋈ . ݁. ݁₊ 🎀 . ݁ ݁
Douglas C retweeted

Our #BSidesPyongyang2026 supreme merch store is now live: bsidespyongyang.myshopify.co…

Douglas C retweeted
The people’s cyber vanguard announces the glorious arrival of #BSidesPyongyang2026.
Douglas C retweeted
Big cybercrime is here.
Is your security team ready to defend against it?
@MsftSecIntel joins us today to talk EvilTokens and what it means for defenders when threats hide in plain sight.
May 5, 2026 | 3pm ET | 12pm PT
🎟️ Last chance to register: okt.to/8cpPKx

Douglas C retweeted

I have an open spot on my team for a Principal Threat Intelligence Analyst here at @HuntressLabs !
You will be able to help lay the foundation for our CTI program going forward. We have a lot of interesting telemetry and some hard problems to solve:
job-boards.greenhouse.io/hun…