

PhD Student @vu5ec (Systems Security). Previously: decompilers @_revng, rockets @skyward_er
───○─ 🔊
Joined September 2018
- Tweets51
- Following247
- Followers183
- Likes566

alvise retweeted

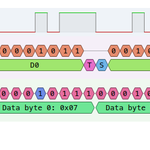
Hardware glitching masters have taken on Intel's microarchitecture - very, very cool! I'm so glad our work is contributing to research that was previously unimaginable. Research into hardware attacks on Intel processors has enormous potential...
download.vusec.net/papers/mi…
alvise retweeted
Remote code execution on a Yamaha piano.
psi3.ru/blog/swl01u/
The Spectre exploit chef @SanWieb just gave an impeccable talk at @USENIXSecurity about our work on Spectre gadgets analysis and native BHI exploitation. Very happy - and proud of the Distinguished Paper award too :)

Happy to report that our InSpectreGadget paper won a Distinguished Paper award at @USENIXSecurity:
download.vusec.net/papers/in…
@vu5ec @SanWieb @HBitmasks @c_giuffrida
Here is @SanWieb presenting the paper:

alvise retweeted

Just a few days left to apply to our PhD and PostDoc positions available at @vu5ec. If you love low-level systems hacking and would you like to work at a top systems security research group in Amsterdam, consider applying: workingat.vu.nl/vacancies/ph…
alvise retweeted
😎 We’re going to REcon 2024! 😎
This will be the first talk in which we introduce the decompiler since the open source release.
It will be very much an hands on talk. Don’t miss it.
See you in June in Montreal! ⚜️🌹☘️
cfp.recon.cx/recon2024/talk/…
If you ever happen to look for Spectre gadgets manually and feel pain and loneliness, you should check github.com/vusec/inspectre-g… ... It's been a wild ride, but working with @SanWieb was the best thing ever :) Also, BHI is back baby


Branch History Injection (BHI) is back! Disclosing Native BHI, bypassing deployed Spectre-v2/BHI mitigations (e.g., eBPF=off) to leak arbitrary kernel/host memory (e.g., root password hash below). Joint work by @SanWieb @HBitmasks @herbertbos @c_giuffrida: vusec.net/projects/native-bh…
alvise retweeted
We ended up on HN and some interesting discussions emerged: news.ycombinator.com/item?id…
alvise retweeted
Disclosing #SLAM, aka how to combine Spectre and Intel LAM (& co.) to leak kernel memory on future CPUs (demo below). Thousands of exploitable "unmasked" (or pointer chasing) gadgets in the Linux kernel. Joint work by @MatheHertogh @SanWieb @c_giuffrida: vusec.net/projects/slam


alvise retweeted

I'm thrilled to announce that our paper "Speculation@Fault" @USENIXSecurity is online! Read about how we automatically find information leakages arising from CPU exceptions by fuzzing against speculative contracts.

alvise retweeted

I am extremely happy about this paper, which is the brainchild of my PhD student @__L4w__ and my colleague @JinBlackx.
BINO addresses the irksome problem of identifying inlined functions (specifically from C++ template classes) in binaries.
authors.elsevier.com/c/1hD5K…
alvise retweeted

Debug Location coverage for the variables in the optimized binaries compiled with the newest release of LLVM look nice. A bit longer post is at djolertrk.github.io/2023/05/…. We started from 45%, and now we are at 71%, nice! @llvmorg

alvise retweeted

Should we lose hope already on Rowhammer attacks? Andrea Di Dio from Vrije Universiteit Amsterdam is showing us at #NDSS23 that it is feasible to devise a software-based design to mitigate ECC-aware Rowhammer attacks.

alvise retweeted
Disclosing CHOP, aka how attackers can bypass commodity return address protections such as stack cookies by hijacking the exception handling process. Paper to appear @NDSSSymposium: download.vusec.net/papers/ch…. Joint work by @victor_duta Fabian Freyer @pagabuc @nSinusR @c_giuffrida
alvise retweeted

Easily the highest impact bug I found (yet)

We audited SPL-Token-2022 for the @SolanaFndn. It's an update for the SPL-Token program.
In our review, we found an inflationary bug that would've allowed infinite minting of tokens for free. The audit was pre-launch. The code was not enabled, so no funds were at risk. 👇🧵

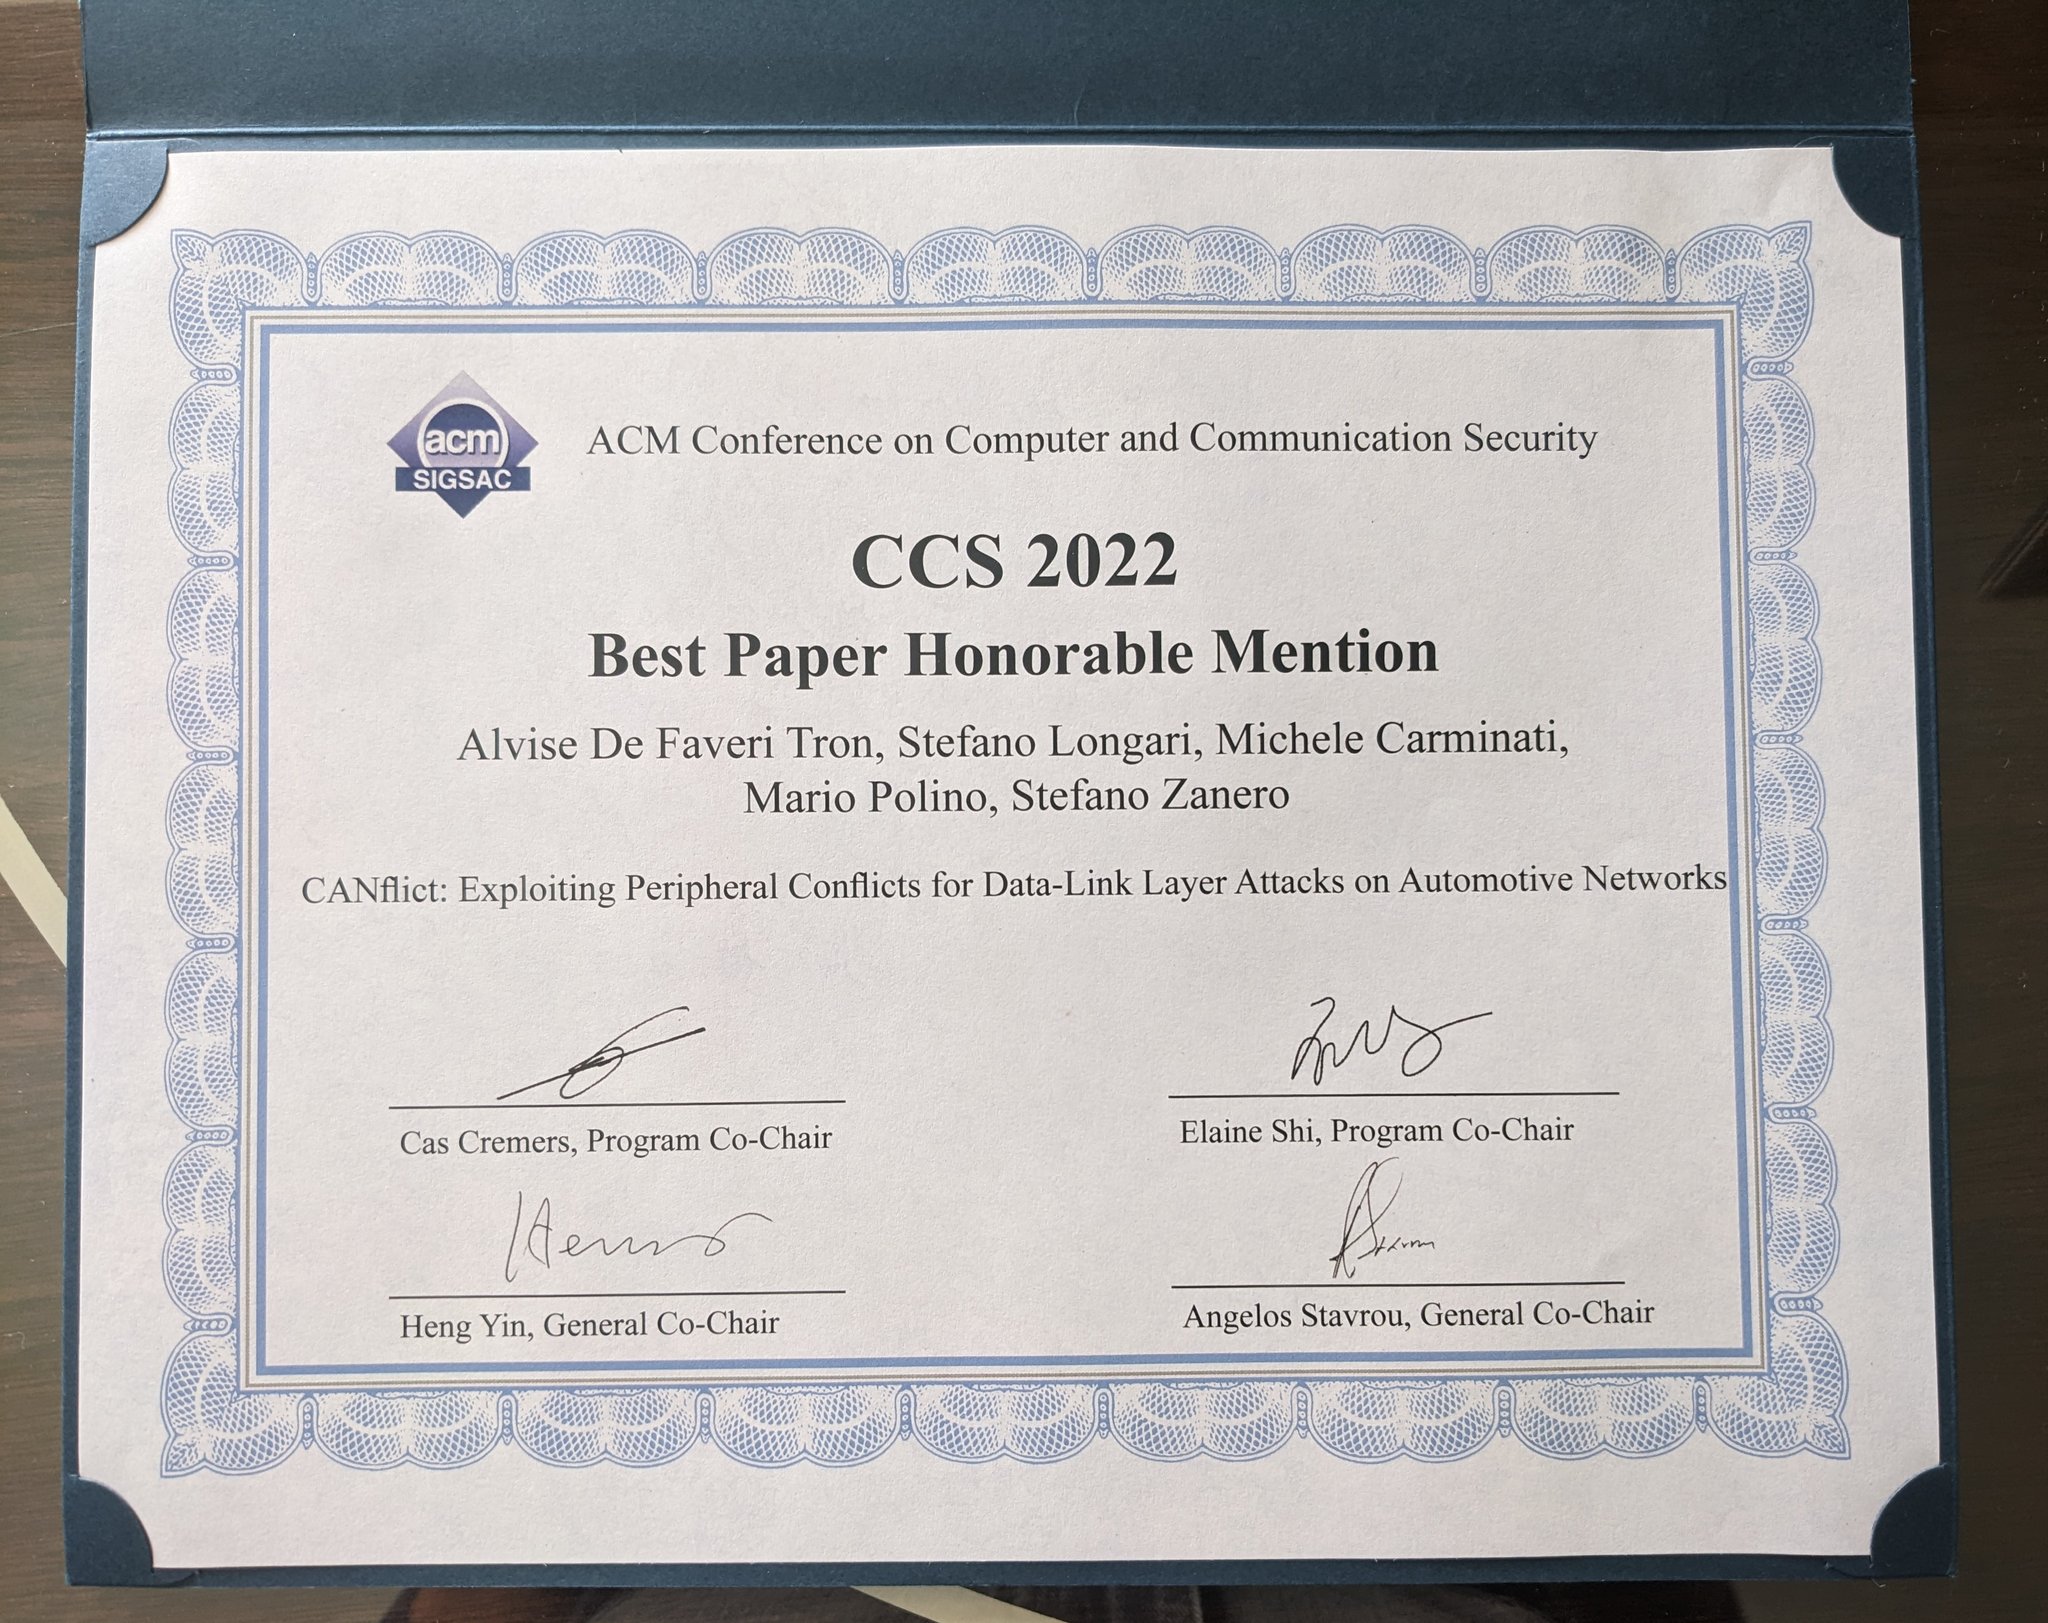
What a blast! Thanks to all my incredible co-authors @aScarecrowHat @JinBlackx @mcarminati1988 @raistolo



alvise retweeted

I am at @acm_ccs , where @HBitmasks is about to present "Canflict: Exploiting Peripheral Conflicts for Data-Link Layer Attacks on Automotive Networks".
Thanks to all coauthors: @HBitmasks, @aScarecrowHat, @mcarminati1988, @raistolo
Full paper: dl.acm.org/doi/pdf/10.1145/3…

You know what @angealbertini does with file formats, right? Well, we did the same thing with communications protocols - because, why not? 1/N


[update] We are presenting this work at @acm_ccs in a couple of weeks🥳 Come and say hi if you want to see some car hacking shenanigans :)
Paper: arxiv.org/abs/2209.09557
