

LevelBlue. Secure What’s Next.
Dallas, TX, USA
Joined February 2009
- Tweets34.4K
- Following3.5K
- Followers75.8K
- Likes12.3K





LevelBlue retweeted

Big congratulations to @LevelBlueCyber on its 2026 Global Managed Security Services Company of the Year recognition from Frost & Sullivan! 👏
Learn more: frost.com/news/levelblue-rec…

12 months of analyst research, market evaluation, customer impact assessment, and best-practice benchmarking have determined one thing: LevelBlue is the 2026 Global Managed Security Services Company of the Year, per @Frost_Sullivan! 🏅
levelblue.com/newsroom/press…

LevelBlue retweeted

🔱 We observed active exploitation attempts targeting Citrix NetScaler appliances affected by CVE-2026-88771, including activity progressing beyond basic command-execution testing.
The vulnerability allows unauthenticated attackers to inject commands through attacker-controlled authentication data that is later processed by a privileged NetScaler component, potentially resulting in command execution.
🕷️ @LevelBlueCyber THOR identified malicious authentication events containing command-injection payloads across multiple customer environments.
🕷️ Observed activity included payload retrieval, NetScaler configuration collection and staging, reverse-shell deployment, and attempted configuration exfiltration.
🕷️ Analysis of main.py identified a second-stage payload designed to overwrite customsnmpd and establish a reverse shell to attacker-controlled infrastructure.
🕷️ A separate Perl payload, update_c08937.pl, creates a privileged sec_monitor account, collects NetScaler configuration data, and deploys a PHP web shell.
🕷️ Our analysis includes observed IOCs and behavioral detection opportunities defenders can use to identify exploitation and post-exploitation activity.
Full analysis: levelblue.com/blogs/spiderla…
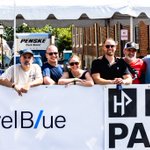
We have a thing for speed. 🚴⚡️
Proud to sponsor the Bucks County Classic and spend the day celebrating the incredible athletes, passionate fans, and thrill of competition.
Congrats to all who raced! 🏁


Saying that "bots are a security challenge" would be an understatement.
Kory Daniels explains what AI-enabled bots mean for security teams in @TechTargetNews' look at the growing rogue bot risk:
hubs.ly/Q04xtjWQ0

LevelBlue retweeted
@LevelBlueCyber #OpsIntel recently identified a new campaign exploiting trusted Electron applications. Victims were lured into executing a JavaScript file that silently downloaded a MSI installer containing a tampered #Exodus Wallet.
The MSI contains a modified #ASAR (Atom Shell Archive), a custom archive format designed specifically for #Electron applications to bundle application resources.
The initial payload is an encrypted PE loader that can be decrypted using AES-256-CBC. Once decrypted, the loader reflectively loads the RAT payload directly into memory.
🧐 IOC:
hXXp://35.212.159[.]20/setup2026.msi
e9e5b8e5aa3bf03eca0bda9d1c08f11a70e4d03bbd9e8ac27b2cc7de4f4000c2 (setup2026.msi)
a4e1513e58a5b70389a08714d97c4eb2e22f052856c1471d068451451bfe7840 (exodus_patch.js)
15836a5ab798a5955be566c0322aa9a4140662b91cdda60714ffbe5e57bfcb43 (keystorage.js)
8fa059c30b75233d1e2d1f9b289c899a112a9964a216f0ebc35514ace152a23a (index.js)
eb2d09773e5cb6eecad4bf14ed05b0c885465610a354ea0c9665ffcf56aced18 (app.asar)
56ec5bfb62e9b615b8bb949a76e1d4f6bb3f34983139f0c48cfc73b350961f1c (decrypted buffer)
lgapistorage123.table.core.w…[.]net
🔎AES-256-CBC parameters:
Key: KlABCwCvW5oplWMsSxjTlKb0o+iOK6OsxCGZZ0td/1U=
IV: 4b44GYeQwOVmpFKlbWdPVw==


LevelBlue has been named SentinelOne’s premier remediation partner for Wayfinder Frontier AI Services.
Because AI may uncover exposures at remarkable speed, but the real challenge starts after the findings arrive.
hubs.ly/Q04wzY660
LevelBlue has been named a @USNEWS 2026-2027 Best Company to Work For in 3 categories: Overall, Information Technology, and Midwest!
To every member of the LevelBlue team: thank you for making this a place where great people can do great work. 💙
hubs.ly/Q04rlm3H0

LevelBlue retweeted
Threat activity is already in motion before it gets named, tracked, or reported. #SpiderLabs stays on the moving edge, turning live activity into decisions teams can act on without slowing down. 🕷️
Threat intelligence that holds up when operations are moving at full speed: it’s the SpiderLabs standard.
hubs.ly/Q04pbnNc0
Agents are already active across your environment.
The real work is configuring them so you can actually monitor what they’re doing.
Part 1 of our Agent 365 series walks through how to set up the Microsoft stack to support real-world security operations:
hubs.ly/Q04mk17K0

If you didn’t know where to find us before at the PGA Championship, you do now. We’re only about 50 yards right of the second fairway - thanks for driving attention to #LevelBlue, Bryson DeChambeau! 🏌️⛳️👏
LevelBlue is built for what's next: relentless, AI-powered managed security to reduce noise, surface what matters, and help organizations stay resilient as threats evolve in minutes (not months). ⏱️
Watch how we help you secure what's next. ⤵️
hubs.ly/Q04984Pk0
We’re excited to announce a global partnership with @SentinelOne. 🌟
Together, we’re unifying AI‑driven detection with intelligence‑led managed security and global incident response to help organizations reduce dwell time, accelerate remediation, and strengthen resilience.
We're strongly recommending a "shields up" security approach in light of the recent United States-Israel-Iran confrontation that has spilled over into full cyber warfare. Insights below:
levelblue.com/blogs/spiderla…

LevelBlue retweeted

New Provider Announcement: @LevelBlueCyber joins Sandler Partners with a Sandler Strong Evergreen agreement—giving Partners expanded coverage in managed detection and response, threat intelligence, risk management, and compliance-driven security solutions.

This year, IoT won’t be defined by the number of connected devices, but by the trust & autonomy they deliver.
In @DigitalITNews1, Bindu Sundaresan shares how cybersecurity will be redefined & what adequate protection needs to look like.
bit.ly/45XzjUp

According to IDC, organizations now view utilizing an MDR security service not as an optional add-on, but as a board-level priority vital to maintaining operations and trust in the face of complex adversaries and growing regulatory pressure. See why 👇
bit.ly/3LZLWaM

In 2026, the most dangerous breaches won’t announce themselves.
Identity-driven, cloud-native attacks that blend in, persist quietly, & exploit trust will redefine incident response.
Take a look at what we expect compromise to look like this year 👇
bit.ly/4rsxIyv

What are the biggest cyber challenges in 2026?
Our SpiderLabs experts shared insights with @SecurityInfoWatch on infrastructure risk, ransomware evolution, and what security leaders need to watch this year 👇
bit.ly/46992m6

We're witnessing a fundamental shift in how organizations think about access control. But many organizations are struggling with these new barriers to modernization.
We’re sharing more on this new shift in access control 👇
bit.ly/3NxX534
