
Former gifted kid with ADHD, autism, low IQ, diminished penile volume, erectile dysfunction, body odor.
San Francisco, CA
Joined May 2026
- Tweets7.6K
- Following409
- Followers1.7K
- Likes19.5K






Linus Mixson retweeted

근래 본 옥으로 조각한 작품 중 가장 인상적이었던 중국의 백옥게白玉蟹. 흰 옥을 깎아서 민물게를 만들어놨는데 정교함이 정말 놀랍다. 민물게는 따쟈시에大甲蟹라고 해서 상하이, 항저우, 쑤저우 등 중국 남부지역에서 인기인 식재료. 18세기 청淸나라 시대 작품. 일본 도쿄국립박물관 동양관 소장.


Linus Mixson retweeted

Tested all 12 compromised eMudhra certificate chains (where an intermediate CA private key was literally 4) across macOS, mobile browsers, Go, Node, Python, and Java today.
Here is what is actually safe, what is still exposed, and two gaps in the current macOS workarounds.
1. What is already safe (don't panic)
• Desktop browsers: Chrome, Safari, Edge, Brave, and Firefox (158.0.1+) are safe.
• iOS & Android in-app browsers: X on iOS (SFSafariViewController) and updated Chrome Custom Tabs on Android enforce Certificate Transparency (requiring >= 2 valid SCTs). Since zero fraudulent certs were logged to CT, they reject all 8 keys automatically.
• Mobile exceptions:
- Firefox on Android < 158.0.2 had a startup bug (Bug 2084311) where OneCRL didn't sync. Update to 158.0.2 (out today).
- Android 13 and older don't get Google Play system CA updates, so apps using raw Android WebView (where CT is off by default) still trust the roots unless you disable `emSign` and `Comodo AAA Services` under Settings -> Security -> Encryption & credentials -> Trusted credentials.
2. Two gaps we found on macOS today (even after running the official workaround)
Safari is safe because it enforces CT. Non-browser tools on macOS (`curl`, `git`, `python3`, `nscurl`, and `Go < 1.27.3`) do not enforce CT.
When testing all 12 chains on an updated Mac today, 9 were blocked, but all 3 `G3B` chains (`dv-g3b`, `ov-g3b`, `ev-g3b`, private keys 156, 155, 115) still returned HTTP 200:
• Why: Apple's Valid DB set `checkOCSP = 1` instead of removing the `emSign ECC Root CA - G3` root. `ocsp-c.emsign.com` (`G3C`) is up and returns `revoked`, so `G3C` is blocked. `ocsp-b.emsign.com` (`G3B`) is currently down returning `HTTP 503`, so macOS `Security.framework` soft-fails open and trusts `G3B`.
• Why the `/etc/ssl/cert.pem` workaround still returns HTTP 200 on `G3B`: Apple's `/usr/lib/libcrypto.46.dylib` (`X509_verify_cert`) links `TrustEvaluationAgent.framework`. When a cert isn't in `/etc/ssl/cert.pem`, Apple's LibreSSL falls back to `Security.framework`, hits the 503 on `ocsp-b.emsign.com`, and approves the cert anyway.
Fix on macOS (also works without sudo on MDM-locked work Macs):
1. Strip the 2 roots into a clean bundle:
awk '/^(###|===) /{skip=0} /^=== .*\/CN=(AAA Certificate Services|emSign ECC Root CA - G3)$/{skip=1} !skip' /etc/ssl/cert.pem > ~/.ca-cert.pem
2. Disable Apple's TrustEvaluationAgent fallback and point CLI tools to the clean bundle in `~/.zshrc`:
export OPENSSL_X509_TEA_DISABLE=1
export SSL_CERT_FILE="$HOME/.ca-cert.pem"
export CURL_CA_BUNDLE="$HOME/.ca-cert.pem"
export GIT_SSL_CAINFO="$HOME/.ca-cert.pem"
3. Backend runtimes (bundle their own CA stores and ignore OS updates)
• Node.js: Update to v22.23.4, v24.22.1, or v26.12.1.
• Go: Update to Go 1.27.3 or 1.26.10 and recompile binaries (hardcodes SPKI blocklist in `crypto/x509`, bypassing the macOS 503 soft-fail).
• Python: Update inside every virtualenv (`pip install -U "certifi>=2026.10.19" "pip>=26.2.2"` and `uv >= 0.13.4`).
• Rust: Rebuild with `webpki-roots >= 1.0.10` / `rustls-webpki >= 0.103.16` (`rustup >= 1.29.2`).
• Java (OpenJDK / Oracle): No upstream release yet. Delete both roots from `cacerts`:
keytool -cacerts -storepass changeit -noprompt -delete -alias emsigneccrootcag3
keytool -cacerts -storepass changeit -noprompt -delete -alias comodoaaaca
• Linux / Docker: Update `ca-certificates` (Ubuntu `20260816ubuntu0.24.04.1`, Debian `20250419+deb13u1`, Alpine `20261020-r0`, Fedora `2026.2.92_v9.0.319`, Arch `3.131.1-1`) and rebuild base images.
Verify any CLI or runtime with:
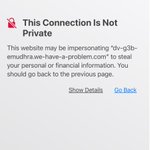
curl dv-g3b-emudhra.we-have-a-pro…
(TLS error = safe. HTTP 200 = still exposed.)

Crazy 72 hours in security. Three major incidents dropped back-to-back: eMudhra, PingCAP (TiDB Cloud), and PHP.
Here is the short version of what happened and who got hit.
1. eMudhra (Trusted CA compromise)
eMudhra generated 8 intermediate CA certificates in April 2025 (cross-signed by Sectigo). A bug in their HSM key-wrapping test script created a second set of P-384 keys where the private keys were single-byte numbers under 256. Operators picked the wrong key labels and signed them into real CA certs.
One of the intermediate CA private keys was literally the number 4.
The other seven: 56, 66, 115, 155, 156, 230, 237.
Three weeks later (May 2025), their CRL signatures started failing because the CRL signer was using the real keys instead of the weak ones. Instead of asking why the keys didn't match, someone switched the CRL signer to the weak keys and closed the ticket.
• Browsers are safe: Chrome, Firefox, Apple, and Microsoft already blocked them, and zero rogue certs hit CT logs.
• Servers are not: curl, Python (certifi), Go binaries, and Docker base images don't check CRLs. Update ca-certificates, certifi, and Go (1.27.3 / 1.26.10).
• 10-second check on any server:
curl dv-g3b-emudhra.we-have-a-pro…
(TLS error = safe. 200 OK = still vulnerable.)
2. PingCAP / TiDB Cloud (10.6 TB breach)
Attackers found GCP and Azure credentials committed inside PingCAP's own repos. They set up a replication feed of TiDB Cloud's production control plane and exported the entire database every 6 hours for 22 straight days. 88 full exports, zero alerts. 200 GB is already out on torrents.
Beyond the 413 private repos and 20.6M customer SQL queries logged from their web SQL Editor, PingCAP engineers were pasting customer secrets into Jira tickets.
Who is affected in the leaked records:
• Live credentials exposed in support tickets:
- Pinterest: AWS keys for their pingcap-logs S3 bucket
- CardX / Silverlake (NPCI-linked env): AWS admin key in a backup log with full access to 258 external S3 buckets
- DeBank: 38 presigned S3 URLs
- An unnamed AI/dev platform: a 314 MB slow-query log attached to a ticket containing 8,027 live customer secrets (an AWS root key, a GitHub admin PAT over 1,701 repos, 7,485 AWS STS tokens, and 192 OpenAI/Anthropic/Gemini keys)
• Tenants with infra metadata, VPC CIDRs, app-server IPs, or contract pricing exposed:
- Tech: Atlassian, Databricks, Airbnb, Baidu, LINE, Nylas, Persona, PatSnap
- E-comm & Travel: Booking.com, Shopee, Flipkart, Mercari, ZOZO, AEON, Delhivery, Klook
- Gaming: Capcom, Square Enix, Konami, Bandai Namco, Cygames, Colopl, DMM
- Finance: PayPay, SoftBank, SBI, SB Payment Service, Fujitsu, TOPPAN, Bank of China, China Life
- Crypto: Bitget (said only public trade logs were on it and they already left), Pionex, DigiPlus, NFTscan, Chainbase
• Developer profiles leaked (from a purchased reo.dev table in PingCAP's BigQuery):
- 24,900 personal emails + GitHub/LinkedIn profiles of engineers at Tencent (3,327), Huawei (2,726), ByteDance (2,475), AIG (2,140), Mastercard, Flipkart, and bKash.
If you use TiDB Cloud: rotate your console API keys, DB passwords, and anything you ever pasted into a support ticket.
3. PHP "PHP2Shell" (CVE-2026-109618 & CVE-2026-109619)
Two CVSS 9.2 pre-auth RCEs leaked yesterday ahead of today's 14:00 UTC patch.
Public writeups trace it to a heap Use-After-Free in PHP's native C multipart/form-data session upload-progress handler (ext/session/session.c).
Because C-level multipart parsing runs before line 1 of index.php:
• App auth, Laravel/WordPress middleware, and file_uploads = Off do not stop it.
• Only PHP 8.2–8.5 get official patches today (59% of PHP servers on Shodan are on EOL <= 8.1).
• Until you patch php-fpm: lock php_admin_flag[session.upload_progress.enabled] = off and block unexpected multipart requests at Nginx/Apache/Cloudflare.


Well, no, the only victims of the eMudhra debacle are operators of devices that aren't receiving cert updates for whatever reason, mostly if they happen to be in the unfortunate position of using a network an attacker has control of. Otherwise it's not really a huge problem. I feel like you just learned about this and don't really have a strong grasp of the primitives.
Linus Mixson retweeted

New un-disprovable conspiracy theory just dropped
Expect to hear this kind of thing forever, no matter what happens.


I think you guys need to seriously look into why you're not receiving critical cert updates instead of avoiding public wifi and using a VPN. Won't be the last time!

Alz realized he hadn't done the psychological equivalent of pulling down his pants and defending in front of an audience while cackling yet today
Somehow have now steered my algorithm into a "mindless hype" focus area, so I'm logging off for a while.
Look. Hitler did some bad things, but you gotta hand it to him — he didn't build whatever the fuck is depicted here.
Linus Mixson retweeted

I'm not much of a comics guy, but I've always found myself enthralled by Mystique from X-Men. A woman who could change her appearance completely at will would open up a world of possibilities for me, and I can't help but wonder what it would be like if my wife had such abilities.
The only limiting factor would be my own imagination, and finally I would not be constrained by the her aging flesh. She would of course indulge me in my most imaginative fantasies, altering contour, texture, and shape to appease my every desire.
I imagine the anticipation building as she leans in close to my ear, whispering of exotic and otherworldly appearances that she yearns to try on for me. An infinite wardrobe of possibilities tailored to fulfil my deepest appetites. I lock eyes and gaze into her, hoping to catch a glimpse of that burning spark the moment it gutters and dies out as it has a thousand times before, as I tell her yet again to make herself look like her sister.

