

https://xitter.gq/t.co/zsQ7Ptb0CT Theatre director in LA / Honolulu / Tokyo #landback #healthcare4All #housingIsAHumanright #bansharkfins
Tongva Land
Joined June 2009
- Tweets3.5K
- Following585
- Followers416
- Likes2.6K




Pinned Tweet
Example - how to find a fraudulent doc (#robosign). Google signers. Check the dates to see if it matches the title (ask your #realestate friend). There were several confirmed #docx locations like in #Florida #georgia etc #bankfraud


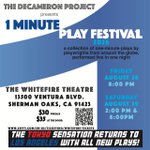
1分劇フェスティバル
劇選びましたー。 全て日本初公開です。
LIne up has been announced for #1minplay festival #tokyo2026
youtube.com/shorts/n2wUTj578…

1
36


Cat from Japan retweeted

This is a message for @realDonaldTrump.
Donald, this is on the table. Guarantee healthcare for every American, from cradle to grave.


Cat from Japan retweeted
Last night saw some of the greatest progressive victories in modern American history. All across the country, in rural and urban areas, Americans said NO to oligarchy, and YES to an agenda that fights for the working class.
Congratulations to the following candidates:
U.S. SENATE
Abdul El-Sayed (MI)
Peggy Flanagan (MN)
Troy Jackson (ME)
U.S. HOUSE
Bob Brooks (PA-7)
Rebecca Cooke (WI-3)
Sam Forstag (MT-1)
Adam Hamawy (NJ-12)
Melat Kiros (CO-1)
Brad Lander (NY-10)
Will Lawrence (MI-7)
Donavan McKinney (MI-13)
Brian Poindexter (OH-7)
Analilia Mejía (NJ-11)
Claire Valdez (NY-07)
Randy Villegas (CA-22)
Aisha Wahab (CA-14)
Cat from Japan retweeted
Democrats will now control the House and Senate and be able to hold Trump accountable. That's great.
At a time of massive income and wealth inequality, we must do more. We must aggressively fight for working families.
No more excuses.
Cat from Japan retweeted

I wrote a quick new post on "Digital Hygiene".
Basically there are some no-brainer decisions you can make in your life to dramatically improve the privacy and security of your computing and this post goes over some of them. Blog post link in the reply, but copy pasting below too.
Every now and then I get reminded about the vast fraud apparatus of the internet, re-invigorating my pursuit of basic digital hygiene around privacy/security of day to day computing. The sketchiness starts with major tech companies who are incentivized to build comprehensive profiles of you, to monetize it directly for advertising, or sell it off to professional data broker companies who further enrich, de-anonymize, cross-reference and resell it further. Inevitable and regular data breaches eventually runoff and collect your information into dark web archives, feeding into a whole underground spammer / scammer industry of hacks, phishing, ransomware, credit card fraud, identity theft, etc. This guide is a collection of the most basic digital hygiene tips, starting with the most basic to a bit more niche.
Password manager. Your passwords are your "first factor", i.e. "something you know". Do not be a noob and mint new, unique, hard passwords for every website or service that you sign up with. Combine this with a browser extension to create and Autofill them super fast. For example, I use and like 1Password. This prevents your passwords from 1) being easy to guess or crack, and 2) leaking one single time, and opening doors to many other services. In return, we now have a central location for all your 1st factors (passwords), so we must make sure to secure it thoroughly, which brings us to...
Hardware security key. The most critical services in your life (e.g. Google, or 1Password) must be additionally secured with a "2nd factor", i.e. "something you have". An attacker would have to be in possession of both factors to gain access to these services. The most common 2nd factor implemented by many services is a phone number, the idea being that you get a text message with a pin code to enter in addition to your password. Clearly, this is much better than having no 2nd factor at all, but the use of a phone number is known to be extremely insecure due to the SIM swap attack. Basically, it turns out to be surprisingly easy for an attacker to call your phone company, pretend they are you, and get them to switch your phone number over to a new phone that they control. I know this sounds totally crazy but it is true, and I have many friends who are victims of this attack. Therefore, purchase and set up hardware security keys - the industrial strength protection standard. In particular, I like and use YubiKey. These devices generate and store a private key on the device secure element itself, so the private key is never materialized on a suspiciously general purpose computing device like your laptop. Once you set these up, an attacker will not only need to know your password, but have physical possession of your security key to log in to a service. Your risk of getting pwned has just decreased by about 1000X. Purchase and set up 2-3 keys and store them in different physical locations to prevent lockout should you physically lose one of the keys. The security keys support a few authentication methods. Look for "U2F" in the 2nd factor settings of your service as the strongest protection. E.g. Google and 1Password support it. Fallback on "TOTP" if you have to, and note that your YubiKeys can store TOTP private keys, so you can use the YubiKey Authenticator app to access them easily through NFC by touching your key to the phone to get your pin when logging in. This is significantly better than storing TOTP private keys on other (software) authenticator apps, because again you should not trust general purpose computing devices. It is beyond the scope of this post to go into full detail, but basically I strongly recommend the use of 2-3 YubiKeys to dramatically strengthen your digital security.
Biometrics. Biometrics are the third common authentication factor ("something you are"). E.g. if you're on iOS I recommend setting up FaceID basically everywhere, e.g. to access the 1Password app and such.
Security questions. Dinosaur businesses are obsessed with the idea of security questions like "what is your mother's maidan name?", and force you to set them up from time to time. Clearly, these are in the category of "something you know" so they are basically passwords, but conveniently for scammers, they are easy to research out on the open internet and you should refuse any prompts to participate in this ridiculous "security" exercise. Instead, treat security questions like passwords, generate random answers to random questions, and store them in your 1Password along with your passwords.
Disk encryption. Always ensure that your computers use disk encryption. For example, on Macs this total no-brainer feature is called "File Vault". This feature ensures that if your computer gets stolen, an attacker won't be able to get the hard disk and go to town on all your data.
Internet of Things. More like @internetofshit. Whenever possible, avoid "smart" devices, which are essentially incredibly insecure, internet-connected computers that gather tons of data, get hacked all the time, and that people willingly place into their homes. These things have microphones, and they routinely send data back to the mothership for analytics and to "improve customer experience" lol ok. As an example, in my younger and naive years I once purchased a CO2 monitor from China that demanded to know everything about me and my precise physical location before it would tell me the amount of CO2 in my room. These devices are a huge and very common attack surface on your privacy and security and should be avoided.
Messaging. I recommend Signal instead of text messages because it end-to-end encrypts all your communications. In addition, it does not store metadata like many other apps do (e.g. iMessage, WhatsApp). Turn on disappearing messages (e.g. 90 days default is good). In my experience they are an information vulnerability with no significant upside.
Browser. I recommend Brave browser, which is a privacy-first browser based on Chromium. That means that basically all Chrome extensions work out of the box and the browser feels like Chrome, but without Google having front row seats to your entire digital life.
Search engine. I recommend Brave search, which you can set up as your default in the browser settings. Brave Search is a privacy-first search engine with its own index, unlike e.g. Duck Duck Go which basically a nice skin for Bing, and is forced into weird partnerships with Microsoft that compromise user privacy. As with all services on this list, I pay $3/mo for Brave Premium because I prefer to be the customer, not the product in my digital life. I find that empirically, about 95% of my search engine queries are super simple website lookups, with the search engine basically acting as a tiny DNS. And if you're not finding what you're looking for, fallback to Google by just prepending "!g" to your search query, which will redirect it to Google.
Credit cards. Mint new, unique credit cards per merchant. There is no need to use one credit card on many services. This allows them to "link up" your purchasing across different services, and additionally it opens you up to credit card fraud because the services might leak your credit card number. I like and use privacy dot com to mint new credit cards for every single transaction or merchant. You get a nice interface for all your spending and notifications for each swipe. You can also set limits on each credit card (e.g. $50/month etc.), which dramatically decreases the risk of being charged more than you expect. Additionally, with a privacy dot com card you get to enter totally random information for your name and address when filling out billing information. This is huge, because there is simply no need and totally crazy that random internet merchants should be given your physical address. Which brings me to...
Address. There is no need to give out your physical address to the majority of random services and merchants on the internet. Use a virtual mail service. I currently use Earth Class Mail but tbh I'm a bit embarrassed by that and I'm looking to switch to Virtual Post Mail due to its much strong commitments to privacy, security, and its ownership structure and reputation. In any case, you get an address you can give out, they receive your mail, they scan it and digitize it, they have an app for you to quickly see it, and you can decide what to do with it (e.g. shred, forward, etc.). Not only do you gain security and privacy but also quite a bit of convenience.
Email. I still use gmail just due to sheer convenience, but I've started to partially use Proton Mail as well. And while we're on email, a few more thoughts. Never click on any link inside any email you receive. Email addresses are extremely easy to spoof and you can never be guaranteed that the email you got is a phishing email from a scammer. Instead, I manually navigate to any service of interest and log in from there. In addition, disable image loading by default in your email's settings. If you get an email that requires you to see images, you can click on "show images" to see them and it's not a big deal at all. This is important because many services use embedded images to track you - they hide information inside the image URL you get, so when your email client loads the image, they can see that you opened the email. There's just no need for that. Additionally, confusing images are one way scammers hide information to avoid being filtered by email servers as scam / spam.
VPN. If you wish to hide your IP/location to services, you can do so via VPN indirection. I recommend Mullvad VPN. I keep VPN off by default, but enable it selectively when I'm dealing with services I trust less and want more protection from.
DNS-based blocker. You can block ads by blocking entire domains at the DNS level. I like and use NextDNS, which blocks all kinds of ads and trackers. For more advanced users who like to tinker, pi-hole is the physical alternative.
Network monitor. I like and use The Little Snitch, which I have installed and running on my MacBook. This lets you see which apps are communicating, how much data and when, so you can keep track of what apps on your computer "call home" and how often. Any app that communicates too much is sus, and should potentially be uninstalled if you don't expect the traffic.
I just want to live a secure digital life and establish harmonious relationships with products and services that leak only the necessary information. And I wish to pay for the software I use so that incentives are aligned and so that I am the customer. This is not trivial, but it is possible to approach with some determination and discipline.
Finally, what's not on the list. I mostly still use Gmail + Gsuite because it's just too convenient and pervasive. I also use 𝕏 instead of something exotic (e.g. Mastodon), trading off sovereignty for convenience. I don't use a VoIP burner phone service (e.g. MySudo) but I am interested in it. I don't really mint new/unique email addresses but I want to. The journey continues. Let me know if there are other digital hygiene tips and tricks that should be on this list.
Link to blog post version in the reply, on my brand new Bear ʕ•ᴥ•ʔ blog cute 👇

And reminder … 81 years ago, the president of the United States said:
"We are the victors and Japan is the vanquished. We do not propose to bargain with Japan."
Something never changes

14


I followed this instruction - my inbox was flooded with 6000+ emails because it deleted the filters.
I had to manually remove junk’s- but it feels good to have updated - zero emails before I go zzzzzz
For sure I’ll have 100+ mails by tomorrow morning #delete


🚨 BREAKING NEWS: Gmail Users Need to Read This!
If you have a Gmail account, you need to read this.
Google’s AI is now rifling through your inbox emails and attachments, bank statements, tax docs, medical letters, the whole stack. It was enabled by default, and that quiet rollout is now facing a class-action lawsuit.
Here are 5 steps to turn it off because the kill switch is buried in two different spots:
1
28

Cat from Japan retweeted

PSA: This week was kind of a turning point for AI and cybersecurity. Please take this weekend to do some simple cleanup for your family. Some suggestions:
- Set up a password manager like 1Password and give your spouse or partner access to a shared vault. Teach them how to use it.
- Update your passwords for critical stuff - your email account, your bank or financial stuff, etc. Store in your password manager and use the strongest password you can.
- Use two factor auth for everything you can. SMS is not ideal although better than nothing. Google Authenticator or a passkey is better. Hardware key is safest.)
- Add a sim pin to your phone. Makes it harder to sim jack.
- Update your phone and your computer to the newest releases. Turn auto-updates on.
- Freeze your credit - takes 5 minutes.
- Get an IRS Identity Protection PIN.
- If you’re using claude code or have AI agents that browse the web, they’re probably using Node.js. It’s also vulnerable. Update claude code, update node on your machine.
- If you’re building stuff on your computer, ask claude or grokbot (which is connected to twitter and likely has the most current info) to audit any of your repos for vulnerabilities. Ask grok to make it a scheduled task so it can do this daily - things are moving very quickly in the space right now.
- Consider some light resiliency stuff. This probably sounds silly, but it sounded silly at the beginning of covid too. Having printed out copies of important stuff - especially financial accounts. Having some cash on hand. Having some shelf-stable food and clean water or a water filter. Having a map. Having a generator that can at least power your fridge or some devices. Cheap insurance.
Again, I don’t want to alarm people, but I was taught that you should have a Secure plan, a Comfortable plan, and a Wealthy plan. And it seems pretty clear the secure plan needs to now factor cybersecurity risk as a legit threat. Take a weekend and shore yourself up.
Cat from Japan retweeted

🚨 MIT just published the most comprehensive report, proving universities have no remaining reason to exist.
A committee of professors and students spent five months studying what AI is doing to learning on campus. The findings are a warning, not a footnote.
Study groups are disappearing. Office hours are emptying out. Problem sets and take-home exams no longer prove anything, because AI can produce a credible answer to almost any undergraduate assignment.
The report has a name for what's happening to students: "cognitive surrender." Reaching for AI the instant something gets hard, before even trying to think it through.
The numbers back it up:
46% of MIT undergrads use LLMs daily
90% say they're worried about their own overreliance
More students now believe AI makes them replaceable than believe it makes them capable
MIT's answer wasn't more surveillance. No AI detectors, no lockdown browsers. The committee called that path unreliable and said it just breeds distrust.
Instead: oral exams, semester-long portfolios, in-person project work, a required social component in every subject. They're even floating rethinking grades entirely, since without a GPA to game, most of the incentive to cheat disappears.
The most famous tech school on the planet just admitted the machines broke its teaching model.
Its answer was more humans, not more software.
(Paper link in comments)


I heard IT salaries in Japan are surprisingly low.
When compared to the US or China, Japanese IT engineer salaries often lag behind at less than half or even one-third of what engineers earn abroad—making Japan’s pay scale notably low among major economies. #CyberSecurity

17

福沢諭吉 脱亜論のプロパガンダですね。 #DNA

TBSが社運を賭ける番組「VIVANT」、おととい放送の回は完全に底が抜けていました。
仲間を一人殺された報復に、中国人数十人を惨殺。武器を携帯して密入国した相手国の警察も敵に回して銃口を向け、人質にした警察幹部を「人間の盾」にして空港に強行突入。やってることは完全にテロリスト集団です。

81