


OneKey retweeted

We get asked this a lot: “How do I know my hardware wallet hasn’t been tampered with before it gets to me?”
Between the factory and your door, a wallet spends time in warehouses and in transit. Packaging is only one part of preventing supply chain attacks, but it matters. It helps you check for signs of tampering when the wallet arrives. That’s why we’ve put a lot of work into ours.
OneKey has four layers of protection:
1. Clear shrink wrap around the whole box.
2. A destructible seal on the box that breaks when removed.
3. A holographic tamper-evident seal on the device that shows “VOID” when peeled off.
4. Device authentication in the official OneKey App, plus firmware signature checks by the Secure Element (SE).
Our manufacturer is in the same tier as those making Apple and Google Pixel devices. To enter the factory, you have to pass through multiple gates and three security checks, sign in, and verify your identity. All phones and other communication devices have to be handed over and kept in lockers. There are cameras throughout the factory.
There’s still a lot more to do. We’ll keep tightening security and improving these measures.
OneKey retweeted
After the recent Ledger incident, I wrote about how hardware implants can steal a recovery phrase without breaking the secure chip, what remains unconfirmed, and the changes we're making at OneKey.
OneKey retweeted

OneKey Pro : la nouveauté qui vient d'arriver chez Neowalt. 🆕
4× Secure Element certifiés EAL6+, déverrouillage par empreinte digitale, signature air-gapped par QR code.
Ce hardware wallet coche toutes les cases pour protéger tes cryptos hors ligne, sans sacrifier le confort d'usage.
Le détail des caractéristiques techniques (écran tactile 3,5", batterie 530 mAh, recharge sans fil Qi2, Bluetooth, NFC, USB-C, support multisig, compatible BTC/ETH/SOL/TRON et bien d'autres) est à retrouver en swipant ➡️
Disponible dès maintenant en noir ou blanc sur neowalt.com 👇
#OneKeyPro #HardwareWallet #ColdWallet #CryptoSécurité
#cryptosecurity


OneKey retweeted
we hacked ledger.
the @OneKey_Anzen team has successfully reproduced a transaction replacement attack against ledger ethereum app 1.22.1 in our lab.
the bug is a race condition between the transaction display logic and the underlying transaction buffer.
an attacker can overwrite the transaction waiting to be signed while the user is still reviewing a legitimate one.
in simple terms:
- you see transaction a on your ledger.
- you approve transaction a.
- your ledger can end up signing transaction b.
- and you never see transaction b.
to reproduce this, we built the 1.22.1 ELF ourselves, fixed the speculos reset 502 issue, and got the full attack flow working end to end.
ledger fixed this in ethereum app 1.22.3.
if you’re still on an older version, update it.
Readers added context they thought people might want to know
The described bug matches a vulnerability publicly disclosed by TestMachine on August 22 which Ledger fixed in Ethereum app 1.22.2, not 1.22.3.
donjon.ledger.com/lsb/023/
github.com/LedgerHQ/app-e…
x.com/testmachine_ai…
OneKey retweeted
eight months ago, i handed my boss @cz_binance the prototype. he said, “keep going, make it great.”
today, in bhutan, i finally handed him the new one.
pretty proud to say i think we’ve built the best hardware wallet experience in the world. hope he likes it hehe.
the team won’t let me leak a single detail yet, so that’s all i can say for now. but give us a little more time. i think you’ll be meeting it very soon :)

OneKey retweeted

New feature release!🌟
We now support deposits directly from your @binance account.
Binance is one of the biggest centralized exchanges, powering over 300M users globally. Now users can move funds from Binance straight into any platform powered by Unifold in just a few seconds.
We're excited to keep expanding our support across the Binance ecosystem and serve more @yzilabs portfolio companies with seamless funding infrastructure.
OneKey retweeted
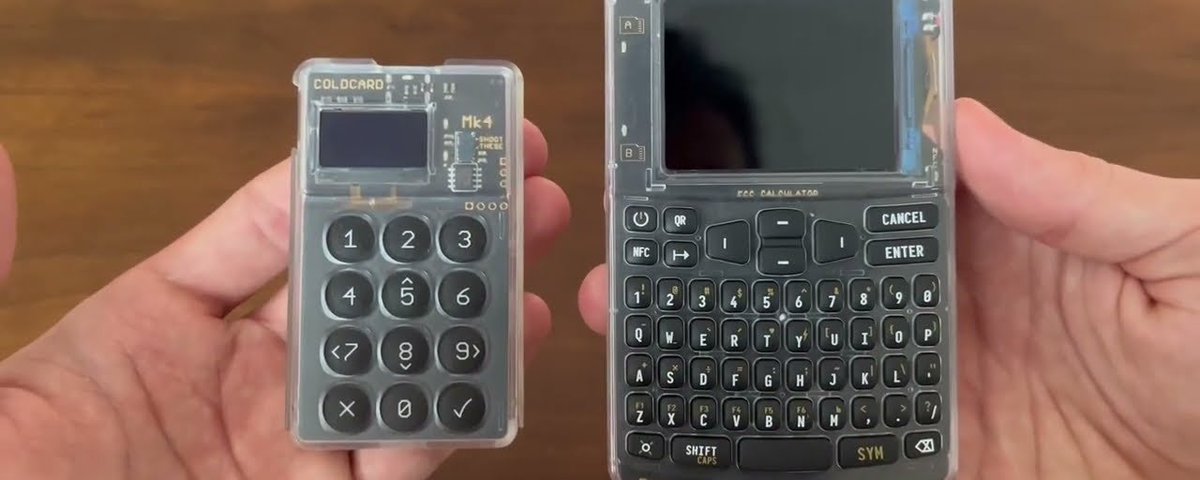
just built a small open source tool tonight to test the quality of your device’s entropy and verify that your seed phrase is cryptographically secure.
entro.tools




OneKey retweeted

ForeDex has officially secured a sponsorship agreement today with “OneKey,” a global digital asset security and hardware wallet company.
We would like to sincerely thank the OneKey team for recognizing the potential and value of ForeDex, even at this early stage of our platform.
As the official sponsor of the “ForeDex Recognized Analyst” program, OneKey will support prize rewards for the top-ranked analysts at the end of the year.
@OneKeyHQ @OneKeyCN

OneKey retweeted

Cold Storage for Your Assets, Incognito Mode for Your History.
@OneKeyHQ x Houdini
Your keys are safe, now your on-chain history is too.
Toggle Incognito Mode directly in the OneKey app to bridge, swap, and send without leaving a trace on the public ledger.
The ultimate privacy stack has arrived. 🧙♂️🪄
OneKey retweeted
⚠️ Axios supply chain attack notice:
Axios is one of the most popular HTTP client libraries for JavaScript/Node.js.
AI tools like Cursor, Copilot, and Claude often generate npm i axios without pinning a version, which can install the malicious 1.14.1 or 0.30.4.
Quick actions:
> Check package.json and your lockfile
> Safe versions: 1.14.0 (1.x) / 0.30.3 (0.x)
> If affected, treat the machine as compromised and rotate all keys/credentials immediately
OneKey security team has reviewed all our repos — we are not impacted. We use strict version pinning across projects.
Supply chain attacks are rising. Pin your dependencies.

🚨 CRITICAL: Active supply chain attack on axios -- one of npm's most depended-on packages.
The latest [email protected] now pulls in [email protected], a package that did not exist before today. This is a live compromise.
This is textbook supply chain installer malware. axios has 100M+ weekly downloads. Every npm install pulling the latest version is potentially compromised right now.
Socket AI analysis confirms this is malware. plain-crypto-js is an obfuscated dropper/loader that:
• Deobfuscates embedded payloads and operational strings at runtime
• Dynamically loads fs, os, and execSync to evade static analysis
• Executes decoded shell commands
• Stages and copies payload files into OS temp and Windows ProgramData directories
• Deletes and renames artifacts post-execution to destroy forensic evidence
If you use axios, pin your version immediately and audit your lockfiles. Do not upgrade.


OneKey retweeted
the wallet with the lowest perp trading fees and the best liquidity in the world. period.
This quoted post is unavailable.


OneKey retweeted
OneKey retweeted

We’ve teamed up with @OneKeyHQ to give away hardware wallets 👇
🏆 Prizes:
1× OneKey Pro
2× OneKey Classic 1S
How to enter:
1️⃣ Follow @Bitrefill & @OneKeyHQ
2️⃣ Tell us why you need a hardware wallet (wrong answers only!)
Winners will be selected in 48 hours, good luck!

We’re excited to welcome @Bitrefill as an official OneKey reseller.
Bitrefill is one of the most trusted platforms in Bitcoin and crypto, helping people live on crypto for more than 11 years.
Together, we’re making self-custody practical, accessible, and real.
Buy OneKey via @Bitrefill and enjoy 20% Cashback.
Secure your keys, spend your crypto.
