

Chaos. Claws. Conviction. Only the bold dare to click. 🐾
The Litterbox On X
Joined March 2013
- Tweets5.7K
- Following3.3K
- Followers750
- Likes4.6K




Pinned Tweet
I found a historical bug in Berkeley DB 4.8.30 that shipped with the original bitcoin. Full write up can be found here. It's a endianness thing..
bitcointalk.org/index.php?to…
Everything is about to get hacked.
Don't think this is the end this is only the start.
My advice..
Touch grass for a month or two while the dust settles.
Nothing is safe anymore.


Patch the patch quickly. 😂

🚨ALERT: PHP warns of ANOTHER UNPATCHED security flaw that could let hackers take control of vulnerable web servers, just TWO DAYS after releasing emergency fixes for critical PHP2Shell vulnerabilities.
The NEWLY discovered flaw, CVE-2026-115560, affects websites using an uncommon technical setup.
PHP has urged affected website administrators to disable a specific feature until a security fix is released.
The warning comes as hacking attempts targeting the TWO earlier PHP2Shell flaws have surged into the MILLIONS, per Cloudflare.
Where Things Stand:
- The latest flaw affects only an unusual combination of PHP session settings.
- No exploitation of the new vulnerability has been reported.
- PHP recommends disabling session upload progress until its next routine bugfix release.
Unlike the earlier critical flaws, PHP considers the new vulnerability an unlikely attack vector and is not issuing another emergency patch.

PHP - Payload Handling Problem 😂
The internet is going into a LOCKDOWN.
Hundreds of millions of websites are potentially at risk from cyberattacks.
Governments, banks and major platforms have already taken their websites OFFLINE.
Many are already calling it “Black October.”
At the centre of the shutdowns is something most of us have never heard of, but use every day.
PHP, the software behind roughly 7 in 10 websites, has two critical flaws that can let hackers break in without a password.
Dubbed PHP2Shell, both are rated 9.2 out of 10 for severity.
Details began circulating on Oct 20. Emergency fixes arrived the next day, but attackers were already moving.
Cloudflare’s CEO says hacking attempts then jumped from thousands to MILLIONS within hours.
Cybersecurity agencies across several countries are telling PHP site owners the same thing: Patch it now, or take it offline.
Websites have gone dark worldwide, from government portals and hospitals to banks.
CrowdStrike warns these attacks leave almost no trace, so some sites may not know if they’ve been hit.
Around 2.6 MILLION internet-facing servers run PHP, potentially hosting hundreds of sites each.
Over 1.1 million use older versions no longer receiving official PHP updates.
Older installations may need an upgrade to a supported PHP version or a fix from their software provider.
And patching does not remove a backdoor an attacker may already have planted.
Cloudflare also says hackers are now tweaking their attacks to try to slip past its protections.
But PHP isn’t the only security story unfolding.
-Japan’s Onamae suspended ALL Desktop Cloud plans after malware was found on customer servers.
-India’s eMudhra had 8 website-certificate keys so weak, one was literally the number “4”.
-State Bank of India confirmed 3,897 customer records on the dark web.
-Criminals used AI agents to break into 400+ Latin American banks.
-Capcom confirmed a breach exposing 11.7 million email addresses.
-GitLab disclosed a 10/10 severity flaw in versions going back to 2014.
-LiteLLM removed a malware-containing release. Railway reported possible exposure of customer secrets.
None of these has a confirmed link to PHP2Shell.
We’re seeing separate breaches unfold together.
The true number of incidents could take months to come out.
The world is still on alert. Attacks are still coming.
Just taking more and more when will people wake up and start the revolution.. Is there anyone left who will fight them?

🇬🇧 UK TAX AUTHORITY RESUMES DIRECT SEIZURES FROM BANK ACCOUNTS
HMRC has reinstated powers suspended during the pandemic that allow it to recover unpaid taxes directly from individuals’ and businesses’ bank accounts without obtaining a court order.
The policy, restarted in a “test and learn” phase in 2025, applies to tax debts of £1,000 or more and allows HMRC to withdraw funds from current accounts and cash ISAs.
Safeguards include:
• A minimum of £5,000 must remain in the debtor’s accounts.
• HMRC must make a face-to-face visit before initiating recovery.
• Debtors have 30 days to appeal before any funds are transferred.
• Vulnerable individuals and those experiencing financial hardship may receive additional protections.
The powers allow the government to compel banks and building societies to transfer funds directly to HMRC to settle outstanding tax liabilities.


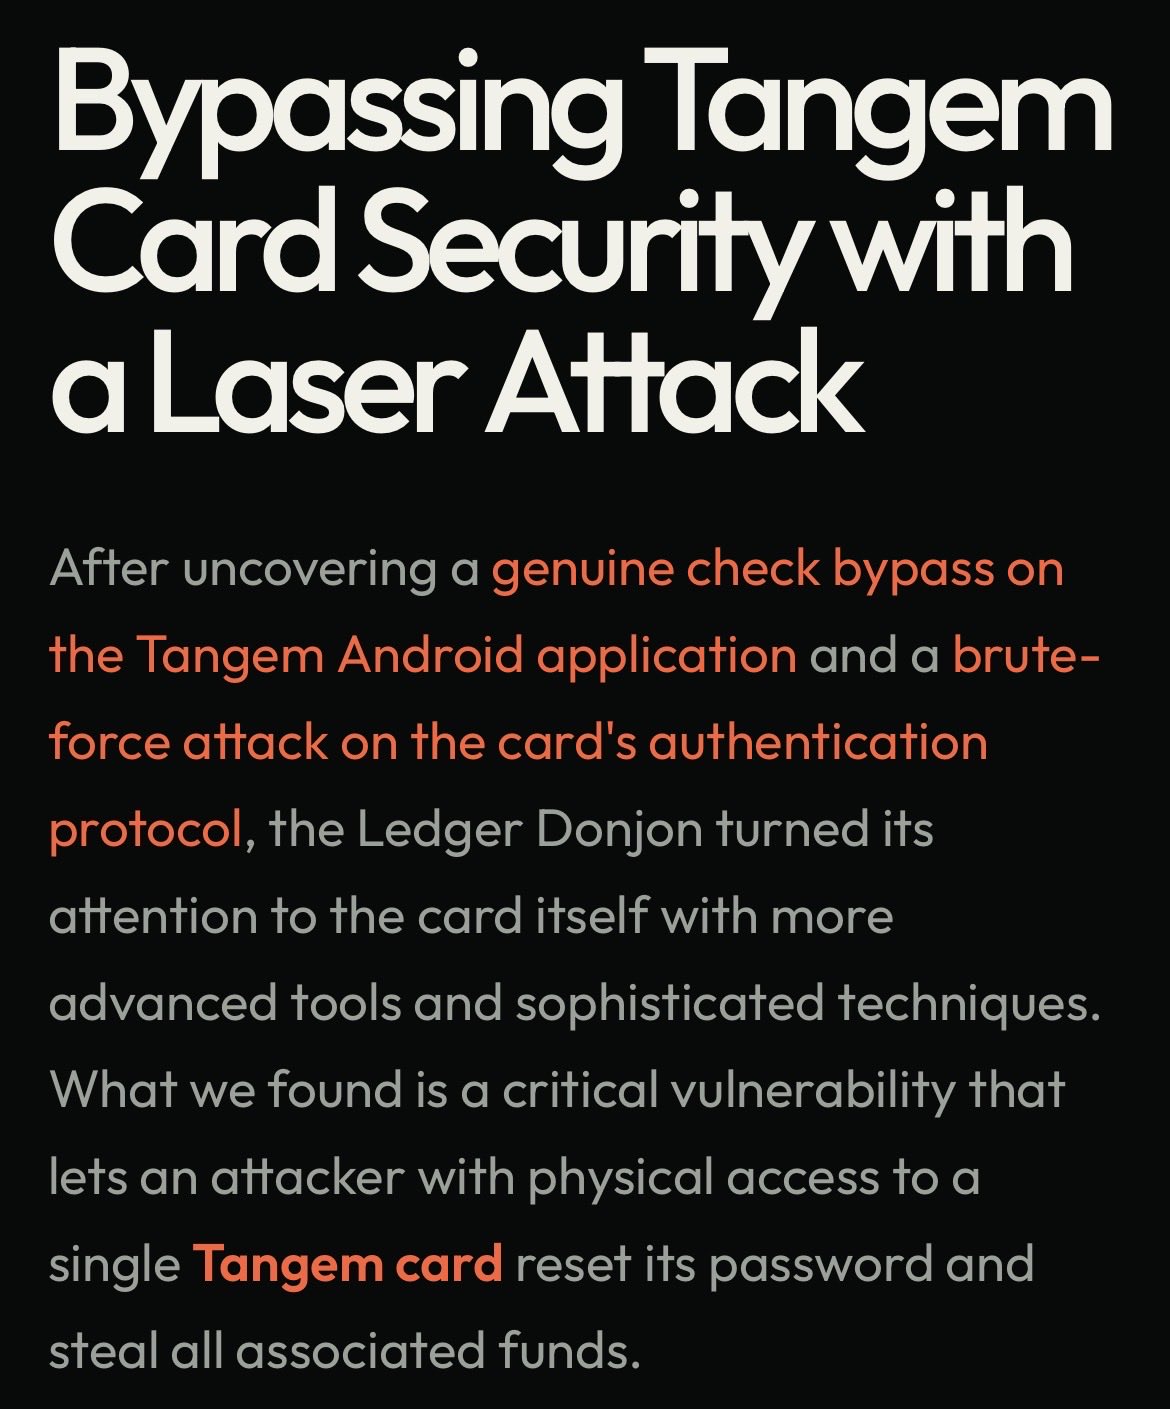
Support this guy he is a gem in the space and really puts in the effort. Forget the KOL's this is the type of people we should be supporting.
Give this a share and donate if you can.

I’m at rock bottom financially, and I’m not ashamed to say it.
I’ve always been honest with you, and that includes admitting when I’m struggling, even in a space that treats honesty about hardship as weakness.
What hurts is wondering whether I’ve failed to make this sustainable, whether I was naive to believe my work would receive enough support, and whether putting so much into building solutions was the wrong decision.
I can no longer carry it on my own. I’m sorry to those reading another appeal, but the situation has become unsustainable.
After my cancer diagnosis, followed by multiple sclerosis, I hoped to gradually earn a living through Web3 work that would be more manageable physically. I still have a regular job and build MASTR in my spare time. I made mistakes, invested more time and money than I could afford and overextended myself.
Over 3 years, I’ve helped thousands of people, handled thousands of scans and requests, investigated scams and built apps and a public crypto wiki.
Everything I’ve learned about token scans, wallet connections and tracing onchain money flows has gone into MASTRtrade and its scan bot.
I offered my services for free. Since asking for fair compensation, almost nothing has come in. My attempts to find backing in this industry have repeatedly gone nowhere.
Sometimes it feels like the work I do makes me inconvenient to support.
I’ve never accepted money to shill tokens, despite receiving offers every day. I would rather ask openly for help than earn money through the shady practices I’ve spent years exposing.
I want to remain independent.
I still have serious plans for MASTR, but I need financial support soon to continue. Being forced to stop while the casino or the scammers keeps attracting money in millions would hurt more than I can explain.
If my work has helped you, please consider donating or booking a paid investigation.
Your support helps cover research time, data, hosting and development while reducing the burden on my family.
Small contributions matter too. If you cannot donate, sharing this or referring paid work helps.
To everyone who has already supported me, thank you.
Services and investigations: mastrlabs.com/services/
Donate on Solana: 6ELa36JmfYL8RFFu5i6WfRAQAykkyVNRqBtpoaTaEwNq
ETH / EVM: 0xa66336d7b1effe7e0c9866b72534d4f59494e888


Is this not fraud?
Votes for pay?
🇺🇸JUST NOW: President Trump promises AGAIN to give every adult US citizen $5,000 if Republicans win the midterms.
Trump claims Republicans can do it because "we're taking in massive amounts of money through tariffs."
The payments would cost an estimated $1.2 TRILLION and need approval from Congress.
