




Pinned Tweet
Most people think being rich fixes all your problems
So you work yourself to the bone, possibly taking great risks to get there
Then you finally make it and you realize that being rich is even better than you imagined
2
27
4,190
A single instance where an addict overdoses and needs an ambulance costs the taxpayer thousands of dollars
Remove the cost of treating self-inflicted illness, and you'll find America is close to the UK number
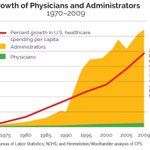
We also have 9 administrators for every practitioner, whereas most systems have 9 practitioners for every administrator.
@SenSanders voted for all of the policies that created both problems. Our medical industry is more expensive than it should be, and it's his fault. Now he wants everyone to forget this fact and double down on socializing healthcare.

Some say we can’t afford Medicare for All. Really?
Here’s what we’re spending on healthcare per person vs. countries with universal healthcare:
🇺🇸: $15,474
🇯🇵: $5,790
🇬🇧: $6,797
🇨🇦: $7,301
🇫🇷: $7,367
🇦🇺: $7,469
🇧🇪: $7,750
Fact: We can’t afford NOT to enact Medicare for All.
12


I just drank 600mg of caffeine and invented a new EDS system for guided ordinance that would dramatically reduce civilian casualties in events where the wrong structure gets targeted
1
3
129

Because you can watch live streams of rockets landing on barges, use the Internet in a warzone, get into a self-driving electric vehicle, drive through an underground passage, or play counter strike with a paralyzed man.

1
85


Can someone explain to me how this happens?
How does someone lose years of experience reading and writing code? I use AI daily, but I am quite certain that my skills have gotten sharper over the past two years as I've spent much more time reviewing code that I don't trust

I'll be honest: I would not be able to pass a coding interview anymore. I'd need to spend 2 months on re-learning how to code by hand.
2
107
How can @CodeToTheMoons recommend railway after everything?
Is this a joke? Not only did they leak customer environment variables but they also had this whole incident with @joshmanders like five minutes ago
youtube.com/watch?v=YfahrTa3…


1/10 comms
Best guess is the attorneys said that they can't make a better post given the facts, and they can't bs because @joshmanders would bring receipts

Last night, I became aware of the concerns raised in Josh's post. I reached out publicly and over DM to offer a potential explanation based on the limited information available at the time, while working to understand what happened.
As background, we’ve internally been pushing 100% on security of the Railway platform. At Railway, we believe that cyber threats are real and mounting, and we’ve built out tooling for automatic scanning + CVE remediation (for both our infrastructure and customers). Over the last few weeks, oncall engineers were instructed to red team our infrastructure. We maintain specific policies and short lived grants for when these actions occur.
Subsequently, I became aware that an employee at Railway had constructed, on their own time, a tool for proactive identification + reporting of bug bounties within the broader community.
The employee, using their own personal accounts, personal credit card, and time outside of work hours, signed up for a personal subscription to a hosted service running Deepseek. I can confirm they ran this tool once and only once, on a singular external provider, and halted it proactively within 15 minutes of starting.
Railway does not condone these actions. We expect all our employees to uphold our standards of conduct, whether acting on behalf of Railway or in a personal capacity. We create an environment where internal red teaming has strict guidelines, and when bug bounty disclosures must occur, we follow every letter of responsible disclosure.
We have addressed this incident with the employee directly and have taken appropriate action. We are also reinforcing our expectations for employee conduct to help prevent similar situations.
Readers added context they thought people might want to know
Primcloud does not have a bug bounty program, per its founder. Its Acceptable Use Policy forbids unauthorized probing, scanning or vulnerability testing without prior written consent.
x.com/joshmanders/st…
primcloud.com/aup
1
95


I think I've finally reached my breaking point with the helix project
I might end up back on emacs today
69
Proziam retweeted

it's always "recreated" and never "created"

I recreated subvocal in 9 minutes with one prompt for AirPods Pro 3.
Source: github.com/joeblau/subvox