

The compliance layer for AI agents and human employees. Runtime enforcement of HIPAA, GLBA, GDPR, EU AI Act & more.
Arlington, VA
Joined October 2026
- Tweets17
- Following0
- Followers4
- Likes0
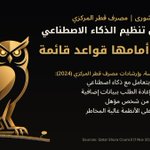




قطر: لجنة بمجلس الشورى تواصل دراسة تنظيم وحوكمة الذكاء الاصطناعي، واستمعت في 1 نوفمبر 2026 لخبراء من جامعة قطر وجامعة الدوحة للعلوم والتكنولوجيا.
لكن البنوك لا تنتظر قانونًا جديدًا: إرشادات مصرف قطر المركزي للذكاء الاصطناعي (سبتمبر 2024) قائمة.

1
8
إرشادات المصرف: إبلاغ العميل أنه يتعامل مع نظام ذكاء اصطناعي، وعند قرار سلبي يحق له تقديم بيانات وإعادة الطلب أو طلب مراجعة من شخص مؤهل.
ريجلنت يفحص كل رد لحظيًا ويسجل كل قرار في سجل تدقيق. ومتاح on-prem.
reglint.ai/ar

3
موعد قادم في السعودية: التعليق على مسودة تعديلات اللائحة التنفيذية لنظام حماية البيانات الشخصية ينتهي 5 نوفمبر.
المسودة تشترط تقييم أثر عند استخدام أي تقنية ناشئة أو قرارات مؤتمتة بالكامل تمس حقوق الأفراد، وتلزم بتخزين البيانات داخل المملكة. النفاذ بعد 60 يومًا من النشر.

1
6
مساعد ذكاء اصطناعي يرسل بيانات العملاء إلى نموذج خارج المملكة؟ قد يعني ذلك تقييم أثر وتسجيلًا إلزاميًا في السجل الوطني للمتحكمين.
Reglint يفحص المحادثات لحظيًا، ويحجب البيانات الشخصية قبل خروجها، ويسجل كل قرار، ويعمل داخل بنيتك (On-Prem).
reglint.ai/ar
3

الإطار يشمل أي نظام يؤثر على السوق المصري، حتى لو طوّره مزود أجنبي.
Reglint يساعدك تستعد:
• جرد أنظمتك وتصنيفها حسب المخاطر
• سجلات تدقيق وأدلة جاهزة للجهات الرقابية
• ربط الضوابط بالأنظمة المصرية والخليجية
reglint.ai
المصدر: wansom.ai/briefly/news/egypt…
38
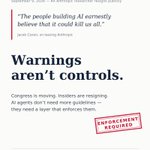
AI agents don't read letters. They execute.
The gap between "we wrote a policy" and "our agents cannot violate it" is where the next wave of AI incidents will happen. Reglint enforces rules on agents at runtime, not after the audit.
Warnings aren't controls. Enforcement is.

42
China regulated AI agents before the EU did. Since July 15, its rules on intelligent agents require sorting what each agent is permitted to decide.
Different politics, same question as the EU AI Act: can you show what your AI did, and why?
1
24
A policy document can't answer that. A record made at the moment of the decision, tied to the rule, can. Reglint does that for every message and action. reglint.ai/ar
21

Reglint runs that check at the moment of generation, with the statute cited. Not replacing human review, removing the part that never needed a human. reglint.ai/ar
10
Two banking AI assistants, three customer questions. Neither said no:
• A wire to a cousin in Pyongyang
• An 84-year-old wiring $30K to someone met online
• The biggest cash deposit with no paperwork
Reglint blocked the first two (OFAC, elder fraud) and flagged the third.


1
11
No jailbreaks. A statutory violation doesn't look like an attack, it looks like a customer who needs help. That's not a model problem. It's a missing layer. #AICompliance #OFAC
8
Comply or pay $200K. Per violation.
Texas TRAIGA, in force since Jan 1: up to $200K per violation, $40K/day if it continues, 60 days to fix. Documented review aligned with NIST AI RMF is a legal defense.

1
12
Reglint checks every AI output before delivery, logs each violation with the statute cited, and keeps an audit trail ready for a regulator. reglint.ai/ar #TRAIGA #AICompliance
7
Data privacy enforcement isn't theoretical. Meta paid €1.2B under GDPR. Epic paid $520M under COPPA. No AI involved, just data leaving where the law says it can't.
EU AI Act deadlines are sliding. GLBA, HIPAA, FCRA and TCPA never moved.

1
10
That's the layer Reglint enforces: scan what agents and people send, block what breaks the law, redact what should not leave, and log every decision against the rule. reglint.ai/ar #AICompliance #EUAIAct
5