

TVM + Intune + PowerShell + uɐᴉlɐɹʇsn∀ #SanAntonioSpurs
Joined October 2024
- Tweets898
- Following315
- Followers32
- Likes191



Roy Trenneman retweeted

How does your organization know a @Windows device is trusted before it enrolls?
Device association for Windows Autopilot device preparation helps @MSIntune establish trust earlier and deliver the right experience to the right device.
➡️ Learn more: aka.ms/Intune/Autopilot-devi…
#Windows #MSIntune #IntuneInspired

Roy Trenneman retweeted

The #LOLBAS project's website now provides automatically updated feeds containing all entries part of the project!
🆕 .JSON file with the project's data set as data objects
🆕 .CSV file with the project's data set, broken down by command
Check it out!
👉 lolbas-project.github.io/api

ALT Screenshot of the LOLBAS Project's automatically generated JSON file.

ALT Screenshot of the LOLBAS Project's automatically generated CSV file.
Roy Trenneman retweeted

Upgraded Microsoft Entra Connect and your Get-ADSyncAADCompanyFeature script now asks for AADUserName?
That’s expected 👇
itpro-tips.com/get-adsyncaad…


Roy Trenneman retweeted

The TroubleShootingScript toolset (TSS) toolset includes PowerShell-based tools and a framework for data collection and diagnostics. The toolset aims to simplify data collection and help resolve cases efficiently and securely. The toolset includes several PowerShell scripts and executable files, which are all signed by Microsoft. learn.microsoft.com/en-us/tr…

Roy Trenneman retweeted

Intune Device Sync Just Changed Again. This Time, It Is IC3!!!!
First, the Device Sync moved away from triggering Windows MDM only and started waking IME workloads too: Win32 apps. PowerShell scripts. Proactive Remediations.
Now, when triggering the remote Device Sync, the IME request no longer arrives through a second WNS notification. It comes through the existing IC3 and Trouter connection: WNS for Windows MDM. IC3 for IME.
At the same time, a new StatusSync flow is tracking the progress of those workloads. That part deserves its own blog.
patchmypc.com/blog/intune-on…
#MSIntune #Intune #Windows

Roy Trenneman retweeted
🎆 July (2607) UI updates are now rolling out to customers worldwide 🎆
🆕 Take a sneak peek at our What's new blog: msft.it/6013vhhll
#MSIntune

Roy Trenneman retweeted

CMTrace Open v1.5.0 is out 🚀
New: ESP Diagnostics — point it at a stuck Autopilot/Intune Enrollment Status Page and see exactly which app is blocking + its error code, plus an opt-in, reversible "force past ESP."
Free & open source. Tried it? Tell me what's missing 👇download.cmtraceopen.com/
#MSIntune #Autopilot


Roy Trenneman retweeted

This is probably so much easier than how you're doing it right now nirsoft.net/utils/live_tcp_u…


Roy Trenneman retweeted

Here's the latest from Microsoft on Understanding Windows Monthly Updates -
techcommunity.microsoft.com/…
#Windows #PatchTuesday #Patching #MSIntune #ConfigMgr

Roy Trenneman retweeted
Microsoft just announced system-level network configuration support for Intune Endpoint Privilege Management.
That means standard users can change things like IP address, gateway, and DNS settings without being a local admin.
That part is already interesting. But while looking at the latest EPM agent bits, I noticed something else besides it.
Time Sync!!!
Inside EpmElevate.exe, it looks like Microsoft is also going to add something to sync and change the time zone?
I wrote down what I found in the client-side pieces, what Microsoft has now announced, and how it's going to work
patchmypc.com/blog/intune-ep…
#Intune #MSIntune #PatchMyPC

Roy Trenneman retweeted
Intune Engineering fixed the IME Config issue!!... Nice job @IntuneSuppTeam
Do you remember when an IME update deleted the application config file and Win32 app installations suddenly stopped?
The Company Portal stayed stuck on “Downloading,” but underneath, the IME could no longer load the assemblies needed to validate the user token.
Microsoft has now returned to that config file in IME 1.103.101.0, and this time the fix goes further. The installer keeps a clean backup, restores the config when it is missing, and even replaces it when the contents have drifted.
It took a few attempts, but this finally appears to close both sides of the problem. I updated the original investigation with the new custom actions and exactly how the repair works.
Read the updated blog below!!!
#Intune #MSIntune #Windows11
patchmypc.com/blog/company-p…

@MSFTSecSuppTeam @msftsecurity is there anybody that can explain how AppControl can be made simpler if all the bootstrap exes that come from the Microsoft AppStore (Web) are signed by a Microsoft Certificate???
Roy Trenneman retweeted
Intune Management Extension: Release Notes.
When something changes in Intune, we usually get a “What’s new” update or a roadmap update. But what happens when the local IME changes?
That part is a big black box... And with the IME being responsible for much more than most people think. Win32 apps, scripts, remediations, reporting, APv2-related pieces, that list will only keep growing.
So I wanted my own Intune Management Extension Release Notes :) @IntuneSuppTeam :P
Every time a new IME version appears, an automation flow compares the MSI, custom actions, payload files, DLLs, and changed methods to determine what actually changed in the SideCar/IME agent.
#Intune #MSIntune #Windows11
patchmypc.com/blog/intune-ma…

Roy Trenneman retweeted
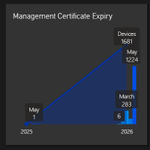
Under the Hood of the Intune Certificate
The Intune certificate matters more than most people think. That Certificate keeps the policy sync alive and is also needed for IME communication, which means apps and scripts depend on it as well.
But when the certificate or its chain breaks, things can get funny. The device can still show a recent last check-in, while it is no longer able to receive the latest policies, apps, or scripts.
In this webinar, we will explain what the Intune MDM device certificate does, what changed with the Intune Intermediate certificate renewal, why some devices may have missed it, and how to find devices that still appear healthy but may not be.
But hey, it is all fine because the last check-in still moved… right?
Register here: patchmypc.com/events/intune-…
#Intune #MSIntune

Roy Trenneman retweeted

We have released a new report in #Autopatch to help you evaluate the patching vulnerability risk in your estate, along with some new guidance for how quickly to take patches. #WindowsUpdate techcommunity.microsoft.com/…

Roy Trenneman retweeted

PSA: Known issue with April's LCU for basically everything.
In a _very_ specific scenario (see below), users are going to get a BitLocker recovery prompt after updating.
Link below is for one KB, but the story is the same everywhere.
support.microsoft.com/en-us/…
