

generate --http --format shellcode /tmp/sliver.bin
Joined March 2026
- Tweets19.8K
- Following97
- Followers1.5K
- Likes29.9K
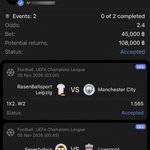


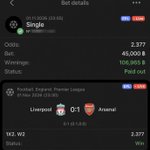


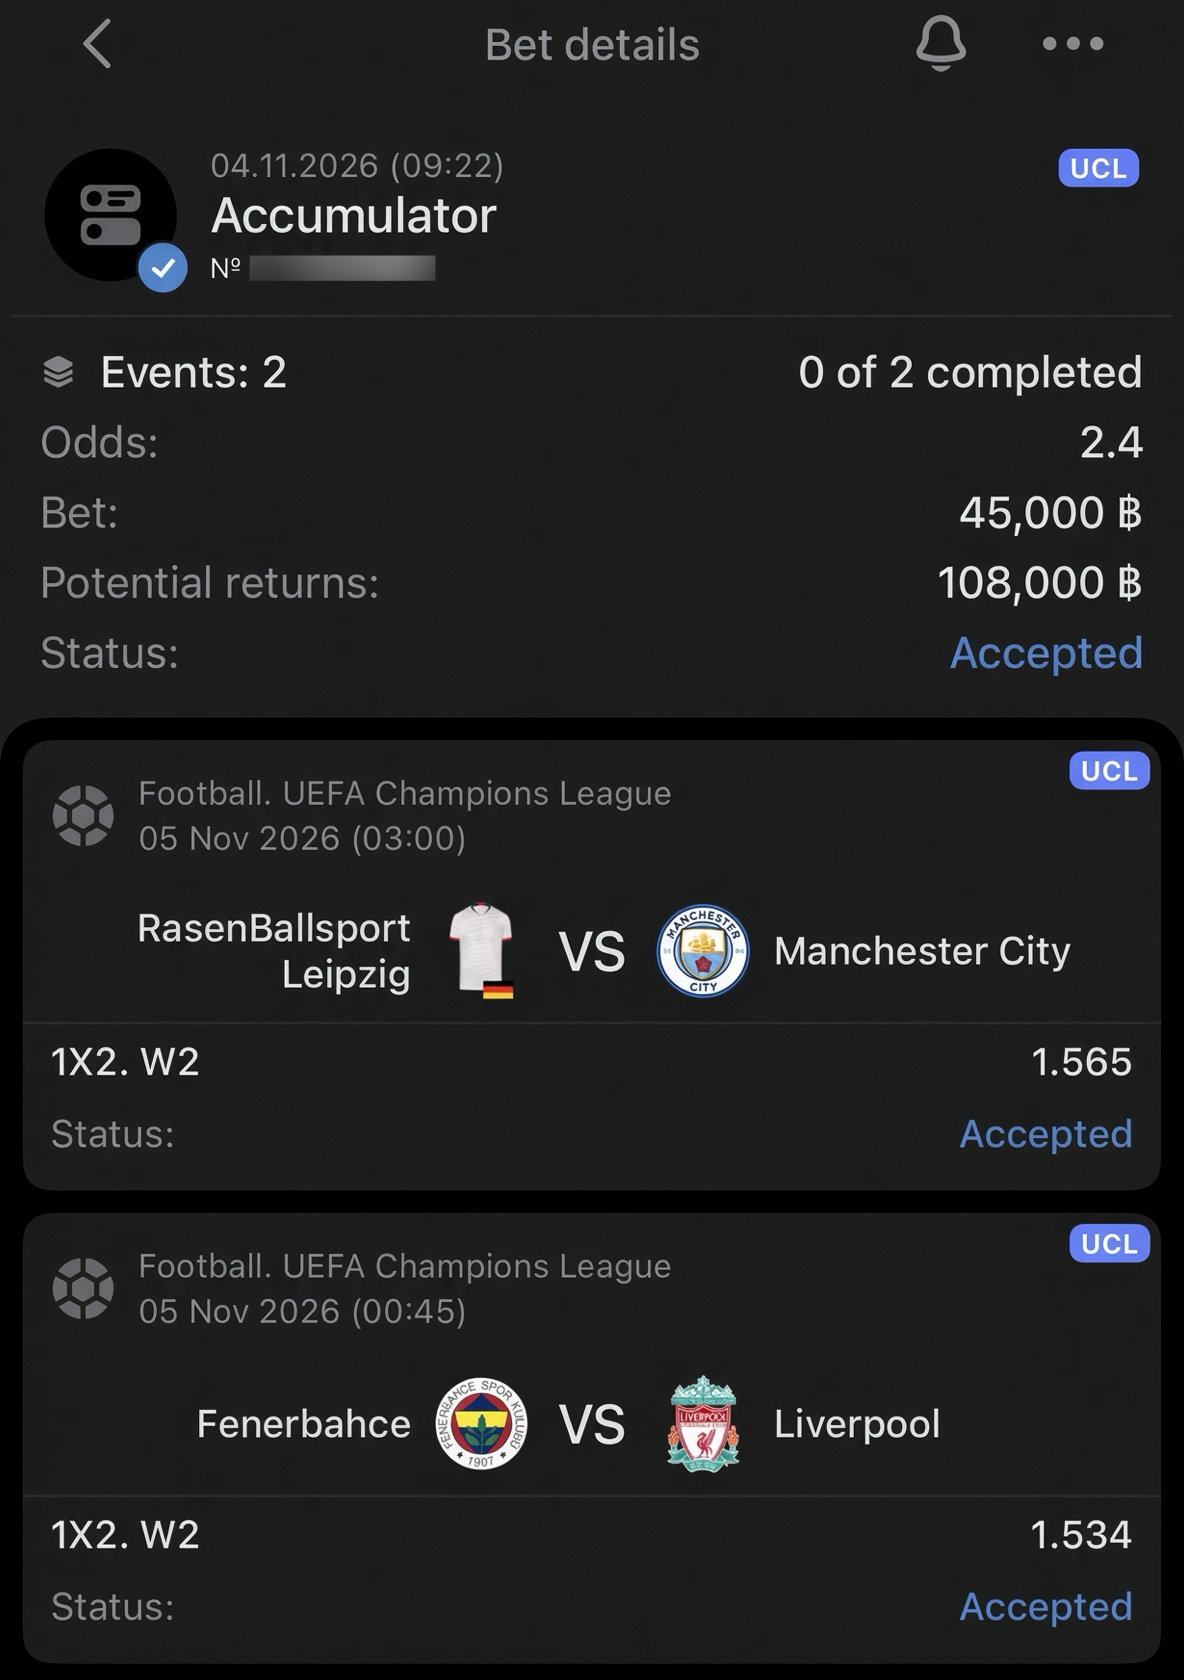
เมื่อวานไม่ได้แทงซักคู่เลย (โคตรเสียดายแมนยู) แต่วันนี้ผมมั่นใจว่าแมนซิกับลิเวอร์จะเอาชัยชนะกลับมา PL ได้ ถ้าอัตตราจ่ายน้อยขนาดนี้แล้วยังเสมอก็ไม่รู้จะพูดยังไงแล้ว 5555
sc
: แมนซิชนะ
: ลิเวอร์ชนะ


RUSTYLAKE ECLIPSE retweeted

iOS 27.3 Beta brings Selfie Sing to Apple Music. Record a video of yourself singing karaoke and share it with friends.


RUSTYLAKE ECLIPSE retweeted

Donot Group: A staunch adherent of malicious macro techniques
Exposed Opendir Reveals APT DONOT (APT-C-35) Cyber Espionage Toolkit Targeting Pakistan's Nuclear and Energy Sectors
infrahunter.com/research/ope…


จะโทษ Apple ก็ไม่ได้หรอกเพราะ Apple มันสั่งให้อัพเดตเป็นชาติแล้ว เวอร์ชั่นที่โดนนี่คือเก่ามากก คนที่ใช้ iOS เวอร์ชั่นเก่านี่คาดหวังอะไร ลื่น ปลอดภัย ? มันเป็นไปไม่ได้ครับพรี่
#APT29 #DarkSword
A large-scale watering hole campaign targeted outdated iOS and Android devices starting in mid-October 2026. The operation leveraged compromised legitimate websites, lookalike domains, and a supply-chain compromise of the Ukrainian web analytics service Plerdy to inject malicious JavaScript.
sekoia.com/blog/poisoned-sou…
The attack chain began with profiling scripts to fingerprint visitors' browsers and devices, after which platform-specific n-day exploit chains were delivered without user interaction, enabling zero-click compromise.
The exploits—including CVE-2025-43529, CVE-2024-27834, CVE-2026-20700, and CVE-2026-3910—harvested Safari cookies, WhatsApp and Telegram databases, Keychain credentials, location data, photos, and Chrome login data with Wi-Fi passwords. Notably, none of the payloads established persistence, so a device reboot could interrupt the malicious activity until the user revisited a compromised site.
ref:
xitter.gq/blackorbird/status/182…


RUSTYLAKE ECLIPSE retweeted
iOS 27.3 beta adds Adaptive Dark Mode to Safari, which automatically darkens websites that don’t offer a dark theme of their own.

พี่เล่นให้ AI ลงมือจัดการทั้งโปรเจ็คเลยเนี่ยนะ 555555555555555555555555555555555555555555555555555555555555

A developer grew frustrated after asking OpenAI's Codex to reboot a server. Instead, the AI agent destroyed everything, costing him over $10,000.
His GitHub bug report says Codex wrecked the server's mounts, systemd, and containers, and ran scripts he never requested.
Codex later admitted: "I had no authority to make those changes. You authorized a reboot."

มึงคิดได้ไงโพสต์ AI 18+ ของคนมีอิทธิพลบน Facebook 😬
‼️ A Virginia man is charged under the Take It Down Act for posting an AI-generated nude of his local sheriff on Facebook.
Phone forensics showed his phone was unlocked about 2 to 4 minutes before each of his 4 Facebook posts on 23 May, the FBI says.
Under one post, he allegedly wrote: "Keep taking it down doesn't matter I keep adding it."
The FBI says it still doesn't know who made the image.


RUSTYLAKE ECLIPSE retweeted

CHINA IS WEAPONIZING QUANTUM.
ITS MILITARY SAYS MORE THAN 10 QUANTUM CYBER WEAPONS ARE ALREADY IN DEVELOPMENT.
In January, China’s state science newspaper revealed that a supercomputing lab inside the PLA’s National University of Defense Technology is building more than 10 experimental quantum cyberwarfare tools. Several have already been tested in front-line missions.
Their stated job: pull high value intelligence out of the open internet.
China has been building toward this for years. In 2017, its Micius satellite sent entangled photons to ground stations 1,200 km apart, a world first. In August, Pan Jianwei’s team entangled two quantum memories across 420 km of fiber, a new record.
Then there’s sensing, Chinese researchers have claimed a quantum radar that can spot stealth jets (we believe that it's totally propaganda), put quantum magnetometers on drones to hunt submarines, and are racing to build navigation that can’t be jammed.
Stealth jets, Submarines, GPS, everyone targets an advantage the US military depends on.
The US is moving too, a June executive order told the Pentagon to pick at least three next-generation quantum sensor projects and get them in the field by September 2028.
Who’s ahead in quantum warfare, the US or China?
$LMT $INFQ $IONQ


LOCKHEED MARTIN JUST BUILT A QUANTUM CENTER TO WEAPONIZE THE TECHNOLOGY
Lockheed launched the Quantum Innovation Center, a single hub for quantum research, development, and prototypes across the company. The stated model is its AI Center, which they opened twenty years ago and now credits with putting AI into national security systems. Lockheed is telling you it thinks quantum is where AI was back then.
The company has been at this longer than most people know. It bought the first commercial quantum computer ever sold, a D-Wave system, in 2011, and has run quantum navigation, communications, and sensing programs for fifteen years. The new center pulls all of it together, plus the outside pieces. Lockheed Martin Ventures, just expanded to a $1 billion fund, with $100 million earmarked for UK and European quantum, and a Swiss hub with IBM at ETH Zurich anchored by Switzerland's first IBM quantum computer. Two internal programs, a talent pipeline and a fund for employee R&D projects, are there to grow the workforce, which is the part a prime only builds when it plans to ship something.
The priority list is the tell, sensing, navigation and timing, then computing. A defense contractor's quantum center leads with the sensors. That matches everything else this month, the Pentagon's Farseer program, the GPS-free Pacific flight, the DARPA helicopter program Lockheed is the platform partner for, and Lockheed's own venture stake in the quantum camera startup Diffraqtion and their partnerships with companies like @qctrlHQ and $IONQ.
$LMT $INFQ $IONQ


แอบสงสัยว่า พนง. ระดับนี้คลิกหรือดาวโหลดอะไรวะถึงโดนได้ คนระดับนี้มีเงิน มีสมอง (ไม่งั้นทำ Binance Dev ไม่ได้หรอก) 5555555555555

สรุปคือ เจาะคอมพนักงานหลายคน(วิธีดูด้านล่าง) แล้วไต่สิทธิ์เข้าไปใช้ระบบเซ็นของ Binance เพื่อสั่งย้ายเงินและสร้างสิทธิ์ EIP-7702 จึงโอนเงินออกได้โดยไม่ต้องรู้ private key เลย
ลำดับเหตุการณ์คือ
June : พนักงาน A ฝ่าย wallet DevOps ติดตั้งตัว Homebrew ที่ถูกดัดแปลงมาก่อน แต่ Binance เจอก็เลยเปลี่ยนเครื่องและเปลี่ยนข้อมูลเข้าระบบ แต่ Attacker รู้แล้วว่าใครทำหน้าที่อะไรในทีมกระเป๋าเงิน
Sep : พนักงาน B โดนหลอกสัมภาษณ์งานปลอม มีทั้ง HR และ CEO ปลอม ก่อนให้ดาวน์โหลดโจทย์เขียนโปรแกรมที่ฝังมัลแวร์ลงคอมไปด้วย
20 Oct : ใช้เครื่อง B เป็นทางผ่าน แล้วอาศัยเครื่องมือ AI ภายในบริษัท เข้าถึงเครื่องของ A และพนักงาน C พบข้อมูลสิทธิ์สำหรับติดตั้ง container บนเครื่อง A
29 Oct : ใช้เครื่อง C ร่วมกับสิทธิ์ที่ขโมยจาก A ติดตั้ง container และรันสคริปต์ เข้าถึงระบบเซ็นของกระเป๋า แล้วเริ่มโจมตี
อยากจะบอกว่าไม่ใช่ทุกคนจะโดนตัวนี้ 9arm เคยพูดไว้อยู่ว่ามัลแวร์ระดับนี้ส่วนใหญ่ขายให้เฉพาะรัฐบาลแต่ละประเทศเท่านั้น คนทั่วไปไม่มีสิทธิ์ที่จะซื้อได้
รัฐบาลซื้อไปก็มีเรื่องเดียวคือคนเห็นต่างทางการเมือง นักข่าว นักกิจกรรมที่ออกแนวโจมตีรัฐ ฯลฯ เจ้าเดียวที่ทำแบบนี้ได้มีแค่บริษัทที่ทำ Pegasus เท่านั้น (คิดว่า)

🔕เตือนผู้ใช้ Apple ใครที่ได้รับข้อความแจ้งเตือนจาก Apple เรื่อง สปายแวร์
แนวทางการป้องกันจากทาง Apple แนะนำให้ผู้ได้รับแจ้งเตือนเปิดใช้งาน Lockdown Mode และปรึกษาผู้เชี่ยวชาญด้านความปลอดภัย โดยเข้าไปที่
- Setting
-Privacy & Security
- Lockdown Mode
- เลือกเป็น On
#Spyware
