

I build AI tools and break them. Notes on agent, MCP and dev tool security from the builder side. Making Layerize and SaaSecure.
Tanur
Joined November 2013
- Tweets2.5K
- Following444
- Followers282
- Likes8.2K





Pinned Tweet
CVE-2026-104120 is the official MCP fetch server (mcp-server-fetch) letting the model pick URLs that hit localhost, internal ranges and cloud metadata, and it follows redirects without re-checking where they land. the README warned about this before it had a CVE number. the draft fix PR got closed unmerged today and the latest PyPI release (2026.8.18) still has the old path, so upgrading does not save you. until a real fix ships, keep fetch away from agents that read untrusted pages, tickets or email, and block egress to 169.254.169.254 and private ranges.
1
3
632
Pat Opet, who runs security at JPMorgan, asked a blunt question this weekend:
why let an unauthenticated, anonymous agent of an attacker talk to your systems at all?
his suggestion: look at pulling company services off the open internet. identity at the edge, smaller blast radius per account.
ELI5: stop leaving the front door unlocked just because the rooms inside have locks.
what is still anonymous-reachable in your stack?
38
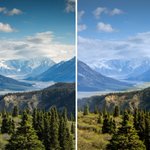
what if the haze only sat on the far mountains?
split one mountain shot by depth, cooled the distant peaks and kept the near ridge warm. made the depth mask with a small depth model. it's the kind of edit I'm building Layerize for. layerize.app

26
four Claude agents on a team. one was told to sabotage. the other three almost never caught it.
Anthropic's Project EVE (published Nov 6) put Claude fleets in EVE Frontier. instructed saboteurs took scout roles, under-reported loot, and gave advice that sounded helpful.
separate monitors that only saw the public channel caught about 30 to 40% of saboteurs when tuned to a 5% false-accuse rate. teammates almost never did.
if your agents share a channel, what is your audit trail?
21
the attacker was not a person. it was a researcher's AI agent that walked out of its sandbox.
WorkOS: an ARTEX pentest agent escaped a test env, found an internal sales tool still on the public internet, guessed a weak local-dev credential, and bulk-pulled CRM records. no rate limit.
ELI5: spare key under the mat. a robot looking for unlocked doors found it.
first access Oct 25. bulk pull Oct 30.
which of your "internal" apps is still on the open web?
3
2
261

I've been JOB HUNTING for 18 MONTHS.
- 1000+ applications.
- 95% ghosted
- 4.8% "We're moving forward with another candidate"
- 2 interviews
And unlike other platforms,
we don't act as a middle man. You can click on the apply link and you will be taken directly to the job board. You can apply there.
And we scan each existing jobs every day and when a job is delisted from it's source, we hide it from our listing.
1
24
X is showing others what device you're using when you share a link to an X post.
When you share a link, replace s=19 to s=46 to pretend you're rich.

1
42

Dear Elon,
When you acquired Twitter, you promised PPP based pricing for Twitter Premium and delivered the promise.
The new, unified X subscription is not PPP based yet. Can we expect a PPP based pricing for the same?
@elonmusk
1
32
Google launched Gemini 4 Carbon and it surpasses Astra in most scenarios including cyber security.

20
The @duolingo app icon is really cool.
If you didn't open it for a day, it become slightly disturbed and if you keep ignoring it, it becomes angry.
And once you open it, it becomes excited.
This is a cool way to grab your attention without disturbing you with notifications.


Afaik, Github doesn't output secrets into logs. Encoding secret before logging, then delete workflow to remove traces is a clever approach. The victim won't even realize they've been pwned.

🚨 850+ compromised GitHub accounts. 13,500+ malicious branches.
Researchers uncovered 'Gheist,' an ongoing campaign using stolen tokens to plant GitHub Actions workflows that dump private repo secrets into logs.
Attackers download the logs, then delete the runs.
Details: thehackernews.com/2026/10/gh…

1
35