

Danish National Cyber Team 2026 | young security researcher
Joined August 2025
- Tweets633
- Following108
- Followers111
- Likes1.4K




Sergio retweeted
I largely agree with you, but I honestly understand their perspective. And I would even go as far to say that Daybreak blue is a bit TOO permissive, compared to what is actually proved.
Imo, if OpenAI had the background checks like Anthropic do in strictness for their CVP program, then yes, make it this permissive.
But for somewhere where the only thing you actually need is KYC, this is way too permissive. I shouldn’t be allowed to make a chromium exploit with only KYC. We already see how threat actors sell crypto KYC accounts for relatively cheap, and chances are they are probably also already selling access to Daybreak blue accounts as well.
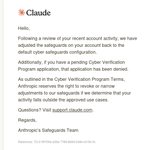
Anthropic on the other hand are a bit too strict on their program. I think you should at least be able to get a slightly less restrictive version for vulnerability research/discovery, since the default safeguards provide a kind of fake access to vulnerability research.
And then tiers for active probing/attacking.
Idk exactly the best model as I haven’t thought about it enough for it, yet. But that’s my opinions.
I have released the FIRST poc of the wp2shell exploit on my github. Still working on getting command execution github.com/sergiointel/wp2sh…


Sergio retweeted

Anthropic CEO, wasn't lying when he said
“I have engineers within anthropic who don’t write any code, they just let Claude write the code and they edit it and look it over”
he gave us live examples and respect for the transparency 🫡

Claude code source code has been leaked via a map file in their npm registry!
Code: pub-aea8527898604c1bbb12468b…

Sergio retweeted

LeakBase admin "Chucky" was arrested.
For those unfamiliar, LeakBase was this big ass fuck off website which sold, traded, auctioned, and freely distributed stolen data from compromised websites or companies.
LeakBase audience was primarily Eastern European.
Despite the wide spread identify theft, credit card fraud, extortion, initial access brokering, and money laundering that "Chucky" enabled, he was a nice guy.
I used to send silly pictures of kitty cats to him.
Sergio retweeted

Gave an interview for Inside Darknet! 🕵️♂️
Do you think it’s possible to de-anonymize the leaders of the most dangerous ransom groups?
My experience is in the text version of the interview: archive.ph/NKNNP
Thanks to @insidedarknet for the interesting questions!
