

The elite security team at @LevelBlueCyber. Response & Investigations. Analysis & Testing. Research & Development. Follow for info on the latest threats.
Everywhere
Joined January 2009
- Tweets6.1K
- Following364
- Followers27K
- Likes270






Ransomware has dominated conversations for years.
But over this past quarter, we saw the pressure point shifting. 🔃
Across @LevelBlueCyber incident response engagements, data exfiltration appeared in more network and cloud intrusion cases than encryption, indicating that stolen data is becoming a faster route to extortion.
The numbers from Q3:
📊 BEC accounted for 32% of incidents
📊 Network intrusion accounted for 22%
📊 Ransomware accounted for 20%
More attackers are finding they don’t need encryption to create leverage.
Our Q3 TTP Briefing breaks down what we observed across real-world investigations worldwide. 🔎🌎
View the recap below:
hubs.ly/Q04CB-_W0

🚨 New research: Our team is tracking #Wazza, a multi-stage device code phishing kit targeting #Microsoft 365 accounts. Active since at least July 2026.
Victims receive PDF lures and are routed through a phishing chain using staging and redirector links, Cloudflare Workers and attacker-controlled domains. The kit uses filtering and decoy pages to steer targets to the final device code page. Final pages seen so far impersonate #Adobe, #DocuSign, and #Microsoft services and abuse Microsoft OAuth device authorization.
Read our full analysis: levelblue.com/blogs/spiderla…

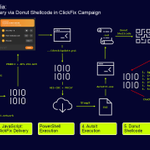
The #OpsCTI team analyzed a #PhantomPolia campaign leveraging #ClickFix to deliver #RemusStealer through #DonutShellcode. The investigation also identified Sepolia smart contract addresses relevant to the campaign.
🔍 Read the full #SpiderLabs analysis:
levelblue.com/blogs/spiderla…
IoCs:
Sepolia Smart Contract Addresses
0x4dbdca7277427edee4d5b4e3d012bca73aefadf1
0x28b7605be52b7107cd7710f6f855a1a026e72f4a
0x5ea589954314fe8d5ecb509b35d77a389912b42f
0x5a3589462b41fa8cf91ac2c7773a285d9c790548
0x3b14187b76dc39005e8d568b26455d53bd198749
0x61b3e0681f6485e4e85e5ee981757d8b12ec414f
0x5a155a3f01fa60c3fa0177022ba05fcc6a313a4d
#PhantomPolia domains
voderlence[.]com
nightflamevortex[.]top
voidravenstorm[.]top
velnoderic[.]com
ironphantomcore[.]top
stormvenomforge[.]top
shadowemberstrike[.]top
URL path
/check/update[.]ps1
#RemusStealer C2
oceanvw[.]click
cruahop[.]shop
drepace[.]click
spogear[.]click
Main Installer
05629f35dfe1409ea963c135581c228e3b71869b0707974244f6938af635a70e
8f4903b8b110ec1b9580a5a27bf49c3e4793538a863100559d085b7545fcda25
f02e2fefd74c7268e3aced61017173fff92e2a1d0e7eaf7807189f371fbfcc1f
AutoIt Scripts
61def8b242913b520ec110458a416b02a6a38dc8765bc76bd571ee7ae8350aae
22b0fc350b5e5c557344267b3c44323ac117d3fbeb5cf1bcb8b027352155fa11
a38e6f54efe342b4a2ca9ac4428a5268faed96cd602baa1886efb09f72435abb
Donut Shellcode
5363bc92bac44aa2ba87b46c59fd3f78d5cdd32839efa854e97380a55fdacabb
Remus Stealer
dc0a864f441f0237853b40217eda577defb7c1dd15af407c7241688b1b3a3b46
a0923188fbd52277e1711ae312f3c6fb841f3cdebe1a95d5c89fe2455f8ace32


🚨 #MalwareAlert: A fake bank payment receipt MSI installs a LuaJIT runtime alongside a Lua script disguised as a font. The decoded Lua runs Donut shellcode in memory, which carries Agent Tesla infostealer set for FTP exfiltration.
#IoCs:
ADCB_Bank_Payment_Transfer_Receipt pdf.msi
14f920e611772134999e437c05956970aa4ac8e1a07ba65568e7c24d5b641390
LuaJIT runtime (MainExeFile)
52f0c0230b580e2fdf53a378b5c6d0db9829af900dae43e0df8f18635cd9f0c1
Disguised Lua (ScriptFile)
bbc8388371a9a41079191d88893e4599964c6b6246d97953de5c94033b19f900
Raw Donut shellcode
11ca4a2f90b53a58477bf86d565f73e0ada6846a8bab7ff110ffedc4ee8b85be
Recovered Agent Tesla EXE
ddc85ad4885dd3da9ac8de4c3bc0392c0b2ccee075b79c8564ba71394d5b7aa6
FTP exfiltration host: ftp[.]fundacionpiaz[.]org
#MailMarshal #cybersecurity

🔎Observed IoCs:
70.172.58[.]168
45.141.21[.]130
162.243.36[.]88
173.40.135[.]209
47.230.224[.]154
23.27.143[.]20
62.133.62[.]80
64.94.85[.]67
92.118.204[.]229
87.224.84[.]82
31.56.197[.]72
hxxp://62.133.62[.]80:80/xd7h/x
hxxp://23.27.143[.]20:9000/main.py
hxxp://64.94.85[.]67:443/update_c08937.pl
hxxp://64.94.85[.]67:443/update_result_3567cs.tgz
hxxp://31.56.197[.]72:9090/lula
e9fe43968c6c0955300e3bc4d7fb0b05a18570b4733aaf4f5c6f7f09be5a242c
974b69782fdf5d67b97cfd508465939e44ee10798dbcc1e82b92d78776bad938
/var/netscaler/logon/LogonPoint/.local_journal
/tmp/update_result_3567cs.tgz
/var/netscaler/logon/insight-new.js
/var/netscaler/logon/LogonPoint/xua.html sec_monitor

🔱 We observed active exploitation attempts targeting Citrix NetScaler appliances affected by CVE-2026-88771, including activity progressing beyond basic command-execution testing.
The vulnerability allows unauthenticated attackers to inject commands through attacker-controlled authentication data that is later processed by a privileged NetScaler component, potentially resulting in command execution.
🕷️ @LevelBlueCyber THOR identified malicious authentication events containing command-injection payloads across multiple customer environments.
🕷️ Observed activity included payload retrieval, NetScaler configuration collection and staging, reverse-shell deployment, and attempted configuration exfiltration.
🕷️ Analysis of main.py identified a second-stage payload designed to overwrite customsnmpd and establish a reverse shell to attacker-controlled infrastructure.
🕷️ A separate Perl payload, update_c08937.pl, creates a privileged sec_monitor account, collects NetScaler configuration data, and deploys a PHP web shell.
🕷️ Our analysis includes observed IOCs and behavioral detection opportunities defenders can use to identify exploitation and post-exploitation activity.
Full analysis: levelblue.com/blogs/spiderla…
🔱 We observed active exploitation attempts targeting Citrix NetScaler appliances affected by CVE-2026-88771, including activity progressing beyond basic command-execution testing.
The vulnerability allows unauthenticated attackers to inject commands through attacker-controlled authentication data that is later processed by a privileged NetScaler component, potentially resulting in command execution.
🕷️ @LevelBlueCyber THOR identified malicious authentication events containing command-injection payloads across multiple customer environments.
🕷️ Observed activity included payload retrieval, NetScaler configuration collection and staging, reverse-shell deployment, and attempted configuration exfiltration.
🕷️ Analysis of main.py identified a second-stage payload designed to overwrite customsnmpd and establish a reverse shell to attacker-controlled infrastructure.
🕷️ A separate Perl payload, update_c08937.pl, creates a privileged sec_monitor account, collects NetScaler configuration data, and deploys a PHP web shell.
🕷️ Our analysis includes observed IOCs and behavioral detection opportunities defenders can use to identify exploitation and post-exploitation activity.
Full analysis: levelblue.com/blogs/spiderla…
Noise is everywhere. Signal is rare. 🎯
#SpiderLabs focuses on what actually matters so your team can move faster with fewer distractions. 🕷️
Take a closer look at how that kind of visibility shows up in the real world:
hubs.ly/Q04pPTc00
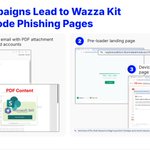
🪝 We are observing active PDF #phishing campaigns impersonating #Adobe and #Microsoft that redirect victims to #Wazza Kit device code phishing pages hosted on workers.dev.
- #MailMarshal detected phishing emails from compromised accounts containing PDF attachments with document-themed lures
- The broader campaign leverages Google Sites (sites.google.com), Cloudflare Workers (workers.dev), and .eu Top Level Domains to host phishing content and related infrastructure
- Wazza kit supports 19 themes via the ‘?thm=‘ URL parameter across six lure categories: file-sharing, account, document, payment, HR, cloud and brand impersonation.
- The kit validates URL patterns, including subdomain and slug checks, to selectively serve phishing content and redirect non-targets to decoy pages.
#IOCs:
beacon-surge-sync[.]workers[.]dev
beton-beton[.]eu
bike-msca[.]eu
bodi-project[.]eu
bruoth-family[.]eu
cardamomo[.]eu
coppietersrecherche[.]eu
diabetesnet[.]eu
dymowski[.]eu
euniverza[.]eu
hutspotmaken[.]eu
illuminatedminds[.]eu
jetcapital[.]eu
languagesforwork[.]eu
lesbolides[.]eu
mdiament[.]eu
nbi-training[.]eu
nellarmonia[.]eu
originalpizza[.]eu
polskaprezydencjacsr[.]eu
robologic[.]eu
safetystock[.]eu
electroloys[.]com
hacsg[.]com
sites[.]google[.]com/view/hgfdsqazxcvhjoswwqq/home
sites[.]google[.]com/view/adobe-docus/home
sites[.]google[.]com/view/miticabo/home
sites[.]google[.]com/view/ctfvygbuhgyftvbgyfpoiuytrftgyh/home
sites[.]google[.]com/view/kjvcfdswqazxcfvghjoplkjmnbvcf/home
sites[.]google[.]com/view/securespdf/home
sites[.]google[.]com/view/onwajuly/home
dv0psh-purv3w-azfn-b2c0-msauth3-m365svc-s3ntln-4zrfn3x-cntnrx[.]workers[.]dev
ssosvc-m365s-kvl-dv0pshb-s3ntln-c0mply-4zrmonx-apimgwx-evnthb[.]workers[.]dev
wndws-pip3ln-sql3-waf3-purv3-gdprsx-dfn-azfn-appsvc-0ffapx[.]workers[.]dev
purv3w3-t3ms4pp-certs-intun3-sbussvx-4zredg-siemsv-pip3ln-0ffc3[.]workers[.]dev

Some vulnerabilities patch. Some vulnerabilities keep sending follow-up emails.
Just days after Microsoft's September Patch Tuesday, Nightmare-Eclipse dropped ShieldCrash, the latest chapter in a Defender bypass lineage we've been tracking through RoguePlanet and ShieldBreak.
3️⃣ PoCs.
2️⃣ patches.
1️⃣ underlying mechanism that's proven remarkably difficult to evict.
Our testing found the public release is more "skeleton" than fully weaponized exploit, but buried in the artifacts, telemetry, and object-manager activity is a bigger lesson for defenders: understanding how a technique survives remediation often matters as much as understanding the vulnerability itself.
hubs.ly/Q04xP4GN0

Our researchers recently found a 7-stage exploit chain that abuses Cloud Files, Windows Object Manager namespaces, Defender remediation and Windows Error Reporting to escalate from a standard user to SYSTEM on fully patched Windows systems.
levelblue.com/blogs/spiderla…

A ClickFix case brought our team down a BabaDeda chain that led to an undocumented end: CNCMachineRMS, a 1.14 MB RAT with zero imports, every string built on the stack, and its own scripting language.
The full research + PDF report below. ⤵️
hubs.ly/Q04swfMb0

🪝#Phishing Alert: LevelBlue #MailMarshal has detected a phishing campaign targeting hotels, venues, and wedding service providers. Threat actors are sending convincing fake business inquiries covering wedding venues, event planning, and related services to trick recipients into responding.
The initial emails contain no links or attachments and use recently registered Reply-To domains. Once a target replies, attackers follow up with another email with either phishing links or malware attachments.
IOCs:
absolutdmc[.]com
apexvistaventures[.]com
aurellefashion[.]com
eu-starstups[.]com
eventr[.]cc
grandcrestevents[.]com
grandstayrental[.]com
inwoods-hotels[.]com
iwonderpicture[.]com
quantumtradecollective[.]com
shinilglobals[.]art
sophiaevent10[.]com
sophiatech[.]xyz
westsinvalencia[.]com
westpeakproperties[.]net

Some teams follow alerts. SpiderLabs follows behavior, patterns, intent, and instinct, long before it reaches your environment. 🕷️💡
Precision matters when threats evolve overnight.
Take a closer look at how that kind of visibility shows up in the real world. ⤵️
hubs.ly/Q04pPM7H0
Our gift to you: we have decided to do something for the community, with the hopes that more security vendors follow suit. We've been developing an advanced open-source Linux engine - dubbed owLSM - and have made it accessible for free, just for YOU.
Meet owLSM:
⭐ A full Sigma rules engine in the kernel, implemented with eBPF LSM (Linux Security Module).
⭐ Kernel prevention capabilities that allow us to block operations before they occur.
⭐ Broad anti-tampering capabilities.
⭐ Security-focused system monitoring where each event contains all the context a security expert needs.
Explore how owLSM can help you mitigate vulnerabilities: hubs.ly/Q04pwTrm0

A fake photo. A legitimate http://Node.js download. A blockchain-hosted C2.
This campaign layers familiar tools and emerging techniques to stay hidden.
hubs.ly/Q04pvSWB0

🚨#BEC Alert: We recently detected a Business Email Compromise (BEC) attack targeting newly hired employees. In an effort to bypass corporate email security defenses, threat actors sent messages to both employees' corporate and personal email accounts. After the initial welcome message, victims are instructed to purchase gift cards for a fake employee gift-giving initiative.
Always stay vigilant as threats don't stop in the corporate inbox!
IoC:
oofficemail[.]co[.]nz@mail[.]ru

Threat activity is already in motion before it gets named, tracked, or reported. #SpiderLabs stays on the moving edge, turning live activity into decisions teams can act on without slowing down. 🕷️
Threat intelligence that holds up when operations are moving at full speed: it’s the SpiderLabs standard.
hubs.ly/Q04pbnNc0