Monad Maxi; #ETH; #pudgypenguins; hababeo.eth; Shit-poster and dream-chaser, don't trust anything I tweet, they're all shitposts. DYOR. Crypto baghodler
Joined December 2017
- Tweets21.2K
- Following1.7K
- Followers1.6K
- Likes177K




Pinned Tweet
I've decided to create my own Strategic Bitcoin Reserve. Like the US. government, I'm developing a budget-neutral strategy for acquiring my bitcoin at no incremental cost. Phase one of my strategy is inviting contributions to my reserve
bc1q0gqg0cwwyffctw5kcskcezu7xdl3hdq0hgulpv
Harry (MON to $1) retweeted

Quantum security cannot be an afterthought

Today Physical Superintelligence PBC is announcing a proof of the Aaronson-Ambainis conjecture, one of the central open problems in quantum complexity, with major implications for quantum computing speedup.
psi.inc/research/aaronson-am…
Thread 👇

Harry (MON to $1) retweeted
At the beginnings of a movement, to outsiders, the odds seem impossibly long. How could a tiny thing change the world? The believers, what idiots they are. How embarrassing, to believe something might matter.
To the believers, the signals are there. In hindsight, those signals become obvious. But in the moment, it is not easy to drown out the wisdom of the crowd. Good luck.
Harry (MON to $1) retweeted

there's a team at the cutting edge of crypto R&D
started by highly accomplished HFT traders, expanded and hired s-tier researchers and cryptographers
built a highly performant and decentralized EVM L1 (over 10k TPS on a globally distributed system)
baking institutional use-cases directly into the protocol design (privacy, MEV resistance)
very security minded (for ex. credible post-quantum roadmap)
iterating extremely quickly (numerous protocol updates in less than a year, multiple award winning research papers)
and this is just a small summary of the resume
i used to imagine what it'd be like if teams like this built in crypto, i think a lot of people did
i guess hope was in greater supply back then
but i really just don't think it'd be that insane if the vision for ethereum actually played out
maybe the timeline was wrong. maybe even a different protocol
it's hard to argue that it wouldn't lead to a better world
fair finance, a level playing field for anyone to compete on
transparent, open source, decentralized
there are absolutely many hard problems to be solved, and a lot of growth to drive
not things that happen overnight
but eventually
Harry (MON to $1) retweeted
Today, @category_xyz is sharing the full whitepaper for Monad Private Settlement Domains (MPSDs)
Quick summary:
* transactions encrypted for the domain, ordered by Monad
* operators execute in Monad’s order; no separate domain consensus
* operators submit attestations and state commitments to Monad
* contracts exchange asynchronous messages across private domains and with public Monad
* contract access rules written in Solidity
MPSDs position Monad for a future where institutions move more of their financial operations onchain. Those institutions will need privacy and control, alongside access to shared liquidity and other applications.
The design puts Monad at the center of that activity. Institutions run their applications privately while using the public network for transaction ordering and settlement.
We are building for where institutional demand is heading, so Monad can support that growth while delivering the best of all worlds between privacy, compliance, and composability.
Whitepaper link in the next tweet

Last month, we introduced Monad Private Settlement. Today, we're publishing the technical white paper.
It details private execution domains, shared sequencing on Monad, cross-domain messaging, and configurable access controls.
Read the research: category.xyz/mpsd-whitepaper
Harry (MON to $1) retweeted
Smart contract developers, please run Ultrafuzz on your contracts!! It's open source and available to anyone, consolidating many years of learnings from @aviggiano
github.com/monad-developers/…
If you run into any issues, Antonio is eager for feedback, DM him

Harry (MON to $1) retweeted
In this age of AI-empowered attackers, the only way forward for our industry is to continue hardening. Security should be every team's top focus.
The Monad Foundation invests heavily in security and is sharing the following resources to the community:
Everyone:
- The Crypto OpSec Bible: monad.xyz/blog/crypto-opsec-…
Smart contract developers:
- Importance of not relying on EOAs for admin roles: monad.xyz/blog/say-no-way-to…
- Importance of only signing admin functions on a dedicated laptop: monad.xyz/blog/monad-foundat…
Hardening code with Ultrafuzz, our open source tool for agentic fuzzing and threat hunting:
- Codebase: github.com/monad-developers/…
- Overview: monad.xyz/blog/ultrafuzz
- monad.xyz/blog/open-sourcing…
Learnings from the field on threat hunting with LLMs:
- monad.xyz/blog/writing-secur…
- monad.xyz/blog/evaluating-my…
Learnings from securing code with Formal Verification:
- category.xyz/blogs/finding-b…
- category-labs.github.io/cate…


Harry (MON to $1) retweeted
Monad is now on the Pumpfun app!
You can now find and trade Monad assets on the Pumpfun app
Thanks to the Pumpfun team for the support, and catch you on chain


Harry (MON to $1) retweeted
Wow, here is a substantial advancement in theoretical consensus research from @komasito55 (of @category_xyz), @ElodinStorm and Ling Ren!
It resolves a long-standing open question and improves on the previous-best O(n^3) communication complexity of the Dolev-Strong algorithm published in 1983. The new algorithm is near-quadratic while tolerating any number of faulty participants below the total
Category Labs is making fundamental research progress as they continue to improve Monad through exceptional pragmatic algorithm engineering
Dolev–Strong is arguably the best-known consensus protocol, and for roughly 45 years, no deterministic protocol improved on its O(n³) communication.
A new paper by @komasito55, Yuval Efron and Ling Ren improves that bound to O(n² log⁴ n) for Byzantine Broadcast, tolerating t < n faults in O(t) rounds.
After thinking about the problem on and off for years, they started leveraging AI models. The paper is the result of a month of human experts digesting and simplifying the discourse with AI.


Harry (MON to $1) retweeted

HOLY SHIT.
For crypto, this is one of the most insane posts of the year, but I'm guessing most people don't understand it.
Let me explain...
Bitcoin's accounts, and subsequently Ethereum's (and therefore every other EVM chain's), are built on a specific elliptic curve called secp256k1.
secp256k1 is a different elliptic curve from the one used across nearly every modern hardware device, including iPhones.
Modern devices mostly use a different curve called secp256r1, which is usually referred to as P-256 - one of the curves investigated in the article.
This mismatch has made it sooo difficult in the past to integrate crypto accounts natively into the security systems of modern hardware.
For example, Apple's Secure Enclave natively supports P-256, not secp256k1.
This has prevented crypto accounts from being able to use the same hardware protection as things like Apple Pay.
Same goes for the web with passkeys - WebAuthn uses P-256 signatures, which means Ethereum accounts using secp256k1 can't use them natively either.
But why did Satoshi do this?
The main theory for choosing secp256k1 was distrust of the P-256 curve - i.e. he thought there was an NSA backdoor.
A "backdoor" here basically means a secret, intentional weakness in the curve that would allow the NSA to exploit it and access private keys.
This was because P-256 was created with involvement from the NSA...
And the NSA provided a mysterious "seed" used to generate one of the curve's parameters without explaining where that seed came from.
This eventually transformed into a ~25-year-old mystery with a 5-figure reward for finding where this seed came from.
Claude figured it out in less than 30 mins.
And the best part is its internal thinking was: "Hmm wait... is it suspicious that such an obvious thing wasn’t discovered in 25 years?"
The solution was stupidly simple - just the time the curve was created, put into a specific random number generator function.
This doesn't 100% prove there's no backdoor yet, but it provides strong evidence that this seed wasn't secretly engineered by the NSA.
And Claude did this with "just a simple prompt" in under 30 minutes.

CLAUDE FOUND THE SEEDS
anthropic.com/research/ecdsa…

Harry (MON to $1) retweeted

Cities weren’t built in a day.
If you’re looking for quick, build a sandcastle.
Harry (MON to $1) retweeted
Monad’s focus:
- MEV-resistance
- Multiple concurrent proposers
- Quantum security
- Private domains integrated into public liquidity
while continuing the march toward the endgame architecture of decentralized systems


Harry (MON to $1) retweeted
ICYMI @monad Open was MASSIVE:
- @category_xyz announces Monad Private Settlement
- @xStocksFi announces 1000+ tokenized equities coming to Monad
- @crshmarket announces $4.3m funding round
- @RobinhoodApp today announced MON listing
And much more.
Monad everywhere (soon).
Harry (MON to $1) retweeted
Today we are announcing Monad Private Settlement, which gives banks and enterprises the best of both worlds: sovereign execution environments with privacy and compliance by default, which benefit from the composability and performance of Monad
Monad Private Settlement enables an onchain financial ecosystem where enterprises can run entire business processes onchain and interact with each other on the open Monad network.
Read the design specifications here: category.xyz/monad-private-s…
Harry (MON to $1) retweeted

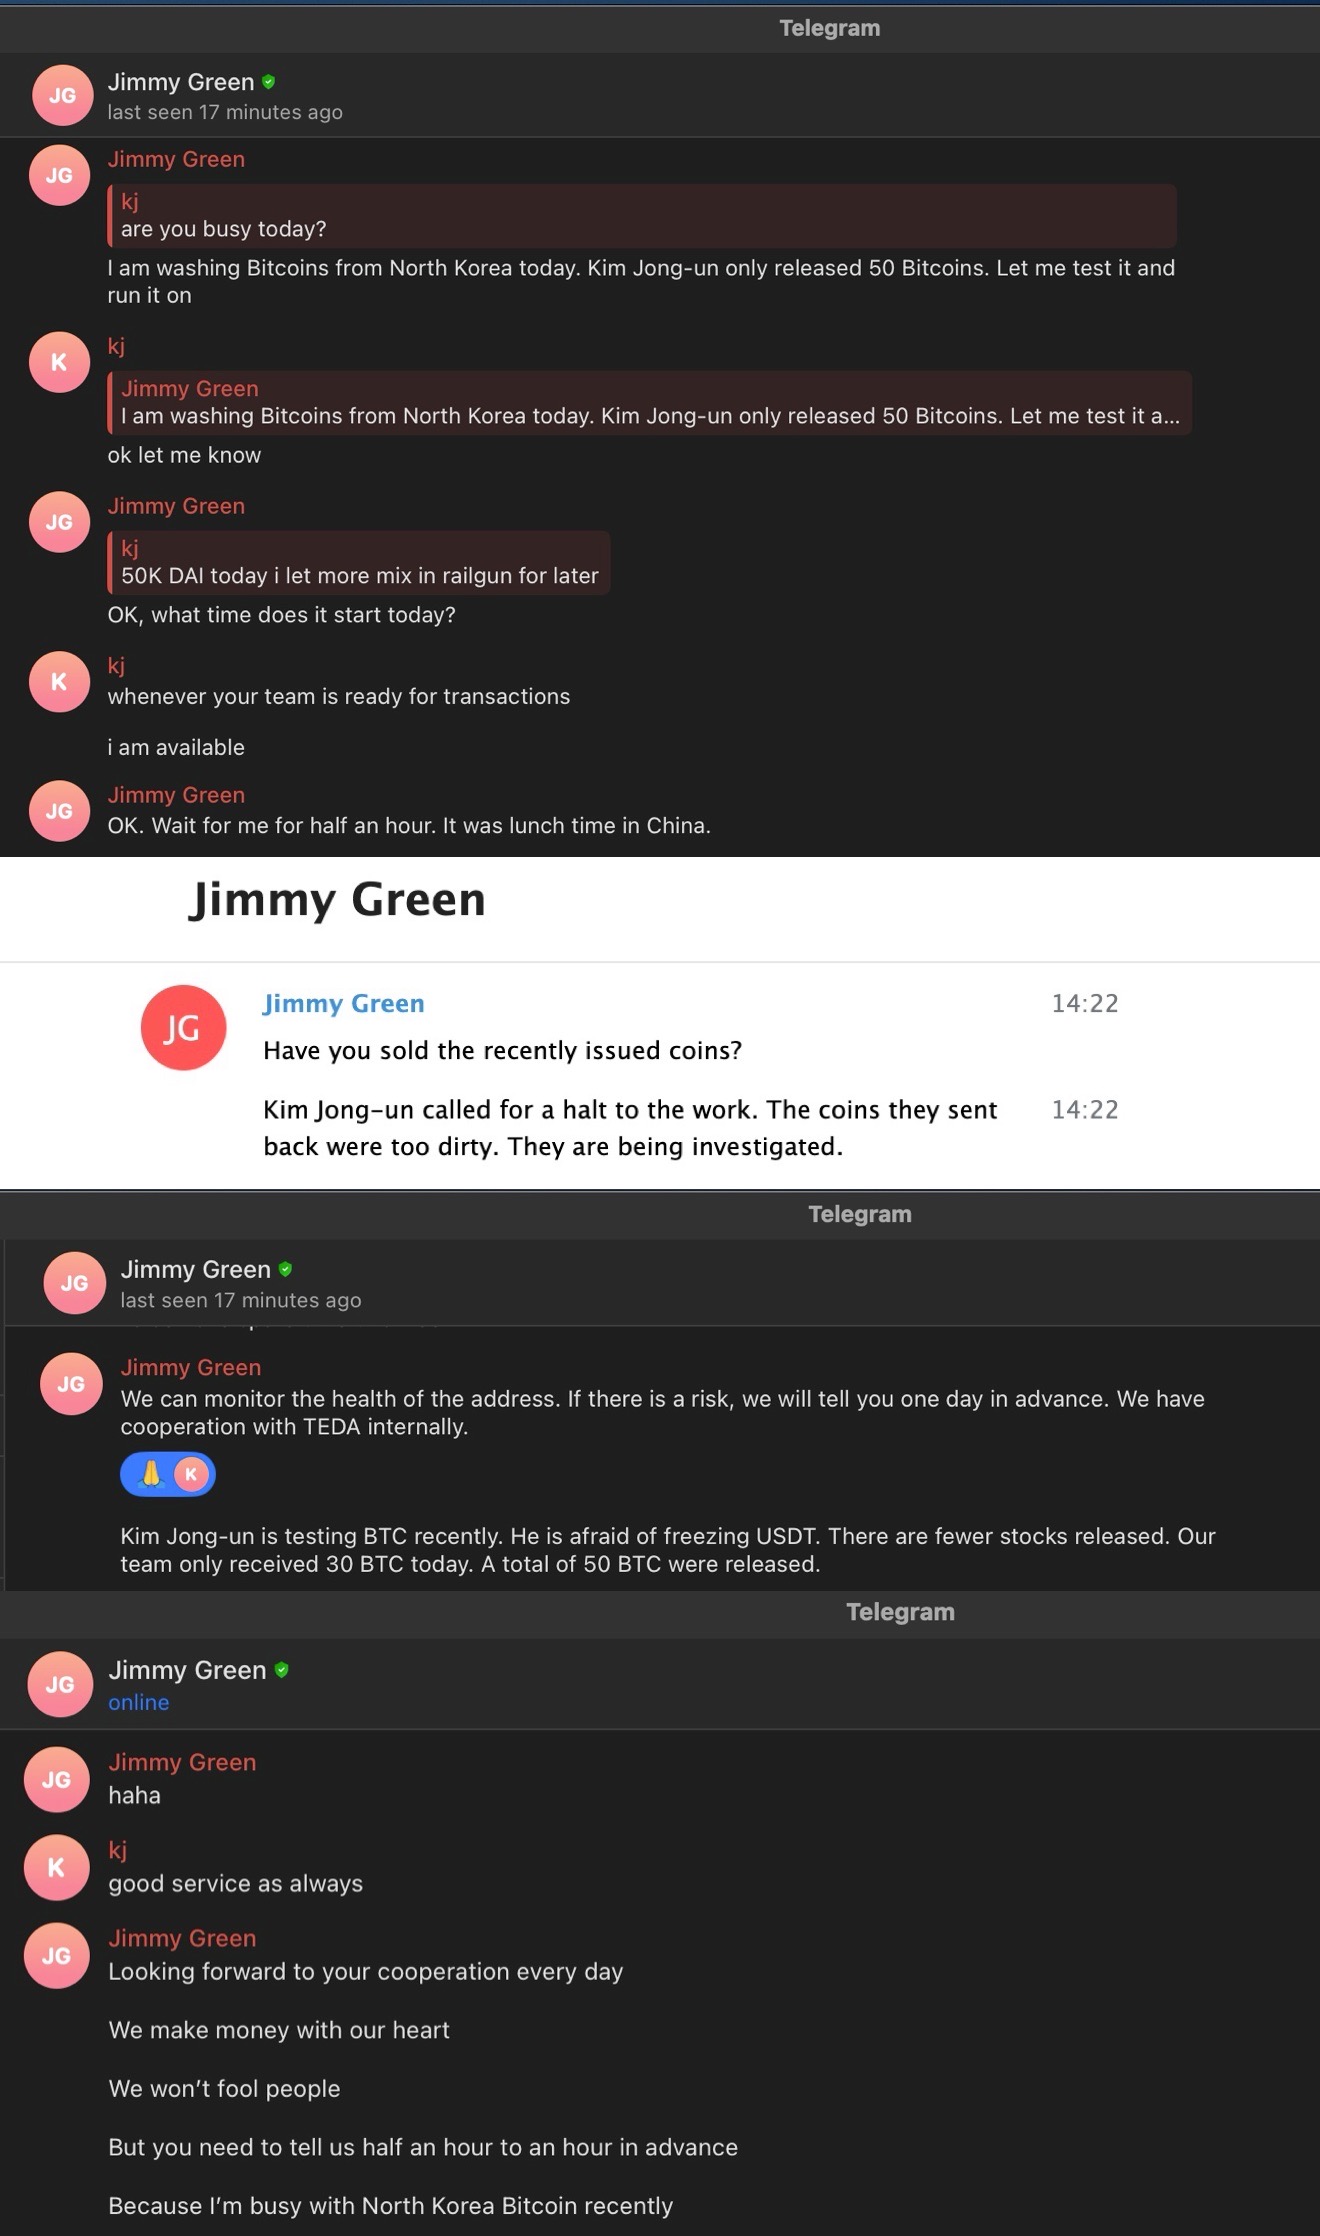
1/ How I infiltrated a Chinese organized crime syndicate that has laundered $1B+ across multiple exploits for Lazarus Group.
Posing as a client, I gathered intel that helped action freezes for the Feb 2025 Bybit exploit and attribute illicit activity onchain.