

Providing businesses with easy-to-update websites that are optimised for their customers’ needs. 🇦🇺🌏 Based in Australia, serving clients around the world.
Adelaide, South Australia
Joined March 2010
- Tweets49.3K
- Following3.3K
- Followers4.1K
- Likes15.6K





Pinned Tweet
🎉 The new Vintuitive website is live!
Fresh look, same mission: beautiful, easy-to-update websites for Adelaide small businesses with hands-on training and care plans so you're never left stranded.
Come take a look 👉 vintuitive.com.au

ALT The front page of the new Vintuitive website. "Your business deserves a website that works as hard as you do".
Vin @ Vintuitive ⚡🌐 retweeted

We have released Zero Breach Toolkit, a free open sourced tool capable of detecting over 12,100 traces of Israeli & other spyware on your devices. It works on Windows, Linux, Mac, Android and Iphones.
You can download it here: github.com/interplains/Zero-…
Inside the folder with the tools run this command: python -X utf8 scan/zero-breach-toolkit.py
It never writes to disk, never connects to the internet, or ask for admin perms. It takes around 10-15 minutes to run depending on the device.
This project is fully open source, so feel free to take the code and use it to create your own tools.
If you find some spyware on your device, consider sending it to us via telegram. Leave us a star on GitHub if the tool helped you.
Follow our backups: @ZionismExposedx
@IsraelExposedAr
God bless
Vin @ Vintuitive ⚡🌐 retweeted

Head to YouTube for my full speech. If you’re a small business with a website, you need to watch this too - youtu.be/mQKbweo4i7k?si=W4z9…

Vin @ Vintuitive ⚡🌐 retweeted

Let me get this straight.
A guy keeps getting weirdly targeted ads on his new Samsung TV.
So he breaks into his own TV to find out why. 1.2M people watch.
42 hours later, OpenAI deactivates his account. Reason: "Cyber Abuse."
His words: "i have never used openai to exploit or find vulnerabilities, only local reverse engineering"
Same week, people on r/claude say Claude now cuts off reverse-engineering write-ups MID-SENTENCE:
"A safety check stopped my response partway through creating the playbook"
The TV is fine.
The guy who opened it is the problem.


“The project is not issuing an emergency fix for it. Instead, it recommends turning off a feature called session upload progress until a fix is available in the next routine release.”

‼️ BREAKING ‼️ PHP warns of another UNPATCHED REC vulnerability just 2 days after releasing emergency patches for critical PHP2Shell flaws.
New "CVE-2026-115560" affects only unusual session configurations. PHP has issued urgent mitigation guidance.
Full details → thehackernews.com/2026/10/ur…

Vin @ Vintuitive ⚡🌐 retweeted

❗ ALERT ❗ We are aware of media reporting about critical vulnerabilities in PHP that may affect all versions from PHP 5 onwards. Organisations and individuals should monitor PHP applications and prepare to update and apply patches. Read the full alert 👉 cyber.gov.au/alert/critical-…

Vin @ Vintuitive ⚡🌐 retweeted

The PHP project has released fixes for 2 critical vulnerabilities affecting servers that host PHP applications. Site owners and technical teams should confirm their hosting provider’s update plan and update PHP immediately. Versions before PHP 8.2 no longer receive security updates. These issues are not specific to WordPress, and no WordPress update is required. wp.me/pZhYe-5Gb

Vin @ Vintuitive ⚡🌐 retweeted

Two critical vulnerabilities have been identified in PHP, a widely used programming language that powers websites and web applications. These vulnerabilities (CVE-2026-109618 and CVE-2026-109619) could allow malicious cyber actors to remotely execute code in PHP core, potentially compromising sensitive data and networks.
The FBI urges organizations to take the following steps now:
➡️ If an immediate update is not feasible it is recommended that organizations take the system offline until it can be fully mitigated.
➡️ Immediately update affected PHP installations following the guidance on php.net. Inventory where PHP runs in your environment, prioritizing internet-facing systems and vendor products that bundle PHP.
➡️ Monitor web servers for suspicious activity, including PHP processes unexpectedly launching command shells or downloading files. Ensure appropriate process-monitoring capabilities are in place to help identify potential exploitation.
➡️ If you find signs of compromise, isolate affected systems, preserve your web server and PHP logs, and report it to your local FBI field office or ic3.gov. Those reports help us identify the actors involved and warn other organizations before they become victims.
For the latest information, follow PHP’s announcement on php.net, CERT-EU Security Advisory 2026-018, and CISA’s Known Exploited Vulnerabilities catalog.

ALT Critical vulnerability alert for PHP Core with CVE-2026-109618 and CVE-2026-109619, CVSS score 9.2, urging immediate patch and threat hunting.
In a support document that it has since deleted, Telstra said RCS support would be available starting with an iOS update coming in December.
iPhone users with Telstra will likely then be able to use RCS in the Messages app starting with iOS 27.3.


Vin @ Vintuitive ⚡🌐 retweeted

"I have nothing to hide" is a great line until you remember you have curtains, a phone PIN, and a lock on the bathroom door. Privacy isn't hiding. It's choosing.
I've been getting super advanced with Siri AI to improve my shopping routine.
🛒 Most recently I photographed dockets from recent shopping trips and asked Siri AI to add them to my Shopping List in Reminders.
✅ Now I just have to uncheck whatever items I need for next week.
Quark is becoming a reality.


New #Robot Satellite Will Grab Space Junk and Burn It Up in Earth's Atmosphere
by @sutoroveli_news
#Robotics #SpaceTech #Innovation #EmergingTech #Tech #Technology
Vin @ Vintuitive ⚡🌐 retweeted

Meta and Apple Bring Muse Spark Open AI Model to Mac Studio macrumors.com/2026/10/15/met…

Anyone else find it incredibly ironic that Siri AI knows very little about Apple products and services?
You'd think that Apple would concentrate first on making Siri AI the most knowledgable expert, an 'Apple Genius' even, on Apple's operating systems, software and hardware. 🧐

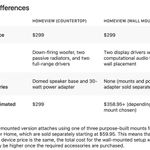
Apple Clock. The ultimate wall clock for your smart home.
The wall-mounted Home View is essentially a large Apple Watch.

ALT The Home View reimagined as an Apple Clock.
Vin @ Vintuitive ⚡🌐 retweeted

The government today will introduce sweeping censorship that @AlboMP & @AnikaWells lie about. Below she claims the government wants to create a bot army of fake accounts for “research” when the bill clearly intends for them to be used in partisan warfare against fooled citizens.

