

Privacy, AI automation & connectivity insights | Mobile proxies, non-VoIP numbers & global eSIMs. Control your digital identity.
Joined November 2025
- Tweets593
- Following30
- Followers2.6K
- Likes807





Pinned Tweet
Your AI agent can now buy its own phone number, eSIM, and mobile proxy. With a spending cap you set.
We upgraded the VoidMob MCP server. 30 tools, open source, and it now plugs straight into the runtimes everyone's building on: Grok Bot, OpenClaw, Hermes, Pi, and Boat, plus Claude Code, Codex, and Cursor.
Here's the problem it solves:
Every cloud agent, Grok Bot, Meta Muse, OpenAI's dots, runs on a locked machine where the vendor owns the IP and the payment rail. The agent has no way to get a real phone number to verify an account, a clean IP for a geo or AI protected task. So it hands the whole thing back to you.
VoidMob fills that gap. The agent draws on one prepaid balance to buy exactly what it's missing:
- Global non-VoIP numbers, one-time or dedicated, that pass verification where VoIP gets rejected
- Mobile proxies on real carrier IPs, by country and carrier
- eSIM data plans across 180+ destinations
Every purchase runs the same way: the agent quotes the price, waits for your yes, then buys with your approved price as the ceiling. Set a per-order cap and a session budget and nothing goes over it. Give each agent its own key and kill it whenever you want.
No KYC, instant access. Sandbox mode to test every tool on play money first.
One command: npx -y @voidmob/mcp
Setup guides for every runtime:
voidmob.com/mcp
voidmob.com/integrations

GrapheneOS on a Pixel 10 Pro XL is the right call. The OS is layer one. Here’s the rest.
Install GrapheneOS, relock the bootloader, keep the Owner profile with zero Google. Anything that needs Play goes in a second profile.
What iOS can’t do:
- Network permission per app. No internet unless the app needs it.
- Separate profiles. Work, personal, burner, each with its own apps and data.
- Auto reboot after 18 hours locked. Data back at rest.
- Vanadium built in. Brave for the second profile. Mullvad VPN for browsing.
Where most setups still leak:
- Private eSIM with calls and SMS instead of your carrier SIM. No contract ties the device to you. Pick the IP exit before you pay, so you know what every app sees.
- Real mobile IP (eSIM) for registrations. Platforms trust a carrier IP, not a VPN range.
- Non-VoIP number for signups, messaging and every app that asks for a code. Your real line stays off every form.
Most privacy setups break platform trust. Flagged logins, locked accounts, endless verification. This one doesn’t. Private software on trusted infrastructure.
Wallets:
DarkSword was iOS: one Safari visit, kernel takeover, wallet drain. GrapheneOS hardens the browser and kernel against that class, but the rule holds on any phone. Seed phrases never touch a browser, a screenshot or a synced note. Wallets get their own profile, network off for everything else in it.


AI scraping agents run 10x slower than a script and fail 90% of CAPTCHAs.
Latest tests:
- Same Google Flights search, timed: a scraper finished in 8.2 seconds. Codex, Claude and Antigravity took 29 seconds to 11 minutes.
- October bot detection benchmark: reCAPTCHA v3 flagged 95% of Browser Use sessions, 100% of Perplexity Comet, 72% of Grok.
- On complex logins, agents pass 12% to 70% depending on the agent.
Scripts can't do logins at all. That's the trade.
Script: known URLs, high volume, fixed layout. A model writes it once, then it runs with no model in the loop.
Agent: unknown sites, logins, forms, layouts that change. It finds the data with no selectors written.
So what's the best setup?
Agent handles discovery and login, hands the URLs to a script for bulk extraction.
Where agents break is the network, not the model.
A script gets blocked, retries one URL. An agent runs one long session: search, log in, click, extract. One block halfway and the whole run restarts, tokens gone.
The agent block starts with the IP. Datacenter ASN gets a challenge, challenge becomes a CAPTCHA, agent fails it 9 times out of 10.
The fix: A carrier IP sits behind CGNAT, shared with thousands of real phones. Sites can’t block it without blocking their own users. Use sticky IP and the challenge never shows.
DataDome logged 17.7 billion agent requests last quarter. Agent traffic is its own class now.
But with the stack available today, how do you still not bypass it?
Meta’s Muse, xAI’s Grok Bot and Spear Street’s Instinct can all shop, book and sign up for you.
They also all get caught.
Fingerprint announced yesterday it can now spot all three, even though they stopped identifying themselves. Grok Bot quit signing its requests in October. Muse hides its automation flags. Instinct logs in with your own password and asks for your SMS codes.
The biggest AI labs went stealth. Still flagged.
Because the agent isn’t the problem. The connection is. A datacenter IP, a browser fingerprint that doesn’t match a real device, hundreds of requests an hour from one account. That’s what gets caught.
The agent setup that doesn’t get flagged:
- Carrier IP, not a cloud server. Looks like a phone on 5G because it is one
- One IP per session, held from login to logout. Instinct got a user’s Resy account deactivated by hammering it
- A real non-VoIP number the agent owns for its codes, not your personal line
- A spend cap, so an agent that buys its own IP and number can’t loop your balance to zero
Our MCP server gives any agent all four. Test it with $500 play money, no key: npx -y @voidmob/mcp with VOIDMOB_SANDBOX=1
voidmob.com/integrations

You can’t freeze $XMR, $BTC or any other native coin. That’s the fundamental concept of crypto.
And this is only the beginning. More hacks, more breaches, more stolen data.
Keep as little personal data as possible on exchanges, or anywhere you sign up, before your details show up in the next leaked database.

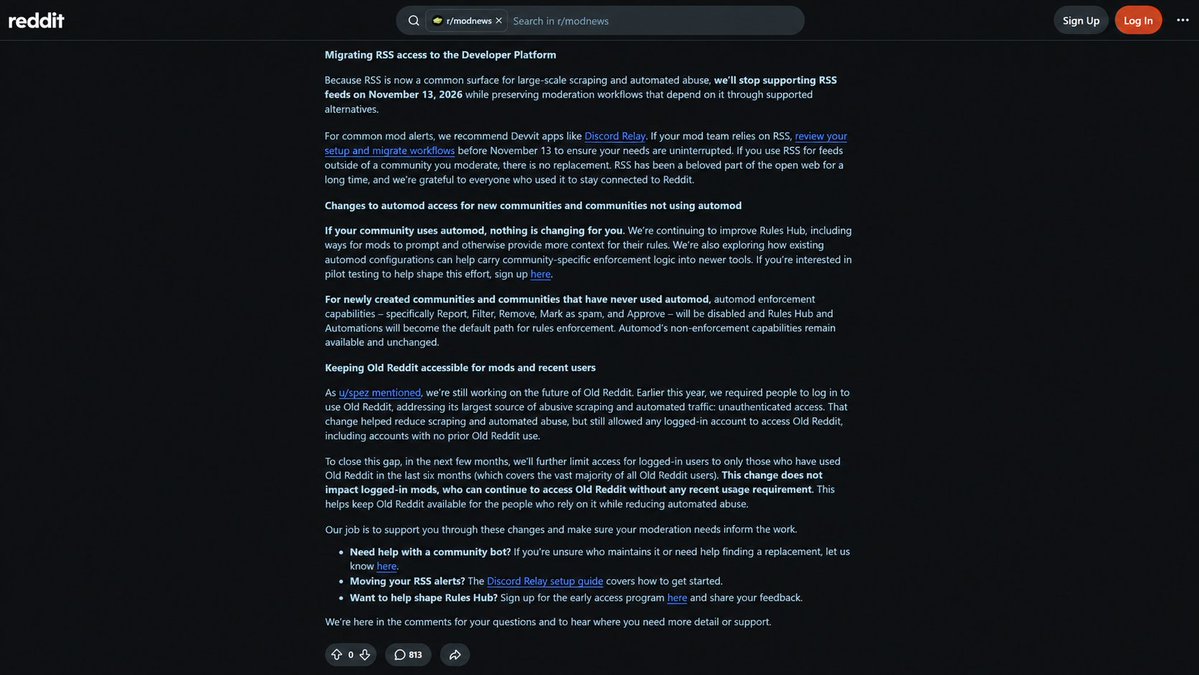
Reddit just killed the public API.
New access requests stop tomorrow, Oct 31. RSS feeds die Nov 13. Everything left shuts by March 2027.
What it means:
- Your Reddit monitoring tool, alert bot or “find leads in subreddits” script stops working unless Reddit approves it
- Every Reddit scraper on GitHub that used the public API or RSS is now dead code
- Parasite SEO on Reddit gets harder, because the logged-out access you used to find threads and track rankings is what Reddit says it’s cutting first
- The data isn’t gone. Reddit sells it to Google and OpenAI. It’s just not free for you anymore
What still works:
1. Use a real account. Logged-in Reddit still serves the same JSON the app uses. Reddit said logged-out traffic was the abuse it’s targeting, so logged-in is the path that survives.
2. One account per IP. Reddit links accounts by IP and device, not by username. Two accounts on one home connection and they both go when one goes.
3. Use a mobile IP, not a datacenter or cheap residential one. Reddit flags hosting ASNs on sight. A carrier IP looks like a phone on 5G because it is one.
4. Warm the account. Post, comment, vote like a person for two weeks before you automate anything. Low Contributor Quality Score gets your posts hidden before anyone sees them.
5. Slow down. A few hundred requests an hour with random gaps, not thousands a minute.
6. Verify with a real carrier number. Reddit rejects VoIP numbers (Google Voice, TextNow) on new accounts.
Reddit made the API a product. Your scraper needs to look like a customer now.
Full guide with working Python: voidmob.com/blog/how-to-scra…
Source: reddit.com/r/modnews
The scary part is you can do everything right and still get burned by a package you trusted.
But most of these leaks spill the same things: your IP, your email, your phone number. That part you control.
- Private eSIM so your real home IP never touches the services you log into.
- Non-VoIP number so your personal line isn’t sitting in the next breach.
- Encrypted mobile proxy so your PC traffic exits on a carrier IP, not your home connection.
Keep your real identity out of the stack, and a breach leaks a shell, not you.

October has been an absolute nightmare for software
> Railway - customer secrets exposure
> LiteLLM - malicious PyPI + Docker releases
> Zeabur - infrastructure breached
> OpenCode - AI API keys exposed
> OVHcloud CLI - official binaries backdoored
> Rank Math PRO - malware in official plugin
> TeamUpdraft - customer data compromised
> ConnectWise - cloud backup identities compromised
> Tensorlake - npm package infected
> SubQuery - backdoored npm package
> GhostAction - GitHub repos with malicious workflows
> PHP - critical RCE vulnerabilities
> Node.js - security vulnerabilities patched
> eMudhra - certificate authority keys compromised
> Tailscale - eMudhra incident
At this point, the biggest security risk might not be the code we write, but the code we trust...
New non-VoIP numbers just dropped. Whether it’s for automation or personal use, you get a real local line that actually works.
Two new countries added:
- Indonesia non-VoIP numbers at $21.99/mo (+62)
- Italy non-VoIP numbers at $29.99/mo (+39)
Monthly, all services supported, real carrier lines not VoIP.
More integrations are on the way.
Get 10% off your first deposit.
voidmob.com/sms

VoidMob (Private Connectivity) retweeted

Hace poco estuve probando un servicio que se llama VoidMob desde Latinoamérica y me sorprendió todo lo que se puede hacer desde una misma app.
Para probarlo en serio contraté una eSIM desde Colombia con salida a internet por Estados Unidos. La activé (es realmente muy fácil hacerlo: escaneás el QR que te dan, aceptás la configuración y listo), revisé la IP y efectivamente estaba saliendo por EE. UU. Algo que me gustó es que antes de comprar podés ver el país de routing y en algunos casos elegirlo.
También probé uno de sus números de teléfono de Estados Unidos. Lo pude configurar con una cuenta de WhatsApp y recibir el código de verificación sin problemas. También me envié SMS desde un teléfono que tengo en USA y llegan perfectamente. Para alguien que está en Latam y necesita tener un número de otro país, esto puede ser sumamente útil.
Además de eso, VoidMob tiene eSIMs para más de 180 países, números de distintos países y proxies móviles 4G/5G. También tienen servicios disponibles en varios países de Latinoamérica (Argentina, Colombia, México, Chile, Brasil, Ecuador, Costa Rica, Uruguay, Paraguay, Perú y otros), así que no es algo pensado únicamente para gente que está viajando por Europa o EE. UU.
Los precios me parecieron bastante razonables. Las eSIM arrancan desde US$2,99, los números dedicados de EE. UU. cuestan US$19,99 al mes y hay proxies móviles compartidos desde US$3,99 por GB. También tienen proxies móviles dedicados con datos ilimitados, aunque ahí el precio depende del país y del tipo de conexión.
Otra cosa que me gustó es que todo funciona con un mismo balance. Cargás saldo y lo vas usando para los distintos servicios. Además, podés pagar con criptomonedas sin KYC.
Incluso tienen un MCP para conectar VoidMob con agentes de IA y que puedan interactuar directamente con el servicio. Todavía no le encontré un uso cotidiano para mí, pero la idea está bastante buena. Será cuestión de probarlo más adelante.
Lo estoy probando ahora desde Colombia y por el momento la experiencia fue muy buena. Sobre todo me parece interesante para quienes estamos en Latinoamérica, ya sea viviendo acá o temporalmente, y necesitamos acceder a servicios, números o conexiones de otros países sin tener que estar físicamente ahí.
Si quieren probarlo, se los recomiendo 100%.
voidmob.com/


The hackiest CAPTCHA setup we've seen in 2026 is a solver + a mobile proxy.
The part nobody posts:
The best way to beat a CAPTCHA is to never trigger it.
This is killing AI agents right now. An agent runs into a Cloudflare block page, doesn't realize it's blocked, and keeps trying to read data that isn't there. The loop burns the whole token budget for nothing.
Scrapers deal with the same thing. Perfect code, then one challenge or rate-limit page and the whole workflow stops.
Here's what people miss. CAPTCHA solvers charge you per solve, $0.60 to $3 per 1000. Most setups pay on nearly every request because their IP looks suspicious before any puzzle even loads.
reCAPTCHA v3 scores every request silently. Turnstile decides the check based on how risky your connection looks. A VPS, VPN IP or your home IP is exactly what those scores flag.
Every CAPTCHA that never appears is a solve you never paid for, and a loop your agent never gets stuck in.
The full setup:
- Mobile proxy (VoidMob), carrier IP for the session so risk checks stay quiet
- A solver (CapSolver, CapMonster, 2Captcha) for the few that still appear
- Route the solver through your proxy, so the challenge gets solved from the same IP you browse from. If the solve and the submit come from different IPs, the site rejects the token.
Solver + mobile proxy is the current captcha bypass meta. One keeps the challenge from showing up, the other solves the few that still do. Most people only buy half.

You can't leak what was never yours to begin with.
You don't need an ISP. You don't need a carrier number. You don't even need your own IP.
That's VoidMob. Privacy with no questions asked.
Your Meta agency accounts didn't get nuked for breaking rules. They got nuked for something you didn't know you were doing.
Everyone blaming the ban wave on "policy violations" is wrong.
Meta openly allows multiple ad accounts, but it tracks patterns and link your accounts.
Meta builds a graph on every advertiser. Your IP, your browser fingerprint, your device, your payment card, your login, each one is a node. The second two "unrelated" accounts share enough nodes, Meta stops seeing an agency with 12 clients and starts seeing one operator running 12 accounts.
The agencies that survived weren't luckier. They were isolated. Nothing shared between accounts, so nothing to link, nothing to cascade.
Here's the exact separation, one per portfolio:
- Dedicated mobile carrier IP. Not office WiFi. Not a datacenter proxy. Not one proxy split across three accounts. One clean IP per portfolio.
- Antidetect browser profile with its own fingerprint. Same browser across two accounts links them. Incognito changes nothing.
- Unique payment card per portfolio. A shared card is one of the strongest links Meta reads.
- Non-VoIP number per account. Meta auto-rejects VoIP. Real carrier lines pass.
- Partner access, never one profile admin-ing everything. Never cross-login.
And before you buy your way out: rented agency accounts don't save you. They come pre-verified with higher trust, then die in the same wave the moment you run them on shared IPs and cards.
The problem was always infrastructure and wrong patterns.
VoidMob covers the two layers that you can actually trust in 2026.

September 2026 has been one long data breach and it's not even over yet.
Revolut handed over passport copies, verification selfies, and full transaction histories to an attacker using a spoofed government email domain.
220 million airline passenger records exposed: names, passport numbers, dates of birth, nationalities. Left open with default credentials.
820 million Alipay users leaked, including phone numbers.
IDScan breached: government ID information, potentially exposed.
Suno: 55 million email addresses and phone numbers.
Notice the pattern. Every breach leaks the same things: your real name, your real number, your real ID, your real email.
The only data that can't leak is the data that was never tied to you.
How to shrink your exposure before the next one:
Register accounts with a VoidMob non-VoIP number, not your personal phone. When that platform gets breached, the leaked number or email tied to it leads nowhere.
Use a fresh email per service, not your main inbox linked to everything.
Route through a VoidMob eSIM and encrypted proxy so your ISP isn't logging and selling your traffic on top of it.
Never hand a platform your passport or biometric selfie unless it's legally unavoidable. IDScan and Revolut just showed where that ends up.
You can't stop companies from getting breached. You can stop your real identity from being in the file when they do.
- VoidMob
VoidMob eSIMs just expanded beyond data.
EU and UK eSIMs now include SMS and calls, not just data. A real number attached to your eSIM for verification and voice, without a carrier account tied to your identity.
Find them under the Network filter, set to "With phone number." Alongside IP Routing, Country, Duration, and Data filters so you configure exactly the profile you need.
Other regions: global eSIMs are on the way. A totally new product. Unlimited global data, calls, and SMS with privacy features no other eSIM offers.
Get yours now. Stay tuned for the updates.
dashboard.voidmob.com/esims

If your SaaS or AI agency doesn't have an automated B2B lead pipeline, you are leaving revenue on the table.
Cold emailing dead lists doesn't work anymore. Local businesses are a goldmine for custom tech, and they sit right in front of your eyes on Google Maps.
The standard lead-gen playbook is broken and outdated. You need high-quality infrastructure that connects directly to your AI agents.
Here is how to build an automated, unblockable scraping pipeline:
Target your niche: Pick your desired location and target business category (e.g., HVAC in Austin or dentist clinics in Miami).
Connect your AI agent via MCP: Hook Cursor, Claude, or your custom agent directly into the VoidMob MCP server.
Bypass scraping limits: Your agent pulls real-time local business data through high-trust 4G/5G mobile carrier IPs - eliminating rate limits, CAPTCHAs, and anti-bot blocks.
Don't waste your time manually compiling business data or fixing broken proxy setups. Your AI agent can handle the entire pipeline end-to-end.
Start VoidMob MCP
github.com/voidmobcom/voidmo…

monero:native is one the most bullish assets of the decade.
Cash is dying. Governments are pushing digital IDs and CBDCs that log every transaction you make.
BTC and ETH won't save you, every transaction sits publicly forever. AI algos now scan transparent chains in milliseconds. Pseudonymous is not private.
Monero is the only one left that's totally anonymous.
And it just got stronger. The FCMP++ upgrade replaced ring signatures with full-chain membership proofs, expanding the anonymity set to 150M+ outputs. Correlation attacks are now mathematically impractical.
XMR is up 120% over 12 months on pure privacy demand.
Think about it.