

Malware reverse engineer, Cryptolaemus member Mastodon: @FirehaK@infosec.exchange
Joined May 2012
- Tweets659
- Following389
- Followers304
- Likes2.1K





Pinned Tweet
I finally did a thing and put some #YARA rules in a public GitHub repository now that some of the ransomware I looked at is no longer relevant. Hope to do more and add an eventual analysis repo one day as well. Check it out!
github.com/FirehaK/YARA

Stephan (@[email protected]) retweeted
We've preserved (yet another) lot of eleven test cartridges for the Nintendo DS, DSi, and 3DS! Included are some never-before-seen pieces of test software, as well as new versions of previously discovered ones! Thanks to those who contributed: March42, Kc57, Haifisch, and XX_75.


Stephan (@[email protected]) retweeted

Check out my latest blog post about Cova loader and Nosu stealer. These two went unnoticed... but only until now :) bitsight.com/blog/cova-and-n…

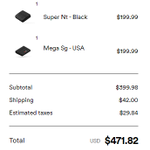
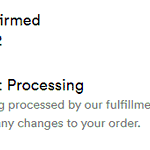
Wish I knew why my @analogue pocket order has been "processing" at the fullment partner for more than a month now while others who have ordered at the exact same time have gotten theirs a while ago now 😔
Stephan (@[email protected]) retweeted

Everyone: Signs in every day to watch Elon slowly running Twitter into the ground.
Elon:

Stephan (@[email protected]) retweeted

Bankrupting Twitter is not an eligible run submission for the second submission period.
Stephan (@[email protected]) retweeted

I've joined the cool kids club @[email protected]
Leave your handle below 👇
#mastodonmigration #Mastodon
Stephan (@[email protected]) retweeted
We are also hunting mealybugs(emotet) and other crimeware actors on Mastodon. Come say hello and give us more things to eat. infosec.exchange/@cryptolaem…

Stephan (@[email protected]) retweeted

Main concern w/ the new Twitter Blue offering is the verified logo has been a marker of trust I.e., “we’ve confirmed the person is who they say they are.” Now it’s “we’re taking their $ & their word for it.” On the cusp of election where source of info is critical, a major risk.

To think that simple payment verifying will pose any sort of meaningful barrier to sophisticated actors on the platform is just not anchored in reality. Agree w/ @ianbremmer
Stephan (@[email protected]) retweeted
To think that simple payment verifying will pose any sort of meaningful barrier to sophisticated actors on the platform is just not anchored in reality. Agree w/ @ianbremmer


Stephan (@[email protected]) retweeted
You can self-host a Mastodon server
Thanks Pokémon Red and @_Kc57 😉

Stephan (@[email protected]) retweeted
Reminder: We are constantly pushing new C2s/Distro URLs/Payload URL/samples to the abuse.ch ecosystem. Please see our submissions at
bazaar.abuse.ch/
feodotracker.abuse.ch/
threatfox.abuse.ch/
urlhaus.abuse.ch/
for more details and info.
Stephan (@[email protected]) retweeted
We have been busy and improved MalwareBazaar's archive parsing 🆕⬇️
The password of PW protected archives is now guessed from the tag list provided 🔐 E.g.:
👉 bazaar.abuse.ch/sample/ddfde…
We have also implemented a feature to de-pump pumped files 📄 E.g.:
👉 bazaar.abuse.ch/sample/0819f…

ALT MalwareBazaar's password guessing for PW protected archives in action

ALT MalwareBazaar's de-pumping functionality in action, de-pumping unnecessary large files
Stephan (@[email protected]) retweeted

Okay, so a few people have asked how you spot the where your Trust Thermocline is, and how to avoid hitting it. I'll give you the same answer I give senior execs:
I don't know.
But the people working on the ground level in the customer-facing sections of your company do. /1

Stephan (@[email protected]) retweeted
One of the things I occasionally get paid to do by companies/execs is to tell them why everything seemed to SUDDENLY go wrong, and subs/readers dropped like a stone.
So, with everything going on at Twitter rn, time for a thread about the Trust Thermocline /1
Stephan (@[email protected]) retweeted

I know what I'm doing, but I also have no idea what I'm doing.
Stephan (@[email protected]) retweeted

Rest in peace, Vitali. Our thoughts and prayers are with your family and friends.
Thanks for all you did for the cybersecurity community.