






Offer stablecoin balances and payments inside the app you already have.
One integration: sign in with Face ID, and you never hold your customers' keys. They hold them through a passkey that cannot leave their devices.
jaw.id/?utm_source=twitter&u…


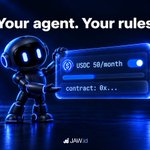
One-off payments are the easy part. Recurring and usage-based charges are where onchain gets pretty awkward.
We fixed this with session keys: the user grants a scoped allowance with an expiry once, and your app charges against it without asking again.
We made zero sacrifices on self-custody, and there would be no centralized servers in your users’ way.
docs.jaw.id

With JAW, your money goes to an @ensdomains name, not a 42-character address.
That removes the step people most often get wrong on a cross-border transfer, and the recipient signs up with Face ID instead of having to install a wallet before they can be paid.
jaw.id/?utm_source=twitter&u… 🤝

Tokenized exposure to Vale has arrived on Base.
Familiar assets are finding their way into onchain markets, bringing new audiences closer to digital accounts.
Making those accounts easy to use and control is part of the work ahead.


JAW.id retweeted
Wallets for Agents:
→ @_JAW_id
→ @privy
→ @get_para
→ @BlockradarHQ
→ @openfort_hq
→ @Alchemy
→ @thirdweb
→ @reown_
→ @dynamic_xyz
→ @safe
→ @MetaMask
→ @zerion
→ @AltanaNetwork


The transfer does not stall on the sending side. It stalls when the recipient has to go install a wallet first to own the keys.
A passkey account created inside your app removes that wait: they receive, then they set up nothing. That’s why we do it at JAW.
Get started now: docs.jaw.id

Money goes to a name, not a 42-character address.
That removes the step people most often get wrong on a cross-border transfer. Plus, the recipient signs up with Face ID instead of installing a wallet before they can be paid.
Built on @ensdomains protocol.
Get started now jaw.id/?utm_source=twitter&u…
JAW.id retweeted

hey, JAW handles the permissions on the level of the smart account, by default the user grants a permission the spend that involves spender account, scope (contract address, function selectors), expiry, tokens that can be spent (with allowance amount ofc)… and we have something special we’re calling “call checkers” which allow you to also add specific constraints on the params of any function you added in the scope, which would allow you to solve for the “pay the wrong merchant”
