

Securing the future of crypto | Cover art by @yueko__ | Emergencies: https://xitter.cf/t.co/DAAyAETsY4
Joined February 2024
- Tweets730
- Following104
- Followers21.4K
- Likes848



Pinned Tweet
SEAL exists because security experts chose to share knowledge instead of hoarding it.
Your donation keeps that infrastructure running: securityalliance.org/donate

🚨 PSA: threat actors are approaching crypto projects on Telegram, posing as white-hat researchers, offering an “exploit PoC” for your own infra. The PoC contains malware. Our detailed write-up is linked below.
It’s a complete, runnable Solana exploit kit (fork harness, fixtures, the real program binary) so it looks legit. But poc.mjs reads a byte array from a JSON field called UnifiedSignatureInfo, decodes it to a URL, and runs curl -fsSL -k "" | sh.
The decimal array is plain ASCII posing as a Solana signature. Following the README (npm install, start fork, node poc.mjs) is what detonates it.
IOC: hxxps://162[.]35[.]174[.]231:5000/stage2.
Treat any unsolicited PoC as hostile, review statically in an isolated VM, and never run the setup steps on a box you care about. Report any suspicious reachouts to SEAL.
radar.securityalliance.org/a…

Many thanks to @Lavaragexyz for tipping us off on that attack vector! Security aware community is the first line of defense against malicious actors.

SINT-69, an uncategorized intrusion set, keeps minting fake Zoom/Teams domains:
03nweb[.]us
04webz[.]us
05webz[.]us
web05z[.]us
lives[.]eu[.]com
teamlives[.]business
teamslive[.]uk[.]com
u06web[.]us
web06z[.]us
zoomwweb[.]us
Unclassified fake meeting pages:
meets-calls[.]com
msmeet[.]sbs
us89webzoom[.]us
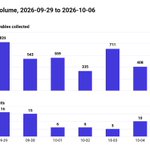
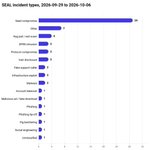
@SEAL_911 is free to anyone who needs it, and stays that way because people fund it.
If this week's numbers are useful to you, fund next week's: securityalliance.org/donate
If you require a direct and more detailed data feed from SEAL Intel contact us on our website (link in bio).

📣 A new patch of updates have landed across SEAL Frameworks!
All of these are community contributions because that's what keeps the Frameworks current and worth using.
Want to contribute? h/u @mattaereal
frameworks.securityalliance.…
Check out all the updates in the thread below.

2) Our Incident Management Framework has a new runbook for a compromised contributor laptop, written from the responder’s side: contain the device, scope what it reached, revoke access in order, and rebuild. The new runbook also connects our malware and DPRK playbooks to the org-side response process.
@S1ns3nz0S71060 contributed this update too with a solid Steward review from @hexnickk4997. 🙏
frameworks.securityalliance.…
3) Our Wallet Security Framework now includes a Security Best Practices section for beginners and small balances, covering auto-lock timers, a dedicated browser profile with sync turned off, and malware protection.
Thanks @0xusmanf for these additions & @pinalikefruit for the Steward review!
frameworks.securityalliance.…
Security Alliance retweeted

It's an honor to help support @_SEAL_Org's mission and bring trusted threatintel feeds to a wider community.

🔬 Introducing SEAL Labs, where we’re partnering with outside experts on time-boxed experiments, starting with a six-month collaboration with @blockthreat to expand SEAL Intel’s incident coverage across the ecosystem.
radar.securityalliance.org/i…

Security Alliance retweeted

It's been an incredible journey, but I've made the difficult decision to step back from day-to-day operations at @_SEAL_Org. I'll be transitioning onto the Board while @sbatt55 transitions from COO to Interim CEO
🔬 Introducing SEAL Labs, where we’re partnering with outside experts on time-boxed experiments, starting with a six-month collaboration with @blockthreat to expand SEAL Intel’s incident coverage across the ecosystem.
radar.securityalliance.org/i…
Security Alliance retweeted
Great reporting by @KimZetter on hardware implants in Ledger wallets stealing crypto recovery seeds via cellular connections.
Buying from an authorized reseller may not be enough.
Question for hardware security researchers: Could we develop an inexpensive SDR-based test to detect these implants by monitoring for unexpected LTE transmissions during wallet initialization, without opening the device?
zetter-zeroday.com/who-is-pl…


SINT-69, an uncategorized intrusion set, remains active after an infrastructure migration. New fake Zoom/Teams domains:
02webz[.]us
02zweb[.]us
05zweb[.]us
06webz[.]us
06zweb[.]us
micvosoft[.]com
teamlives[.]app
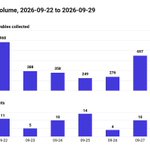
@SEAL_911 is free to anyone who needs it, and stays that way because people fund it.
If this week's numbers are useful to you, fund next week's: securityalliance.org/donate
If you require a direct and more detailed data feed from SEAL Intel contact us on our website (link in bio).