

@immunefi Elite All Star | Currently, an alter-ego of @ControlZ_1337 (previous member @pwnmansh1p) | https://xitter.cf/t.co/lcba8yYqqY
Joined February 2023
- Tweets173
- Following128
- Followers2K
- Likes591






Blockian retweeted

And here I am, having reported vulnerabilities throughout my career that could have resulted in a total of several billions (yes, with a B, > $2B) being *stolen*, while my total earnings are around $2M.
So what's the lesson the industry is teaching researchers?
That next time we should steal the funds first, then negotiate a "responsible disclosure," return 80–90%, and walk away with 10–20%?
Obviously, no. But it's insane that the incentives can make that rhetorical question even possible.
The bounty world is broken.
Blackhats exploit a protocol and get treated like kings in negotiations. Meanwhile, whitehats disclose the exact same kind of vulnerability privately, prevent any damage from happening, and then spend months arguing with projects that try to downgrade the finding and pay the bare minimum.
I'm fighting several cases like this right now. Millions of dollars protected, vulnerabilities responsibly disclosed, and yet projects still don't want to pay the amounts they themselves advertised.
We should be making responsible disclosure the overwhelmingly obvious choice.
Instead, the current state of Web3 is doing its absolute best to discourage whitehats while creating increasingly attractive incentives for blackhats and "grayhats".
Those incentives are backwards, and eventually the ecosystem pays the price.


Blockian retweeted
I read KiiChain’s postmortem and realized something pretty crazy. About 3 weeks ago, we privately reported a critical exploit chain to another Cosmos-based project that reached the same unsafe StateDB subtraction through a completely different path. Thankfully, they confirmed and fixed it really quickly.
These weren’t the exact exploit chain, but they shared the same unsafe StateDB balance primitive: a native balance subtraction that could wrap around in `uint256`. Letting it underflow is an important primitive, but the subtraction alone isn’t enough to steal anything.
Normally, the EVM checks that an account has enough balance before subtracting. To exploit this, you still need another state or accounting bug that breaks that assumption, and then a way to turn the broken balance into real money.
So this does NOT mean every Cosmos EVM chain was exploitable. It depends on the implementation and how each chain keeps its Cosmos and EVM balances in sync.
Sadly, we made a mistake: we didn’t go looking through every other chain that might have had the same primitive.
I tried to understand why, and I think there are 2 main reasons:
1. We focus our research on targets that have bug bounty programs. We didn’t even know some of these other chains existed, and we weren’t aware of a bounty program for projects like KiiChain. Blackhats don’t have that restriction.
2. The underflow primitive on its own isn’t enough to steal funds. An affected project would also need a separate bug that makes the underflow reachable and exploitable. This made us wrongly assume the issue was specific to the project we were reviewing.
I’m genuinely sad that we didn’t connect the dots before real users got hurt.
But on the bright side, our report helped protect literally tens of millions of dollars (no exaggeration) on the chain we reviewed (though we haven't gotten paid for this one yet).
I think this incident shows why bug bounty programs and responsible disclosure matter. It also shows why security updates need to be coordinated between upstream maintainers and the downstream projects using their code.


Blockian retweeted

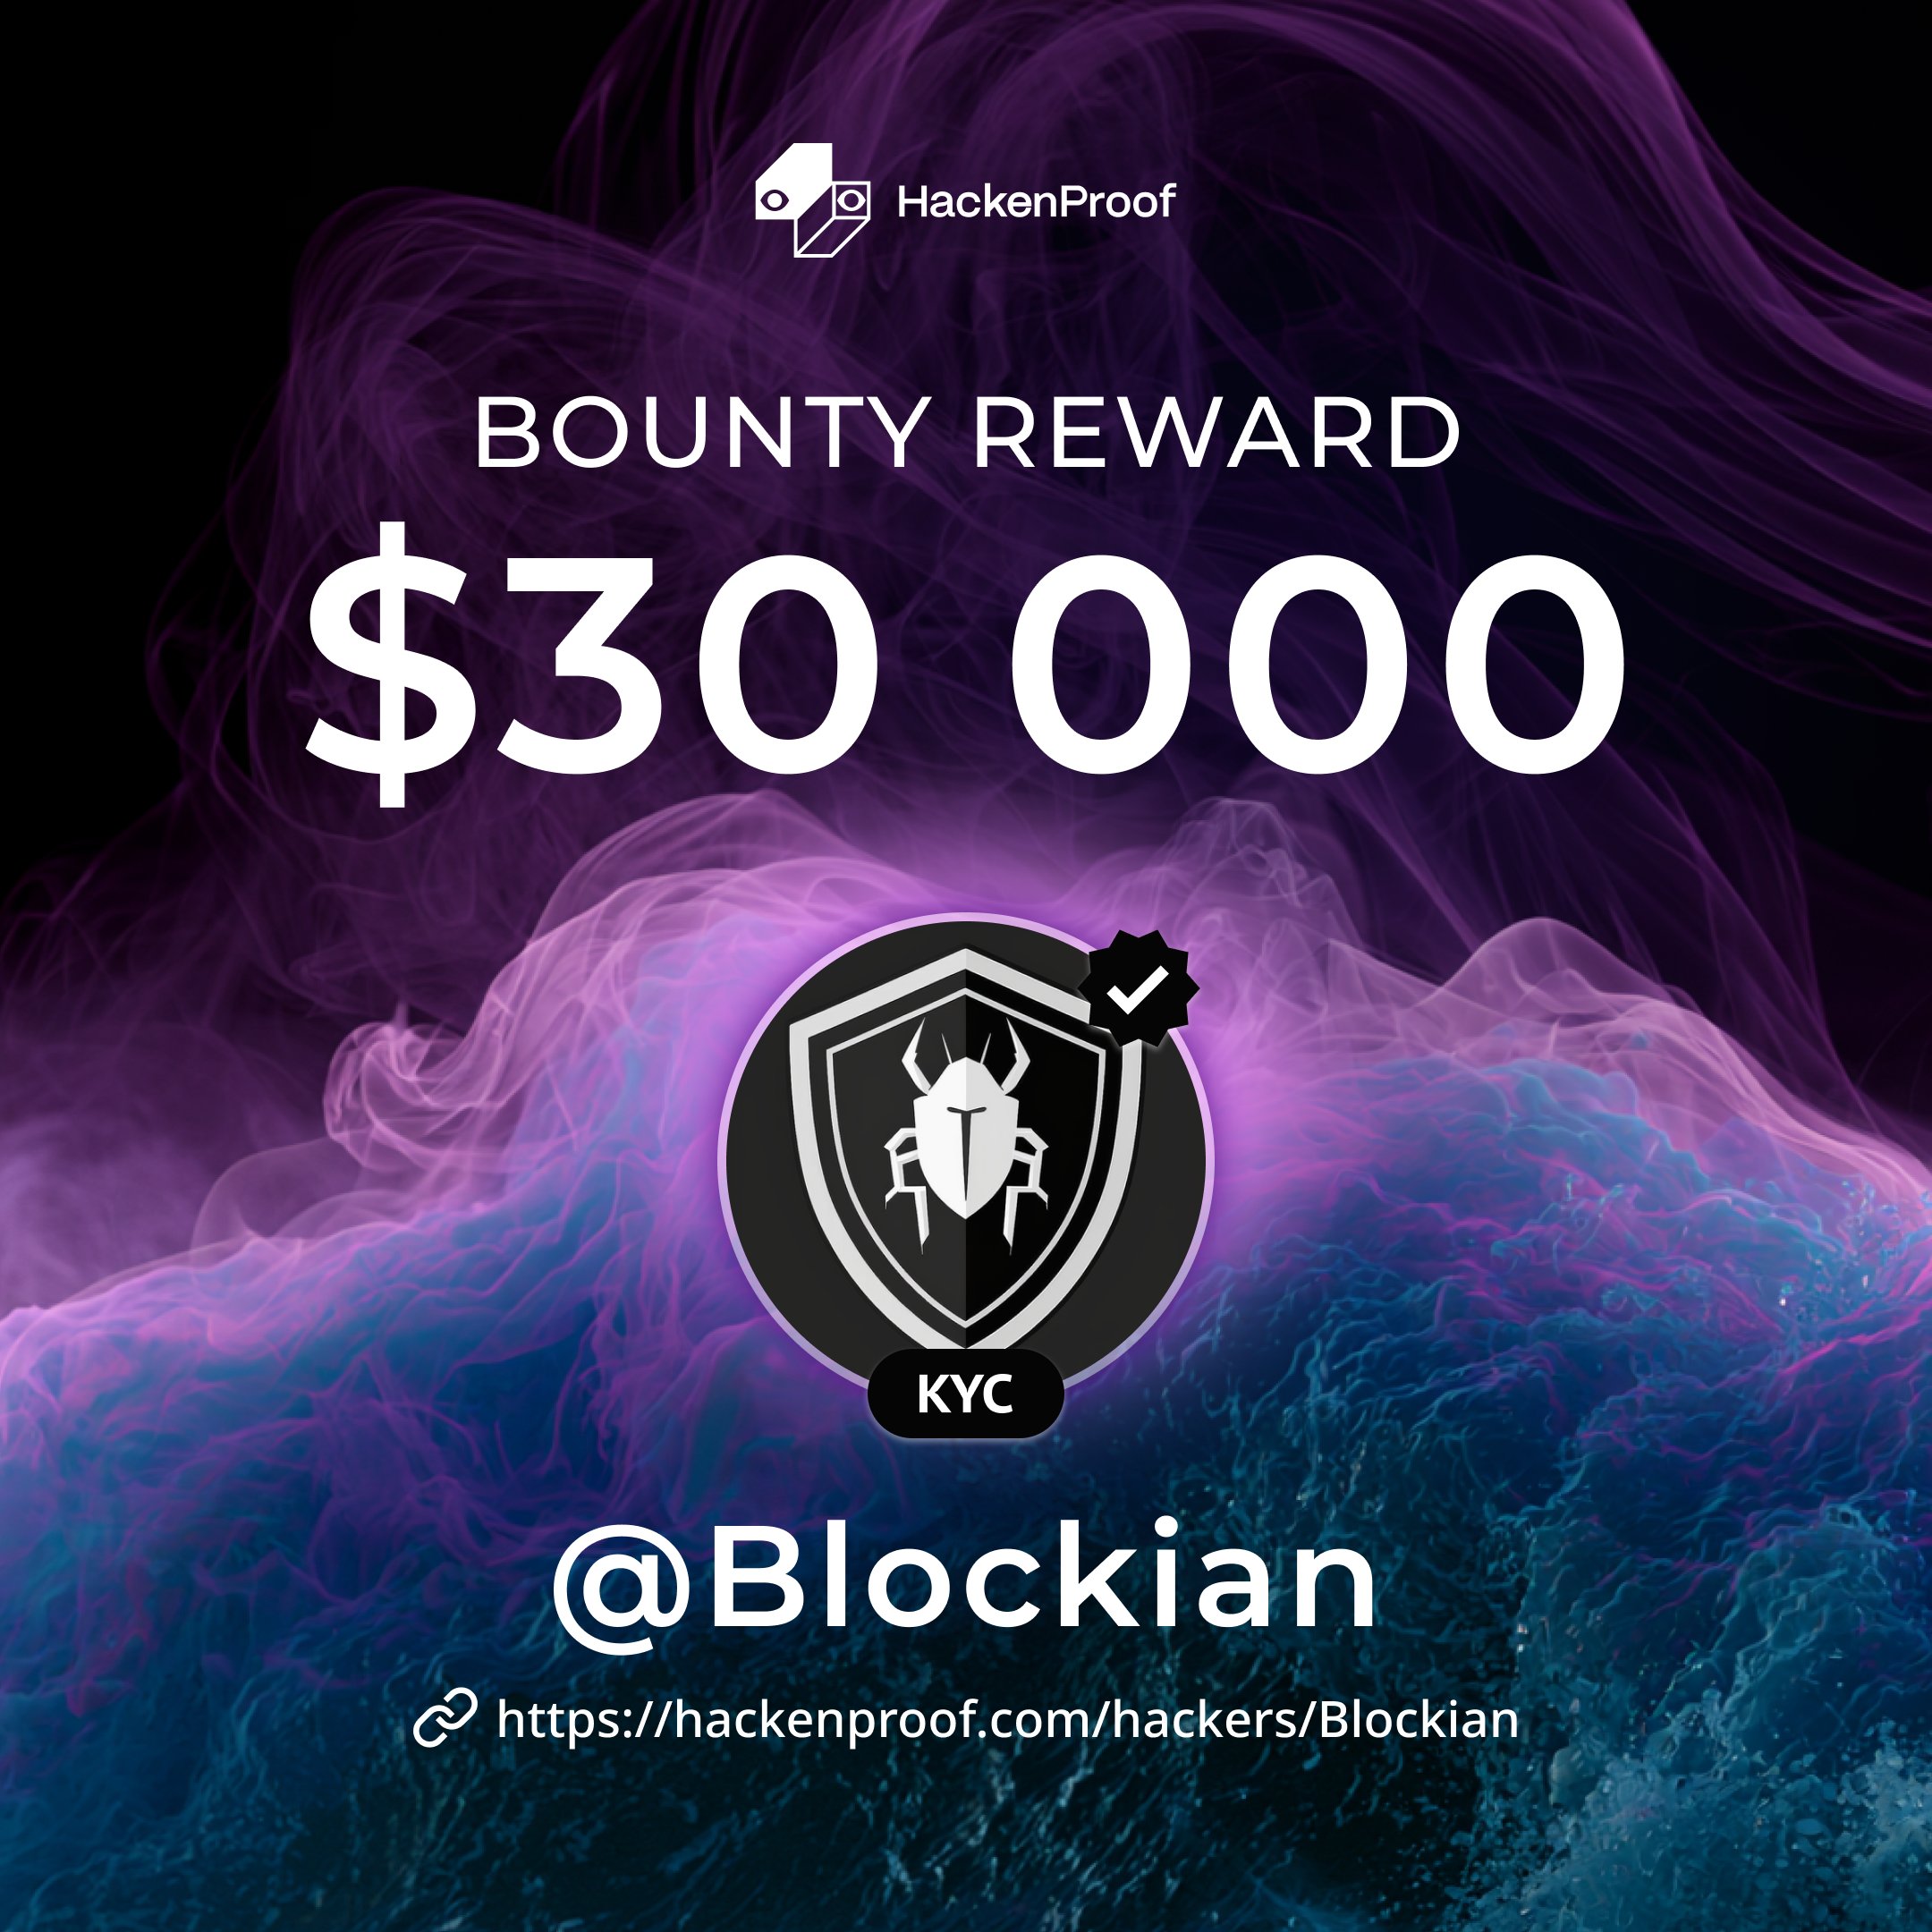
$30,000 in bounty rewards goes to @_blockian!
One more achievement, and certainly not the last.
Well deserved. Congratulations from HackenProof! 🏆
Blockian retweeted
I think this might be the largest bounty so far for an AI-assisted finding.
And yes, confession time: I used the AI tools I’ve been working on over the past few months to help find this bug. I’d love to say it was all me, but that wouldn’t be honest. The world is changing, and AI is clearly becoming a big part of it.

Just a few days ago, the legends behind @_blockian found a max critical that earned them $250,000.
Merry Christmas!

Blockian retweeted
How did I do on my 2025 New Year’s resolutions?
❌ $1M in revenue -> Failed
Total revenue this year across all platforms + audits: $907K
❌ $1M in a single bounty -> Failed
Biggest single bounty: $250K on Immunefi
✅ Top #30 on @immunefi -> Success
Reached rank #22 just yesterday
✅ Full planche -> Success
Can hold a full planche for ~4 seconds
Some accomplishments that weren’t on my original list:
✅ Top #10 on @HackenProof
At the start of the year I’d never even tried HackenProof, but after @WhiteHatMage went on a journey to other realms, I decided to give it a shot. Had a lot of fun and reached #7 all-time.
✅ Snowboarded for 4 months
Took a much-needed break at the start of 2025 to snowboard. Best trip of my life.
✅ Had fun
Beat Silksong, E33, and generally learned to slow down a bit. This year taught me that taking breaks and enjoying life actually matters.
So while I technically failed most of my 2025 resolutions, it was still a great year overall. Here’s hoping 2026 will be just as good -
and that I’ll do a better job sticking to my resolutions this time 😄
Blockian retweeted
Ok, here are the statistics for confirmed and paid findings from the past ~2 months, assisted by the AI tools I’ve been working on:
@immunefi :
2 Criticals
1 High
1 Low (marked as Critical but should be downgraded due to default configuration restraints)
@HackenProof :
1 High
@Hacker0x01:
1 High
Private Bug Bounties:
2 Critical
1 Low
Total payouts are expected to be roughly ~$400K. Payouts tend to move slowly, so more of the results should become public over time.


Yesterday I shared that, over the past ~2 months, I’ve been working on AI agents for security research in the Blockchain/DLT space. It seems to have sparked some interest, so I’m wondering - would you be interested in seeing the actual results and stats from that period?
93%Yes! Reveal those numbers
7%No, who cares?
124 votes • Final results Blockian retweeted

🧙♂️Wise sage @_blockian once sad:
🧠 DEBUG
📜 "Don’t underestimate the importance of a working debug setup"👇
web3-sec.gitbook.io/art-of-a…

Blockian retweeted
I think it’s fair to say me and @Schnilch share the first place, only $800 difference, now that’s a close one!
Great job my friend! And thanks to @HackenProof and @Somnia_Network

@Somnia_Network Audit Contest — Results Are In! 🚀
The world's largest C++ security showdown has concluded with epic finds and fierce competition.
Here's the scoop on our top performers and their well-earned bounties:

Blockian retweeted
Ok, I think I’ve got it done.
Rank 7 @HackenProof all time leaderboard 🤘🏻

Damn, I thought it would be enough to pass @WhiteHatMage on the @HackenProof leaderboard
Oh well, guess I'll keep going


Blockian retweeted
Damn, I thought it would be enough to pass @WhiteHatMage on the @HackenProof leaderboard
Oh well, guess I'll keep going
Blockian retweeted
Ok, just wrapped up @expedition33 by @SandfallGames (yes, including Simon), and here’s where I’m at:
1. Easily the best game I’ve played in a while - my heart is broken.
2. Esquie is my spirit animal.
3. Y’all had your chance to find bugs. Now that I’m back, it’s over and I’m about to cook.
I’m feeling Wheee

Blockian retweeted
🌟 This June, HackenProof paid out $402,800 to ethical hackers!
💰Top payout: $100,000 to @_blockian for an epic find!
Join our community of cybersecurity heroes and unlock massive rewards by securing the digital world!


Blockian retweeted

7/⛵️ Jack's Revenge
Motto: “Avenging All The Hacks in Web3"
Led by the infamous SR duo @_blockian, and with Season 2 favorites @0jovi0, @KeiZo_Zo, and more, forming one of the best assembled teams on Island 3.
#ImmunefiIsland3

Blockian retweeted
I didn’t participate in the @spectra_finance contest - and after seeing how the team handled the outcome, I’m very glad I didn’t.
Their latest response is one of the most baffling attempts I’ve seen to avoid fairly compensating security researchers. Let’s unpack their reasoning:
Spectra argues that the line on the [contest page](immunefi.com/audit-competiti…) -
"A reward pool of $40,000 USD will be distributed among participants, if any valid bugs are found"
somehow contradicts the rest of the page. They support this claim with three questions:
- "Why did Immunefi create and publish a reward structure broken down by severity?"
- "Why did Immunefi state that each tier would receive a "portion of the pool"?"
- "Why did Immunefi repeatedly describe the rewards as "up to $40,000"?"
I'd like to clarify that I don’t speak for Immunefi, but here’s how any reasonable reader would interpret this in my opnion:
1. Severity-based reward breakdowns exist because vulnerabilities aren’t binary. Not all issues are created equal - a Critical is more impactful than a Medium or Low. So if 10 Criticals and 10 Mediums are found, they shouldn’t get equal shares. That’s the point of the severity tiers: _to fairly distribute the pool based on impact_, not to gate how much of the pool is unlocked.
2. "Portion of the pool" refers to the dynamic nature of bug discovery. You don’t know in advance how many bugs of each severity will be found, so you can't preallocate fixed amounts. If it were a fixed distribution, the page would’ve said something like: "Critical: $10k, Medium: $5k," etc. That’s not what it said. Also, yes - 10/10 is still a portion. A portion doesn’t necessarily imply “less than the whole.”
3. "Up to $40,000" is accurate because the full amount is only unlocked if valid bugs are found. If only insights are found, only 15% is awarded, as stated explicitly on the same page -> "If not a single bug is found (Insights do not count as bugs), the reward pool is $15% of $40,000 USD rewards → $6,000". So the full range of outcomes is:
- $0 for no insights or bugs
- $6,000 if only insights are found
- $40,000 if _any_ valid bugs are found
There’s no deception here, this is a clear "Up to $40,000". The tiers describe severity-based allocation, not unlocking of the reward pool.
-------------------------------------------------------
Spectra then claims:
"If the full reward pool was always meant to be triggered by any valid finding, there would be no reason to introduce tiered severity logic or language about capped distribution."
This is just wrong. The tiered severity logic exists to fairly _divide_ the reward pool if multiple issues of different severity are found. And “capped distribution” accurately describes the tier-based allocation - not the conditions for unlocking the pool.
And here’s the kicker: Spectra admits they were shown a preview of the full contest page on April 2. That means they saw all the relevant language - including:
- "A reward pool of $40,000 USD will be distributed among participants, if any valid bugs are found"
- "If not a single bug is found (Insights do not count as bugs) the reward pool is $15% of $40,000 USD rewards → $6,000"
They had this information. They just chose to ignore what it clearly meant.
-------------------------------------------------------
Now let’s talk about their proposed solution - and the flaws in their logic.
Spectra “generously” offered $10,000 (25% of the pool) and later increased that to $15,000 “as a gesture of goodwill,” to pay to the two unique medium-severity issues that were confirmed.
But under their logic, if researchers had found one Medium and one Low they would have unlocked both the `low` portion and the `medium` portion, so they’d have gotten more than two Mediums (unlocking only the `medium` portion as claimed by Spectra). So… 1M + 1L > 2M? That makes no sense.
What if 10 Criticals were found? Would that only merit $10k under their model?
For me, it’s clear their approach isn’t based on rewarding actual severity or impact - it’s just an attempt to minimize payout.
In my opinion, if Spectra genuinely misunderstood the structure, a somewhat fair resolution would’ve been to offer at least $20k, to account for both Medium and Low tiers. Instead, they’re cherry-picking language to justify underpaying researchers who did exactly what was asked.
-------------------------------------------------------
In my view, this isn’t a miscommunication - it’s a strategy to avoid honoring the commitment to researchers.
-------------------------------------------------------
Much respect to @immunefi for standing up for their SRs and making sure they get what they’ve earned.


Blockian retweeted
🚨 Remember @_blockian, who earned $125,000 on HackenProof?
We’ve got a full podcast episode with them on our YouTube channel.
Hear their story, mindset, and tips for breaking into top-tier bug bounty hunting.
Watch now: youtube.com/watch?v=sRBBMJAm…
Wow, what a milestone!💥
Congratulations to @_blockian for racking up an incredible $125,000 in bounties on HackenProof!

Blockian retweeted
Wow, what a milestone!💥
Congratulations to @_blockian for racking up an incredible $125,000 in bounties on HackenProof!


