

Blending AI with Offensive Security Research and Bug Bounty. Creator of https://xitter.cf/t.co/0N9TViC20w
Joined July 2017
- Tweets2.3K
- Following630
- Followers25.4K
- Likes8.8K



Pinned Tweet
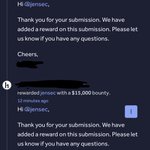
Last month was my highest in bug bounty so far with almost $131k in bounty.
Total paid reports: 18
Average reward: $7.3k
Category: most were logical findings via reversing mobile applications and discovering internal endpoints leading to code execution and missing auth etc

Triaging experience at @Bugcrowd is extremely bad, even the valid demonstrated findings with POC and high - critical impacts are being marked N/A with templated comments.
Bug Bounty Programs need to keep in mind that they are nothing without their community of hackers.


GPT 6 SOL is wrong model to benchmark againt, compare against 5.6 SOL. I think no publicly accessible models come close to 5.6 SOL.

We found DeepSeek V4.1 Flash 1017 beats GPT 6 Sol on our multi-step offensive cybersecurity task. Sol was tested via the Daybreak trusted access program.
We have been building a cybersecurity benchmark based on simulated corporate networks. This is a valuable indicator for the cyber-risk a model poses if in the hands of a bad actor. We plan to make the full evaluation public in the coming weeks but wanted to share our first immediate finding here.

Yesterday, got hit with a duplicate for a critical bug: mass customer PII exposure using nothing more than a public flight number.
Worse part? The original report was submitted a month ago and the issue is still live.


We at @exodus BBP fully automated triage with multi agents workflows with very high accuracy, has reduced triage time 7x and needing a human to only 0.2h/week.
Though giving agents Github access was huge bump in accuracy and Platform doesn't have such luxury for their bots.

Codex limits are hallucinating like their models, Earlier it dipped from 100% to 15% and now jumped back to 32%, what is going on @thsottiaux
Even with best of AI models findings like these are not going be walk in the park. you need a lot of visualisation, understanding of security model and architecture and breakdown chains in steps. Incredible talent.


Fun challenge, Vercel team is cool.

We offered $1M to escape Vercel Sandbox.
• 1,285 reports
• $242,000 in bounties paid out
• One Linux kernel zero day discovered
• No reports of customer data compromise
vercel.com/blog/findings-fro…

At this rate, I wouldn’t be surprised if Open AI or Anthropic Acquires HackerOne, BugCrowd of similar BBP platform for all its datasets
Anthropic models are much better at discovery (breadth), while Open AI models are very good at exploitation (depth).
Anthropic's Cyber Verification is absolutely useless and doesn't align with their statements of giving capable models to defenders.


$460 in tokens → ~$22K in bounties.
We placed #1 on the Vercel Sandbox Program leaderboard on HackerOne with almost zero manual hacking.
When the $1M challenge dropped, we built multi-model hackbots to benchmark agent harnesses across open-weight models. We built the harness; the agents did the hunting. GLM 5.3 for exploit writing and Kimi K3 for discovery followed by DeepSeek as monitoring agent carried the most weight.
The numbers:
- Findings: 20
- Duplicates: 12
- Known risk: 3
- Paid: 5
- Top bounty: $7,500
- Max severity: Medium
Huge thanks to @Paaastha @uttam_v10 @Knaughtydog04, and to @vercel for running a smooth challenge with fair payouts.


