
VP of Technology @ VigilantSec | USAF Veteran | views are my own
Washington, DC
Joined June 2021
- Tweets106
- Following245
- Followers88
- Likes1.3K




Joey Fitzpatrick retweeted

A leader of what was once the world’s most harmful cyber crime group has been unmasked and sanctioned by the UK, US and Australia, following an NCA-led international disruption campaign.
#Cronos @FBI @Europol
Full story ➡️ nationalcrimeagency.gov.uk/n…
Joey Fitzpatrick retweeted
After infiltrating LockBit's systems, we gathered a lot of information about their criminal activity and those who worked with them.
Including their network of 194 hackers or 'affiliates' who we'll be in touch with very soon.
Until then, we hope they have a nice day 🙂
#Cronos

ALT LockBit's 194 affiliates by ID and username

ALT Screenshot of the LockBit leaksite showing the message that now greets their affiliates on logging in
Joey Fitzpatrick retweeted

All of JA4+ in Wireshark!
The JA4+ Plugin is now available!
github.com/FoxIO-LLC/ja4/tre…

👏It’s really amazing to see all of the work that the @FiligranHQ team has put into OpenCTI over the past few years and to see the community of connectors grow. If you're looking to change TIPs, check them out: github.com/OpenCTI-Platform/…
Check out our latest connector update ⤵️


🎉 Our IronRadar connector for OpenCTI has been updated!
New Features:
✅Automatically creates relationships
✅Updates description with threat service + port
✅Adds multiple threat services observed on a single indicator
Trial:aws.amazon.com/marketplace/p…
➡️github.com/OpenCTI-Platform/…


Joey Fitzpatrick retweeted

#IronRadar has been tracking 44 indicators of #c2 🕹️infra observed internally and through public reporting leading to #ALPHV/#BlackCat #ransomware. Let's take a look at how we got here via our research below with IOCs on GitHub ⬇️


Joey Fitzpatrick retweeted
📰 #IronRadar May Update
🎯 10 new detections (e.g. #Havoc: c2.http.listener)
📈 #Qakbot (+72%) #DcRat (+66%)
🕵️ Detected Black Basta & ALPHV
#threatintel


Really exciting to see other brands parter with @Tesla to adopt NACS and to utilize the supercharging network! The other charging networks just cannot compete. Who’s next? 🔌

BREAKING: @Tesla CEO @elonmusk & GM CEO @mtbarra have reached an agreement for GM to adopt Tesla's North American charging standard & provide GM customers access to over 12k Tesla Superchargers across the US & Canada.
Tesla's NACS is now the main standard for Tesla, GM & Ford.

285


Joey Fitzpatrick retweeted
📰 #IronRadar April Update
🎯 6 new detections (e.g. sliver: c2.http.listener)
📈 Stealc (+32%) Viper (+19%)
🕵️ Detected Bl00dy Ransomware Gang


Joey Fitzpatrick retweeted
#TrueBot is indeed back!
First reported by Group-IB:
xitter.gq/GroupIB_TI/status/1659…
#IronRadar is tracking active c2.http.listener(s):
45.182.189.91:80
45.182.189.91:443
45.227.253.100:80
Silence: attack.mitre.org/groups/G009…

Joey Fitzpatrick retweeted
From our #IronRadar collections, let’s take a look at some of the domains recently mentioned by @Unit42 in their #RoyalRansomware post unit42.paloaltonetworks.com/… such as kasperslkyupdate[.]com and kasperskyupdates[.]com

Joey Fitzpatrick retweeted
❗Together with the Military Counterintelligence Service we've detected an ongoing espionage campaign linked to the APT29/NOBELIUM group. We're publishing detailed technical analysis of their latest tools, mostly never publicly described before. Read more: gov.pl/web/baza-wiedzy/espio…

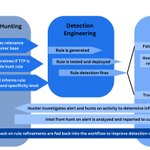
Your operational workflows are just as important to the detection and intelligence lifecycle as the means of how you detect adversary activity. If your workflow is incomplete or sloppy, you miss the opportunity for your detections to become a force multiplier
Building on blogs by @cyb3rops and @Kostastsale on #DetectionEngineering and #ThreatHunting, IronNetTR discusses how we developed an efficient cyber operations workflow and what lessons we learned along the way
ironnet.com/blog/building-a-…
Watching the threat analysis and hunt ops teams collaborating more around intelligence, TTPs, and detecting adversaries in customer environments has been inspiring to say the least @iAmTippett @_brettfitz @PeterRydzynski @MorganDemboski @mylwaremyk @GrengaAJ 🔥
1
3
281