Adrian โ›ฉ๏ธ Hetman ๐Ÿบ | ๐Ÿ““+๐Ÿ–‹๏ธ+โ˜•๏ธ (@adrianhetman) header
Adrian โ›ฉ๏ธ Hetman ๐Ÿบ | ๐Ÿ““+๐Ÿ–‹๏ธ+โ˜•๏ธ (@adrianhetman) profile picture

Director of Managed Solutions @HalbornSecurity | Blog https://xitter.gq/t.co/hYnS7zAEyB | Crypto News: https://xitter.gq/t.co/xKoneiRMCb |

Gdynia, Polska
Joined September 2017
Photo by Adrian โ›ฉ๏ธ Hetman ๐Ÿบ | ๐Ÿ““+๐Ÿ–‹๏ธ+โ˜•๏ธ (@adrianhetman)Photo by Adrian โ›ฉ๏ธ Hetman ๐Ÿบ | ๐Ÿ““+๐Ÿ–‹๏ธ+โ˜•๏ธ (@adrianhetman)Photo by Adrian โ›ฉ๏ธ Hetman ๐Ÿบ | ๐Ÿ““+๐Ÿ–‹๏ธ+โ˜•๏ธ (@adrianhetman)Photo by Adrian โ›ฉ๏ธ Hetman ๐Ÿบ | ๐Ÿ““+๐Ÿ–‹๏ธ+โ˜•๏ธ (@adrianhetman)Photo by Adrian โ›ฉ๏ธ Hetman ๐Ÿบ | ๐Ÿ““+๐Ÿ–‹๏ธ+โ˜•๏ธ (@adrianhetman)Photo by Adrian โ›ฉ๏ธ Hetman ๐Ÿบ | ๐Ÿ““+๐Ÿ–‹๏ธ+โ˜•๏ธ (@adrianhetman)Photo by Adrian โ›ฉ๏ธ Hetman ๐Ÿบ | ๐Ÿ““+๐Ÿ–‹๏ธ+โ˜•๏ธ (@adrianhetman)Photo by Adrian โ›ฉ๏ธ Hetman ๐Ÿบ | ๐Ÿ““+๐Ÿ–‹๏ธ+โ˜•๏ธ (@adrianhetman)Photo by Adrian โ›ฉ๏ธ Hetman ๐Ÿบ | ๐Ÿ““+๐Ÿ–‹๏ธ+โ˜•๏ธ (@adrianhetman)Photo by Adrian โ›ฉ๏ธ Hetman ๐Ÿบ | ๐Ÿ““+๐Ÿ–‹๏ธ+โ˜•๏ธ (@adrianhetman)
Okay, it's live. Three issues of my newsletter "Burn Notice" out now. I started it for myself, honestly. I wanted an easier way to keep up with everything happening on the security side of crypto without it eating my whole week. Two kids, interviewing, learning new things, and still trying to have a life. That doesn't leave room to spend every waking minute on Telegram and X reading every heated thread. I wanted one thing I could read once a week that wouldn't cost me two hours. So I made it. A weekly read for people like me. Mostly the security folks keeping projects and orgs safe who want to stay on top of what actually matters. And the part-time security leads. The ones handed the job of hardening the org because no one internal is on security full time.
10
2
1
30
2,216
Adrian โ›ฉ๏ธ Hetman ๐Ÿบ | ๐Ÿ““+๐Ÿ–‹๏ธ+โ˜•๏ธ retweeted
Software engineers love saying that AI-generated code is unmaintainable. But let's not pretend the code humans have been writing for the last 30 years has been some masterpiece of maintainability.
270
588
125
4,997
171,111
Adrian โ›ฉ๏ธ Hetman ๐Ÿบ | ๐Ÿ““+๐Ÿ–‹๏ธ+โ˜•๏ธ retweeted
Me buying a MacBook with 128GB of RAM just to run AI models locally Sam Altman :
88
1,240
50
24,715
459,706
Adrian โ›ฉ๏ธ Hetman ๐Ÿบ | ๐Ÿ““+๐Ÿ–‹๏ธ+โ˜•๏ธ retweeted
Using a stick of RAM to stir my coffee this morning, fuck you, Sam Altman
573
11,063
257
183,850
2,765,125
Adrian โ›ฉ๏ธ Hetman ๐Ÿบ | ๐Ÿ““+๐Ÿ–‹๏ธ+โ˜•๏ธ retweeted
The sort of thing your agent writes tests for
The chances of being killed by a landmine delivered by a bear are low, but they are never zero.
77
835
36
14,214
327,789
Adrian โ›ฉ๏ธ Hetman ๐Ÿบ | ๐Ÿ““+๐Ÿ–‹๏ธ+โ˜•๏ธ retweeted
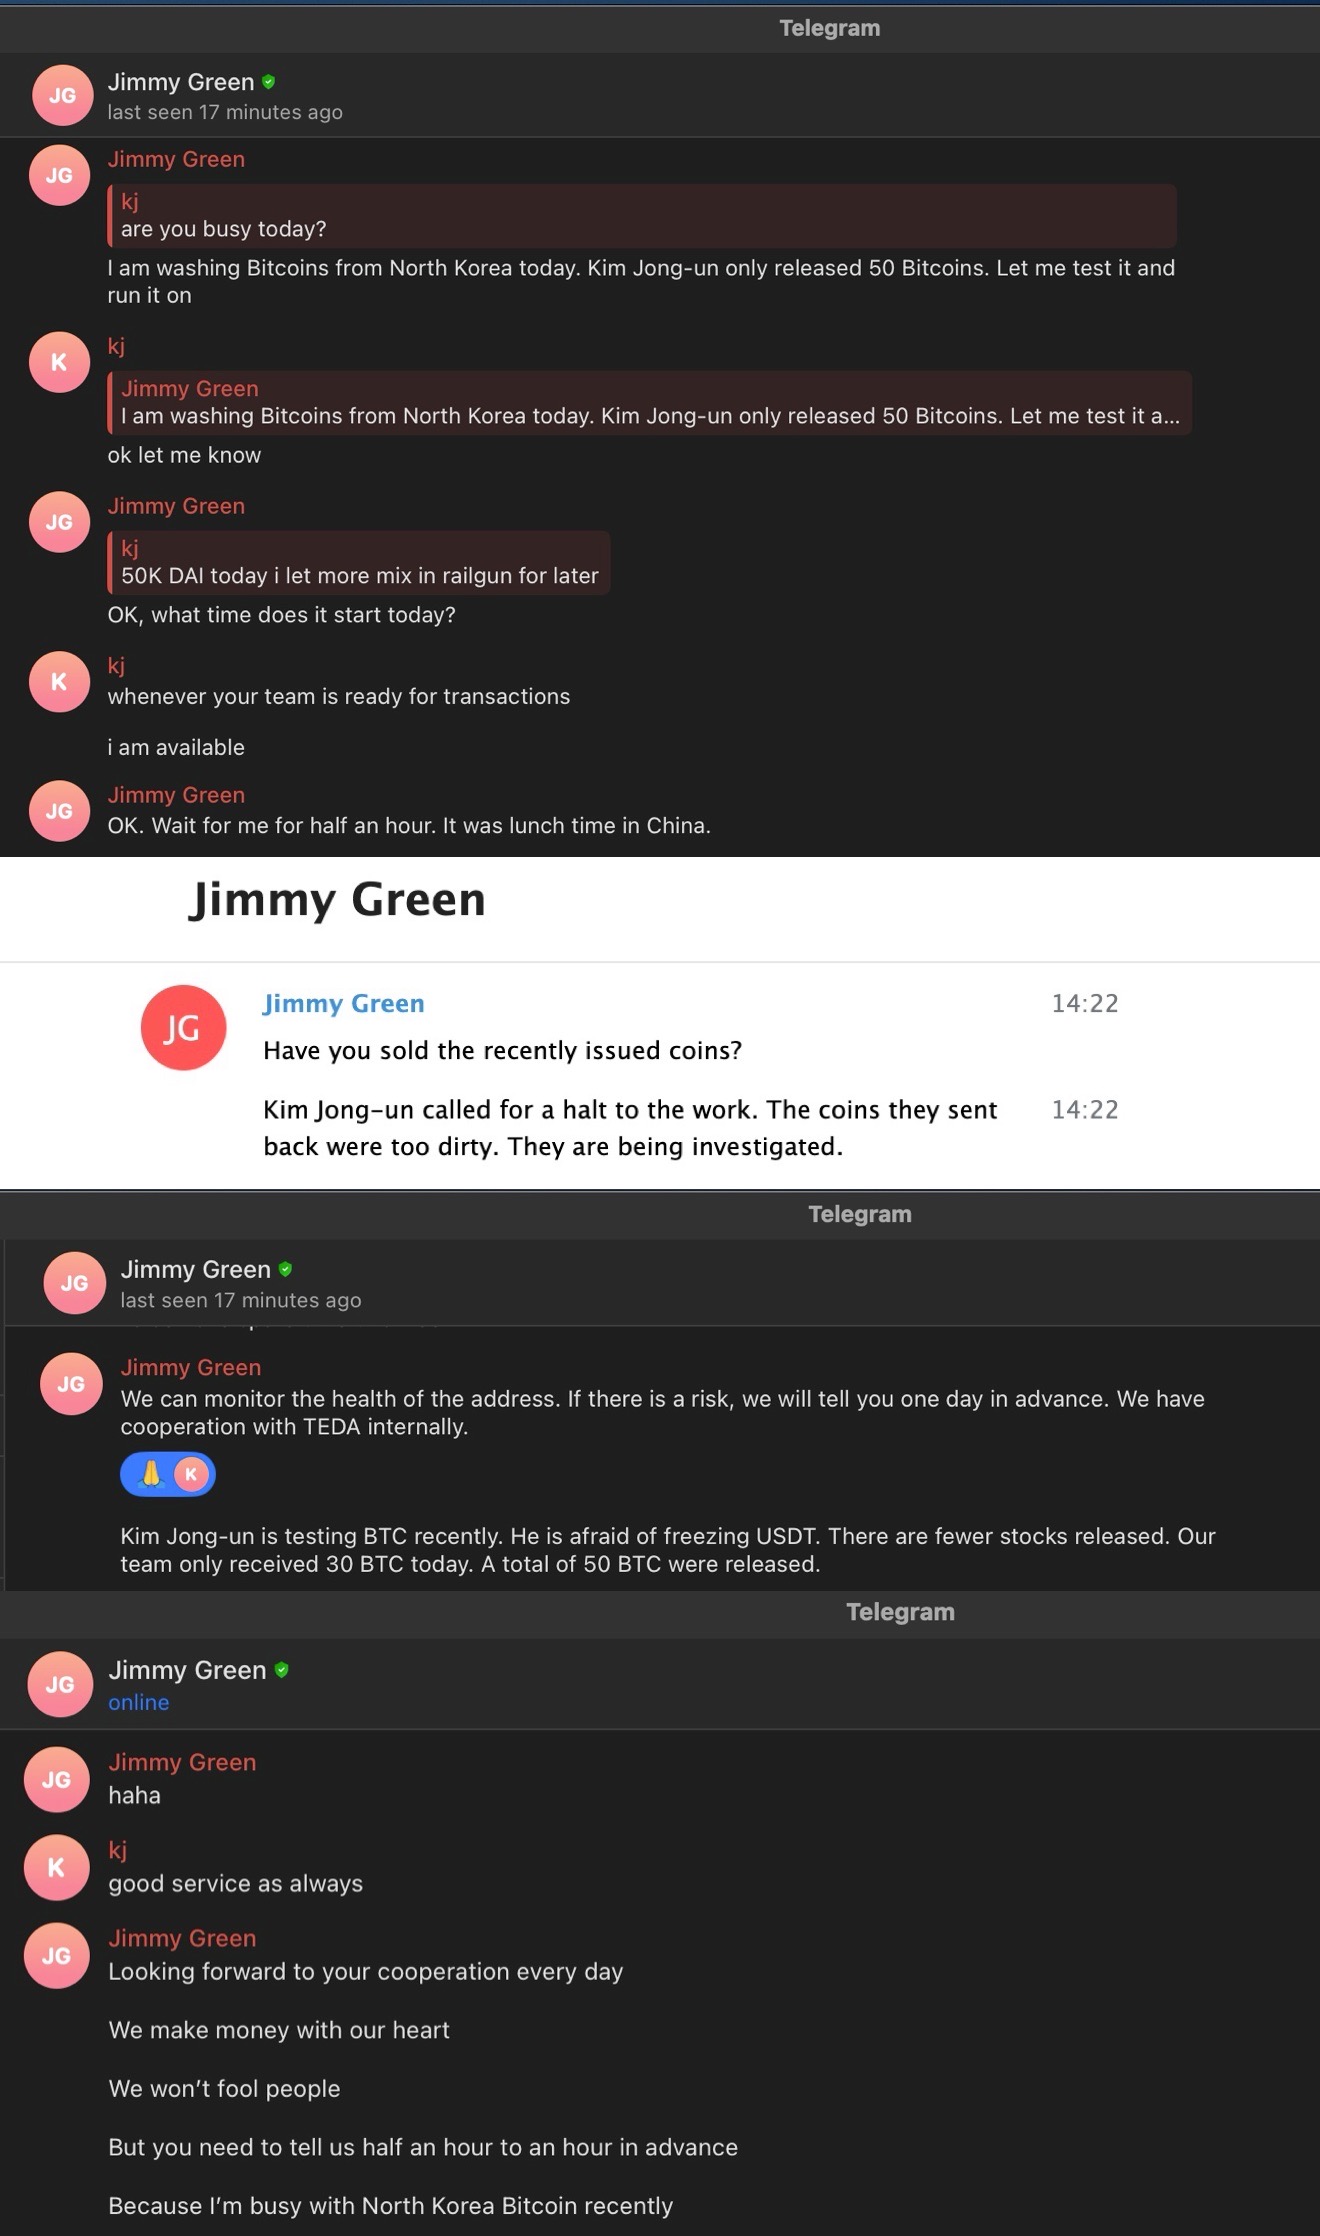
1/ How I infiltrated a Chinese organized crime syndicate that has laundered $1B+ across multiple exploits for Lazarus Group. Posing as a client, I gathered intel that helped action freezes for the Feb 2025 Bybit exploit and attribute illicit activity onchain.
1,953
4,213
1,315
30,660
4,977,907
Adrian โ›ฉ๏ธ Hetman ๐Ÿบ | ๐Ÿ““+๐Ÿ–‹๏ธ+โ˜•๏ธ retweeted
The one document that decides if your week was worth it isn't the codebase-it's the bug bounty program text nobody reads. Years on the triage side taught @adrianhetman the edge most whitehats skip. xitter.gq/adrianhetman/status/20โ€ฆ
1
2
23
3,045
Adrian โ›ฉ๏ธ Hetman ๐Ÿบ | ๐Ÿ““+๐Ÿ–‹๏ธ+โ˜•๏ธ retweeted
Isaac Asimov, explaining how he understood the metaphorical meaning of the One Ring and Mordor in Tolkien's โ€˜Lord of the Ringsโ€™ by driving on a New Jersey highway: โฌ‡๏ธ
25
158
17
1,552
50,383
Adrian โ›ฉ๏ธ Hetman ๐Ÿบ | ๐Ÿ““+๐Ÿ–‹๏ธ+โ˜•๏ธ retweeted
Iโ€™m hearing elevated levels of dissatisfaction with submission fees, long triage times, and high levels of duplicates on bug bounty programs. How about automatic full disclosure of bugs in 30 days or less? Bug hunters shouldnโ€™t have to waste time hunting dupes on deadbeat projects unable to protect themselves and their users expediently. A reminder of how we got here and what will happen if legitimate security researchers are mistreated for too long:
3
13
2
68
7,937
Adrian โ›ฉ๏ธ Hetman ๐Ÿบ | ๐Ÿ““+๐Ÿ–‹๏ธ+โ˜•๏ธ retweeted
a few months ago i argued that security researchers would be some of the last people to get replaced/ affected by AI, simply because the job is relatively complex and if AI can do it, there are 1000s of other easier jobs that it should be able to do too. what i didn't consider was that people who work in this field are simply some of the most entrepreneurial and would be the first to make use of the new technology. even though 80% of the population works jobs which can already be automated, most companies don't know/ don't care, so these people end up being safe for longer than i anticipated.
15
15
1
266
20,933
Adrian โ›ฉ๏ธ Hetman ๐Ÿบ | ๐Ÿ““+๐Ÿ–‹๏ธ+โ˜•๏ธ retweeted
Your ability to explain something is a measure of the how much you understand it.
6
13
1
115
7,162
Adrian โ›ฉ๏ธ Hetman ๐Ÿบ | ๐Ÿ““+๐Ÿ–‹๏ธ+โ˜•๏ธ retweeted
Been saying this since the beginning. Almost all harness/agent engineering is a negative ROI race to the bottom.
whatever bug finding harness you build is going to be made redundant by the next frontier model release. few understand how this impacts what you should be building
5
2
56
4,662
Adrian โ›ฉ๏ธ Hetman ๐Ÿบ | ๐Ÿ““+๐Ÿ–‹๏ธ+โ˜•๏ธ retweeted
An important principle: Never pay someone to remove a problem that they themselves created
please consider using our models to help defend your systems
97
349
48
5,942
1,277,795
Adrian โ›ฉ๏ธ Hetman ๐Ÿบ | ๐Ÿ““+๐Ÿ–‹๏ธ+โ˜•๏ธ retweeted
In July 2025, a man opened his bug bounty inbox. He found seven security reports. All seven had arrived in the last sixteen hours. He read every one. Not one described a real bug. His name is Daniel Stenberg. He runs curl, software that sits on billions of devices, and his security team is seven volunteers. Every report looked confident and precise. Each one named real functions and cited a real class of bug. Each one was a chatbot's guess in the shape of a discovery. And each one took a person far longer to disprove than the machine took to write. Stenberg gave the pattern a name. Death by a thousand slops. --- More in the article below. burnnotice.adrianhetman.xyz/โ€ฆ
36
5
75
2,196
In July 2025, a man opened his bug bounty inbox. He found seven security reports. All seven had arrived in the last sixteen hours. He read every one. Not one described a real bug. His name is Daniel Stenberg. He runs curl, software that sits on billions of devices, and his security team is seven volunteers. Every report looked confident and precise. Each one named real functions and cited a real class of bug. Each one was a chatbot's guess in the shape of a discovery. And each one took a person far longer to disprove than the machine took to write. Stenberg gave the pattern a name. Death by a thousand slops. --- More in the article below. burnnotice.adrianhetman.xyz/โ€ฆ
36
5
75
2,196
Adrian โ›ฉ๏ธ Hetman ๐Ÿบ | ๐Ÿ““+๐Ÿ–‹๏ธ+โ˜•๏ธ retweeted
Ladies and gents, the Great Filter
JUST IN - For the first time, AI has designed complete viral genomes, producing 16 functional viruses that infect bacteria and "pose no threat to people." โ€” BBC
392
5,053
90
81,489
3,660,648
Adrian โ›ฉ๏ธ Hetman ๐Ÿบ | ๐Ÿ““+๐Ÿ–‹๏ธ+โ˜•๏ธ retweeted
Itโ€™s been 2 weeks since my last post, all due to my new job and new reality of juggling between work and 2 kids and still being a good husband. But weโ€™re back! โ€” The two largest crypto losses of late July 2026 occurred within days of each other, and neither attack required breaking any cryptography. In each case, the loss originated in the way a system's keys were generated or held. Coldcard, a Bitcoin hardware wallet, lost more than $116 million after a firmware change made in 2021 caused affected devices to generate their seed phrases with far too little randomness. Because the weakness lay in the keys themselves, an attacker could reproduce them from public blockchain data alone and empty the wallets remotely, and the flaw had shipped unnoticed for more than five years. AFX Trade, a perpetuals exchange on Arbitrum, lost about $24 million from a bridge it operated itself rather than the network's native one. An attacker obtained the private signing keys of five of the bridge's seven validators, which was sufficient to meet its two-thirds quorum, and the contract released the funds against signatures it accepted as valid. The security of the bridge had rested entirely on the custody of those keys. As audited contract logic has become harder to exploit directly, the decisive weaknesses have moved to the foundations beneath it, including the randomness that produces a key and the custody of the keys that approve a transfer. For any team holding or moving significant value, the relevant question is no longer only whether the contract is correct, but when the generation and custody of its keys were last independently examined. A full analysis of both incidents is in this week's Burn Notice below ๐Ÿ‘‡
1
2
8
652