

A malware researcher from Kazakhstan | All views are my own
Kazakhstan
Joined September 2019
- Tweets135
- Following189
- Followers426
- Likes213

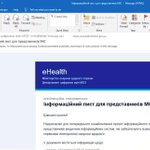




🚨 #ThreatIntel Update: The phishing campaign masquerading as the Ukrainian eHealth portal is actively targeting the government sector.
A mailbox within the infotech[.]gov[.]ua domain (a state IT enterprise) has been identified as a target. This elevates the operation to a highly targeted cyber espionage campaign, likely aimed at a supply chain compromise.
Key Details:
• Targets: Government IT infrastructure and MIS representatives.
• Objective: Credential harvesting via highly specific lures.
• Context: Execution patterns strongly suggest a suspected #APT operation.
• Analysis: The related sample has been observed and analyzed in the ANY[.]RUN sandbox.
Indicators of Compromise (IOCs):
domain: letter-moz.pp[.]ua
url: hxxps[:]//letter-moz.pp[.]ua/?rid=Tb6LDiS
url: hxxps[:]//moh-digital.blogspot[.]com/2026/07/blog-post.html
#CyberSecurity #Ukraine #SupplyChain

Askar Dyussekeyev retweeted

🚨Alleged Daryn.online Breach Exposes 4.2M Kazakh User Records
A darkweb forum post claims the exposure of 4.2 million user records from daryn.online, a prominent educational platform in Kazakhstan. The listing, posted on an underground forum, alleges that a comprehensive database containing personal information, credentials, and academic data for students, teachers, and administrators has been compromised.
According to the post, the leaked dataset includes sensitive personally identifiable information (PII) and authentication details. The actor lists the following fields as exposed:
* Full names (first and last)
* Phone numbers and email addresses
* Password hashes (bcrypt format)
* Individual Identification Numbers (IIN)
* Birthdates and gender
* User roles (student, teacher, admin)
* Academic metrics (grades, ratings, lesson counts)
* Last known IP addresses
The source material includes sample entries showing hashed passwords, active session tokens, and detailed profiles of educators, including one administrator with the email "[email protected]" and another with "[email protected]". The data also reveals internal identifiers such as user_id, school_id, and region_id, suggesting a structured database dump rather than a scraped surface-level leak.
Daryn.online is a significant player in Kazakhstan's EdTech sector, providing online tutoring and preparation for national university entrance exams. The exposure of millions of records, including minors' data and teacher credentials, poses significant privacy risks and potential for credential stuffing or phishing attacks against the educational community.
At the time of reporting, the alleged breach has not been independently verified by Daryn.online or security researchers.

Askar Dyussekeyev retweeted

Lately I’ve been exploring AI tooling for Offensive Security.
After trying a bunch of existing projects, I realized I wanted something with a different workflow and architecture.
So I started building PentestCode - a fork of OpenCode focused on penetration testing.
Current work includes shared engagement state, task planning, automatic parsing of common security tools, attack path generation and cross-agent memory.
Still very early, but I’d love to hear your feedback.
github.com/s0ld13rr/pentestc…

Always great to see major vendors like @Seqrite validating my independent research! 🕵️♂️
I published the exact infection chain, LotL TTPs (Smart Install Maker -> Tray Minimizer -> AnyDesk), and IOCs for this Rare Werewolf aerospace campaign days ago.
Proper attribution in the infosec community goes a long way. I'd appreciate a credit in the blog post! 👇
xitter.gq/askardyuss/status/2070…
seqrite.com/blog/from-invoic…
#ThreatIntel #CyberSecurity #OSINT #RareWerewolf #APT

🚨 #ThreatIntel: Attack on Russian aerospace and electronics sectors ✈️🛰️
Recently, I found a highly suspicious EML file discovered in the @anyrun_app sandbox. The phishing email targeted a Russian manufacturer of semiconductor and electronic components.
While attribution is always tricky and I cannot state this as a hard fact, the operational tempo, targeting, and toolset heavily suggest a suspected Rare Werewolf (Librarian Ghouls) campaign.
🔍 Infection Chain:
1️⃣ Phishing email masquerades as a billing request from a legitimate Russian institute.
2️⃣ Attached is a password-protected RAR containing a PE32 payload disguised as a .com file.
3️⃣ The payload is a Smart Install Maker dropper. It executes curl.exe with the --resolve flag to bypass DNS filtering and download the next stage.
4️⃣ WinRAR extracts the payload (password: limpid29033).
5️⃣ Legitimate tools are abused: Tray Minimizer is used to hide a portable AnyDesk instance from the user for persistent, undetected remote access.
🛑 Indicators of Compromise (IOCs):
Domains:
aviatronika[.]online
vniir-avia[.]space
fgub-vniir[.]space
vniir-info[.]space
nova-stream[.]site
IP Addresses:
198.54.120[.]13
194.87.57[.]81
2.23.88[.]201
Hashes (MD5):
eabd440c996846d0992e37ab01d01208 (Dropper)
6cc3c68c56e099792fdeadde76256d56 (Payload RAR)
#InfoSec #CyberSecurity #Phishing #RareWerewolf #LibrarianGhouls #Malware #APT


🚨 Suspected APT campaign spotted targeting the 🇵🇰 Pakistani military using weaponized CHM files to deliver stealthy, compiled Python payloads.
The core sample was recently identified via the @anyrun_app sandbox.
📬 Infection Vector
The threat actor utilizes a highly targeted social engineering lure: a compiled help document (CHM) displaying a restricted international defense exhibition and military planning schedule for 🇵🇰 Pakistani defense establishments.
⚙️ Technical Details
• Initial execution leverages a classic ActiveX shortcut bypass via the HHCTRL.OCX control, silently spawning a hidden executable from the same directory.
• The payload is packed using the Nuitka OneFile framework, which translates Python scripts into native C/C++ instructions, rendering traditional Python decompilers useless.
• Deep analysis reveals a core payload named client_exe.dll. It imports specialized modules like _wmi.pyd for system reconnaissance/anti-VM checks and _ctypes.pyd for low-level Windows API interaction, backed by Rust-compiled cryptographic libraries.
🔍 Indicators of Compromise (IOCs)
CHM Lure MD5: 9CBE5D435F63E16B85BCA1F8C6EA4A9B
Dropped EXE MD5: 37B7AABFAD89345AACE02C294AB940EC
Core Payload DLL MD5: 422E4A3F1C69FF834DFC4688E8893716
#ThreatIntel #MalwareAnalysis #APT #Cybersecurity #Pakistan


🚨 #ThreatIntel: New cyber espionage campaign targeting #Kyrgyzstan 🇰🇬 organizations spotted on @anyrun_app sandbox.
The threat actors are utilizing a dual-file archive containing a benign lure PDF and a malicious executable.
Technical breakdown:
1. The Lure:
A PDF file named "Приложение.pdf" containing the official "Brief Statistical Handbook" from the National Statistical Committee of the #Kyrgyz Republic 🇰🇬. This indicates a highly targeted phishing campaign.
2. The Payload:
"Исправленная версия документа.exe" is a 64-bit Windows executable packed with PyInstaller and compiled using Python 3.13.
3. The Backdoor Code:
Decompilation of the core script (exec.pyc) reveals a lightweight HTTP reverse shell. It connects to a remote server, registers for a session token, and polls for system commands every 10 seconds via subprocess.Popen, sending results back via POST.
4. Infrastructure & Attribution:
The C2 server is located at 65.38.120[.]129:5556 (hosted by BL Networks in Romania). Based on the targeted nature of the lure and stealthy execution, this is a suspected APT activity.
Indicators of Compromise (IoCs):
* Malicious EXE MD5: 80fbb8ed636178d30b1a3a864cd1f231
* Decoy PDF MD5: 048de81368e46adf9dd12df7278f7821
* C2 IP: 65.38.120[.]129:5556
#MalwareAnalysis #APT #CyberSecurity
🚨 #ThreatIntel: Attack on Russian aerospace and electronics sectors ✈️🛰️
Recently, I found a highly suspicious EML file discovered in the @anyrun_app sandbox. The phishing email targeted a Russian manufacturer of semiconductor and electronic components.
While attribution is always tricky and I cannot state this as a hard fact, the operational tempo, targeting, and toolset heavily suggest a suspected Rare Werewolf (Librarian Ghouls) campaign.
🔍 Infection Chain:
1️⃣ Phishing email masquerades as a billing request from a legitimate Russian institute.
2️⃣ Attached is a password-protected RAR containing a PE32 payload disguised as a .com file.
3️⃣ The payload is a Smart Install Maker dropper. It executes curl.exe with the --resolve flag to bypass DNS filtering and download the next stage.
4️⃣ WinRAR extracts the payload (password: limpid29033).
5️⃣ Legitimate tools are abused: Tray Minimizer is used to hide a portable AnyDesk instance from the user for persistent, undetected remote access.
🛑 Indicators of Compromise (IOCs):
Domains:
aviatronika[.]online
vniir-avia[.]space
fgub-vniir[.]space
vniir-info[.]space
nova-stream[.]site
IP Addresses:
198.54.120[.]13
194.87.57[.]81
2.23.88[.]201
Hashes (MD5):
eabd440c996846d0992e37ab01d01208 (Dropper)
6cc3c68c56e099792fdeadde76256d56 (Payload RAR)
#InfoSec #CyberSecurity #Phishing #RareWerewolf #LibrarianGhouls #Malware #APT
Askar Dyussekeyev retweeted

A Chinese security company first detected a #SilverFox sample using the EDRchoker technique in May 2026.
ctfiot.com/311213.html (Chinese)
According to reports, the technique was being used even before Zero Salarium publicly disclosed EDRchoker. zerosalarium.com/2026/06/edr…
More than 1,100 phishing domains and over 90 counterfeit software packages were reportedly identified.
@plebourhis @askardyuss
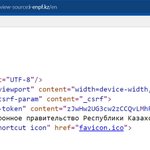
A #phishing domain impersonating the state pension fund of Kazakhstan (ENPF)🇰🇿 has been discovered.
Malicious domain: i-enpf[.]kz

I have deobfuscated the payload wt1 and uploaded it on VirusTotal.
format: corrupted pe32 (loaded manually by powershell script)
md5: bfd018cc79f039142843d6b31dfa9b98
detection rate: 0/70


'взвод розвідки.rar' seen from Ukraine @abuse_ch
CVE-2025-8088 exploit.
420f1931af9b3f7d02c5edfc78eb69abdad6e71d2c3e9b81f9cbc3823a503654
bazaar.abuse.ch/sample/420f1…

3
641
I have extracted the payload and uploaded it to VirusTotal.
md5: 41f9450bba235c37d40cd0315c1013cf
detection rate: 30/70
🚨 #ThreatIntel: A sophisticated phishing campaign targeting the Greek Military Representation to #NATO has been spotted in the @anyrun_app sandbox. The observed attack chain and infrastructure setup strongly suggest suspected #MustangPanda (#TA416) activity, though definitive attribution remains open.
The threat actors utilized a spoofed Montenegro diplomatic email, delivering a highly relevant lure regarding the Ankara Summit. The phishing link redirects through a fake Cloudflare check to a pixel-perfect Google Drive clone, dropping a malicious ZIP archive.
Execution relies on a hidden PowerShell script triggered by an LNK file. It uses data carving to extract a TAR archive from the ZIP, unpacks it using the native Windows tar.exe, and establishes persistence via DLL Side-Loading using a legitimate Canon binary (CNMNSST.exe) to decrypt a hidden payload.
Indicators of Compromise (IOCs)
Network Infrastructure:
▪️ resources.babyafrosapparel[.]com (Phishing Gate)
▪️ drive.babyafrosapparel[.]com (Fake Google Drive Delivery)
▪️ concreteinportland[.]com (C2 Server via HTTPS GET beacons)
Associated Cloudflare IPs:
▪️ 104.21.90.16
▪️ 172.67.151.3
MD5 Hashes:
▪️ B791C416988D068A3E548A0F21CD3518 (MNE_Readout_Alice_Rufo_Briefing_Ankara_Summit_22Jun2026.lnk)
▪️ c836a6bbe16354a21ee688e3eeb32d86 (CNCLID.dll - Malicious Proxy Loader)
▪️ e70a5908e5eaee1bcd15eef82b1bcfdd (Canon.dat - Encrypted Payload)
▪️ adb67ffe941a706b6343f94413f6e5f2 (CNMNSST.exe - Legitimate Canon Executable)
Email Artifacts:
▪️ Sender: stasa.stojkovic.mne@gmail[.]com
#ThreatIntel #Cybersecurity #MustangPanda #TA416 #MalwareAnalysis
@ccdcoe


🚨 #ThreatIntel: A sophisticated phishing campaign targeting the Greek Military Representation to #NATO has been spotted in the @anyrun_app sandbox. The observed attack chain and infrastructure setup strongly suggest suspected #MustangPanda (#TA416) activity, though definitive attribution remains open.
The threat actors utilized a spoofed Montenegro diplomatic email, delivering a highly relevant lure regarding the Ankara Summit. The phishing link redirects through a fake Cloudflare check to a pixel-perfect Google Drive clone, dropping a malicious ZIP archive.
Execution relies on a hidden PowerShell script triggered by an LNK file. It uses data carving to extract a TAR archive from the ZIP, unpacks it using the native Windows tar.exe, and establishes persistence via DLL Side-Loading using a legitimate Canon binary (CNMNSST.exe) to decrypt a hidden payload.
Indicators of Compromise (IOCs)
Network Infrastructure:
▪️ resources.babyafrosapparel[.]com (Phishing Gate)
▪️ drive.babyafrosapparel[.]com (Fake Google Drive Delivery)
▪️ concreteinportland[.]com (C2 Server via HTTPS GET beacons)
Associated Cloudflare IPs:
▪️ 104.21.90.16
▪️ 172.67.151.3
MD5 Hashes:
▪️ B791C416988D068A3E548A0F21CD3518 (MNE_Readout_Alice_Rufo_Briefing_Ankara_Summit_22Jun2026.lnk)
▪️ c836a6bbe16354a21ee688e3eeb32d86 (CNCLID.dll - Malicious Proxy Loader)
▪️ e70a5908e5eaee1bcd15eef82b1bcfdd (Canon.dat - Encrypted Payload)
▪️ adb67ffe941a706b6343f94413f6e5f2 (CNMNSST.exe - Legitimate Canon Executable)
Email Artifacts:
▪️ Sender: stasa.stojkovic.mne@gmail[.]com
#ThreatIntel #Cybersecurity #MustangPanda #TA416 #MalwareAnalysis
@ccdcoe


The domain keden-kgd-gov[.]kz has been suspended by KazNIC.
I have found a phishing domain keden-kgd-gov[.]kz impersonating the KEDEN information system used for customs clearance in Kazakhstan.
#CyberSecurity #Phishing #ThreatIntel

5
963
#ThreatIntel: A highly targeted spear-phishing campaign against Turkish defense giant Baykar Tech (#Bayraktar #UAV manufacturer) was discovered on @anyrun_app
The analyzed EML file reveals a critical case of #VendorEmailCompromise (VEC) and #SupplyChain hijacking. The attack originates from aviaventures[.]net, the legitimate domain of Avia Ventures (Baykar's official factory partner in Ukraine). Because SPF, DKIM, and DMARC checks passed perfectly, it confirms the attackers successfully compromised the partner's mail infrastructure to hijack ongoing business threads.
🔍 TECHNICAL DETAILS:
* The delivery vector is a password-protected ZIP archive hosted on LimeWire.
* Contains a heavily padded VBS downloader bloated to 6.14 MB to bypass automated sandbox size limits (often capped at 5 MB).
* Deploys a fileless PowerShell RAT establishing persistence via HKCU Run key disguised as "WindowsUpdateSync" in %APPDATA%\Microsoft\Vault.
🚨 IOCs:
* Compromised Domain: aviaventures[.]net
* Mail Server IP: 37[.]77[.]29[.]120
* C2 Stager URL: hxxp[:]//181[.]215[.]18[.]89/hurry[.]ps1
* Decoy PDF: hxxps[:]//filesdownloadsecurely[.]netlify[.]app/letter[.]pdf
* Downloader MD5: E030A7A1AE5685E62879D522F2DB2104
* RAT MD5: C0376786BD41F9851554000A15E5AB15
#MalwareAnalysis #Infosec #Cybersecurity

⚡️ Phishing Cyberattack Targeting Kazakhstan’s Intelligence Agency (KNB) 🇰🇿
🔍 A lookalike domain nab-gov[.]kz was recently registered (June 9, 2026). It mimics the old domain of the National Anti-Corruption Bureau, which was later reorganized under the KNB (National Security Committee).
🏢 The threat actors didn't lack audacity: they used the actual address of the KNB's Almaty branch (15 Zhibek Zholy Ave) in the WHOIS data. The clear targets are the KNB and/or its contractors.🎯
IOCs & Details:
🌐 Domain: nab-gov[.]kz
📅 Creation Date: 2026-06-09
👤 Registrant Name: Malik Askarov (likely spoofed)
🖥️ IP: 89.35.125[.]9
Stay vigilant!
#Cybersecurity #Phishing #OSINT #Infosec #Kazakhstan #KNB

🚨 #ThreatIntel: New cyber espionage campaign targeting Pakistan's defense sector (Ministry of Defence / Air Force) 🇵🇰
An @anyrun_app sample reveals a malicious ZIP archive leveraging a WinRAR Path Traversal vulnerability (CVE-2025-6218) with NTFS Alternate Data Streams (ADS). 🛡️⚠️
📦 Mechanics:
1. Victim opens a decoy invoice (Payment_Receipt.pdf).
2. Vulnerable extractor drops a hidden LNK via ADS traversal straight into the Startup folder.
3. The LNK executes obfuscated PowerShell to fetch a payload from docs[.]files-windows[.]top/j658K via Invoke-RestMethod. 🕸️
4. It masks the attack by launching Chrome to a legitimate Pakistani gov URL. 🕵️♂️
🔍 IoCs:
ZIP MD5: 563442c7538069cc5630fed7a947d826
LNK MD5: 49069ca3d2bd90d40660ca3bdc517bff
C2: docs.files-windows[.]top
#CTI #MalwareAnalysis #CVE20256218 #Infosec


