
kinda polymath person - only techy tweets here.
Texas, USA
Joined June 2015
- Tweets15.3K
- Following4.7K
- Followers569
- Likes42.5K





Augusto Bortoluzzi retweeted

Quad9's free 9.9.9.9 DNS resolver stops working for everyone in France on 24 November.
The Swiss non-profit lost a court case brought by beIN that orders it to block piracy-linked domains for French users. Rather than alter DNS answers, it is pulling out: "We categorically refuse to alter or lie to you about the DNS responses you receive."
Cloudflare warned on 17 Nov that a Belgian order now demands blocking through its own, Google's and Cisco's public resolvers by early January 2027.

Augusto Bortoluzzi retweeted
A root user inside a rented cloud VM could read the physical host's memory, including other customers' VMs, through a KVM bug on AMD servers.
Terra Security's Oren Yomtov used CVE-2026-99312, a nested-virtualization flaw that sat in the kernel for almost four years, to map about 127 GB of host RAM from an ordinary DigitalOcean droplet. On Terra's own AMD server, the VM also wrote 32 bytes into a live host kernel page.
On Hacker News, a commenter posting as KVM maintainer "bonzini" put it bluntly: "nested is the single biggest attack surface in the hypervisor."
The fix is in Linux 7.3.5, 6.18.64 and 6.12.118, and setting kvm_amd nested=0 closes the hole. Intel hosts are not affected.


Augusto Bortoluzzi retweeted

🚨 New attack bypasses Windows Hello and BitLocker security, cracking PINs in hours instead of months
Security researchers at TU Berlin have demonstrated a hardware attack dubbed "Hello Again" that bypasses TPM lockout protections, allowing attackers with physical access to repeatedly guess Windows Hello and BitLocker PINs.
The attack manipulates security counters stored in motherboard flash memory, reducing the estimated worst-case time to crack a 4-digit Windows Hello PIN from 69 days to just 40 hours. A 6-digit BitLocker PIN could be cracked in approximately 20 days instead of 19 years.
The vulnerabilities affect certain AMD and Intel-based systems. AMD has acknowledged one flaw as CVE-2026-43613 and is preparing firmware updates.
Researchers recommend longer PINs to reduce the risk.

ALT Attacker setup
Augusto Bortoluzzi retweeted

‼️ BREAKING: A 10-year-old flaw in #NGINX could let attackers execute code on servers — no login required.
Dubbed #nginx2root (CVE-2026-123007), the critical HTTP/2 vulnerability scores 9.2/10.
Public PoC available. Patches released.
Full details ↓ thehackernews.com/2026/11/10…

Augusto Bortoluzzi retweeted

‼️ UPDATE: Security firm Calif says it took over Jira, Confluence, Jenkins and Keycloak servers with Java4Shell, without even logging in.
The flaw sits in the code Java uses to decode Base64, a common way to send data as text. A short malformed string makes it write past the end of its memory.
Calif's researcher says OpenAI's Codex helped him find the bug in an hour and build a working exploit in two more, for under $200 in AI costs.
Oracle shipped a patch tonight. Calif is holding back its exploits until people have patched.


Augusto Bortoluzzi retweeted

An FPGA board plugged into an active Thunderbolt or M.2 port can patch your live RAM and unlock a locked Windows screen with any random password.
So how does Direct Memory Access (DMA) attacks bypass OS authentication? Well high-speed peripherals need fast data transfers, so modern laptops let PCIe devices read and write physical memory directly, bypassing the CPU and operating system permission checks.
Running open-source firmware like PCILeech on an FPGA card (such as a PCIe Screamer), an attacker connects to an exposed Thunderbolt port or an internal M.2 slot. The board registers as a standard PCIe endpoint and streams raw physical RAM over USB to another laptop. From there, PCILeech scans live memory for the Windows authentication library (msv1_0.dll inside winlogon.exe) and patches a single conditional jump instruction. Typing any random password at the lock screen then unlocks the desktop, leaving BitLocker volume keys and active sessions intact in memory.
Let me give you two settings stop this:
* Enable strict IOMMU (Intel VT-d or AMD-Vi) in BIOS so peripherals only access isolated memory buffers.
* Turn on Kernel DMA Protection, which blocks external PCIe tunneling while the screen is locked.
(Second image was enhanced with AI)
🤖 Made with AI


Augusto Bortoluzzi retweeted

Apple built Exclaves (🤌) with a microkernel, hardware isolation, and formal verification to prevent this ... or at least convince us they were trying to make spying harder.
Meanwhile, the sad reality: Apple's audio daemon just trusted the identity supplied by the app. 🫠
Meta's red team found an Apple bug that let iPhone and Mac apps record from the microphone even after the user denied permission.
The app forged an ID token to pose as Apple's own audio service, which then skipped the permission check.
On one iOS 27 beta, the orange mic dot never lit up, and the logs pinned the recording on Apple's service, not the app.
Apple fixed it in August with iOS 26.6.1 and macOS Tahoe 26.6.2. Its patch note calls it just "a logic issue."


Augusto Bortoluzzi retweeted
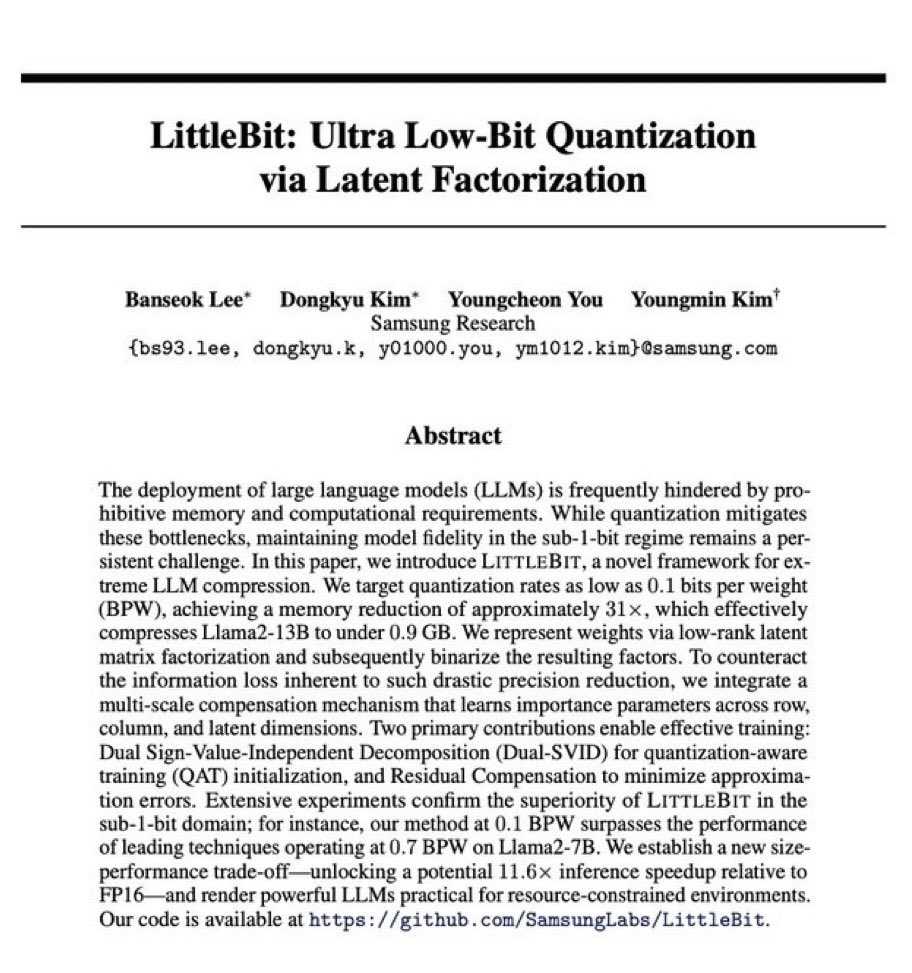
Samsung open-sourced a method that shrinks 13B parameter LLM into less than 1 GB.
The method is named "LittleBit"
Normally, AI weights are stored as regular numbers. LittleBit instead uses latent factorization to compress them below 1 bit each.
Some setups get all the way down to 0.1 bits per weight.
The architecture is where it gets wild.
Once a model is compressed this far, most of the math goes away.
LittleBit doesn't make the hardware grind through expensive floating-point multiplications. It runs the core computation with a simple bitwise XOR.
Heavy matrix math becomes simple sign flips.
What this means for deploying models:
• Up to 11.6x faster inference than standard FP16 models.
• Much less memory needed, and much less bandwidth to load the model.
• Holds up even below 0.5 bits, where older compression methods completely break down.
This is more than a smart optimization.
It's a roadmap for running huge, advanced AI locally on cheap, low-power hardware.
Augusto Bortoluzzi retweeted
‼️ Facebook's Android app read the photos, videos and metadata on Italian users' phones without specific consent. Italy's privacy watchdog has fined Meta €805M for it.
The feature suggests gallery shots to post. It was on by default, behind one vague, app-wide permission that, granted in full, lets the app read the entire photo library.
About 20 million Android users in Italy have had it since 2023.
Meta wanted Ireland's regulator to handle the case. The watchdog refused.
Meta has 60 days to switch it off by default and ask for consent separately.


Augusto Bortoluzzi retweeted

‼️ NoisyTCP: 11-Year-Old Linux Kernel Flaw Allows Attackers to Crash Servers Remotely
Details: cybersecuritynews.com/noisyt…
NoisyTCP is an 11-year-old Linux kernel bug. It lets a remote attacker crash a server without logging in.
The flaw is tracked as CVE-2026-99288. The flaw sits in the kernel’s TCP code, which handles almost all network traffic on Linux. Kim says it can be triggered against plain TCP listeners.
A server doesn’t need unusual settings, firewall rules, or special sockets. It only has to call listen() and receive packets from the attacker. That puts Nginx, Apache, and SSH servers in their default setups at risk, as well as proxies.
#cybersecuritynews #Linux

Augusto Bortoluzzi retweeted

这绝对是今年最让人拍案叫绝的硬件逆向神作:安全研究员 Kate 发现英伟达旗舰计算核心 GA100 芯片内部存在一个电压故障注入漏洞(Voltage Fault Injection),并亲手把一张当年矿潮遗留下来的阉割版 CMP 170HX 8GB 矿卡,原地解锁成了满血的 A100-80GB!
当年英伟达为了防止矿工抢占数据中心显卡,拿 GA100 大核心切出了 CMP 170HX 矿卡,不仅在硬件熔丝(Fuses)层面砍掉了显存容量、禁用了 NVLink 高速互联、把 PCIe 降到 Gen1,还锁死了张量计算吞吐。
Kate 顺着 GA100 上电启动读取板载熔丝配置寄存器的微妙时间窗口,用精密控制的电压毛刺(Voltage Glitching)去干扰芯片的熔丝传感放大器——让芯片在自检瞬间把原本烧断的限制熔丝全部误读为 0(未熔断状态),再配合重新植球焊满的高带宽显存,一举解开了英伟达在硅片层面的全部封印:不仅显存认满 81,920 MiB(80GB),连原本被阉割的 PCIe Gen4、NVLink、MIG 切分 也全数复活。
更离谱的是实测性能:因为英伟达在卖零售版 A100 时为了保证晶圆良率,统一锁在了 108 个流多处理器(SM);而这张被毛刺攻击彻底放飞自我的 GA100 核心,居然把晶圆上全部完好的 120 到 126 个 SM 单元 全点亮了,跑出来的真实算力比官方正版 A100 还要快出整整 1.2 倍。

Augusto Bortoluzzi retweeted
🚨 Hackers exploited Log4Shell in VMware vCenter to breach a Russian software developer.
BO Team gained root access, planted backdoors, and compromised its code-signing server—raising fears of a software supply chain attack.
Read: thehackernews.com/2026/11/bo…

Augusto Bortoluzzi retweeted
Meta's red team found an Apple bug that let iPhone and Mac apps record from the microphone even after the user denied permission.
The app forged an ID token to pose as Apple's own audio service, which then skipped the permission check.
On one iOS 27 beta, the orange mic dot never lit up, and the logs pinned the recording on Apple's service, not the app.
Apple fixed it in August with iOS 26.6.1 and macOS Tahoe 26.6.2. Its patch note calls it just "a logic issue."
Augusto Bortoluzzi retweeted
‼️ BREAKING - Trezor confirms hidden hardware implants in 3 'Safe 5 crypto wallets' sold by former reseller CryptoBilis.
The implants can steal recovery phrases and transmit them over mobile networks.
A firmware update won't undo earlier exposure.
Details ↓ thehackernews.com/2026/11/tr…

Augusto Bortoluzzi retweeted

any ladies out there disgusted by the jensen huang cheating allegations?
if you own an RTX 5070 or higher, it’s time to take a stand
sell that disgusting piece of hardware to me for $50
don’t let that man’s GPU sit in your house. know your worth ladies
Augusto Bortoluzzi retweeted
‼️ BREAKING - Critical Apache HTTP/2 flaw could allow unauthenticated remote code execution.
CVE-2026-119618 affects versions 2.4.55–2.4.70 with HTTP/2 enabled.
CVSS 9.8. Fixed in 2.4.71, but some #Linux distributions still await patches.
Read more → thehackernews.com/2026/11/cr…

Augusto Bortoluzzi retweeted
In November 2024, 404 Media reported that Detroit police circulated an internal warning claiming seized iPhones were mysteriously rebooting inside evidence lockers. Detectives theorized that newer iOS devices were communicating over a secret Bluetooth mesh to trigger remote reboots through Faraday cages.
Reverse engineer Dr. Jiska Classen audited the iOS 18.1 code and found the real trigger: Apple had added Inactivity Reboot. It does not rely on cellular, Wi-Fi, or Bluetooth state. It is an idle timer managed directly by the Secure Enclave Processor (SEP).
Mobile forensics centers on two states: After First Unlock (AFU) and Before First Unlock (BFU). Once you enter your passcode after boot, Apple's Data Protection architecture derives class encryption keys and caches them in memory so background tasks, calls, and notifications work. Forensic boxes like GrayKey and Cellebrite target this AFU state to exploit memory vulnerabilities or pull unencrypted caches.
Apple narrowed that exploitation window. When an iPhone stays locked for 72 hours, the SEP notifies the AppleSEPKeyStore kernel extension. The extension coordinates with user space to gracefully terminate SpringBoard and reboot. If any process attempts to block the reboot, the system triggers a kernel panic to force the restart anyway.
Rebooting into BFU does not make extraction impossible. Cellebrite and GrayKey can still pull unencrypted system logs and certain cached thumbnails in BFU. But sensitive user data protected by Class A, B, and C keys stays locked behind the Secure Enclave's anti-replay and rate-limiting hardware.
The forensic industry immediately adapted. By October 2026, 404 Media revealed leaked documentation showing Magnet Forensics developed GrayKey Preserve, a field device designed to freeze an iPhone's AFU state before the 72-hour clock runs out. Apple did not make forensic extraction impossible. It forced mobile forensics to race against an expiration timer.

Augusto Bortoluzzi retweeted

Recovering AES keys using power analysis: A hacker’s guide to power consumption side-channel attacks. 📟⚡📊 👩🏻💻🔑
More details on:
LinkedIn: lnkd.in/p/d6vyPuWk
Substack: it4sec.substack.com/p/recove…
Telegram: t.me/it4sec/104

Augusto Bortoluzzi retweeted

Motorola has announced their new high end flagship phone including upcoming official support for GrapheneOS as an OS option.
Motorola Signature 27 will be the first Motorola device supported by GrapheneOS. More devices will be supported in the future.
motorolanews.com/motorola-si…


