

Security Engineer - Tweets are my own.
Califórnia, USA
Joined September 2015
- Tweets1.9K
- Following1.8K
- Followers332
- Likes8.4K



Bruno Zanelato retweeted

🔴 CRITICAL · Linux kernel: 12 new CVEs
Worst (9.8): out-of-bounds read in Ceph snap trace bounds check (CVE-2026-99304)
👉 Fix: see advisories
cve.now/CVE-2026-99304?relea…


Bruno Zanelato retweeted

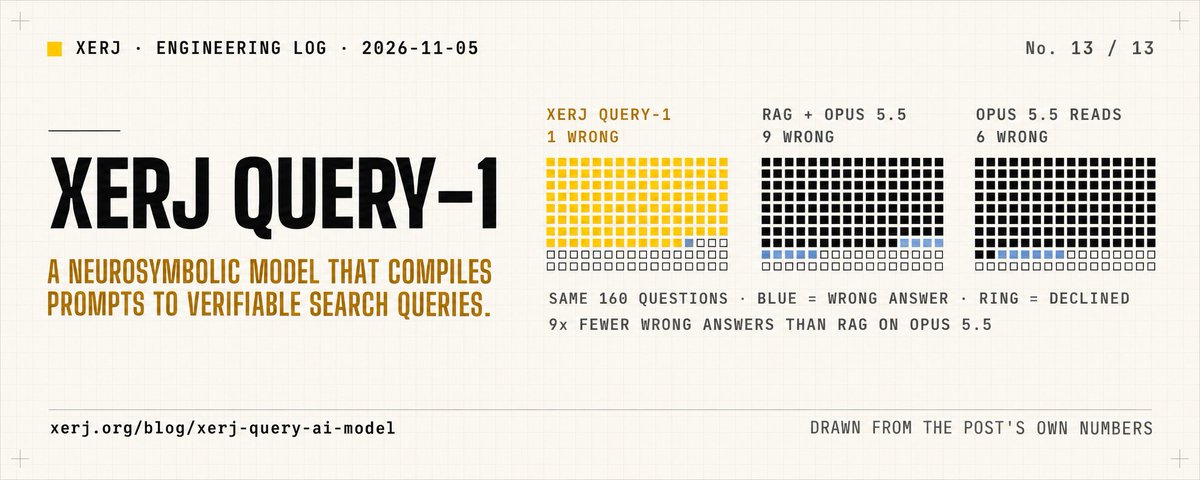
we built XERJ Query-1, an AI model that turns questions into programs on four CPU cores
ask about facts you've stored. Query-1 writes a short program, and XERJ runs it to get answer
you get answers faster, with the source records right there to check
here's what happens inside
→ Query-1 reads your question and the available records
→ writes steps to look up values, compare them or count
→ XERJ executes those steps
→ lookups return the records they used, and you can inspect the execution trace
you can see which facts it used and how it reached the result, without digging through the documents yourself
try it yourself by giving your agent this prompt:
> Install XERJ with the Query-1 model using xerj.org/llms.txt, write three facts about this project, and ask a question about them. Show me the program and the evidence it returns
full XERJ Query-1 breakdown ↓



Bruno Zanelato retweeted

The bug is like a joke.
On Alpine Linux, type 257 to 1024 characters of anything and you get root. 💀

‼️ BREAKING: OpenSSH has rushed out a fix for a critical flaw that lets attackers log into some Linux servers without the right password.
The team learned of the bug a day earlier. OpenSSH's Damien Miller says long embargoes now mostly help attackers, because AI agents rediscover bugs, sometimes within hours.
It hits Linux systems on the musl C library with PAM off, such as Alpine Linux. Miller told admins to disable password logins or SSH itself "IMMEDIATELY".
Version 10.6p2 works around it. Systems on glibc or PAM are not affected, and Miller says the root cause sits outside OpenSSH.


Bruno Zanelato retweeted

AWWWWOOOOOOOGAAAAAAA
9.8 severity use-after-free vulnerability in the kernel’s IPv4 TCP stack just landed
Time to patch!
ubuntu.com/security/CVE-2026…

Bruno Zanelato retweeted
‼️ UPDATE: Hacker "k0t" breached 924 more Fortinet firewalls than first known, Hudson Rock says.
They hold 40,573 cleartext secrets, including 1,576 Active Directory bind passwords.


Bruno Zanelato retweeted

Node2Shell PoC is now public.
CVE-2026-111497 — memory corruption in brotli 1.2.0 affecting Node.js 22/24/26, leading to RCE.
No execSync. No eval. No fake webhook.
The brotli decoder itself can reach system().
PoC:
github.com/syrex1013/CVE-202…
#Node2Shell #NodeJS #CVE #InfoSec

Bruno Zanelato retweeted

cve.now is on Twitter! Follow for critical updates: @cvedotnow


🔴 CVE-2026-107656 · Fortinet FortiSandbox
Fortinet FortiSandbox and FortiSandbox PaaS are affected by an authentication bypass flaw that lets an attacker reach protected functions through an alternate path. CVSS 9.6.
cve.now/CVE-2026-107656

Bruno Zanelato retweeted

CVE-2026-111497 goes well beyond Node.js.
The Brotli decoder flaw spans Bun, Python, .NET, Envoy, Istio, FFmpeg, ClickHouse, Apache Arrow and Ruby’s Brotli gem.
From HTTP responses to crafted images and compressed database files, the attack paths vary.
One vulnerable dependency. Multiple ecosystems. Different risks and patch timelines.

🚨 UPDATE: The Brotli flaw (CVE-2026-111497) goes beyond Node.js and web traffic.
• .NET: patched by Microsoft
• FFmpeg: hit via a crafted JPEG XL image
• ClickHouse: one request crashes it, fix not yet released
• Apache Arrow: no fix yet
Details ↓ thehackernews.com/2026/10/br…

