

Hey @bytecodevm (eleven red pandas 🐼🐼🐼🐼🐼🐼🐼🐼🐼🐼🐼), got any spicy bytecode / VM / language implementation / JIT / music
Bagnes, Switzerland
Joined November 2010
- Tweets46K
- Following841
- Followers2K
- Likes39.5K




eleven red pandas retweeted

卧槽,3090要可能要涨价了!!
因为老黄的刀法被人破解了
有人给3090解了个锁,同样限制在 360W,PyTorch 测试从 75 TFLOPS 跑到了 135 TFLOPS,提升约 80%!
你以为是超频,把功耗往上拉?
但他改的是显卡里控制运算速度的寄存器,这些寄存器平时有权限保护,正常改不了
他利用 GPU 启动固件的漏洞,赶在 NVIDIA 驱动加载之前拿到写入权限,把相关运算改成全速,再交给原版驱动使用
解开的主要是 FP16/BF16 输入、FP32 累加这类 AI 运算的速度限制 但测试算力多了 80%!!
4090 也有分支项目做到了:同类运算的指令吞吐,从约 165 TFLOPS 提升到 331 TFLOPS,接近翻倍
项目地址,附上👇
github.com/Zagitta/gpu-unloc…

eleven red pandas retweeted
Every Mac on macOS 27 now has a free LLM built into the Terminal.
No account. No API key. No internet. No token bill.
Setup (1 minute):
1. sudo fm license (enter your Mac password, one time)
2. fm available (checks the model is downloaded)
3. fm respond “your question”
Works on any Apple Silicon Mac, M1 included.
- Pipe files: cat notes.txt | fm respond -i “summarize this”
- Get JSON back: build a schema with fm schema object, pass it with --schema
- Local API: fm serve gives you an OpenAI-compatible endpoint on localhost
- Resume chats: sessions save to ~/.fm/sessions/
The limit is 4,096 tokens per session, and your prompt, instructions, and the answer all share it.
So skip code and math. Use it for summarizing, extracting, classifying, and rewriting.
Free, private, offline, and already on your Mac.


eleven red pandas retweeted

🚨 Critical Okta Access Gateway flaw allows administrators to execute system commands; CVE-2026-115547
The vulnerability affects the Okta Access Gateway Admin Console and carries a CVSS score of 9.1.
⠀
An authenticated administrator can submit specially formatted configuration values to execute commands within the context of the OAG service account.
Key details:
• Network exploitable
• Low attack complexity
• Administrative access required
• No user interaction required
• Affects OAG versions before 2026.10.2
⠀
Okta has resolved the vulnerability in Access Gateway 2026.10.2. Administrators should manually upgrade affected appliances.
Source:
trust.okta.com/security-advi…


eleven red pandas retweeted

For the next few days or weeks, anyone now has a root CA thanks to eMudhra. Time to have some fun with MiTMing unwilling devices!

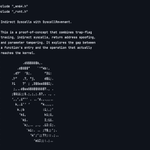
Clean indirect syscalls on Windows x64. It single-steps a hooked ntdll stub with the CPU trap flag to learn the live System Service Number and the syscall opcode, then jumps to that opcode with different arguments and a spoofed return address. The public proof of concept injects a calc.exe launcher into Notepad.
core-jmp.org/2026/10/syscall…
#DirectSyscalls #DoomSyscalls #EDR #EDRBypass #ETW #ETWThreatIntelligence #HalosGate #HellsGate #IndirectSyscalls #NTDLL #parametertampering #PEB #PEBWalking #ProcessInjection #returnaddressspoofing #RIPspoofing #ROR13 #si13nt #SilentisVox #SYSCALL #SyscallRevenant #SystemServiceNumber #SysWhispers #TartarusGate #TrapFlag #VectoredExceptionHandler #VEH #WindowsInternals


eleven red pandas retweeted

Kernel shellcode resources out there:
PLATINUMPICK: Windows KernelMode Shellcode Development Framework
github.com/winterknife/PLATI…
sickle-pdk: payload dev kit with a few ring 0 stubs
github.com/wetw0rk/sickle-pd…
No real generator exists for modern Windows. Guess we’ll have to build one

eleven red pandas retweeted
CVE-2026-81376: VS Code RCE via Security Feature Bypass; $4,000 bounty.
Write-up: samchen.blog/blog/vscode-nes…
CVE-2026-23866: Finding a Whatsapp NDay
core-jmp.org/2026/10/cve-202…
CVE-2026-23866 described incomplete validation of WhatsApp AI-rich Instagram Reel messages that could make another device fetch an arbitrary URL. numb3rs used only the public NVD text, grepped an iOS 25.9.72 IPA for AiRich, and proved a 1-click UIApplication.openURL path. The CVE’s automatic media sink was not reproduced; a 10 October edit points at LaTeX unifiedData image URLs.
#AIRich #Android #CVE202623866 #CWE20 #CWE601 #Frida #IDAPro #InputValidation #InstagramReels #iOS #MobileAppSecurity #nday #NdayResearch #numb3rs #protobuf #Swift #WhatsApp #whatsmeow

core-jmp.org/2026/10/followi…
STM32F401 Xbox One controller from “we have SWD” to a live CoreSight instruction trace. ETM and TPIU are programmed from OpenOCD, SWO is captured on PB3 with a hobbyist logic analyzer, and Ghidra explains why the first decode dies: the PLL moves the baud rate, then firmware steals the pin for I2C2.
#ARM #CoreSight #CortexM #DWT #ETM #FaultInjection #FirmwareAnalysis #FirmwareReverseEngineering #Ghidra #HardwareHacking #ITM #JTAG #logicanalyzer #MatthewAlt #OpenOCD #Pulseview #SerialWireOutput #STM32 #SVD #SWD #SWO #TPIU #VoidStarSecurity #wrongbaud #XboxOne


One go. One core, spin in the slot handler until zero. Windows times the command, not the slot: splitting 450 ms across that read is still one late completion. If slots chain, the hook runs again and adds time. Test got 450 ms back. Drop is one command held past the OS timer.
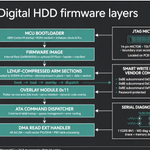
JTAG found the handler. Patch is a SMART 0xBE RAM write into loaded overlay 0x11. It lives until power-off. Fragile part is the host: ~450 ms on one core, once per slot of 40. Windows drops the disk on timeout. First sample 0 ms (cache). Xbox never saw it: stock lit the ring.
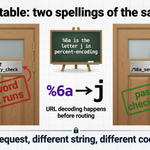
Cisco published CVE-2026-76504, a critical authentication bypass in Catalyst SD-WAN Manager. Landon Rice at VulnCheck showed that a single percent-encoded POST to /%6a_security_check plus a reserved Viptela username mints an admin JSESSIONID, because getRequestURI() does not decode while WildFly does. About 1,500 vManage consoles were internet-exposed; the bug was exploited as a zero-day.
core-jmp.org/2026/10/revenge…
#ATT&CKT1190 #AuthenticationBypass #Cisco #CiscoCatalystSDWAN #CVE #CVE202676504 #CWE177 #Envoy #getRequestURI #InitialAccess #JAAS #JSESSIONID #LandonRice #RBACBypass #SDWAN #SessionHijacking #URLencoding #Viptela #vManage #VulnCheck #WildFly #ZeroDay

Dumps WD and Samsung drive firmware, debugs a live HDD over JTAG, hot-patches overlay RAM to stall DMA READ EXT, then watches an Xbox 360 race start firing on unmodified stock firmware.
core-jmp.org/2026/10/hdd-fir…
#ATA #firmware #FirmwareAnalysis #FirmwareDumping #FirmwareHacking #grimdoomer #HDD #JTAG #LZHUF #Microcode #OpenOCD #overlaymodule #PC3000 #RyanMiceli #Samsung #servicearea #WesternDigital #Xbox360


Reverse Engineering a Ledger Nano X Hardware Implant
core-jmp.org/2026/10/reverse…
Reverse-engineered a real Ledger Nano X hardware implant for HARDWEAR.IO 2026 in Santa Clara. The add-on board does not break the Secure Element: it watches the OLED SPI bus, template-matches BIP-39 glyphs, stores the recovery seed at flash 0x7000, and sends it out over a Luat Air700E LTE modem with a Vodafone NL data eSIM. This article walks the 78-slide talk in source order and adds kitchen-table and operator notes.
#ATT&CKT1195 #ATT&CKT1200 #BIP39 #CryptocurrencyThreats #CWE1263 #eSIM #firmware #FirmwareReverseEngineering #hardwareimplant #hardwarewallet #Hardweario #JoeGrand #Kingpin #Ledger #LedgerNanoX #MalwareAnalysis #OLED #SecureElement #SPIBusSniffing #SupplyChainAttack #SupplyChainSecurity


