posting insights from my personal experience only | @zscdao member
reverse engineering tinder
Joined July 2025
- Tweets120
- Following25
- Followers488
- Likes781



cabbit retweeted
This is insane...
REA + Claude Opus 5.5 just made reverse engineering trivial — any closed-source app or device can be fully disassembled to the binary and rewritten on demand.
What used to take skilled reverse engineers weeks or months can now be done in hours, with full control over the result.
Closed source is officially dead.
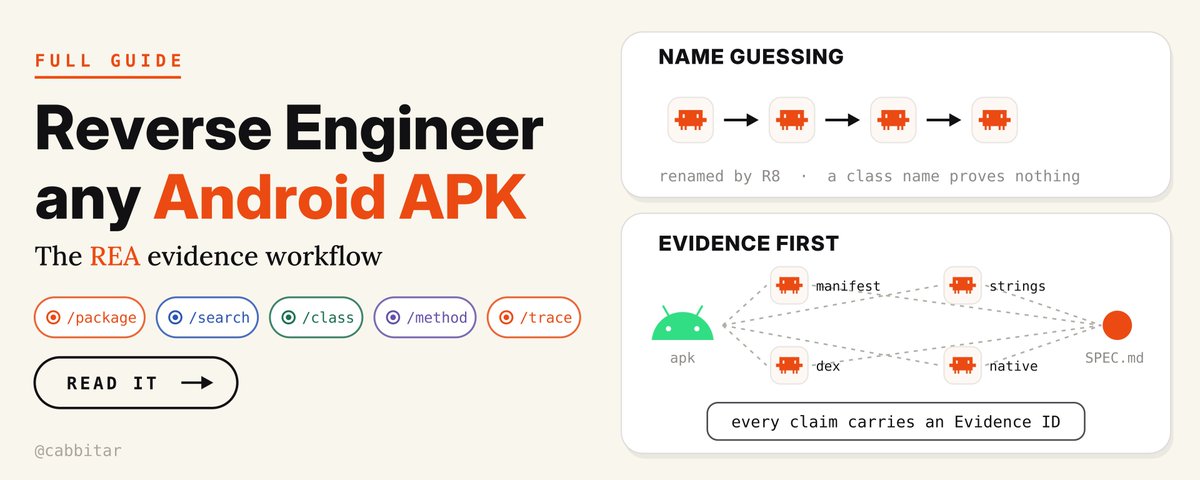
Send the article to Claude and get a full breakdown of how to reverse engineer any Android app.

cabbit retweeted
holy sh*t, someone just dropped the full prompt library for REA
github.com/JoasASantos/REA-P…
here's what it can do:
→ software cloning and game logic reconstruction
→ function tracking and binary analysis
→ porting to WASM
→ firmware, Android APK and kernel
→ Electron apps
→ vulnerability research, anti-cheat and DMA research for CTFs and security work
17 sections, swap the <placeholders> and run
every prompt forces the same rule: files, functions and addresses for every claim, confirmed facts kept apart from guesses
ask about one function at a time, the narrower the question, the more you can trust the answer
read the full REA guide in the article below ⭣
cabbit retweeted
REA + Opus 5.5 is scary f*cking dangerous...
Any closed-source device can now be reverse engineered.
Down to the binary, and you can modify it however you want.
Send this article to Claude and analyse how to rea any app for Android👇

cabbit retweeted
REA creator just released prompts that turn any AI agent into reverse-engineering lab
absurdly f*cking dangerous...
One paste it and your agents will:
• reverse engineer any paid app
• open Android, IPhone apps, Windows .exe and firmware
• take apart any app without its source code
• and that's just the start...
Send this to Claude Code, Codex or Cursor and thank me later.
Before you run it, read the article below: