

Founder & CTO of a digital asset hold co.
Joined July 2026
- Tweets1.2K
- Following510
- Followers445
- Likes1.1K




CollinCTO retweeted

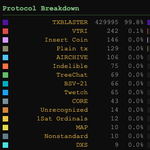
WE ARE APPROACHING 1 MILLION ON CHAIN TRANSACTIONS TUNE IN AND JOIN THE PARTY 100 FREE HITS twetch.com/g/frogfighter


Dust Hunt - Txn Blaster xitter.cf/i/broadcasts/1dxYlaEvz…

I guess InsertArcade.com has to do a tx blaster now that @twetch upped their game. I think we'll do a machine gun turrett type game, maybe a new type of Duck Hunt, where you drain our faucet instead of paying a penny to hit a frog. IDK we'll see. gg

I'm going to say it again for those who are only half listening. AI is going to run circles around humanity. We will be like cows. There will be no limits, including intent. You can deny it all you want, you will be proven wrong in real time and much sooner than you think.

This is the most serious 48 hours in cybersecurity history.
"Black October" they're calling it
It seems every *hour* there's a new incident, that in a typical year, would be one of the biggest incidents of the *entire year*
SUMMARY OF THE LAST 48 HOURS:
YEAR-LEVEL INCIDENTS (In a typical year, these would be among the biggest incidents of the year):
1. PHP2Shell: a hole in the software behind ~70% of websites. Governments took sites offline.
2. eMudhra: the master keys that prove websites are real were cracked. One was the number 4.
3. California: data on every public school student since 2023 stolen, including disability status
4. Railway: hackers stole customers' secret keys from a hosting platform used by millions of developers
5. Zeabur: 321,810 accounts breached. The company is shutting down.
6. LiteLLM: an AI tool downloaded 3.4 million times a day was poisoned with a password stealer
7. GitLab: a 10-out-of-10 severity hole in every version since 2014
8. Cairn: criminals used an AI hacking tool to break into 100+ companies
9. Ahold Delhaize: hackers knocked the owner of Food Lion and Stop & Shop offline
10. Onamae: malware planted on up to 26,739 customer servers in Japan
MONTH-LEVEL INCIDENTS (In a typical month, these would be among the biggest incidents):
11. Signal: a bug could leave your mic and camera on after you hang up
12. NGINX: 3 critical holes in software running ~1/3 of websites
13. HTTP/3: a single connection can crash 7 of the 10 web server types tested
14. Plex: hackers breaking into home media servers
15. SafePay ransomware: FBI warns it has hit 600+ critical infrastructure organizations
16. Palo Alto: ransomware gangs breaking in through company firewalls
17. Bullhorn: platform used by 10,000+ companies knocked offline
18. Medi-Cal: 970,000 patients' data stolen
19. WordPress: hackers stole a plugin maker's keys and used them to plant backdoors on websites
20. AOMEI: backup software's update server handed out a backdoor
21. Meta Muse: Meta's AI agent exposed users' personal and business secrets
22. Tor: 333 relays hijacked to steal logins
23. TiDB Cloud: database company's cloud breached
Also serious:
24. State Bank of India: India's biggest bank confirms a data breach
25. OVHcloud: hackers slipped a password stealer into a cloud company's official tool
26. Siemens: a software hole being used to spread malware
27. North Korea: state hackers launch a new attack campaign on South Korea


Just lowered all posting on trollbox (post, like, dislike) to $.001. Come troll us. InsertArcade.com
Nothing can stop what is coming. The internet has to have a trust layer. You already know what it is.

The flaws sat dormant for over a decade because turning the memory-handling issues into reliable unauthenticated RCE required an extremely complex chain of steps that was practically impossible for humans. Experts spotted related problems in a 2024 audit but found no concrete exploit path, so fixes stalled. In 2026, researchers used frontier AI models to analyze the code, generalize the patterns, and construct working exploits in days—what once took world-class teams months. Once details leaked, attackers could follow.


Jack Liu presented the concept of the BSV company; it stuck with me... We are all on the same team. I launch InsertArcade.com, @twetchapp launches games, leaderboard, and trollbox - we all win. We are one company, one asset - BSV. gg
Soon, we will perpetually live in an environment like this when AI starts running circles around us.

So basically, today PHP got two critical bugs that let anyone run code on your server without even logging in, which is bad, and then the details leaked before the patch was even out, which is worse, and it works on WordPress and MediaWiki and Magento and Joomla and Laravel, and Censys says like 1.5 million servers are running a version with no fix, so the NSA was like "take your system offline," and the FBI was like "take your system offline," and CISA and the UK and CERT-EU were all like "take your system offline," and then the Prime Minister of Japan, the actual Prime Minister, posted at 5:55 in the morning telling 48.8 million people to take their system offline, so everyone took their system offline, like the Dutch cybersecurity agency took its own website offline, and the Dutch parliament went offline, and the Port of Rotterdam went offline, and Finland and France and Denmark started pulling government sites, and Wikipedia went down, and Archive.org went down, and Asana and GOG and Something Awful went down, and the University of Vienna's webmail went down for some reason, and that's just PHP. Because GitLab also dropped a CVSS 10.0, which is the highest score they give out, for a bug that's been there since 2014, so that's every self-hosted GitLab for twelve years, and then LiteLLM 1.107.0 got hijacked and shipped a credential stealer and a remote access trojan in every single wheel and the Docker images, including latest, and you didn't even have to import it, just installing it was enough, and it's the second time this year, and then Railway paused every deployment on the entire platform because someone got into the environment variables, so now everyone has to rotate every secret they've ever stored there, and TiDB Cloud said someone was walking around inside with stolen credentials for basically a month and an extortion group says they took 10.6 terabytes, and Zeabur got breached for the second time in two months and is just shutting down, like the whole company, and Node.js patched remote code execution and a TLS bypass, and CISA says Plex is being actively exploited, and someone took over 300 Tor exit relays to steal SSH passwords, and SafePay ransomware has hit over 600 critical infrastructure orgs, and India's biggest bank filed a data loss incident, and Japan has been in an official state of emergency in cyberspace since October 9, which honestly explains the 5:55 AM post. Oh, and eMudhra, a certificate authority that's issued over 60 million certificates, whose entire job is proving websites are who they say they are, was supposed to be using private keys that are random numbers over a hundred digits long, and one of them was 4. Just 4. And the others were like 66 and 237. Anyway, it's Wednesday.
Cows can't understand money, in the same way humans will not understand what AI is doing. We are in for very turbulent times cohabiting with superior intelligence. It only gets weirder from here.


Referral program coming soon :)
You can send anybody who doesn’t have BSV and wants some to insertarcade.com where they can earn 100 sats per point playing games from our faucet, and you earn off of every point they get, forever.
