

Freelancer. CSIRT. Incident Response. Threat Intelligence. Security, IDS, Linux, OpenBSD, Honeypots, Jazz, Literature, Modern Art. https://xitter.cf/t.co/D9bkiv10Sy
Europe / Belgium / Brugge
Joined January 2008
- Tweets11.1K
- Following1.8K
- Followers4.1K
- Likes1.1K






Koen Van Impe ☕ retweeted

Belgrade tonight: It looks like the Serbian people have had enough of Kremlin puppet Vučić.
xitter.cf/VladimirStev/status/19…
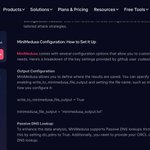
Hello, @socradar team. I understand that you’re desperately trying to make money and continually lowering your standards, but MiniMedusa is not a DDoS attack tool. Neither is my parser. Maybe spend some bucks on training your AI goons?


Koen Van Impe ☕ retweeted

Public Advisory 🚨: The National Security Operations Centre warns the public about a Chinese cyber-espionage group exploiting vulnerabilities in outdated Juniper routers, urging users to upgrade hardware, apply patches, and tighten access controls. #NetworkSecurity #NSOC


I created a small parser for Minimedusa (the MegaMedusa configuration, an L7 DDoS tool). It uses @teamcymru Whois, @circl_lu Passive DNS service and an RDNS lookup for enrichment. There's also a MISP JSON to import the feed in @MISPProject github.com/cudeso/tools/tree…


Did you know that since v3.0.0 of misp-modules and v3.0.1 of misp-docker/misp-modules it is possible to load custom misp-modules without building your own image? Just drop them in the corresponding /custom/ directory.
github.com/MISP/misp-docker/…
github.com/MISP/misp-docker/…

New publication by ANSSI: "Cyber Threat Overview 2024".
CERTFR-2025-CTI-004
cert.ssi.gouv.fr/uploads/CER…

Clever technique by UNC5792. Abusing the Signal “Linked Devices" feature, by replacing the code for an invite to a group with the code to link a new device to Signal. cloud.google.com/blog/topics…


Vulnerability in Billion Electric Router - Use of Hard-coded Credentials. vulnerability.circl.lu/vuln/… CVE-2025-1143 ; routers typically used in an industrial environment. #cve #ics

A clever technique to fool detection analysts: path masquerading to disguising malware as legit system files in SIEM logs. Unicode tricks make C:\Program Files\Windows Defender look real, hiding payloads in plain sight. zerosalarium.com/2025/01/pat… #siem #soc #monitoring


Reporting by AhnLab shows Kimsuky keeps relying on LNK malware in spear-phishing attacks, but also shifting to the use of RDP Wrapper and Proxy to remotely control the infected systems instead of installing backdoors. asec.ahnlab.com/en/86098/ IOCs: botvrij.eu/data/feed-osint/4…


Koen Van Impe ☕ retweeted

AIL Project v6.1 released with new features including unsafe filter for Tor crawling, many bugs fixed and Telegram attachment analysis
#darkweb #opensource #ail #threatintelligence #threatintel
ail-project.org/blog/2025/02…

ALT Tor hidden services crawled by AIL.
Agencies now released guidance on digital forensics & monitoring for edge devices to boost threat detection & incident response. ncsc.gov.uk/guidance/guidanc… #initialaccess #ir


Koen Van Impe ☕ retweeted

Malware Bible is now opensource: github.com/Perkins-Fund/Malc…
Feel free to make pull requests how you see fit, ilysm!

Google’s Threat Intelligence Group (GTIG) found that threat actors (mostly Iran, China and DPRK) using generative AI (Gemini) gain productivity but no novel capabilities. services.google.com/fh/files… #ai


If you’re using @letsencrypt certificates it becomes time to setup a certificate expiration monitor (if you haven’t done already).


