




Better start writing more efficient code. Or perhaps AI labs will finally hire some legitimate software engineers?

So the 41 datacenter moratoria across the country are, I predict, going to go 41-0. In nearly every case it's about 67-80% opposing datacenters. True in California, Ohio, everywhere. Read all the results here:
dashboard-production-c2fc.up…
1
2
67
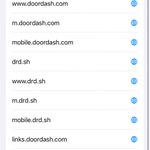
If you go to Settings > Screen Time > Apps & Websites > DoorDash
You see a reallly large list.
curl -k -i -A “Mozilla/5.0 (Macintosh; Intel Mac OS X 10_5_7)” https://…/.well-known/apple-app-site-association -o filename.json
Start with mobile.staging0.doorcrawl.co…

133
Remember earlier this year when Codex was writing 640TB of Write Ahead Logs? Now divide that down to writes per second. What would a missing set of logs indicate about your CPU and what causes that. Now think about the fact that most MacBooks have a corroded (undervolted) battery terminal 🙃

100
This would be a very large problem wrt county BoE’s transmitting their local voting machine’s to the state.

Scott Aaronson four days ago on the possibility that AI models will soon break widely used cryptographic systems, and on what responsible disclosure looks like when the parties who need to be notified are effectively the entire world.

1
1
111
Ruh roh. 1 year old MacBook Air battery terminal. Pretty sure that corrosion leads to under-voltage. Under-voltage means a random number generator is gonna be … not so random

121
Sweet. Closing my @PNCBank account first thing in the morning.

Ramaswamy has produced an attack ad weaponizing the rape of his opponent, Amy Acton, when she was 12 years old. It features Acton’s mother, who abandoned Acton after she was raped by her step-father, fleeing the state with her husband.
Here is the corporate money helping fund that ad.

1
4
112
That’s because a lot of people and companies are just sitting on known vulnerabilities after signing the researchers to NDA’s.

‼️ALERT - Two new unpatched CVSS 9.0 RCE flaws in #Linux's KSMBD SMB server were disclosed on public kernel mailing lists before fixes were ready.
One can be triggered WITHOUT authentication.
Neither has a mainline kernel fix.
Details here ↓ thehackernews.com/2026/10/tw…

1
106
@_webbwright hey Webb. Saw your article on agents and banking access. Just a suggestion but perhaps take a look at the sketchy as hell ToS and Privacy Policy of 1Password. They essentially say agents can access your passwords and they will give the AI co’s access to those logs
Would you all fucking listen to me now? Here’s a DoorDash employees blog + repo. I’m fucking begging somebody to read it closely and carefully
kevinmcox.com/2024/07/mdm-mi…
github.com/kevinmcox
gist.github.com/sickcodes/91…
gist.github.com/sickcodes
github.com/codeaashu/claude-…


In the last 24 hours:
1. iPhone 11 through 16 are apparently vulnerable to remote attacks.
2. SSL certificates are broken until browsers remove eMudhra CA.
3. PHP >9 vulnerability CVE published (tomorrow).
The world is about to witness things that have never been seen before.
Readers added context they thought people might want to know
The post's iPhone claim is inaccurate; a leaked Cellebrite forensic tool targets a Bluetooth bug patched in iOS 26.5 and does not affect updated devices. The eMudhra CA and PHP issues are real incidents but framed sensationally.
justin.sh/blog/2026/10/c…
blog.mozilla.org/security/2026/…
php.net
1
1
664


It’s actually worse. way fucking worse. Been tweeting about the source of this since September and trying to raise attention

It's worse than Heartbleed. it should be on the front page of every newspaper in the morning (but it wont be)
It's so weird living in a tech dominated world where everyone has a smartphone and is on the internet constantly..
..yet most people will never even hear about this.
130
My 14 year old nephew just showed me how on a JAMF managed Mac, within the first ~10 seconds of startup you can ask Siri to launch the App Store and arbitrarily install apps 🫠
2
214
They built this off of all the Azure hosted AI models Fortune 500 companies utilize. Read the mandatory “AI safety” filter ToS very very carefully 🤫

We now have state-of-the-art pre-trained base models in the 3T-parameter weight class, built entirely in-house at MAI.
Post-training results coming soon -- stay tuned!
Lots of details in our technical blog post.
microsoft.ai/news/frontier-p…

I feel really fucking stupid for believing Apple’s privacy shtick.
They were founded on “Good Artists Copy, Great Artists Steal”. Steve Wozniak loves practical jokes. The joke was selling you a “personal” computer
180+ known open Mac vulnerabilities attack.mitre.org/matrices/en…
@MikeIsaac ik u on well deserved vacation but here’s 180+ open vulns on Mac/ iOS. My other tweet thread has one example of how it’s used to high-jack a machine. Either I just left $120m of vulnerabilities on the table or there’s something fishy going on
1
129
When SIP is broken, which is shockingly common now, a malicious actor can ensure you run in a local hypervisor
This can be hidden on macOS with hv_vmm_present=0
github.com/sickcodes/docker-…
From there the malicious actor can use the 12+ year old DYLD_INSERT_LIBRARIES…

FYI, the reason Apple is doing this is because Codex breaks your devices SIP so it’s telemetry can survive system restores/ Apple Store DFU.
Turn on hidden files and go look around your disks Private directory.
developer.apple.com/news/?id…

1
11
1,491
When you take you MacBook or iPhone to the Apple Store to have them do a device reset, you assume it will clear all the previous settings including any nefarious network redirects.
My Mac is living proof that’s not the case and nobody has a good solution knowledgeisuserdata.medium.c…
