

147. RickettsiaN. Professor X. Healer. Senior Games Developer / DnB DJ Producer @one4sevendnb / openframeworks Games: Super Hexagon, Rumu, Pass Off
Sydney Australia
Joined August 2011
- Tweets6.4K
- Following2.3K
- Followers1.1K
- Likes17.9K







Danoli3 retweeted
Live webcast of Starship's 15th flight test starts now → xitter.gq/i/broadcasts/2brajgZlO…

Danoli3 retweeted

Bastiaan Olij explains what it's like receiving a flood of AI pull requests while working on the open source Godot engine.


Danoli3 retweeted
BREAKING: Estimated $5.7 billion stolen in hack of world's largest exchange Binance
Danoli3 retweeted

In lieu of flowers, memorial contributions may be made to:
Johns Hopkins Alzheimer’s Disease Research Center Fund
alzresearch.org/giving/
Alzheimer’s Foundation of America Caregiver Resources
alzfdn.org/donate/
Photo Credit: Tommy Garcia


Danoli3 retweeted

macOS Developers should update their /etc/ssl/cert.pem file to remove the compromised eMudhra certificate.
Apple has directions here: support.apple.com/en-us/1495…

Danoli3 retweeted

PSA for macOS users:
1. Apple’s supplied SSL certificate bundle at /etc/ssl/cert.pem still trusts certificates attackers can forge using compromised eMudhra keys.
2. I confirmed this on macOS 26.7.1 and 27.0.1 using Apple’s built-in curl and Git.
3. An attacker intercepting connections from tools using this bundle could replace downloads with malware. With commands like curl … | sh, that malware would execute immediately.
4. Removing the roots that authorize those certificates blocks the tested chains. Both OS updates restored roots I’d previously removed, requiring me to remove them again.
4. I’ve submitted the findings to Apple’s security team and am awaiting their response. In the meantime, you can apply a temporary fix as outlined below.
5. To check and fix your machine, give an agent like ChatGPT/Codex or Claude Code the following prompt:
“Independently verify whether Apple’s /etc/ssl/cert.pem still permits trust in certificates signed with compromised eMudhra keys. If so, back it up and remove the roots enabling that trust, identified by verified SPKI fingerprints. Confirm Apple’s built-in curl and Git reject those chains while ordinary HTTPS still works. Preserve rollback and never disable TLS verification.”
Note that removing these roots can also block legitimate sites. This is a temporary mitigation, not a substitute for a fix from Apple.
I’ll share the script I used in a follow-up post if you’d prefer to use that directly.

PSA for Codex CLI users:
1. Codex 0.163.0’s release lockfile pins rustls-webpki 0.103.15 and root bundles that can still trust compromised eMudhra certificates.
2. An attacker intercepting your connection could impersonate a server, steal sensitive data, or alter responses, potentially tricking Codex into running malicious commands.
3. Codex 0.164.0, released October 23 at 12:48 a.m. ET, updates those dependencies to fixed versions.
4. To check your codex version run "codex --version". It should be at least 0.164.0.
5. To patch the vulnerability, run "codex update".
6. Apps that bundle their own Codex copy must also be checked.
Danoli3 retweeted

⚠️🚨 THIS IS NOT A DRILL 🚨⚠️
Google has officially declared a bug in Brotli, its tool that shrinks web traffic, CRITICAL: 9.2 out of 10. Last night "Node2Shell" evolved into HTTP2SHELL.
A formal CVE record has been issued citing CVE-2026-111497 -- a hole in versions 1.0.3 to 1.2.0 that can hit any app unpacking data from strangers, and could let them take it over.
What this means:
▪️ This is not a Node.js problem anymore. This is an HTTP PROBLEM.
▪️ Every unpatched app across Node.js, Python, Bun, and Envoy that unpacks Brotli now has a hole attackers need no login to use
▪️ Istio. curl. Python's requests and httpx. All at risk under one CVE.
▪️ EVERY project that bundles Brotli must ship its own fix, and not all are out yet
This changes everything.
A normal bug can be fixed in one place.
A 9.2 bug inside a shared tool cannot.
We just entered the most dangerous phase of this crisis. If you're not paying attention - start now.
Save this. Share this. This is the moment it escalated beyond return.

Danoli3 retweeted

BREAKING: Albanese has been plotting against Helen Haines for the last five weeks because she criticised a $6 million grant to Albanese’s Marrickville Golf Club as “pork-barrelling by design”
Since then, Albanese has been on the attack. The day after her comments his staff gave a dirt sheet on Haines to journalists with a list of requests including:
-A list of Haines’ advocacy for projects in Indi of $1.8 billion then raising questions about the value for money and due diligence of those projects
***Asking journalists to check for personal or professional connections, donations, or undeclared benefits that might create conflicts*** framed as potential avenues to examine, not proven allegations…
Specific examples given included:
-Whether Haines had received undeclared wine or food from local businesses, held business interests, received political donations, or had personal associations with businesses that could benefit from tourism funding?
-For an $8 million Benalla Art Gallery redevelopment request, Albanese asked whether Haines had visited, been a member, donated, or had any personal professional connection with employees or the board?
-For a local recreation centre upgrade Albanese asked if Haines had played or trained with local clubs, watched games, or received jerseys/equipment?
-Made reference to her, and her spouse’s receipt of Mount Buller ski lift passes, alongside later requests for resort infrastructure funding
The document supplied no proof of undisclosed wrongdoing but Haines told the Daily Mail she had not seen it previously, and described the approach as “pretty desperate”
See how Albanese and Labor operate? See how the media play their part?

Danoli3 retweeted
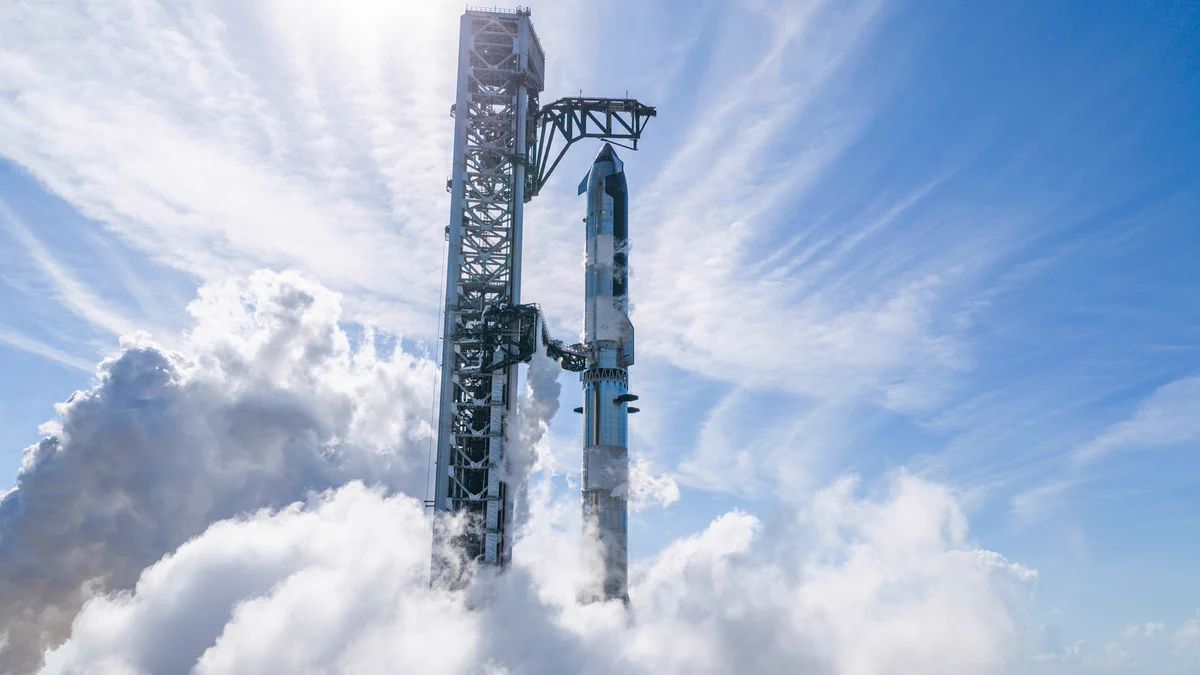
Starship’s 14th flight is set to launch on Monday, Sept 28. The 75-minute launch window opens at 7:15 a.m. CT. Live coverage of the mission starts ~35 minutes before launch → xitter.gq/i/broadcasts/1qxvvenMP…
Danoli3 retweeted

The 1995 cult film "Hackers" was released 31 years ago today. HackersDay.com
#Hackers #HackersDay #HackersMovie #HackThePlanet


Danoli3 retweeted

OpenSSL 4.0.2 Released with Important Security and Bug Fixes lxer.com/module/newswire/ext…


