
Building boxes, hunting bugs & earning bounties Pentester @cobalt_io | Maintainer @ExploitDB | Meetup Host @hackthebox_eu Ex: @offsectraining & @ThinkstCanary
India
Joined May 2019
- Tweets97
- Following154
- Followers353
- Likes2.5K



Pinned Tweet
Life is like a video game; sometimes all you need is a reset to conquer the next level!
1
3
607
deathflash ⚡️ retweeted

New writeup from @_specters_ and I: we're finally allowed to disclose a vulnerability reported to Kia which would've allowed an attacker to remotely control almost all vehicles made after 2013 using only the license plate.
Full disclosure:
samcurry.net/hacking-kia
deathflash ⚡️ retweeted

gaining access to anyones browser without them even visiting a website (CVE-2024-45489)
kibty.town/blog/arc/


deathflash ⚡️ retweeted

D'oh, so you leaked your AWS credentials 🤦♂️ Does it matter 𝐰𝐡𝐞𝐫𝐞?
It turns out there's a HUGE difference in how fast attackers will find them.
Idan Ben Ari deployed canary tokens (fake AWS credentials) using @ThinkstCanary to a number of different locations and analyzed:
- How quickly they were accessed.
- Where were they accessed from (IP).
- User agent, etc.
📊 Results
NPM: <1 min.
PyPI and GitHub: ~2 minutes
Pastebin ~1 hour
Web server ~2 days
DockerHub ~7 days
BitBucket and GitLab: …never.
cybenari.com/2024/08/whats-t…

deathflash ⚡️ retweeted
Just some personal thoughts on why you shouldn't force yourself to become a bug bounty hunter -
samcurry.net/dont-force-your…

Big thanks to @offsectraining's UGC program for kickstarting my journey! 🚀
- How it started: Built vulnerable machines, earned OSCP, and joined OffSec as a VM Engineer
- How it’s going: Still building & breaking boxes! 🔥
Grateful for the ride and excited for the future! 🙌

We are thrilled to celebrate the tremendous success of our UGC program and share some exciting milestones we have achieved along the way: offs.ec/4eO0HqU

1
1
252


deathflash ⚡️ retweeted

Decided to start an IoT hacking blog!
The blog will be featuring the best projects from my YouTube vids. First post details the reverse engineering of the VStarcam CB73 security camera.
brownfinesecurity.com/blog/v…
deathflash ⚡️ retweeted

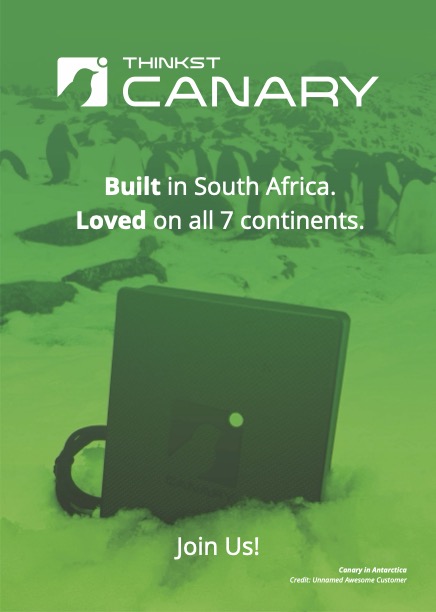
We slipped one of these in the bags at @BSidesJoburg this weekend because we are looking for amazing support engineers (to join our amazing support engineers).
"If you’re driven by a commitment to excellence with impeccable attention to detail, you need to join us"
Join us!

deathflash ⚡️ retweeted
On the nVidia blog:
“Defending AI Model Files from Unauthorized Access with Canaries”
💪💚✊️
developer.nvidia.com/blog/de…

I'm excited to be selected as a Subject Matter Expert by @hackthebox_eu, sharing insights to help over 2 million professionals learn and grow.
Thank you, HTB, for this incredible opportunity!
#Cybersecurity #HackTheBox

3
21
908

deathflash ⚡️ retweeted

After that excellent first Hacker Mixer, I am organising one more on 10th July (Wednesday) in Hyderabad.
Hackers in Hyd, go ahead and register.
lu.ma/y19prv4d

Been using @CaidoIO for a while now, and it's pretty cool! Wrote some workflows recently, it was super quick and easy. 👇🧵
github.com/osmsec/pimp-my-ca…
RequestTinter: workflow that applies color tints to in-scope HTTP requests, making it easier to identify them based on their respective methods.
github.com/osmsec/pimp-my-ca…

1
95
SecretSniffer: workflow designed to detect Secrets and API Key leaks in HTTP responses, leveraging regex patterns.
github.com/osmsec/pimp-my-ca…

1
115
