

IT-Security Consultant | Problem Solver | Father | Mastodon: https://xitter.cf/t.co/ZNMpwcZQ3y | Bluesky: https://xitter.cf/t.co/bNnR31nkOQ
Deutschland
Joined January 2010
- Tweets2.3K
- Following683
- Followers290
- Likes824





Denny Fischer retweeted

If you have Active Directory Certificate Services (ADCS) in your environment, run Locksmith now!
In Active Directory Security Assessments, we have found critical security issues in *most* ADCS configurations.
The great thing about Locksmith is that it doesn't just highlight the security issues in your ADCS environment, but also provides the command to remediate it!
If you're a pentester/red teamer, Locksmith is great for you to provide remediation recommendations to your customers.
github.com/jakehildreth/Lock…
#ActiveDirectorySecurityTip

Denny Fischer retweeted

This is so much! 🔥🔥😎
Found two new Potato triggers just today. Not only Potato but can also be used for LPE as remote auth is done which could be relayed to LDAP without Signing enabled. Or relayed to ADCS for a certificate.
github.com/warpnet/MS-RPC-Fu…


Denny Fischer retweeted

Today, TrustedSec is releasing #Specula (our previously internal framework) into the world, which will transform the Outlook email client into a beaconing C2 agent. @oddvarmoe and @freefirex2 walk through how to use Specula in our latest blog! hubs.la/Q02JfFFN0

Denny Fischer retweeted

ICYMI: @Jonas_B_K and I spoke about ADCS attack paths and #BloodHound at @WEareTROOPERS this week. You can find the full slide deck here: bit.ly/4csKVjc
The video recording will be shared here later: youtube.com/@TROOPERScon

Denny Fischer retweeted
Chat Control: Horse Trading While Nobody is Watching
After another shell game trick to make the massive attack on encryption in chat services appear otherwise, France's resistance is now wavering.
English:
ccc.de/en/updates/2024/chatk…
German:
ccc.de/de/updates/2024/chatk…

Denny Fischer retweeted
The Todos and basically everything can also be done later on from home or work as code snippets and descriptions are now publicly available here:
github.com/rtecCyberSec/Pack…
🙌🔥


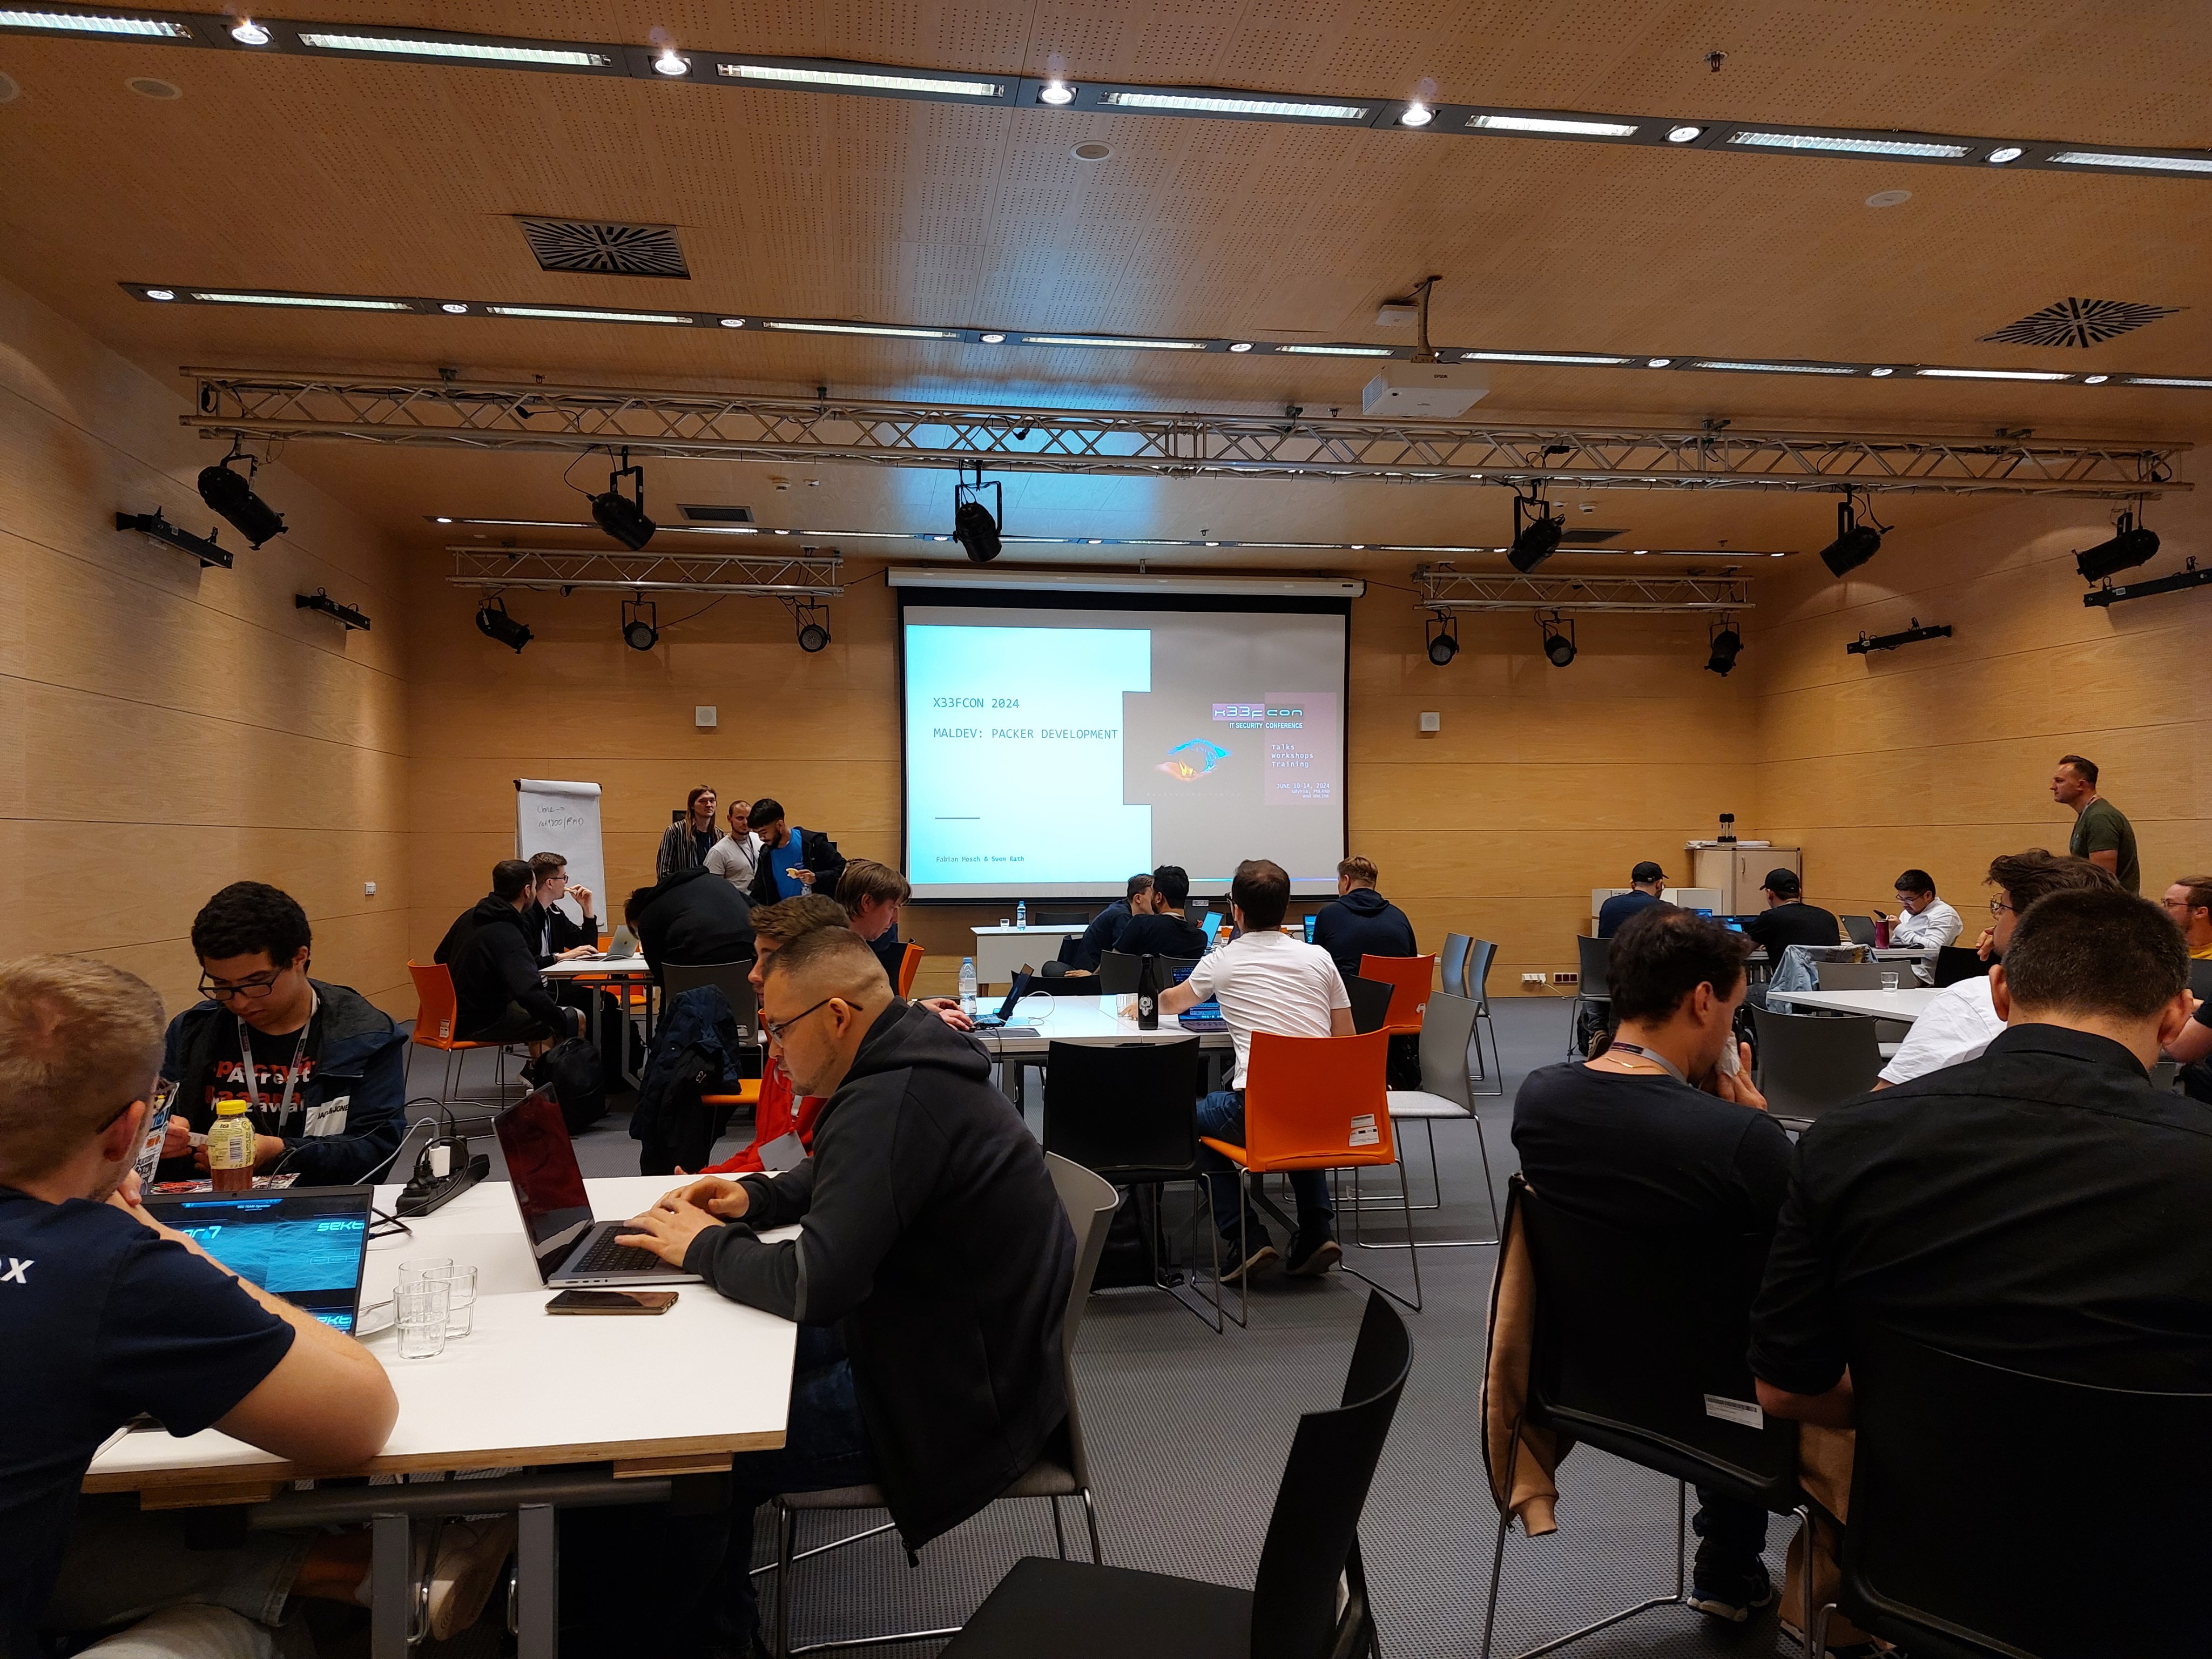
#Maldev - Packer Development is going strong in a #workshop at #x33fcon being taught by @ShitSecure and @eversinc33 - #redteam #blueteam

Denny Fischer retweeted
❗️#CERTWarnung❗️
In #Webex von Cisco wurde eine #Schwachstelle geschlossen, die den Abfluss von Metadaten und unautorisiertes Einwählen in Meetings ermöglichte. Das BSI empfiehlt Kunden Maßnahmen zu ergreifen.
bsi.bund.de/SharedDocs/Cyber…


Denny Fischer retweeted

I wrote a blogpost on injecting code into a PPL process on Windows 11, without abusing any vulnerable driver.
blog.slowerzs.net/posts/ppls…

Denny Fischer retweeted

Active Directory hardening blog post series, like a boss, by Jerry Devore. Posting this so I can reference it later!
Disabling NTLMv1 techcommunity.microsoft.com/…
Removing SMBv1 techcommunity.microsoft.com/…
Enforcing LDAP Signing -techcommunity.microsoft.com/…
Enforcing AES for Kerberos techcommunity.microsoft.com/…
Denny Fischer retweeted

New blog post is up... Identity Providers for RedTeamers. This follows my #SOCON2024 talk, and provides the technicals behind the presentation, looking at other IdP's and what techniques are effective beyond Okta. blog.xpnsec.com/identity-pro…

Denny Fischer retweeted
❗️#CERTWarnung❗️
Der Hersteller #Fortinet hat für zwei kritische #Schwachstellen in FortiOS Patches veröffentlicht. Eine der Schwachstellen wird wahrscheinlich bereits ausgenutzt. #PatchNow
bsi.bund.de/SharedDocs/Cyber…

Denny Fischer retweeted

Our important and timely blog on how to determine if your toothbrush is now part of a botnet.
malwarebytes.com/blog/awaren…

Denny Fischer retweeted

Airdrop doesn't use cryptographic salts, and rainbow tables are easily able to de-anonymize users
Nations like China are already taking advantage of this. Here's how it works:
1. Airdrop broadcasts a Bluetooth advertisement
2. Advertisement contains a partial hash of the sender's phone + email address
3. If the hashes in the recipients device match, they authenticate and allow file sharing.
Because they (can't) be salted, the SHA256 hashes of all possible phone numbers for a single nation are easily computable into a rainbow table only a few TB large. Then it's just a matter of looking up the hash to de-anonymize the original sender.
There is currently no way to prevent your phone number and email address from being leaked via Airdrop.

Denny Fischer retweeted

The first version of an SMTP smuggling scanner is now available at github.com/The-Login/SMTP-Sm….
More tools to come! Feedback is much appreciated!

Denny Fischer retweeted
The new year is almost here, don’t forget to add the following to your password cracking/spraying lists:
Spring2024
Spring2024!
Summer2024
Summer2024!
Winter2024
Winter2024!
Fall2024
Fall2024!
Password2024
Password2024!
Companyname2024
Companyname2024!
Denny Fischer retweeted
My talk “Playing Chess as Red Teams” from @MCTTP_Con got published now:
youtube.com/watch?v=XAvAVKXX…
🔥🙂
Denny Fischer retweeted

Unable to dump LSASS using the previous script? No problem, just ask S1 for a Live Kernel Dump instead! You can open this in windbg (and use mimilib.dll) and go from there.
gist.github.com/adamsvoboda/…


Ever find yourself on an endpoint with SentinelOne and have Local Admin? Just ask SentinelAgent.exe nicely, and it will dump a process for you, including itself!
gist.github.com/adamsvoboda/…
It bombs out on LSASS, but most other processes work.

