

I help invent the future. CTO @cloudflare. Angel investor.
Austin, TX
Joined April 2009
- Tweets5.9K
- Following2.2K
- Followers46.8K
- Likes10.8K



Dane Knecht 🦭 retweeted
overwhelmed by the php vulns and not sure how or where to get started?
we've added a copyable prompt to the cloudflare blog that you can feed your agent
blog.cloudflare.com/php-vuln…

Dane Knecht 🦭 retweeted

Dane Knecht 🦭 retweeted

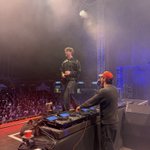
The last 24 hrs were very intense and some of the proudest moments I’ve been part of in a long time. Capped off by dancing with @TheChainsmokers and @tiesto at a region:earth party at the best baseball stadium on the planet. @Cloudflare FTW in so many ways. 🙏
Dane Knecht 🦭 retweeted

if you didn’t come to @Cloudflare connect you hate safe and secure internet

Dane Knecht 🦭 retweeted

Heading to SF to play a @Cloudflare party with our brother @tiesto


The best show on region: earth @Cloudflare connect
@TheChainsmokers


Dane Knecht 🦭 retweeted

Some stats on #php2shell. In the 10 hours before it was publicly announced, across the @Cloudflare network we saw thousands of attempts to exploit it. That jumped to tens of thousands in the 45 minutes post announcement, hundreds of thousands within 2 hours, and millions now.
Not intentional to leave @lcfr_hax out of my post. We appreciate what he has done and they are listed first in our blog post.

Dane Knecht 🦭 retweeted
Two classes extremely bad cyber vulnerabilities disclosed in the last 24 hours. The first potentially impacts everyone online. The second impacts nearly everyone running a server.
tl;dr: Everyone should upgrade their OS and Browser as soon as possible. If you run a server you should upgrade PHP (or ensure it’s removed if you’re not using it) as soon as possible.
The first class of vulnerabilities is a set of root TLS certificates that were discovered to have a trivial private key. Literally the number 4. These roots were controlled by #eMudhra. The problem is that with that an attacker could create a certificate and, if they could get in the traffic flow, intercept traffic to any site or service. The solution is to stop trusting certificates issued by these vulnerable roots. Upgrading your browser and OS is the fastest way for most Internet users to do this.
The second class of vulnerabilities doesn’t apply to most consumers directly, but does apply to most anyone running a server. These vulnerabilities have been dubbed #php2shell. PHP is one of the most widely used web programming languages. It’s estimated 70% of websites run on PHP. These vulnerabilities allow an attacker to send a crafted set of queries to a server running PHP and potentially take over the server. From there they could potentially read, modify, delete, or repurpose anything on the server. The solution is to upgrade PHP to the latest version ASAP. Even if you’re not using PHP for your web development, it’s often included by default. So make sure it is either upgraded or fully removed.
@Cloudflare received advanced warning of both of these classes of vulnerabilities. We’ve ensured that where we act as a proxy we are no longer trusting the vulnerable roots. We are also reviewing certificate transparency (CT) logs for any sign the vulnerability was exploited before its disclosure. We have not found any evidence but CT logs are not perfect and a sophisticated attacker who knew about the weakness could have exploited it without a new certificate being logged.
For the PHP vulnerabilities, we have deployed mitigations available for all customers for free. Because of the complexity of the vulnerabilities and number of ways it can be exploited, we also released new WAF capabilities that are unique in the industry to catch the exploit based on the response. These too are available for every Cloudflare customer for free.
Even if you are taking advantage of Cloudflare’s protection, it is important to upgrade your OS, browsers, and PHP installations as soon as possible. We can provide a strong bandaid, but the best protection is to fix the underlying problem.
If you’re interested in learning more, you can read our blogs:
Vulnerable roots: blog.cloudflare.com/emudhra-…
PHP vulnerabilities: blog.cloudflare.com/php-vuln…

Dane Knecht 🦭 retweeted

had to do nothing ;)


One-click mitigation for php2shell vulnerability:
If you have Cloudflare in front of your PHP website, please login to the dashboard and click this button to make sure you are protected.
dash.cloudflare.com/?to=/:ac…
This reduces your risk but doesn't fix the vulnerabilities in PHP. We recommend updating PHP to a patched version.

Dane Knecht 🦭 retweeted

Over the past two months, we have been leading a coalition to mitigate one of the most severe bugs in open source software found in recent memory, php2shell, found as part of our Patch the Planet initiative.
Credit to @OpenAI @wiz_io @ThePHPF for finding php2shell and running a responsible, coordinated disclosure.
This won't be the last one. Models will keep finding bugs like this in software everyone runs. Maintainers, researchers, providers and governments need a new shared playbook so the response scales with the findings and critical Internet infrastructure gets patched.
That's how we all help build a better Internet.
The Cloudflare's writeup on our php2shell response is up.
Rules went live at 03:02 UTC, about 9 hours before disclosure. Unfortunately the vulnerability leaked early, so we were already watching attackers mutate payloads against the rules and updating as variants appeared.
New rules keep landing in the WAF changelog.
Expect updates through out the day. We will have a more thorough post of what we had to build to better protect people coming shortly.
PHP runs almost 70% of websites. The flaw is in the runtime, so updating plugins won't fix it. Patch PHP.
blog.cloudflare.com/php-vuln…

Readers added context they thought people might want to know
php2shell vulnerabilities were discovered and reported by researchers including Calif (@lcfr_hax / Ryan at Calif.io), Wiz, and OpenAI; the PHP Foundation coordinated the patch and disclosure but did not find them.
blog.cloudflare.com/php-vulnerabil…
github.com/php/php-src/se…
calif.io/php2shell.x
wiz.io/blog/php2shell…
cve.org/CVERecord?id=C…
If you aren’t sure if you are protected for php2shell we are making it one click to check.
One-click mitigation for php2shell vulnerability:
If you have Cloudflare in front of your PHP website, please login to the dashboard and click this button to make sure you are protected.
dash.cloudflare.com/?to=/:ac…
This reduces your risk but doesn't fix the vulnerabilities in PHP. We recommend updating PHP to a patched version.
The new capability that we built to help defend php2shell is live.
The @Cloudflare WAF now has full transaction detection that evaluates the request and the origin response together, and response rules block a match before it reaches the requester.
Example from the post: unauthenticated hit on /admin that comes back 200 text/html. Block it. Auth failures and redirects can then pass through untouched.
blog.cloudflare.com/full-tra…

The Cloudflare's writeup on our php2shell response is up.
Rules went live at 03:02 UTC, about 9 hours before disclosure. Unfortunately the vulnerability leaked early, so we were already watching attackers mutate payloads against the rules and updating as variants appeared.
New rules keep landing in the WAF changelog.
Expect updates through out the day. We will have a more thorough post of what we had to build to better protect people coming shortly.
PHP runs almost 70% of websites. The flaw is in the runtime, so updating plugins won't fix it. Patch PHP.
blog.cloudflare.com/php-vuln…
PHP changes are live. Start patching. php.net/archive/2026.php#202…
Huge thanks to coordinated work by @ThePHPF!

PHP sites behind Cloudflare already have an initial set of WAF rules deployed for the known exploit vectors in these vulnerabilities. The rules are available to all customers, including free.
We are seeing early attacks emerging and are updating mitigations as new vectors show up.
This is a STOPGAP only. Patch as soon as @ThePHPF releases the update at 14:00 UTC today.