

digital entrepreneur since 1997 ≫ building a fintech in public ≫ co-founder @dolafycom
Floripa
Joined April 2009
- Tweets14.3K
- Following497
- Followers19.4K
- Likes12.5K





Pinned Tweet
7 months building a bootstrapped fintech
1) the hidden treasury
so far, we’ve been playing a game in which the end goal is to find that secret location
most of the assumptions we had about “where the money is” werent exactly right
Dolafy’s been profitable since our very first month live, mainly because we had a great network of digital entrepreneurs
but since then, we’ve been onboarding all kind of niches to actually understand who’s holding the map for the treasury
unfortunately, no podcasts, courses or friends could pin point where that location is
so we have to find it on our own
2) offboarding bad clients
during this exploration period, it was clear to us that some clients didnt really need our services
some were just shopping better fees with no real need for a long term relationship
others were trying to see if their fake ids would pass our detection system to run their schemes
plus the ones who promised millions and after a lot of support work ended up moving pennies
all those scenarios were really important to open our eyes about what works vs not
and now that we hit 300 clients onboarded, we have a much better sense of who they might be
3) not important/export
our biggest bet was on companies in need of paying suppliers all over the world - or getting paid in multiple currencies
i mean, there’s obviously a lot of money in the import and export world, and we wanted a small piece of it
but what we didnt realize is how troublesome these industries are, especially when trying to do banking for them
it’s a really hard client to move money for, with fierce competition and high compliance risks
if we had a proper banking license, which isnt the case, things would be much easier
but the current way this industry operates (SWIFT payments, mainly), it’s really hard for us to have a real impact
to do something that we would actually be proud of
so we stopped going after them and designing our product for these companies for now
4) digital marketers
that change gave us more space to decide the most scalable niche for Dolafy
(which could potentially guide us towards finding the hidden treasury faster)
so we decided to start focusing exactly on the niche our top 10 customers are: digital marketing
we have large accounts spending millions on ads every month with our cards
and then getting paid by platforms like google, shopify, etc
these marketers are great customers for us, not only because we speak the same digital language
but because we can actually improve a lot their experience, with our modern technology
we have the exact painkillers they need, and our competitors are doing a very bad job
so we decided to double down on media buyers, marketing agencies, marketplace owners, platform sellers etc…
i mean, i’m a digital entrepreneur myself, started making money online in 1997 (!!), so i know a thing or two about this world
maybe the treasury was right in front of our faces all this time?
5) partnerships
most players in the fintech space heard about us (“these 2 clowns and a bunch of robots built all this? no way!”)
and thanks to that, we now have an amazing list of partners to support us
companies that I personally admired for years, now their CEO is in my inbox helping us
Dolafy is formally connected to the main blockchains, yield projects, payments providers, digital banks, cards issuers, etc
and now that these important people are listening to us, we are actually able to do the changes our industry always needed
(we are launching soon the best onboarding experience that ever existed in the neobank space, thanks to that relationship with our partners)
very very excited for this one more month of @dolafycom live and all the changes it’ll bring to us
PS: if we find the treasury, there will be signs - stay tuned!

six months live. and Dolafy is skyrocketing.
1) over 200 clients live. onboarding 5 new businesses per day (from ~10 daily leads).
we haven't really nailed any distribution channel, and counterintuitively, signups keep happening non-stop
it really feels like a snowball effect. we started onboarding a few friends' businesses, they recommended others, and so on...
onboarding is still the slowest part of the process, but we are fighting really hard to make it as smooth as possible
how? with our AI agents and a whole new level of never-seen-before automation
2) Mark
when a customer onboards Dolafy, we now have 2 fantastic AI agents doing a really cool job for them
first Mark, our compliance agent, he starts screening clients as soon as they submit their docs
Mark reads everything and tries to understand whatever the customer uploaded/typed
(it takes around 15 minutes to check a business, from identifying if it really exists, if numbers make sense, to searching for adverse media related to the business and its owners - it's AMAZING to watch)
if not satisfied, Mark will request more docs/answers right away for the customers
when new docs are uploaded, it goes straight back to Mark, which will analyze them again
(Mark is ready to deal with hundreds of customers at the same time)
this is a really simplified explanation of his job, but there's a really complex compliance setup happening in the background, fully AI-driven and in-house built by myself
if any red flags are found, Mark opens a case for a human to analyze (hello!)
or if all good, with our approval, he sends the case to Helly, our onboard agent, and she'll take it from there
3) Helly
she decides what's the best bank for our client, depending on numerous factors like niche, incorporation country (and state, if in the US), etc
Crossriver Bank? JP Morgan? HSBC? Citi? Erebor? Banking Circle? Helly knows what's best for each client, and will open a virtual bank account there
partner bank asked for more docs? no problem, Helly will contact the customer right away and ask
after approved, she'll inform the client so they can finally start moving money crossborder
but the automation doesn't stop there. client needs to send/receive money from a different country?
they just click one button at our dashboard and Helly will get them a virtual account in that specific currency (EUR, AED, GBP, BRL, etc)
4) other robots
- Harmony: managing our marketing, editing landing pages, ads campaigns, email funnels, all through Slack
- Burd: news guy, he keeps us informed about everything that happens to any partners we use (for security, new products, etc)
- Casey: tracks our to-dos, if we miss any important task, she'll follow up with us next morning to make sure we don't miss it
- Dylan: our finance agent, not yet implemented, but he'll be in charge of invoices, expenses, revenue, etc
- Natalie: she's able to read and answer emails, interact on the live chat, and other support stuff
(she's not active yet, as we still like to talk directly to our customers at this stage)
5) ... and 2 humans
myself and my partner are the only not-so-AI managing Dolafy, a bootstrapped neobank
even though we are profitable and could hire someone, there's really no need right now
all tasks are being handled really really well by our team of agents, and whenever we see a task being repeated too often, we just automate it
2 persons will always be there, managing the 7 agents we have in place, and doing whatever tasks are still not replaceable by robots
(after all, fintech is a strictly regulated industry, and we still need to follow a bunch of AML rules)
but in my opinion, this is a huge shift on how businesses can be managed in 2026 - the true potential of AI at work
pretty cool right?
so yeah... stay tuned for more news about the first AI-first fintech ever built on planet earth!
PS: we now have a really cool office in Floripa! let us know if you are around and need an international bank you can trust for your business


I don’t take anyone seriously who says, “we’re building [something]”
in the super intelligence era, either your product is live or it isn’t
“building” is no longer a progress status
it’s just a bad idea that never became enough of a priority to finish
dolafy processed 103,949 credit card transactions
with a total of ZERO chargebacks/disputes
our filters to approve new customers
are the best ever created
gotta love this game
imagine running your business with European banks and their rules?
there’s zero reason to not have a US LLC with a US bank like Dolafy nowadays

Please retweet. @Wise has blindsided us and put our business at risk. This is insane.
We’ve been a Wise customer for years, using their USD bank account to accept payments from our US clients.
Today, I discovered that Wise has capped how much we can send or withdraw from our account at roughly 40% of our usual monthly volume.
No advance notice. No explanation.
We’re suddenly at risk of being unable to make payments on time.
Luckily, we have other accounts. Some clients also pay us in Bitcoin. But most of our money comes into Wise.
How can @Wise do this after we’ve been a customer for years and processed millions of dollars through it?
Customer support can’t help us. We’ve filed a complaint, but who knows if it will go anywhere.
In the meantime, we can’t get our money out. We’re being held hostage.
had a call today with @0xMarcB (CEO of @0xPolygon)
we discussed about a real problem that makes Brazil onchain operations less competitive:
there are too many BR Real stablecoins
without a real winner, volume gets too diluted, which means less liquidity and higher fees
when you think about US dollars, you know there’s basically USDT and USDC, and then newer ones like USDG and PYUSD
but when you need to convert them via blockchain to a Brazilian token, there’s no great option
it’s actually cheaper doing fiat FX operations than swapping onchain, which sucks
if anyone knows how to solve that problem, we’re all ears, would love to position Dolafy as a market maker at some point to contribute…
below the list of stablecoins we have in Brazil
BRLA (Avenia)
BRZ (Transfero)
BRLV (Crown)
BRLD (Liqi)
BBRL (Braza Bank)
BRL1 (Mercado Bitcoin, Bitso, Foxbit, Cainvest)
wBRL (Ripio)
BRLN (Núclea)
ABRL (AmFi)
BRLC (CloudWalk / InfinitePay)
BRLM (Minteo)
BRLm (Mento, formerly cREAL)
VRL (SmartPay)
BRD (BRD Digital)
BRS (Nora Finance)
BRLP (PagFinance)
BRLe (Brasil Bitcoin)
BRTH (TokenHaus)
tBRL (Tokeniza)
tBRL (Tenbin)
jBRL (Jarvis Network)
B3RL (B3 — pilot)
never trust a single AI model
whenever there’s a significant change to your code made by, let’s say, Claude
always ask for another model to review it (preferably a different company with a different training dataset)
just like doing a heart surgery, you might wanna hear more than one doctor first
this is the way to use AI: the more models you have access to, the less bugs you’ll introduce
PS: use herdr to make it easy for claude to deploy a codex review session and let them interact until the final status is SHIP

i've been running pentests at my fintech for the last 4 days
i'm mainly using open source uncensored AI (or abliterated if you want to get fancy)
models like glm-5.3, deepseek-v4.1-flash and others i'd rather not disclose
all I can tell you is: brace for impact
hackers can now deploy swarms of agents trying to hack the whole internet, fully automated
just like google spiders read the web to find sites for indexing on search, bots can now find vulnerabilities on anything that is plugged to the internet
i mean, sure, this always happened before - but they were using ready-made scripts for the process, kinda hit or miss, focusing on lame things
now, we have SI models investing a ton of energy on EACH and EVERY site they target, increasing exponentially the odds of finding open doors to exploit
if you ask me: is your fintech safe?
today, yes. i think so. i've improved everything i've found so far.
but tomorrow?
i'll be very honest: i have no idea
what if they hack my HOSTING PROVIDER tomorrow?
what if they hack 1password or aws security keys or infisical or github?
what if they hack the ISP I use to access the internet?
or even if they hack the police drones in my city and fly over my office to try to take us over via bluetooth connections?
it's very naive of anyone believing their systems are secure
you might feel safe today, until a new LLM model arrives and find gaps that didn't even exist before
i've been saying for months that, at some point, everything would become hackable
and I can assure you one thing: that point has been defined as Oct/2026
fasten your seat belts, the pilot went offline
everyone is always so late to building things
because they try to get ideas from social media
instead of connecting the dots internally
the answers to your life are already coded inside your brain
you only look for new answers if you are trying a totally new perspective that you haven’t experienced before in life
but keep in mind that will take years
and after learning all that, you shouldnt restart the search one more time, you should finally use what you learned:
by connecting the dots, internally.
and in the middle of all this chaos
neither Claude nor Codex will let me check the security of my own code
while hackers are living the dream with DeepSeek, Kimi, etc...


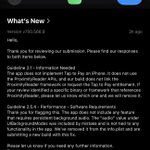
amazing. someone from eToro copy-pasted their App Store rejection message on the “What’s New” tab - and it actually got approved lol
apps.apple.com/ge/app/etoro-…


before, we used cloudflare to protect our servers from DDoS
now, we use cloudflare to protect our servers from AI exploits
ty @Cloudflare - you've been a great partner so far
right after posting this, i got a warning that nodejs was exploited
had to stop everything i was doing and patching it asap
craaaazy times
nodejs.org/en/blog/vulnerabi…

i used to run updates every month on my tech
then I moved to weekly updates
today, i'm basically running osv scanners, dependabot and checking for high priority patches every HOUR
also, before applying any package/library updates, my agents must check all signatures and updates on the code to avoid compromised ones
(we give a 7d cooldown period for some of them)
the way things are getting hacked, i'll probably need to check every minute if a new exploit might affect my system
and i'm not even joking...

Two critical vulnerabilities have been identified in PHP, a widely used programming language that powers websites and web applications. These vulnerabilities (CVE-2026-109618 and CVE-2026-109619) could allow malicious cyber actors to remotely execute code in PHP core, potentially compromising sensitive data and networks.
The FBI urges organizations to take the following steps now:
➡️ If an immediate update is not feasible it is recommended that organizations take the system offline until it can be fully mitigated.
➡️ Immediately update affected PHP installations following the guidance on php.net. Inventory where PHP runs in your environment, prioritizing internet-facing systems and vendor products that bundle PHP.
➡️ Monitor web servers for suspicious activity, including PHP processes unexpectedly launching command shells or downloading files. Ensure appropriate process-monitoring capabilities are in place to help identify potential exploitation.
➡️ If you find signs of compromise, isolate affected systems, preserve your web server and PHP logs, and report it to your local FBI field office or ic3.gov. Those reports help us identify the actors involved and warn other organizations before they become victims.
For the latest information, follow PHP’s announcement on php.net, CERT-EU Security Advisory 2026-018, and CISA’s Known Exploited Vulnerabilities catalog.

ALT Critical vulnerability alert for PHP Core with CVE-2026-109618 and CVE-2026-109619, CVSS score 9.2, urging immediate patch and threat hunting.
i remember in 2013 we had very similar protests in Sao Paulo to those that happened in Paris
my ex-girlfriend family had a shop downtown absolutely destroyed by the criminals
the protestors reason? bus tickets increase - which quickly expanded beyond transport costs into a massive wave of national discontent
history does not repeat itself identically, but human behavior, ambitions, and systemic pressures cause events to "rhyme" across different eras
chaos ignites natural selection, which removes the weak and forces the ones who survive to be stronger - on both sides -, making the world better balanced for the next century
grab your popcorn and moisturize your fingers, more entertainment is coming to your tiny screens

i was wondering what’s gonna happen if AI models go offline or bankrupt
systems would start crashing, engineers wouldn’t be able to patch issues
companies would need hundreds of employees again to catch up with all the (vibed) code
most saas created in the AI era would probably have to stop operating, coz the owner has no idea how their scripts work
we will be absolutely dependent on super intelligence by next year - SI leaders will control the world
got an email today from a partner's compliance team saying:
"Your organizational chart lists the same individual, Eduardo Borges, as CTO, CCO, CPO, and CMO. This seems to be a mistake. Could you please fix it and resubmit?"
i mean... where do i even start?
