




@_@ retweeted

I hold the browser manufacturers responsible for the eMudhra situation. They let some no talent a** clowns endanger all of humanity. Seems like they need some more competent oversight.


"Even the dumb people are smart enough to see it."

Immigration policy must be driven by the present, not the past, and business leaders are too terrified of the left AND the right to acknowledge this.
Recent H1B discourse revolves around a longstanding immigration sleight-of-hand. H1B proponents point to exceptional people who came here decades ago as if they represent the current state of the program in the same way that advocates for low-skill/illegal immigration point to very favorable immigrant crime/welfare/education/etc statistics that do, in truth, have them beating native-born Americans on many fronts.
It is all a sham. The world that created those statistics, people, and businesses no longer exists. Brilliant but desperate Vietnamese fathers who fled communism have nothing in common with young men from Honduras, and the crime rates/economic acccomplishments/integration of the former should not be used to justify mass migration of the latter.
Nor should the accomplishments of people who managed to get an H1B visa in the 90s (when the program was capped to just 65,000 visas) be used to justify staffing agencies and tech companies using the program to replace American jobs for less money. The obvious abuse going on is politically suicidal and something that even the most ardent supporters of the visa should want to crack down on, no immigration program can possibly survive the obvious and widely known reality of what is going on. I am a longtime outspoken advocate for stealing the best people from other countries to make our own better, runaway abuse of existing programs robs the government of the worker trust required to do so.
Lots of people in the tech space know this. Even the dumb people are smart enough to see it. Nobody actually believes these are all incredible people with unique talents performing jobs no American can. Everyone knows the guy in Cubicle Bay 7 doing mediocre but functional web design for half the salary of his American peers is no savant and doesn't meet the statutory requirements for his H-1B visa.
Unfortunately, most people with power or profile are terrified that any public statement or acknowledgement will get them attacked by the right (You guys have been screwing over American workers for years with visa abuse, you damn hypocrite!) or the left (You are racist, sexist, misogynist, and sucking up to this fascist administration!). Or, more likely, both. I know too many tech execs in particular who feel trapped, like the only winning move is to stay silent.
JD is blowing the whole thing wide open by putting facts and stats front and center that nobody wants to engage with. Critics will talk about anything and everything else but these damning facts and this obvious truth, that H1B visas serve neither their original purpose, legal purpose, invented purpose, or the American people.
@_@ retweeted

The big question being asked in cyber security circles right now?
"Was eMudhra intentionally keeping their keys within a small numerical range in order to keep them easy to exploit, so that they could then sell access to backend systems secured by eMudhra as a darkweb service?"
Everything is fraud or CVE on the internet. Fatigue.

@_@ retweeted

You've just sold the entire reason for having guns.
"I want to do violence to you, but I can't, because you're armed."
The violent thugs of the world are kept at bay by the possibility people can resist them.

@_@ retweeted
Go forth and open-source every IoT device in your house. Dump their comms. See what they're sending home.
God speed.
@_@ retweeted

the patch basically is the advisory at this point. once cloudflare is seeing attacks in the wild, holding the fix just means attackers know and defenders don't. was there any word on why they waited?

In which a Cuban anchor baby goes to India to promote more infinity Indians in America, calling Americans "stupid" and "dumb" in front of India in the process, absolutely eliminating any hopes he had of running for president.

In Mumbai, Indian External Affairs Minister @DrSJaishankar and I discussed energy security and defense cooperation while reaffirming the importance of advancing the U.S.-India strategic partnership.


I sent the same advice to clients 4 hours ago.

I pre-emptively disconnected ALL my sites / VPS servers from the web
I'll wait for the patch to hit at 2 PM UTC
If you have a PHP website, probably good to take them down until you patch PHP
69.3% of the web runs on PHP so this is going to be intense!
Good time maybe to buy cybersecurity stocks? (not financial advice)

@_@ retweeted

How on earth did this happen:
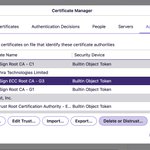
The Indian certificate authority (CA) eMudhra had one job (well, two):
1. Create secure, 384-bit private keys
2. Store these securely and do not leak them
Well, eMudhra chose private keys between 1 and 256 (the numbers!!) and called it a day. WTF


Yes. Today we did. All we had to do was put an incompetent 3-person Indian company in the shared trust pool to pollute and destroy everything.
Complete destruction. ☑️ Good job, internet.

@_@ retweeted

India’s lead “IT specialist” who had “over 15 years of experience” basically secured the network on half the devices in the world with the password equivalent of “123”.
This is the “elite human capital” that our IT industry can’t survive without.

@_@ retweeted

Gross incompetency from Indian certificate authority eMudhra.
You had one job: generate a 384 bit private keys and instead you used: 4, 56, 66, 115, 155, 156, 230, and 237.
This allows attackers to issue certificates for any websites.
Embarrassing that it’s a family business run by largely computer illiterate people. Only 1 of the 3 have a remotely computer-related background and even they never actually worked a technical job in their life. If you look at the LinkedIn, their tech team is young, from tier 3 education and paid sort of bottom barrel.
Imagine how many attacks you can design with AI given the existence of this genre of gross negligence.


