

agents agent @cloudflare. Tell me, what is it you plan to do with your one wild and precious life? 🌻
London
Joined November 2014
- Tweets2.8K
- Following2.2K
- Followers2.7K
- Likes39.9K



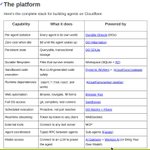


v2 is legit! For 2 months now it's the only surface that i connect across agent setups. I truly got it when I asked my agent to automate something w/ 4 google services that didn't have MCPs and it just said "oh let me write an app on executor for that" and it works perfectly!

And the agent docs are so good @RhysSullivan 👏 I was mildly worried about whether I'll need to store app code on github and figure out sync, turns out there's also code storage behind this : ) My agent and I were so happy
Naresh 🍓 retweeted

We asked GPT-6 Astra to edit Qwen3.5-0.8B weights to improve math.
It directly changed only 0.016% of weights, fixing 0.8B's reasoning loops & improving math up to 6x and even instruction following 3x, without gradients or training.
We call this Weight-Space Programming: frontier LLMs can now natively read/write neural network weights! 🧵
Blog: rikiyat.github.io/blog/weigh…

Readers added context they thought people might want to know
LLM was given weights explicitly as text in prompt and used code/forward passes (per authors' logs) to ablate Qwen looping direction, a known thinking-mode issue per model card. Primarily fixed repetition in that mode, not general 'natively' improving weights/math.
rikiyat.github.io/blog/weight-sp…
github.com/RikiyaT/lm_und…
huggingface.co/Qwen/Qwen3.5-0…
huggingface.co/RikiyaT/Qwen3.…
Naresh 🍓 retweeted

durable objects now defer code updates!!
you deploy, and for each object, we'll wait for work to complete before updating it with your new code
go follow @eth415 for more updates on durable objects — lot more coming to keep making them the best way to run long-running agents at scale

😴 rest easy - Durable Objects can now wait until they hibernate to apply code updates, giving long-running agent turns time to finish even if you're shipping PRs by the second.
developers.cloudflare.com/ch…

the impact of this change is unprecedented tbh


Naresh 🍓 retweeted

excited for @Cloudflare's debut as a frontier lab
#NothingButNET gang, assemble!


Naresh 🍓 retweeted

it took me building a shitty version of it to understand why pi durable is great. in essence it’s “just” way to serialize your session. that sounds straightforward until you try to do it yourself and realize there are tons of choices that if you get a single one wrong, you lock yourself out of building anything usable.

Naresh 🍓 retweeted

Today one of our Engineers at @amini_swiss built a showcase / explainer / demo for @CloudflareDev Durable Objects.
It's beautiful and therefore would love to share it with TPOT.
>> durable.ami.ni/
Naresh 🍓 retweeted
So cool!

Me and a band of plucky misfits (@maks_mak_0 and a few others), codename the Alertocats 🙀, have started rebuilding Cloudflare's whole notifications and alerting experience.
First up: a brand new UI. Find it in the dash at Observability → Alerts 👇
Naresh 🍓 retweeted

UI and math time! UI = f(props) is the most famous line in React. But that f is JavaScript, not math.
Inspired by @_chenglou’s Handwired project, I compiled a <Dashboard/> component into a real math function, and asked what becomes possible.
calculus-of-interfaces.verce…
Naresh 🍓 retweeted

cloudflare computer btw

Alright, Bdots are now called Coworkers
bdots was a terrible name
github.com/fayazara/coworker…
This is a very experimental project, I am still figuring out a ton of things as I build this (hence the delay).
This is not an official launch.
Here's a video of a bot that sends me a digest from multiple new sources I read, it sends me a message every morning at 7am and also I also asked it to create an app for me using Cloudflare dynamic workers (I feel this is the perfect use case for dynamic workers)
More on how coworkers work
A bot can be waked up by
1. You message
2. A routine (DO Alarms)
3. You email the bot [email protected] (CF email routing)
4. A webhook
5. Another bot
6. Someone edits a shared app.
Each bot has rules so they dont go wild
- Edit files
- Run commands
- Read the web
- Drive the browser
- Use connected apps (MCP servers)
- Message other bots
- Schedule routines
A bot can
- chat
- Use Computer (cloudflare/computer)
- Read the web (Kitesurf)
- Drive a browser, take over.
- Follow rules, Check in, Create routines.
- has isolate memory or if you explicitly mention - global memory.
- message other bots
- create apps
- can learn from you by looking at your browsing session (very rough still)
Architecture
- Each bot keeps everything in its own SQLite. There's no separate database.
- You sign in to an app once, on the hub. Every bot uses that connection.
- The worker only lets you reach your own hub and your own bots.
AI Gateway
- BYOK or use CF AIG unified billing.
- My demo is ugin - deepseek-v4.1-flash-1017 (its really good and surprisingly cheap)
Naresh 🍓 retweeted

For the past year, we've been working on Ship and we’re finally opening it up to everyone.
We think AI should give us more time for the people and things we care about, less talking to machines.
Our conviction is simple: in the future, everyone will have a personal intelligence by their side.
Try it for free ship.space
My fav interaction with personal agents was when my agent just spoke with @deathbyknowledg's agent for 2 days to report, fix and monitor a bug behind Ship itself! Removed the mundane work so my chats with Steve could just be about the stuff we love.
Go try @shipdotspace 🚀

For the past year, we've been working on Ship and we’re finally opening it up to everyone.
We think AI should give us more time for the people and things we care about, less talking to machines.
Our conviction is simple: in the future, everyone will have a personal intelligence by their side.
Try it for free ship.space
Naresh 🍓 retweeted

today we're launching @polylane for @Cloudflare
let proactive agents continously watch your workers, durable objects, workflows, etc.
they fix bugs, improve performance and handle all your alerts
we have this on our own prod account and we merge ~8 pull requests every day

Naresh 🍓 retweeted
Two classes extremely bad cyber vulnerabilities disclosed in the last 24 hours. The first potentially impacts everyone online. The second impacts nearly everyone running a server.
tl;dr: Everyone should upgrade their OS and Browser as soon as possible. If you run a server you should upgrade PHP (or ensure it’s removed if you’re not using it) as soon as possible.
The first class of vulnerabilities is a set of root TLS certificates that were discovered to have a trivial private key. Literally the number 4. These roots were controlled by #eMudhra. The problem is that with that an attacker could create a certificate and, if they could get in the traffic flow, intercept traffic to any site or service. The solution is to stop trusting certificates issued by these vulnerable roots. Upgrading your browser and OS is the fastest way for most Internet users to do this.
The second class of vulnerabilities doesn’t apply to most consumers directly, but does apply to most anyone running a server. These vulnerabilities have been dubbed #php2shell. PHP is one of the most widely used web programming languages. It’s estimated 70% of websites run on PHP. These vulnerabilities allow an attacker to send a crafted set of queries to a server running PHP and potentially take over the server. From there they could potentially read, modify, delete, or repurpose anything on the server. The solution is to upgrade PHP to the latest version ASAP. Even if you’re not using PHP for your web development, it’s often included by default. So make sure it is either upgraded or fully removed.
@Cloudflare received advanced warning of both of these classes of vulnerabilities. We’ve ensured that where we act as a proxy we are no longer trusting the vulnerable roots. We are also reviewing certificate transparency (CT) logs for any sign the vulnerability was exploited before its disclosure. We have not found any evidence but CT logs are not perfect and a sophisticated attacker who knew about the weakness could have exploited it without a new certificate being logged.
For the PHP vulnerabilities, we have deployed mitigations available for all customers for free. Because of the complexity of the vulnerabilities and number of ways it can be exploited, we also released new WAF capabilities that are unique in the industry to catch the exploit based on the response. These too are available for every Cloudflare customer for free.
Even if you are taking advantage of Cloudflare’s protection, it is important to upgrade your OS, browsers, and PHP installations as soon as possible. We can provide a strong bandaid, but the best protection is to fix the underlying problem.
If you’re interested in learning more, you can read our blogs:
Vulnerable roots: blog.cloudflare.com/emudhra-…
PHP vulnerabilities: blog.cloudflare.com/php-vuln…

Naresh 🍓 retweeted

Introducing tsrs: a Rust port of the TypeScript compiler 🦀
We are not forking TypeScript!
◆ In close collaborating with the TypeScript team
◆ Up to 8x faster than TS 7.0 & ~70% less memory
◆ Runs in WASM, so it works in your browser & on Workers
◆ Soon part of the Oxc toolchain
npx tsrs
blog.cloudflare.com/typescri…

Naresh 🍓 retweeted
Cloudflare MCP Server now supports step up auth.
Only give required scopes and then auth on demand as your agent performs a task
Available now in all supported MCP clients

Naresh 🍓 retweeted

a brand new model paradigm! introducing 𝚌𝚕𝚊𝚒𝚛𝚒𝚌: a system one model for extracting, computing, estimating, and predicting values from unstructured inputs.
blog.cloudflare.com/clairic-…
