
Security Researcher, System Programmer and Part-Time Garbage Collector
Austin, TX
Joined May 2009
- Tweets3.6K
- Following544
- Followers1.3K
- Likes466
Mohamed Saher retweeted

Austin hackers, let's gather for a night of lectures, libations, and BBQ on Wednesday June 5th. Thanks to our corporate sponsors tagged in the photo for fueling the evening. Limited capacity, register at: eventbrite.com/e/austin-hack… Looking forward to catching up with everyone.

Mohamed Saher retweeted
New blog entry: An Abstract Interpretation-Based Deobfuscation Plugin for Ghidra msreverseengineering.com/blo…
Sorry for the delay, honestly no. This specific one was targetting me personally amongst other similar attempts against my other accounts as well. Fortunately, I know the person behind these attacks. If I out him out and name him here, he's gonna lose a lot.
1
If you don’t know what a logical fallacy is, I would suggest you read about it first, then see what your advice suffer from. I can tell you’re an emotional person and over reaction is your first reaction. Feel free to get upset again and blame this on anything irrelevant again.
1
Elaborate on your first point. Correct me, on your second point. Third point, people have internet and as it’s already been paid for, you might as well use it.
I will simplify it. My criticism was for your advice and not related to the color of your audience, but for any audience in general. The lazy man approach being your advice itself, the illogical fallacies are the incorrect ways you base assumptions/conclusions on.
1
1
The lazy person approach and a common misconception, not to mention also being, not true. That was also a prime example of logical fallacies. How about developing a skill instead of paying money for a piece of paper? Knowledge is and will always be FREE.
@WindowsATP Your EULA (winatpregistration-prd.traff…) for Defender ATP has an invalid URL for the Copyright Infringement. This URL "microsoft.com/info/cpyrtInfr…" needs to end with "HTML" and not "HTM"
1
If you want the deobfuscated javascript, the decrypted payload and the email itself just send me a DM. [2/2]
1
A #phishing email using obfuscated #JavaScript and encrypted HTML with #AES targeting #Apple #iCloud email accounts. Here's the URL if anyone wants to analyze it (hxxp://cl.ly/427897542763/asnkjksansnsfa). [1/2]


Mohamed Saher retweeted

Translate x86_64 and ARM binaries to LLVM IR github.com/Microsoft/llvm-mc…

Mohamed Saher retweeted

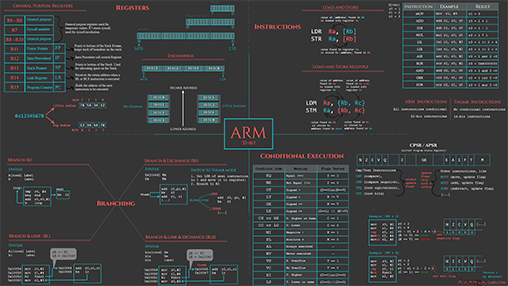
As I was laying in bed with a cold yesterday, I felt like I should use that time to create a cute little cheatsheet on ARM assembly basics for you guys. Enjoy! 🖤
azeria-labs.com/assembly-bas…
Mohamed Saher retweeted

My Metasploitable 3 CTF Start to Finish walk-through of all the challenges including CTF setup/prep, and alternative solutions: docs.google.com/document/d/1… (Now downloadable/printable/copy allowed)

Mohamed Saher retweeted

The world could use a full C/C++ example of MSFT's Antimalware Scan Interface (AMSI), so here's one that I used in my lab: goo.gl/72FjGr


Mohamed Saher retweeted

OMG, look what I got :-) Simply add a registry entry value (UAC free) on windows 10 1803, then we can make our vbscript or jscript files bypass AMSI PERMANENTLY! Isn't it so easy? or is it an Easter egg Microsoft left to us? :-( @tiraniddo @bohops @subTee @Oddvarmoe @domchell


Mohamed Saher retweeted

[DEMO] Recovering a PE with damaged headers with #PEsieve: youtube.com/watch?v=dFJcGYUF… (example: #PrincessLocker) - I am currently testing this feature, if you want to help in tests, pls check the "Latest builds": github.com/hasherezade/pe-si…

Mohamed Saher retweeted

Learn Verilog for #fpga by taking interactive exams in your browser wp.me/pk3lN-1mWS