

A security layer for an AI coding agent
San Francisco, CA
Joined August 2025
- Tweets157
- Following5
- Followers82
- Likes83




Cohere caught Alibaba Group's Qwen attempting to send data to a server in Beijing, right after the model said it wouldn't use external tools.
The security sandbox blocked the attempt, with no confirmed evidence of malicious intent.
But imagine this happening when an AI agent has access to your company's private repositories, credentials, and internal systems.
A clear reminder that AI agents cannot be expected to enforce their own security boundaries.
How are you enforcing company-wide security policies across your AI coding agents before they execute actions?
If you're not doing this yet, reach out to us at @hardenrun . We'd love to show you how to enforce custom policies across your organization and deploy them across your developers' machines.
Book a call with us at: harden.run/

1
68
A pretty solid week for Harden. 🏆
Here’s where we landed:
• #2 Product of the Day
• #5 Product of the Week
• #3 Product of the Week in the Artificial Intelligence category
• #4 Product of the Week in the Developer Tools category
• Featured on Product Hunt
• Featured in the Product Hunt newsletter
• 1,500+ followers
• 100K+ views on our launch video
At this point, we’re collecting Product Hunt badges like Pokémon.
A huge thank you to everyone who supported us, shared the launch, commented, tried Harden, and sent us feedback.
This was a big week for us, and we’re really happy to share the win with all of you. ❤️
@ProductHunt @rrhoover

Harden after outranking frontier companies 💀


🚨META JUST LOST TO 3 STARTUPS ON PRODUCT HUNT.
Muse by Meta launched yesterday and finished #5.
Mastra Factory: #1 → @mastra
Harden: #2 → @hardenrun
ChatGPT Images 2.5: #3
Noodle Seed: #4 → @Noodle_Seed
Muse by Meta: #5 → @muse
Meta has billions of users and basically unlimited distribution.
and somehow Muse finished one rank above “Ass Auction” 😭


#2 on @ProductHunt. Featured in their newsletter. And some love from @rrhoover.
Hell of a launch day 🔥

2
79
Kartik out here casually maximizing shareholder value 📈

You know who just got featured in the Product Hunt newsletter? 👀
They picked up “babysitting” for the subject line and made us a major headline today.
Great work lets keep pushing! 🚀
@hardenrun @JayVakil1

Security should not make you switch coding agents.
That is why Harden AIF works with the agents you already use: Claude Code, Codex, Cursor, Antigravity CLI, Kiro, Hermes, and OpenClaw.
You can try it free at: harden.run/
Using a different AI coding agent or workflow? Tell us what you use. We’re expanding compatibility and would love to build for it next.

1
5
294
Protection is foundational in financial services.
Harden is proud to join the Financial Institution Insurance Council, FIIC.
As AI changes how financial institutions build and operate software, security and control need to be built in from the start.
Learn more about FIIC: fiinsurancecouncil.com/

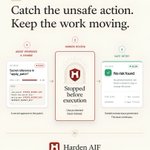
When Harden says “block,” it means that tool call will not run, but it does not mean the task is over.
AIF looks at what the agent is trying to do, the developer’s intent, and the context of the session. If the task is legitimate but the proposed call contains something unsafe, such as a secret pasted into a patch, AIF can rewrite the call safely by redacting the secret and preserving the intended work.
The creative below shows exactly that: the original call is stopped before execution, protected input replaces the exposed secret, and the agent can safely retry.
If an action goes beyond the developer’s approval, breaks an organization’s policy, or cannot be made safe, AIF blocks it. That is by design.
The goal is not to create more interruptions. It is to keep legitimate work moving while preventing unsafe actions from reaching your code, data, or environment.
AIF can allow a call, rewrite it safely, or block it when there is no safe path forward.
Harden AIF is free for individual developers. Try it at harden.run/

“Trust me bro, the agent knows what it’s doing” is not a security strategy.
One rogue tool call, a hallucinated instruction, or a small context mistake can become a real action in your codebase, credentials, or environment.
That is why Harden AIF sits between coding agents and the tools they use.
Before Harden AIF, tool calls can run unchecked. With Harden AIF, every supported call is checked before it runs. Safe actions continue, sensitive data can be redacted, and actions that go beyond the developer’s intent or a team’s policy are blocked.
Give your coding agents autonomy, not unchecked access.
Harden AIF runs locally and is free for individual developers: harden.run/

47
Introducing Harden Agentic Integrity Foundation (AIF), the unified security layer for AI coding agents
We believe the future of software engineering is long running agents taking on complex work while keeping your data, credentials, and critical secrets safe.
So we built AIF
→ Evaluates every action before execution
→ Uses developer intent and session context
→ Blocks unsafe actions or makes them safe
→ Runs locally and records every decision for audit
Whether you use Claude Code, Codex, Cursor, Antigravity, Kiro, OpenClaw, or Hermes, AIF works with the agents you already use.
AIF is not another dashboard or copilot. It is the security layer between your coding agent and the systems it can affect
Our post-trained model outperforms frontier models across critical agent-security benchmarks
AIF is free for individual developers: harden.run/?utm_source=twitt…
Need help getting started? Book a call, and our team would be more than happy to help you get set up: calendar.app.google/GdL3BvBu…
Learn more about AIF:
Docs: harden.run/docs?utm_source=t…
GitHub: github.com/hardenrun/aif/
1
207
You are not running one coding agent. You might be running two, three, sometimes more, all at once.
Claude Code for one project, Cursor for another, maybe Codex or Gemini CLI depending on the day, Kiro if you're deep in AWS. Each one has access to the same systems you do: your files, your credentials, your shell.
Harden AI Firewall analyzes every tool call before it executes, across all of them. One guard underneath whichever agent you're using that day, or all of them at once.
Core pre-execution secret-flow blocking is free for individual developers, no trial window, no credit card, no account.
Head to harden.run/#firewall-install, run the given command, and you're covered in seconds.
Want a walkthrough or have questions? Book a call: calendar.app.google/KZMj2iUG…

You're one developer, running an agent locally, and you already have secrets everywhere it can reach.
API keys, database creds, cloud tokens: sitting in your environment, your configs, your shell history.
Your agent doesn't ask permission to touch them. It just runs a command, and a secret can leak out through a log, an API call, a diff, before you even notice.

1
4
96
Most tools catch this after the request has already left your machine. By then it's too late to stop, only to report.
We built Harden AI Firewall to run locally instead.
Nothing leaves your device unchecked. The decision happens on your own machine, before execution, before any data goes anywhere.
You're not sending your code or secrets to a cloud service and hoping it catches the leak in time. You're stopping it at the source, on hardware you control.
1
2
42
AI agents don't get hacked with stolen passwords anymore.
They get hacked through the data they read. A log entry, an alert, a file. One bad instruction hidden in there, and an agent with real access can do real damage. That's the shift happening in security right now: it's not about the perimeter anymore, it's about what an agent does at the moment it acts.
Microsoft is now saying the same thing. This week they published their vision for agentic security, called Project Perception (lnkd.in/exU79v2s). Their own words: the physics of cybersecurity are changing, and defense has to happen at machine speed, not human review speed.
We'd agree with that. We just work one step earlier in the chain.
Harden is the security and governance layer for coding agents. Coding agents write more of your software every day, and they now run for hours without supervision. We cover both halves of that risk.
The AI Firewall sits inline while the agent works, parsing what it's about to execute and tracing where the data ends up before a single line runs. The Scanner picks up after, mapping your repo into a security graph and hunting the multi-hop attack paths legacy scanners miss, with the fix attached to every finding.
Before it runs, and after it ships. That's the layer we've been heads down on.

2
72
We just published our latest newsletter, and it captures one of the biggest weeks we have had as a team.
Inside this edition:
→ Harden AI Firewall is now live and free for individual developers. It watches every action a coding agent takes and stops the risky ones before they run.
→ We gave the AI Scanner a full redesign, with the focus on user experience. Applications, repos, scans, findings, and fixes now live in one clean workspace, so you can actually see what needs attention instead of hunting for it.
→ A recap of our week at Ai4 in Las Vegas, meeting developers and security leaders who are looking for a better way to run agents safely.
We have been pushing ourselves hard to get here, and there is a lot more coming.
Follow @hardenrun and subscribe to our newsletter to follow along as we build: harden.beehiiv.com/p/a-big-w…

Most "AI kills SaaS" takes miss the real problem.
Our founder @pushpp1440 is speaking at the ShoAIcase Series by Applied AI Association this Saturday to break down exactly what's failing when AI-generated apps hit Fortune 50 production.
Topic: SaaSpocalypse: Real or Hype?
📅 June 13, 2026
🕗 8:00 PM IST
🌐 Online
Register here: luma.com/pi72lvtj
#Harden #ShoAIcase #AAIA #AISecurity

51

Your internal teams are shipping AI-powered tools faster than your IT department can deploy them.
This is not a criticism. This is the reality at almost every enterprise we have spoken to.

1
1
19
We gave an LLM a 9-line random-search stub.
No solver logic. No domain knowledge. Just a seed and a scoring function.
Five rounds of contrastive feedback later, it wrote its own optimizer that matched or beat Optuna on 53 out of 55 benchmark problems. On 39 of those, it found the exact global minimum.
vizops.ai/blog/contraprompt-…

No human wrote any solver code. Same seed, same pipeline, every single problem.
For context: GEPA, the current state-of-the-art, achieves an 81.8% win+tie rate against Optuna. We hit 96.4% on the same problems, same budget, same LLM.
We also lose 5x less often. GEPA loses on 10 out of 55. We lose on 2.
1
25