





Pinned Tweet
Introducing kakuchi.app for Mac
50+ live widgets for your desktop, lock screen, menu bar and notch.
Can't find one? Describe it and it's built for you, using the Claude, ChatGPT or Antigravity plan you already pay for
50 apps, but still missing the one for all your widgets? kakuchi.app


1
27
The way I get X posts from my phone to my Mac is:
1. bookmarking them
2. opening them on my Mac
3. then removing the bookmark
please tell me there's a better way
2
2
110
You think you know what people will use your product for.
Turns out, your users are more creative with it than you are :)
Kakuchi.app

Happy Diwali to everyone celebrating! Check this out 🥳
virtualdiwali.vercel.app/

1
6
241

How did you come up with your product’s name?
I’ll go first.
Kakuchi means “every place” or “various places” in Japanese. my app lets you create pretty much any Mac widget and put it anywhere. seemed fitting :)
also, love Japan 🫰
Your turn 👀
New serious product for Diwali, have fun 🫰
xitter.gq/hm_arora/status/211914…

As promised, a serious product.
pagefighter.vercel.app/


thank me later, MacBook users
kakuchi.app


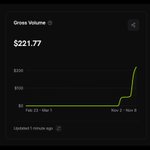
4 days later: $89.86 → $221.77
Still no big audience. Just showing up every day on Reddit and X.
Thank you to everyone who bought it, tried it, or shared feedback 🙏

It's really hard to sell a product without an audience.
First 2 weeks of trying to build one: $89.86 from kakuchi.app, live widgets for your Mac that you build by describing them

1
7
304
let’s connect 🤝
now that i’ve hopefully made it to your timeline, check out kakuchi.app
build custom Mac widgets just by describing what you want. notch, menu bar, pretty much anywhere :)
really excited about this one!
I waited for this statement, but it’s genuinely disappointing and unconvincing.
I empathized with @Railway when it was under attack a few days ago. That shouldn’t have happened, but companies grow and mature with time, and mistakes happen.
But this incident has malicious intent written all over it. Attacking a competitor and calling it “testing”, changing statements, and now seemingly throwing an employee under the bus.
The whole thing is sketchy, and this statement raises more questions than it answers.
Also, huge props to @joshmanders for the security they’ve built at @primcloud 🙌

Last night, I became aware of the concerns raised in Josh's post. I reached out publicly and over DM to offer a potential explanation based on the limited information available at the time, while working to understand what happened.
As background, we’ve internally been pushing 100% on security of the Railway platform. At Railway, we believe that cyber threats are real and mounting, and we’ve built out tooling for automatic scanning + CVE remediation (for both our infrastructure and customers). Over the last few weeks, oncall engineers were instructed to red team our infrastructure. We maintain specific policies and short lived grants for when these actions occur.
Subsequently, I became aware that an employee at Railway had constructed, on their own time, a tool for proactive identification + reporting of bug bounties within the broader community.
The employee, using their own personal accounts, personal credit card, and time outside of work hours, signed up for a personal subscription to a hosted service running Deepseek. I can confirm they ran this tool once and only once, on a singular external provider, and halted it proactively within 15 minutes of starting.
Railway does not condone these actions. We expect all our employees to uphold our standards of conduct, whether acting on behalf of Railway or in a personal capacity. We create an environment where internal red teaming has strict guidelines, and when bug bounty disclosures must occur, we follow every letter of responsible disclosure.
We have addressed this incident with the employee directly and have taken appropriate action. We are also reinforcing our expectations for employee conduct to help prevent similar situations.
Readers added context they thought people might want to know
Primcloud does not have a bug bounty program, per its founder. Its Acceptable Use Policy forbids unauthorized probing, scanning or vulnerability testing without prior written consent.
x.com/joshmanders/st…
primcloud.com/aup