
Passionate about all things cyber security. MITRE ATT&CK is my jam.
Joined July 2016
- Tweets3.9K
- Following1.2K
- Followers954
- Likes10.7K


Ivan Ninichuck retweeted

It's back to school time, and adversaries are taking advantage! If you support higher education or know someone who does, check out our blog on an email campaign targeting a university. Infrastructure pivoting suggests this could affect multiple orgs. redcanary.com/blog/email-acc…
Ivan Ninichuck retweeted

We'll be offering free virtual registration to ATT&CKCon 4.0 in the coming weeks, but would you like to join us Oct 24-25 in McLean, VA? Ticket sales start this Thursday, 8/3, at 12:30pm EDT/1630 UTC and will be $495. We'll be sharing the link here and on our other social media!
Ivan Ninichuck retweeted

Fucking love seeing my frens win. My brilliant friend @megan_roddie wrote a book!! Preordered, can’t wait to crack into this puppy.

Ivan Ninichuck retweeted

We've updated the Elastic Container Project to @elastic 8.9.0. Uses a shell script to deploy Elasticsearch, Kibana, and Fleet server. Useful for detection engineering tests, checking out malware capabilities, sandboxes, or other data analysis use cases. github.com/peasead/elastic-c…

Ivan Ninichuck retweeted
Evading EDR, by Matt Hand, gives an inside look look at how Endpoint Detection & Response agents pinpoint adversary activity. Learn the ways each sensor component collects data, how to design an EDR, & how to evade one. Pre-order at 30% off w/ code GOTCHA: nostarch.com/evading-edr

Ivan Ninichuck retweeted

✨detection-and-response-pipeline 🏗
A compilation of suggested tools/services for each component in a D&R pipeline, along with real-world examples. The purpose is to create a reference hub for designing effective threat detection and response pipelines.
github.com/0x4D31/detection-…

Ivan Ninichuck retweeted
.@redcanary recently helped create an expansion deck for Backdoors & Breaches! This is an awesome game to help learn incident response. Join my teammates plus @BanjoCrashland from @BHinfoSecurity at a webinar on July 13 to learn more! zoom.us/webinar/register/WN_…
Ivan Ninichuck retweeted

🚨I'm starting a new initiative where I share DFIR-related artifacts along with a short blog for context. My goal is to help ppl, especially newcomers, learn from real attacks.
More info in the resources below:
Repo: buff.ly/3NGf2J0
First blog: buff.ly/3NEWzwx
Ivan Ninichuck retweeted

There is a lot of hype around AI and cyber security, but what we really need is detail on specific use cases. I really enjoyed this latest @Mandiant blog that outlines specific examples where AI has helped (AND its limitations). mandiant.com/resources/blog/…

Ivan Ninichuck retweeted

Update on 'Azure AD Attack & Defense Playbook'. We (@Thomas_Live, @PitkarantaM & me) have added the updates on the AADSCA solution:
- Coverage of two new AAD endpoints: 'Default Settings' & 'Admin Consent Policy Settings'
- MS Sentinel integration (Playbook & Analytic rule)

Ivan Ninichuck retweeted
I think an "ATT&CK Mapper" role should exist. Where a person's sole job is to map rules to Att&ck. That shit is hard 😂
Ivan Ninichuck retweeted
I know a lot of excellent people are looking for jobs right now. We have several openings at @redcanary, including my peer, Senior Director of Detection Engineering, and a Threat Hunter on a team I lead. I hope you'll consider applying or sharing. redcanary.com/job-openings/

Ivan Ninichuck retweeted

📢 Exciting news! The Alissa Knight Archives YouTube channel is now open! 🚀 Explore a decade of hacking adventures in banking, healthcare, and connected car APIs, and more. Binge-watch captivating videos, keynote presentations, and guest appearances at youtube.com/@AlissaKnightArc…

Ivan Ninichuck retweeted

#Condifferently Girls Hack Village presents SquadCon is a 3 day conference focused on cybersecurity and inclusivity. Tickets are on sale now! eventbrite.com/e/girls-hack-… #girlshackvillage @girlshackvllg #hackersummercamp #foldingchair
Ivan Ninichuck retweeted

In my last few engagements, I have spent a heap of time in Defender for Office 365. If you use the product, or are evaluating it, or even interested in its capabilities, I can recommend this really well written security operations guide for it - learn.microsoft.com/en-us/mi…

Ivan Ninichuck retweeted
*AI-powered security investigation*
This is amazing! Take a look at the AI-powered capabilities in @chroniclesec Security Operations: cloud.google.com/blog/produc…

Ivan Ninichuck retweeted
ATT&CK's next release is once again coming on the perfect date, Tue April 25th. @_whatshisface and @jamieantisocial will be celebrating from @MITREcorp's #RSAC2023 booth, S-4438.
Come say hi, and chat about the new release next week! Booth schedule is at na.eventscloud.com/mitreatrs….
Ivan Ninichuck retweeted

"Google Cybersecurity Action Team Threat Horizons Report #6 Is Out!"
buff.ly/3UBleVP
<- our next report on cloud threats is out. Very fun stuff there .... because patching -)

Ivan Ninichuck retweeted

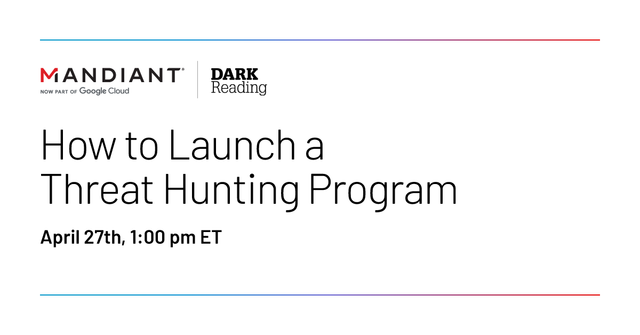
Are you looking to start a threat hunting program? Join Mandiant, now part of Google Cloud, for a webinar to get practical responses on how to get started and who to get involved - April 27th, 1:00 pm ET.
Register here: mndt.info/41hwV6o
#Cybersecurity #ThreatHunting
Ivan Ninichuck retweeted
It's rare to see reporting about an actor operating across on-premise and cloud environments - worth a read!

Microsoft detected a unique operation in which threat actors, tracked as MERCURY and DEV-1084, carried out destructive actions in both on-premises and cloud environments. Learn more about the observed activity and tools and get TTPs and protection info: msft.it/6019gGFEV