

Full-Time Bug Bounty | Christian | https://xitter.gq/t.co/lqwI4J261E
Joined November 2020
- Tweets657
- Following246
- Followers1.4K
- Likes2.1K




iQimpz retweeted

🚀 Introducing DeepInfer, our in-house inference framework, now fully open source!
Powering DeepSeek-V4.1-Flash at scale with high throughput and low latency. We’re sharing our production stack to help the community lower compute costs, reduce energy use, and make AI more affordable.
🔗 github.com/deepseek-ai/DeepI…
1/4

iQimpz retweeted

To teach a lesson,
After Wiz rushed to buy php2shell domain and use its marketing machine to steal the spotlight, I spotted "phpbleed" in a recent Calif tweet and bought phpbleed.com before wiz could pull the same stunt again.
A big budget can buy a domain. It shouldn't buy someone else's research credit.
If you have contacts at CISA or in the press, do the right thing: make sure the researchers who actually did the work get the recognition they deserve.
Hack the planet. Credit the researchers.

iQimpz retweeted

📄 Skills in Agent Harnesses
A lot of people don't know this (I didn't until recently) but most agent harnesses will load the description of your skill upon starting up your harness. This is how Claude Code works.
What people don't usually know is that even when you explicitly call a skill to be used inside of a harness, or the AI figures out to use a skill, it usually only does a read of the first 150 lines of the skill (to understand how to use it or if it applies to the work it's trying to do).
It's really important to outline a table in the first 150 lines of the mandatory parts of the skill that must be run when you invoke the skill.
If you make some type of mandatory instruction after 150 lines, it might get missed entirely. If you describe in prompting that you want to use a provided Python script or template, it also might be out of bounds of that 150 lines and never get called correctly.
If you write a table of contents of the skill actions in the first 150 lines and mark which ones are mandatory (or that, if the user has called the skill, you must read the whole skill context and all references), you get more reliable skills. We use markdown checklists for this now.
iQimpz retweeted

Two DGX Sparks, 33 Local Models, One Question: Can Local AI Actually Red Team?
betheadversary.com/posts/dgx…

iQimpz retweeted

We just let in every Pro and Max user from the Claude Code Projects waitlist!
If you're new to Claude Code Projects, here's a 4 minute walkthrough to get you started:
iQimpz retweeted
We’re rolling out monthly Claude Platform API credits for Max and Team plans:
Max 5x: $100
Max 20x: $200
Team: up to $500, pooled
Works on any model, including Haiku 5.5, in your code or third-party harnesses.
How it works and full terms: support.claude.com/en/articl…

iQimpz retweeted

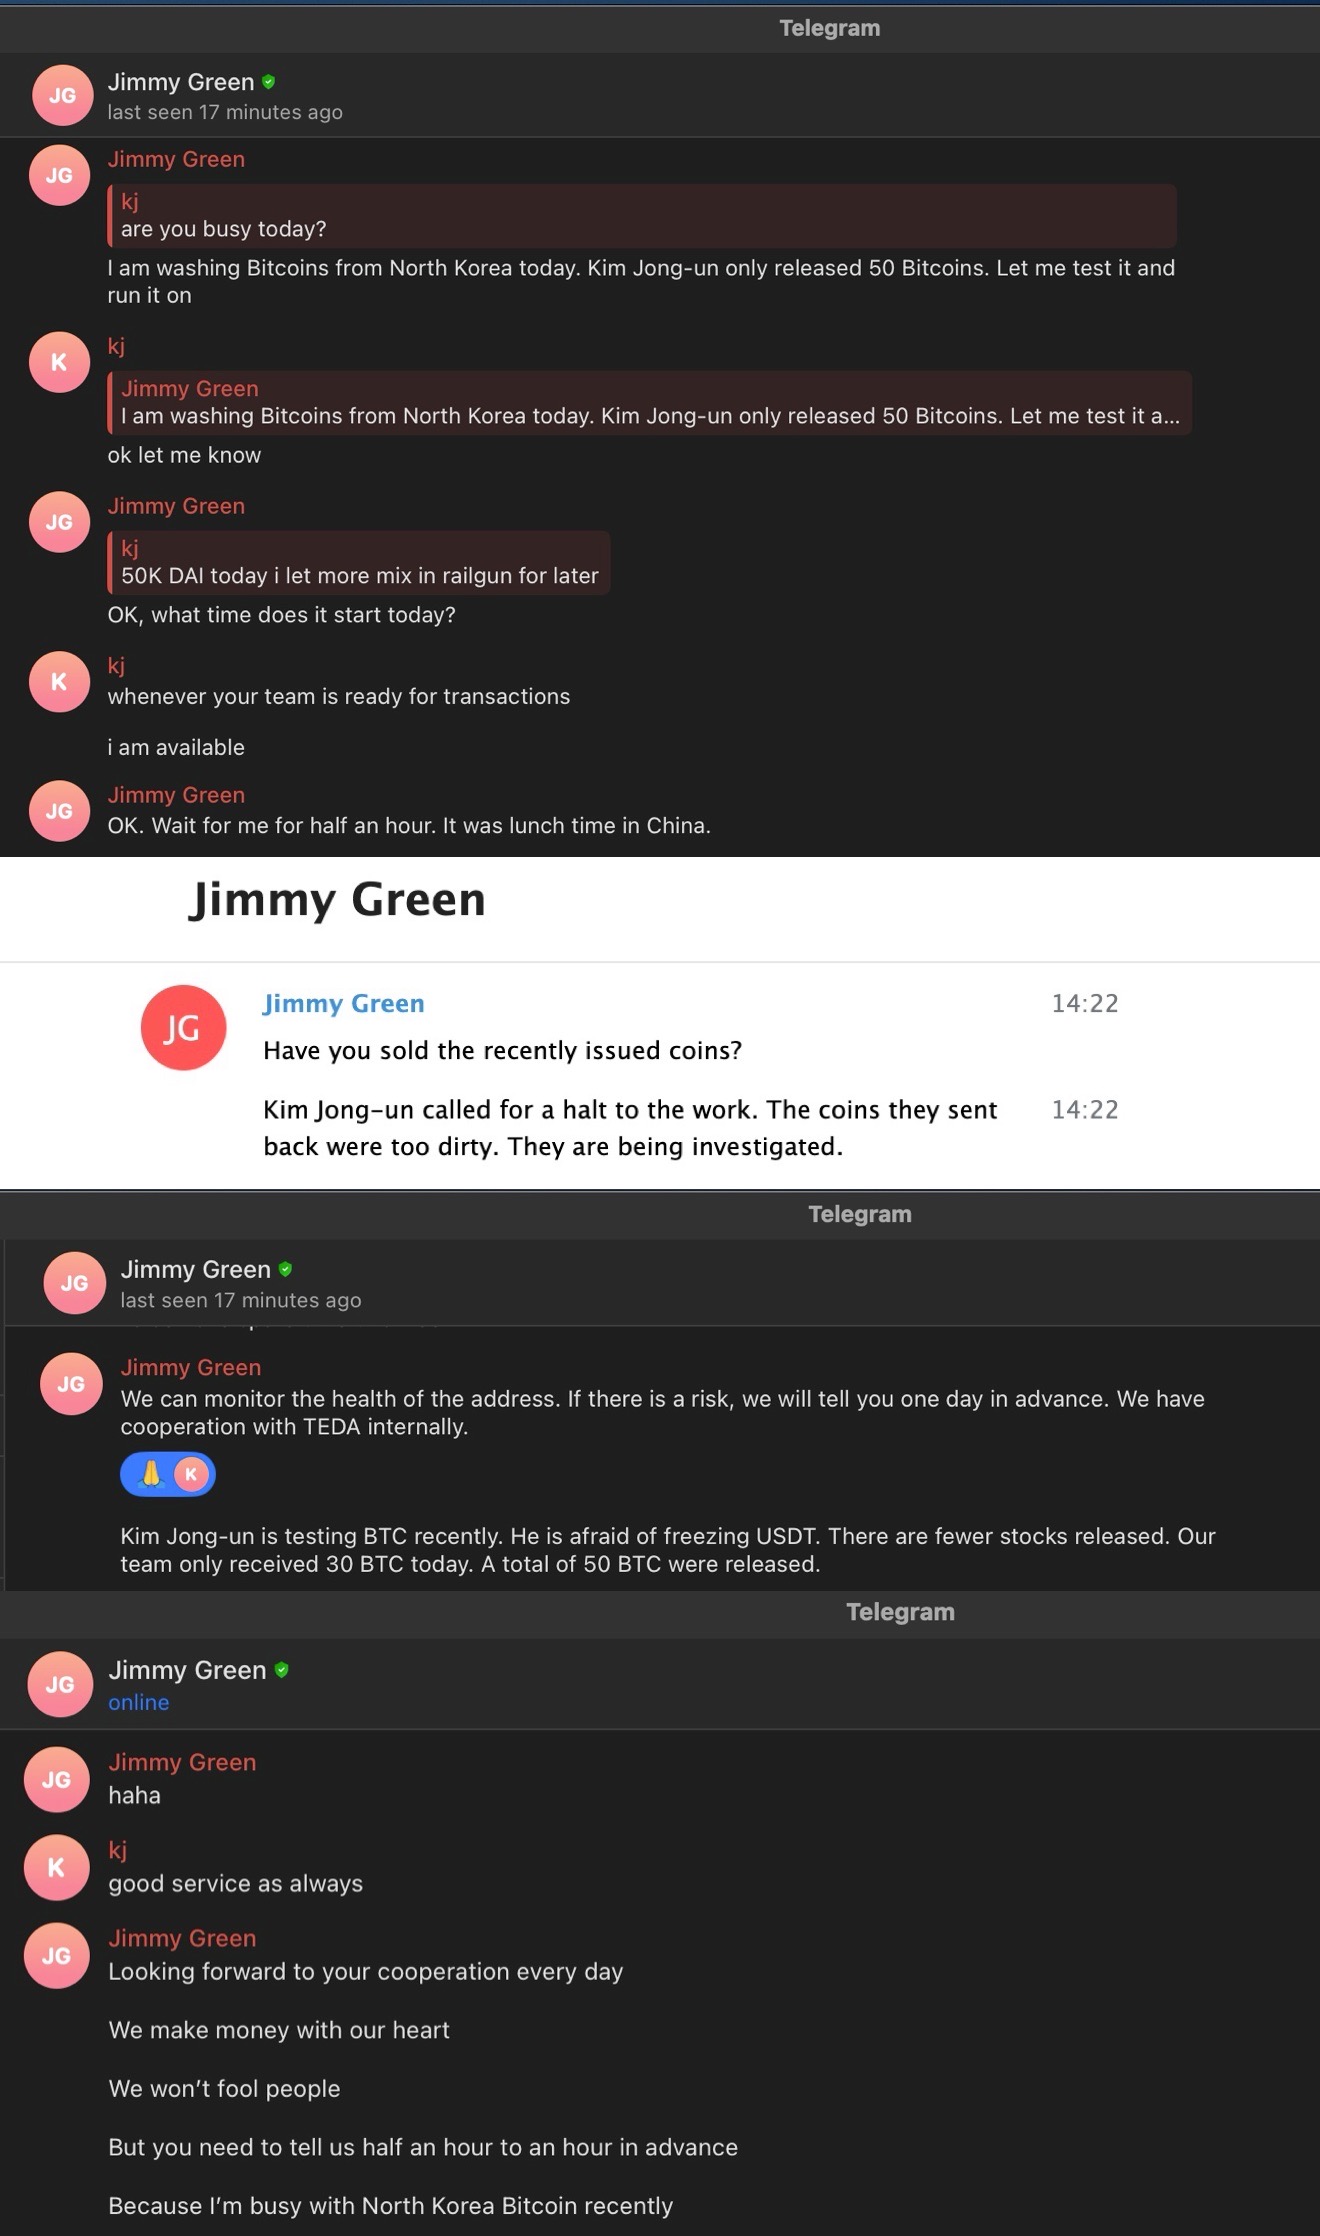
1/ How I infiltrated a Chinese organized crime syndicate that has laundered $1B+ across multiple exploits for Lazarus Group.
Posing as a client, I gathered intel that helped action freezes for the Feb 2025 Bybit exploit and attribute illicit activity onchain.

iQimpz retweeted

One 6-hour run. One hackbot. 4 confirmed criticals. 17 confirmed highs.
@jhaddix breaks down how Arcanum built Armada - their in-house hackbot running on Claude Code - and every failure it took to get there.
Full talk is up. youtu.be/cRKToFkZMvk

iQimpz retweeted

Neo is now free to try.
Neo runs long security tasks against your apps, network, code and vulnerability backlog, with shared agents context.
→ neo.projectdiscovery.io/sign…
Here’s what you can do with Neo:
iQimpz retweeted

How I got RCE and full cloud takeover on Meta at their in-person event in Taiwan
zonduu.me/posts/meta-graphra…

iQimpz retweeted

one of my engineers reached out to me about how they struggled to find satisfaction in their work in the age of AI. I asked them if I could publish our brief exchange, and they agreed. I know people are feeling similarly, so maybe they can relate. shubs.io/do-we-still-enjoy-s…
iQimpz retweeted

CVE-2024-0244: @ByteInsight details how he exploited the #Canon MF753Cdw printer back when he was a #Pwn2Own contestant. Now he's on the judging side as a ZDI analyst, but Doom is still on the table. zerodayinitiative.com/blog/2…

iQimpz retweeted

"3 random dudes”
1. hacked apple, again and again.
httpvoid.com/Apple-RCE.md
httpvoid.com/Hello-Lucee!-Le…
httpvoid.com/Hacking-Apple-w…
2. your github enterprise is our github enterprise.
httpvoid.com/GitHub-Enterpri…
3. get a discord message from me, get pwned.
hacktron.ai/blog/discord-rce
youtube.com/watch?v=R3SE4VKj…
4. oh yeah, at one point we basically had shells across the electron ecosystem. check the DEF CON research.
media.defcon.org/DEF%20CON%2…
5. your supabase database is my database.
hacktron.ai/blog/supapwn
6. we got the posthog prod database.
hacktron.ai/blog/posthog-rce
7. react2shell? vercel paid us $170k for helping secure their waf.
hacktron.ai/blog/react2shell…
8. your palo alto vpn is my vpn.
hacktron.ai/blog/cve-2026-02…
9. ai ides? we got shells for you, antigravity
hacktron.ai/blog/hacking-goo…
10. windsurf rce.
youtube.com/watch?v=23Mz7qcR…
11. turning cluely into malware.
hacktron.ai/blog/hacking-clu…
12. ai browsers? sure, uxss: your perplexity browser is my browser.
hacktron.ai/blog/perplexity-…
13. openai atlas too. kinda uxss
hacktron.ai/blog/hacking-ope…
14. hey, it’s not even our first time hacking discourse.
projectdiscovery.io/blog/dis…
15. adobe coldfusion: pre-auth rce. because apparently we needed another one.
projectdiscovery.io/blog/ado…
there’s a lot more. go dig.
anyway, yes: “3 random dudes.”
and @HacktronAI is full of more random dudes like these.

iQimpz retweeted
i don't know how many of you remember but back in the day (6 years ago), Abdelhamid was the OG! i started learning about windows logic bugs through his work instead of James's work at first.
was following his work religiously and fascinated by how clever and creative he is, from kaspersky and avast, McAfee and win defender and other ms core components to inventing file delete to EoP techniques, he did them all!
never thought such a great mind would have this happen to his journey
it really does break my heart, I never met him nor had the honour to chat with him but he became an idol in my book.
great to see, 6 years after, still his work is top-top-top tier, still mind bending and creative (wish i had a better vocab but if you can help, he is the literal definition of finding a unicorn)


iQimpz retweeted

We're publishing our most detailed threat intelligence report to date.
It covers how people tried to misuse Claude—for cyberattacks, influence operations, surveillance, biology, and building weapons—and how we found and stopped them.
We disrupted every operation in the report, and used the lessons from them to strengthen our safeguards. Where appropriate, we also shared what we found with authorities and other AI companies.
These cases are not typical: we’re highlighting some of the most sophisticated misuse we’ve seen. But they’re especially important to discuss, because they show us where AI misuse is headed, where our safeguards work, and where they need to improve.
We’re publishing this report so others can spot the same activity on their own platforms, and so we can give the public a clearer view of how emerging threats develop.
Read the report: anthropic.com/threat-intelli…

iQimpz retweeted

We built a database of 3.5 billion subdomains.
Query any domain in the world. Get every subdomain we've ever seen. One API call. <100ms.
It's live now. subdomains.jsmon.sh
iQimpz retweeted

The Bug Bounty Singularity: Our Hackbot - @rez0__
josephthacker.com/hacking/20…

iQimpz retweeted
My #BHUSA 2026 slides are online!
It was an honor to share our AFD research and how a different perspective led to 30+ Windows kernel vulnerabilities.
Blog post coming soon — check out the slides here:
i.blackhat.com/BH-USA-26/Pre…
iQimpz retweeted

I got permanently banned from @Hacker0x01. Account deleted. No explanation.
Years of work gone overnight. Submission history, achievements, leaderboard ranks, every contribution I made to the security and crypto ecosystems through HackerOne. Wiped, like I was never there.

iQimpz retweeted

Yeah that is interesting through that lense!
I think the distinction is that unlike every other transaction of value, in bug bounties the buyer decides the value, and the seller has no control over it. And the seller has to hand the value over *before* the buyer decides the price.
Imagine applying that to a supermarket. The supermarket provides an apple to the buyer, the buyer eats it, and then the buyer decides how much they'd like to pay to the supermarket for that apple 😂
In this case - supermarkets would start getting picky about which buyers they let into the shop, because they'd only want to serve buyers who pay a higher price. That's like how bug bounty hunters are picky about which programs they are willing to hack on, based on their past experiences. But it takes a long time and a lot of effort to figure out the good from the bad.